Customizing GodPotato for Improved Evasion
Renaming and modifying GodPotato to reduce obvious signatures and improve payload evasion.
Open Write-up →Active Directory Lab Designer • Red Team Enthusiast • HackSmarter • Founder of R00tF0rce
Building realistic Active Directory penetration testing labs inspired by real-world enterprise environments.
❄️ FREEZE THE DOMAIN

Hi, I'm 2ubZ3r0. Passionate about Active Directory security, red teaming, Windows internals and realistic attack simulations. I design hands-on penetration testing labs that teach modern AD attack paths, privilege escalation and enterprise compromise techniques without unrealistic CTF gimmicks.
RELEASED
Enterprise AD focused on privilege escalation, delegation abuse, advanced Kerberos attack paths.

Satellite Operations / Space Tech
A realistic enterprise satellite operations environment where small pieces of public information become valuable attack vectors.

Municipal Government
An internal government network focused on realistic Active Directory misconfigurations. Phishing, DPAPI, Kerberoasting, IIS.

Cybersecurity Company
Exploit vulnerable dev infrastructure, abuse delegated AD rights, restore deleted users, escalate through AD CS.

Financial Institution
Web apps, internal services, certificate infrastructure. BloodHound, password attacks, tunneling, AD CS abuse.

Healthcare / Enterprise
Complex healthcare AD with multiple paths: SQL injection into linked servers, AD CS, DLL hijacking, SYSTEM priv.

Retail Enterprise
DNS abuse, NTLM relay, certificate attacks, advanced delegation. Realistic enterprise admin mistakes.

Manufacturing
Phishing entry, credential harvesting, Browser Extraction, BloodHound, NTLM reflection, Kerberos delegation.
COMING SOON
Your first steps into a corporate Active Directory environment. Orion Corp is an easy, beginner-friendly Windows lab that rewards careful enumeration, curiosity and connecting the dots. Build confidence as you work toward taking control of the domain.
COMING SOON
Healthcare-themed AD lab featuring Windows administration mistakes, WSL Pivot to Windows, lateral movement, enterprise credential abuse.
COMING SOON
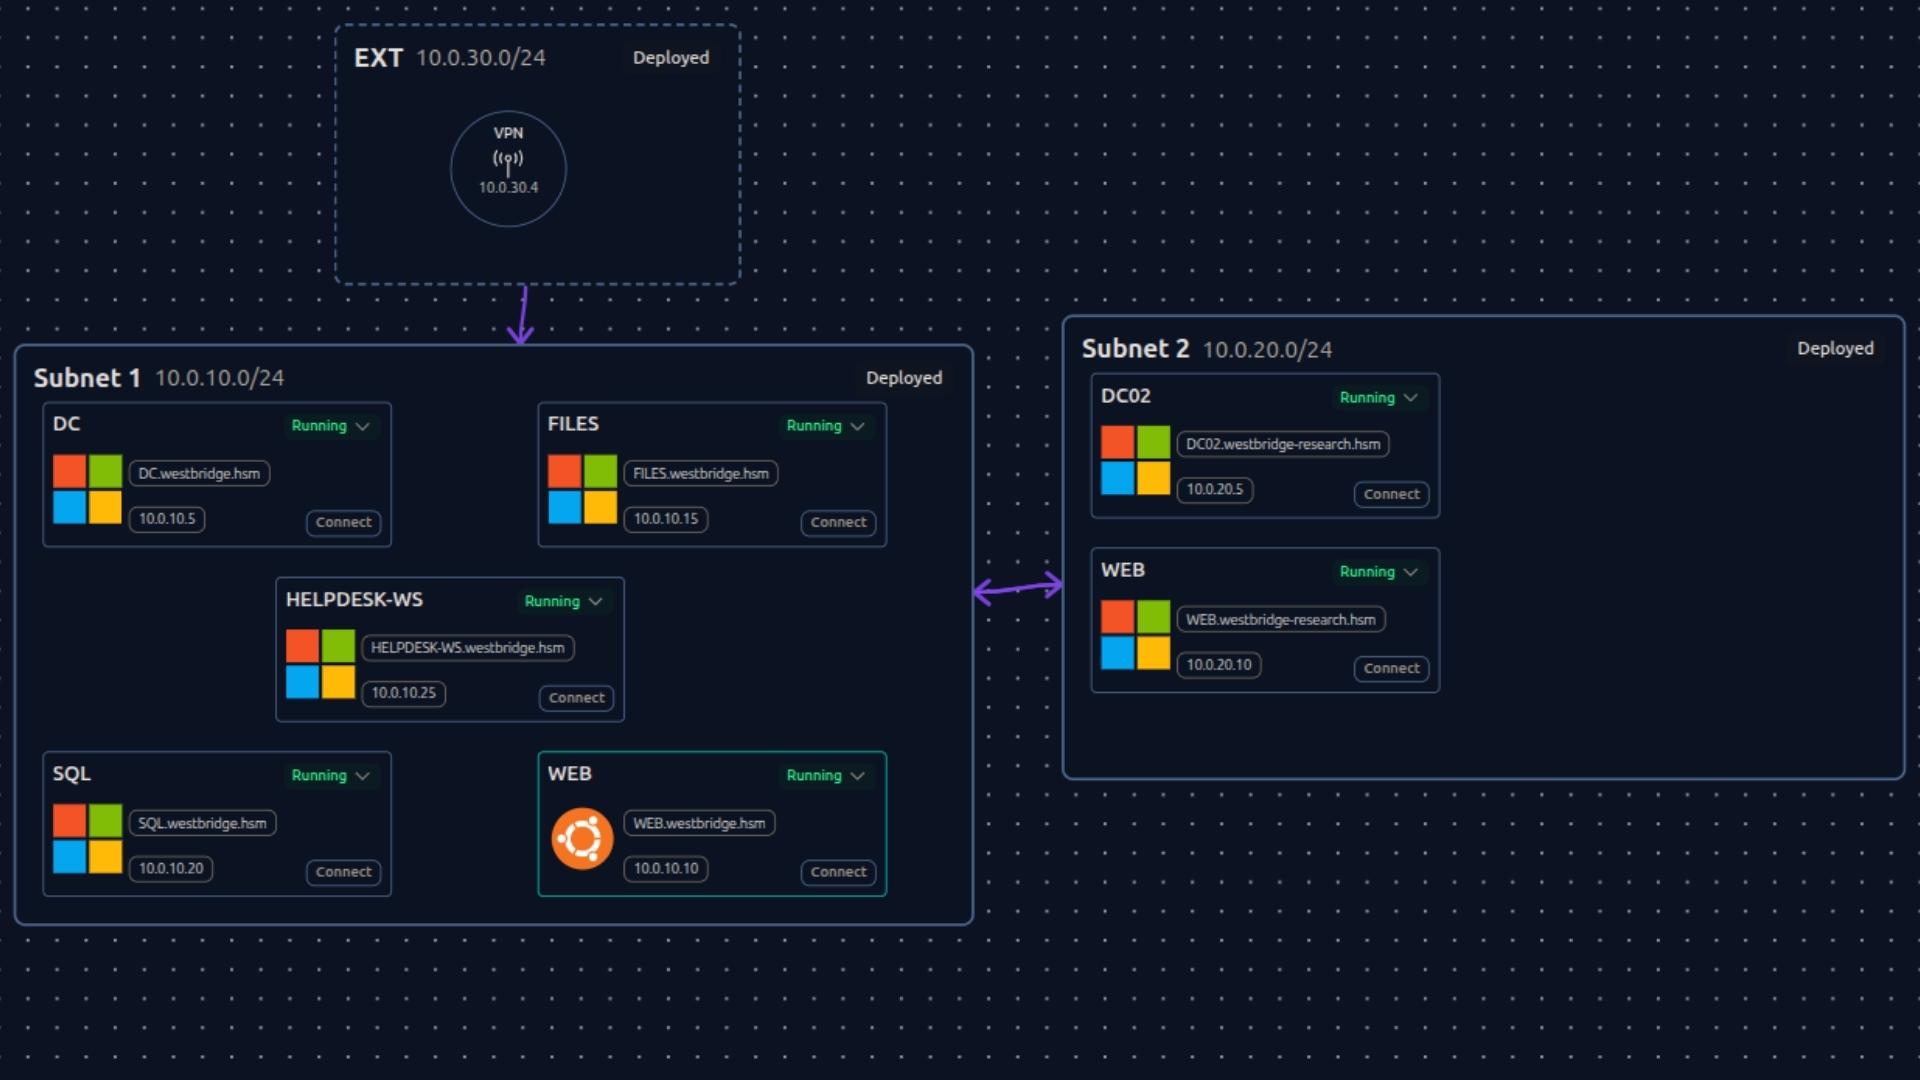
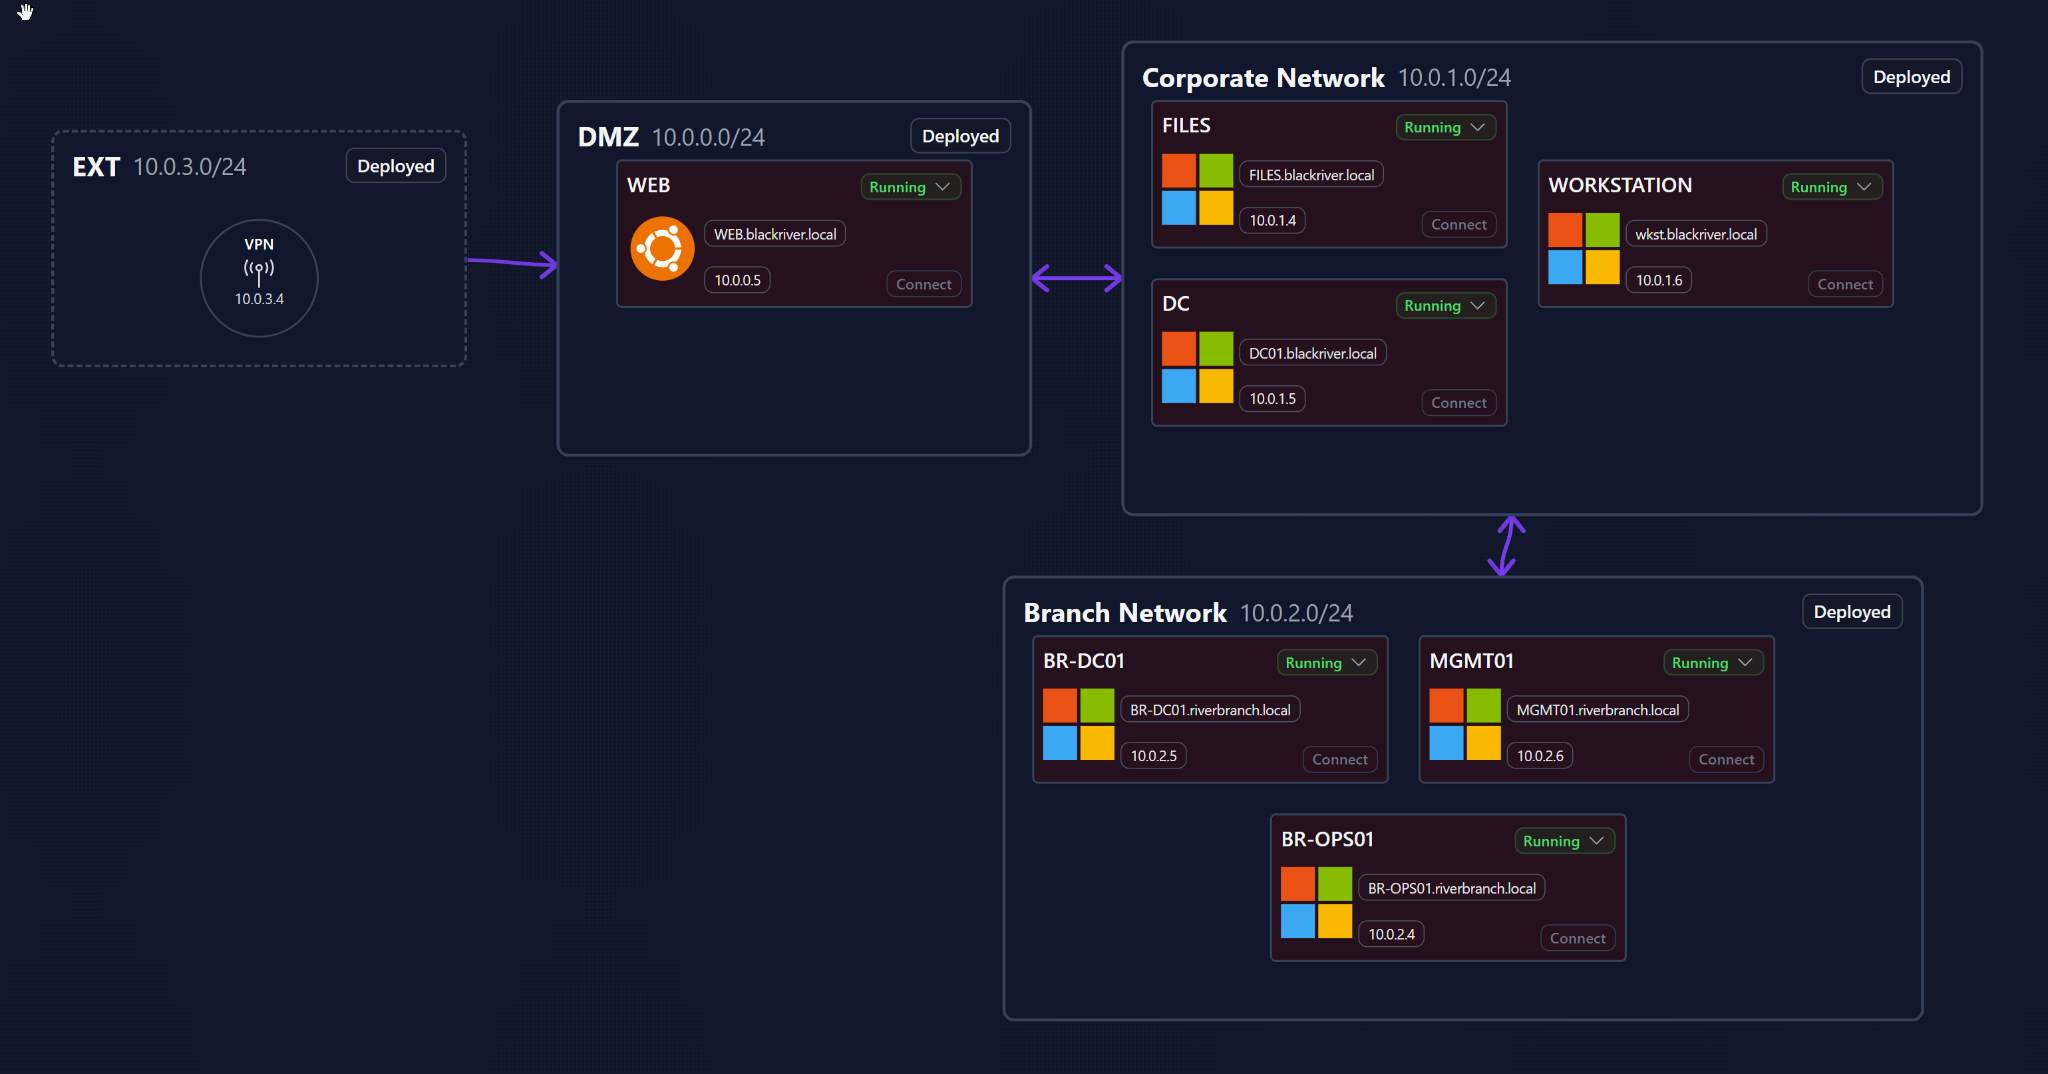
A hard, eight-machine Active Directory range featuring a vulnerable LLM-powered machine. Explore three subnets, parent and child domains, and an external trust as you pivot through the environment.
Free and paid downloadable labs for hands-on practice with offensive security, Active Directory and CTF challenges. Pick up labs at very affordable prices in my Buy Me a Coffee Lab Shop—every purchase supports my work and helps me create more content. The shop exclusively offers previously unreleased labs that are not available on HackSmarter or other platforms.
 FREE
Windows Active Directory · Beginner CTF
Beginner-friendly Active Directory machine in a classic CTF style. Take it with humor and do not expect enterprise realism. Perfect for learning BloodHound, AD enumeration and common Windows attack paths.
Import the .OVA into VirtualBox or VMware. DHCP assigns the IP automatically. The archive includes the write-up and a Description file with the starting credentials.
Download PulpFiction FREE
Linux · Easy
Easy Linux lab available as a free download.
Windows Active Directory · Single-Machine CTF
Redstone is a single-machine Windows Active Directory CTF lab with a Minecraft twist. Gain an initial foothold, uncover hidden services, and navigate AD misconfigurations to take control of the domain. A hands-on challenge combining service exploitation, Kerberos, and privilege escalation—capture both the user and root flags!
Windows Active Directory · CTF Lab
Explore the infrastructure behind a media streaming company in this Windows Active Directory CTF lab. Gain an initial foothold, uncover exposed credentials, and follow a chain of misconfigurations to take control of the domain. Practice service exploitation and database enumeration.
Windows Active Directory · Easy CTF Lab
Explore a university’s Windows Active Directory environment in this beginner-friendly CTF lab. Discover exposed accounts, investigate student shares, and uncover clues hidden in university tools. Connect misconfigured permissions and Kerberos delegation to work your way toward domain compromise.
Windows Active Directory · CTF Lab
Explore the infrastructure of Nexora Systems, an enterprise IT company, in this Windows Active Directory CTF lab. Discover hidden web pages, investigate internal documents, and uncover credentials in forgotten backups. Follow a chain of misconfigured AD permissions, access internal services, and exploit React2Shell to advance toward domain compromise.
Windows Active Directory · CTF Lab
Practice SMB enumeration, DNS manipulation, shadow credentials, MSSQL enumeration, and the abuse of misconfigured AD permissions and Group Policies.
Vulnerability research, CVEs, exploit analysis, payload research and offensive security notes.
Renaming and modifying GodPotato to reduce obvious signatures and improve payload evasion.
Open Write-up →
Building and obfuscating a custom payload with Freeze for cleaner AV evasion testing.
Open Write-up →
Using a custom loader and Metasploit payload workflow to test antivirus bypass techniques.
Open Write-up →
Creating and embedding macro-based payloads in Microsoft Word for controlled phishing labs.
Open Write-up →
Research and exploitation notes for Certighost, focusing on certificate trust abuse.
Open Write-up →
Technical notes on CVE-2025-33073, exploitation flow and privilege escalation impact.
Open Write-up →
Analysis of CVE-2025-54918 with a focus on exploitation and elevated system access.
Open Write-up →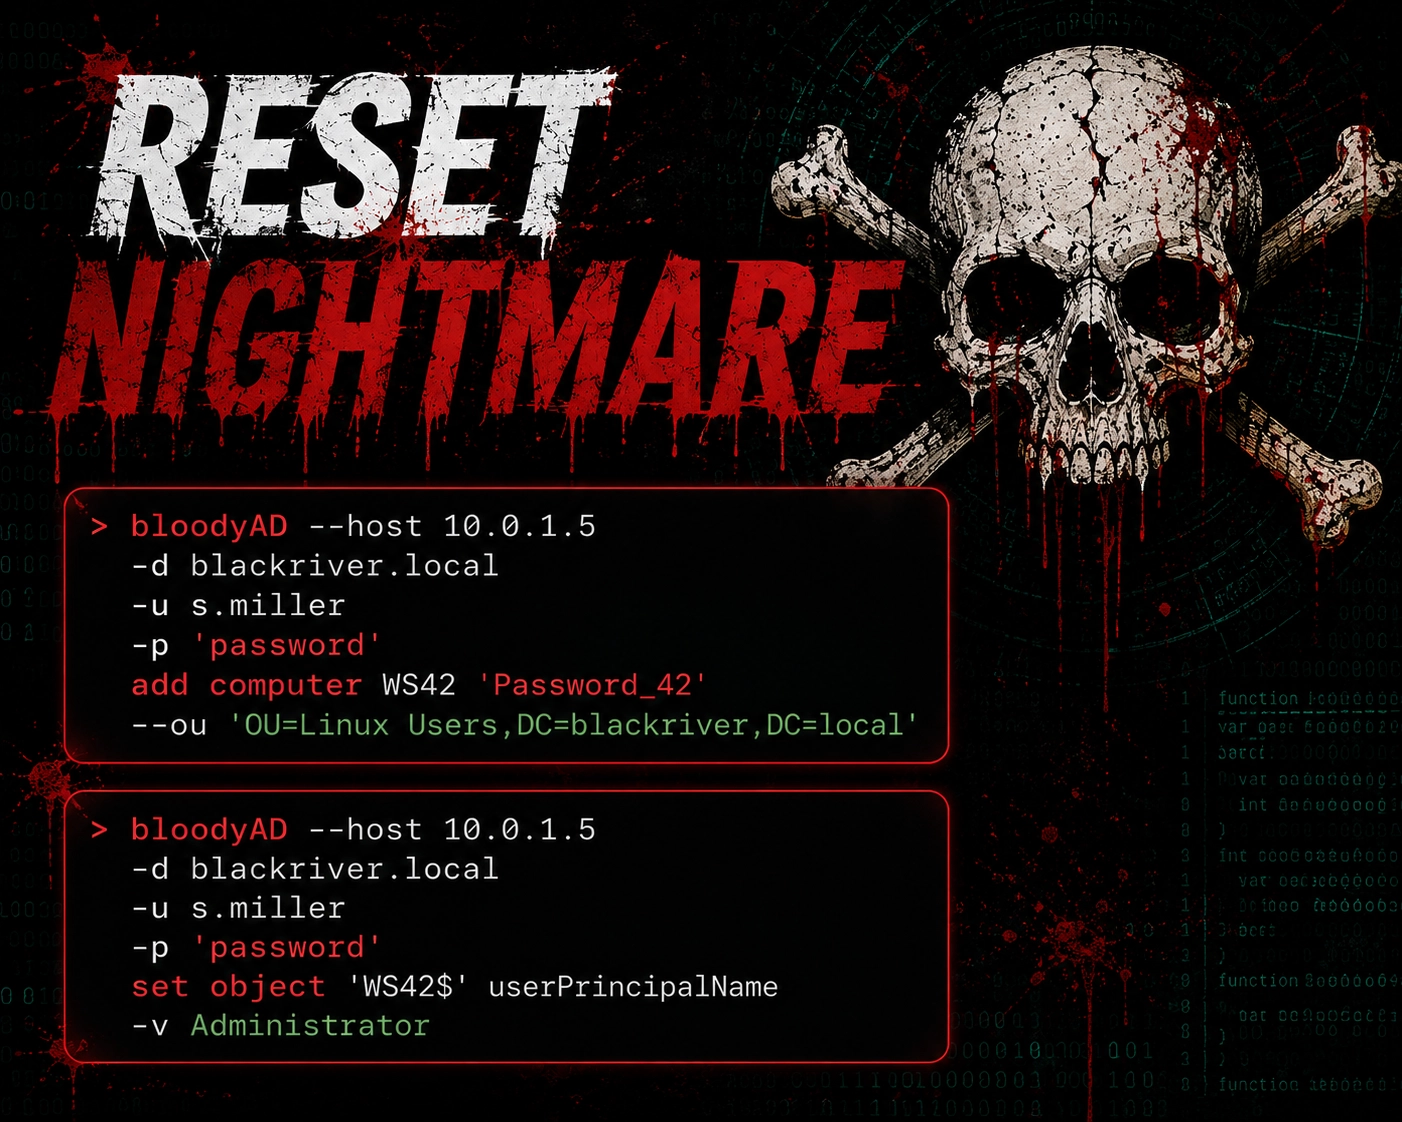
Research into Reset Nightmare, an Active Directory abuse path involving delegated account control.
Open Write-up →
Technical analysis of the WordPress WP2Shell exploit chain, proof-of-concept behavior, impact and mitigation guidance.
Open Write-up →Built from real-world internal penetration testing concepts.
Focus on current attack techniques used in enterprise environments.
More than one valid compromise path exists in many labs.
Enumeration matters more than guessing vulnerabilities.
Walkthroughs of retired Hack The Box machines.
7 Reports
Explore a segmented Linux network where wireless traffic and network services reveal the next lead. A hands-on journey through Wi-Fi security and internal network exploration.
Open Write-up →
Investigate shared reports and a messaging service in a Windows domain. Connect infrastructure clues with authentication behavior across a layered Active Directory challenge.
Open Write-up →
Follow a webmail investigation into a mixed Linux and Windows corporate network. A longer challenge combining web analysis, internal exploration, and domain security.
Open Write-up →
Look beyond a dating website to discover its supporting services. Practice careful web enumeration and local service investigation in an approachable Linux challenge.
Open Write-up →
Explore a browser-extension testing platform and its developer tooling. Follow application behavior and source-code clues to understand how browser and system boundaries connect.
Open Write-up →
Investigate a simulated industrial environment, from its web-facing data flows to internal control services. Documentation and maintenance workflows provide clues along the way.
Open Write-up →A demanding Hack The Box challenge that combines deep enumeration, application analysis, and multi-stage privilege escalation across a complex environment.
Open Write-up →If you've enjoyed my HackSmarter labs and want to support future content, consider buying me a coffee.